
CVE-2024-43629 Vulnerability Details
More in Windows
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- A look inside ESE
Looking inside ESE 🫣 During incident investigations, we at PT ESC IR regularly encounter the need…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…
- Confusion in WSUS vulnerabilities: setting the record straight
Confusion Around WSUS Vulnerabilities: Setting the Record Straight 🕷 One of the most pressing vulnerabilities in…
- Disabling Defender / MpPreference
In addition to the post 👆 Disabling Defender / MpPreference Set-MpPreference -DisableRealtimeMonitoring $true Set-MpPreference -DisableBehaviorMonitoring $true…



😏 Exclusively for Escalator, the ESC-VR team shares details about the vulnerability (CVE-2024-43629) that we found in the Desktop Window Manager component, allowing privilege escalation to system level.
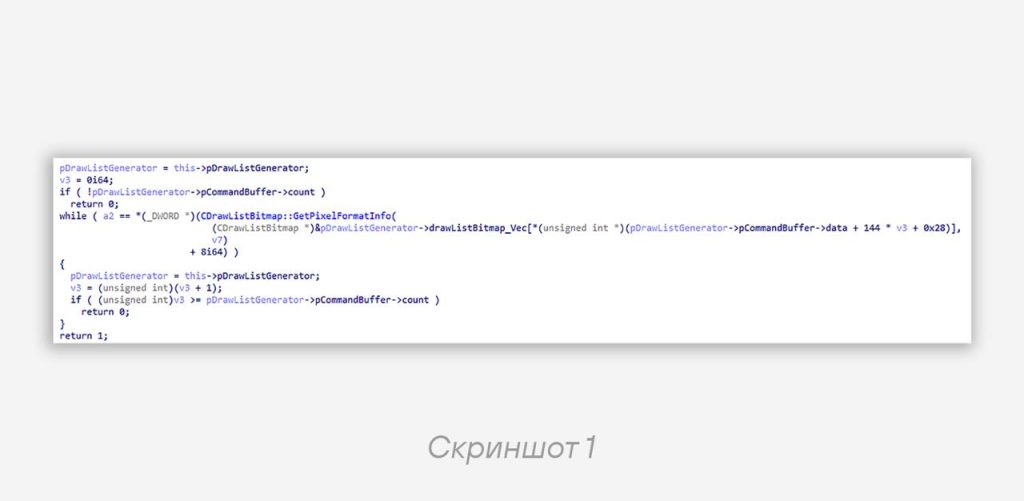
The vulnerability was located in the dwmcore.dll library in the CPrimitiveGroupDrawListBrush::IsColorConversionRequired function (screenshot 1). When the CSurfaceBrush and CPrimitiveGroup classes were used together, it allowed reaching code that calculates the position of a CDrawListBitmap class instance in the drawListBitmap_Vec array, which in turn is located in an instance of the CPrimitiveGroupDrawListGenerator class.
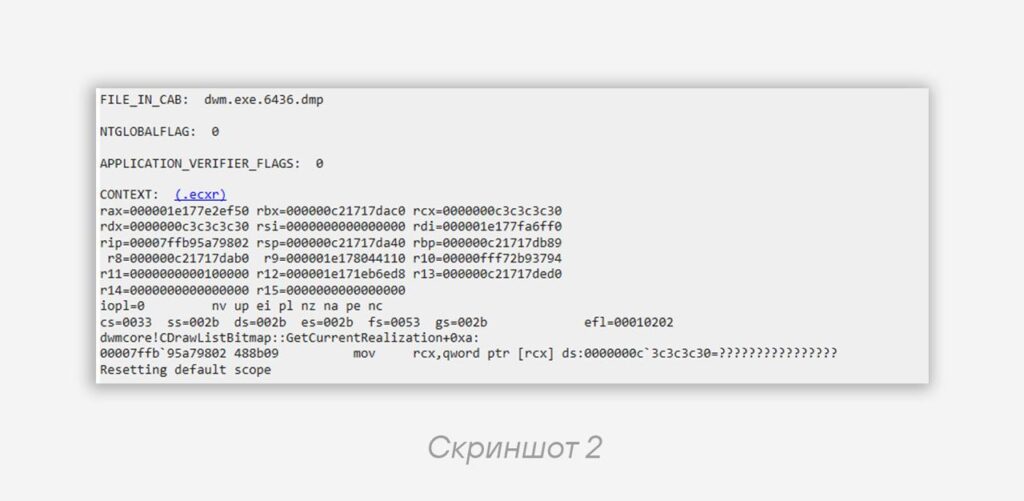
With a certain combination of properties of the CSurfaceBrush and CPrimitiveGroup instances, a situation could arise in which the drawListBitmap_Vec pointer would be equal to zero and all calculations would be reduced to working only with the index, and its value would be fully controlled by the attacker and would have the size DWORD. This way, it would be possible to hijack a pointer to a CDrawListBitmap object (screenshot 2).
#escvr #win #cve
@ptescalator
More from author_vr
- Out-of-bounds write in ntfs!PageUpdateAnalysis
A heap buffer overflow vulnerability exists in the ntfs!PageUpdateAnalysis function of the Microsoft Windows NTFS driver.…
- How to CVE-2025-54916? Low-effort vulnerability research
How to CVE-2025-54916? Low-effort vulnerability research 💻 Hi, ESC-VR here. The Telegram post format is rarely…
- Roots of the CVE-2024-30085 vulnerability
Roots of the CVE-2024-30085 Vulnerability 🌳 Back in September of last year, we at ESC-VR successfully…
- What happened to OpenSSH security in 2024
What happened to OpenSSH security in 2024 🚪 Let's look at the timeline: • Spring. Backdoor…
- Not a Pwn2Own bug
Not a Pwn2Own bug 🙂 CVE-2024-43641: a CWE-190 type error allowed overflowing the reference count on…
More in Windows
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- A look inside ESE
Looking inside ESE 🫣 During incident investigations, we at PT ESC IR regularly encounter the need…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…
- Confusion in WSUS vulnerabilities: setting the record straight
Confusion Around WSUS Vulnerabilities: Setting the Record Straight 🕷 One of the most pressing vulnerabilities in…
- Disabling Defender / MpPreference
In addition to the post 👆 Disabling Defender / MpPreference Set-MpPreference -DisableRealtimeMonitoring $true Set-MpPreference -DisableBehaviorMonitoring $true…