
Exfiltration gone wrong
More in General
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…




😈 Exfiltration Gone Wrong
When investigating incidents, we periodically encounter threat actors exfiltrating data before encrypting infrastructure.
One of the exfiltration tools can be the rclone utility, which is often used in conjunction with MEGA. Hackers clean up and delete the utilities after use.
This is where the USN journal comes to the rescue:
"2024-01-01 00:05:00","rclone.exe","","File_Created","Normal","Archive"...
"2024-01-01 01:01:10","rclone","\Users\<username>\AppData\Roaming\rclone","File_Created","Normal","Directory"...
"2024-01-01 02:01:11","mega.conf","","File_Closed / File_Deleted","Normal","Archive"...
"2024-01-01 02:01:11","rclone.exe","","File_Closed / File_Deleted","Normal","Archive"...
Code language: plaintext (plaintext)
What useful information can we learn:
• the fact that rclone was used;
• the date and time of its use;
• file names (they may be modified, which is a new indicator).
🤷♂️ The config could not be recovered. What should we do?
In the MFT, small files (a few hundred bytes) are stored entirely within the corresponding record. Given this feature, we use the MFTECmd utility with the --dr flag to recover them and then search for the config using the pattern '^(type|pass(word[0-9]?)?) \= '.
Example of the configuration file contents:
type = mega
user = evilname@evildomain
pass = qhLeOj9dBRBMCRPptaZA7rghfCkM7b_fsMR0cQ

[mega_crypt]
type = crypt
remote = mega_clear:files
password = v55MNmgFh3qEIfsNA0UtwNaRPYufBOyWNb69pOE
password2 = Ooxh0-uHI2Wb9MrrmPrTgOSsgqUN4QaKwsi0Yt4
Code language: plaintext (plaintext)
Once you have obtained information about the account, you can file a complaint with MEGA and try to prevent the data from appearing in public access.
✨ Bonus
To decode the data in the pass field, you can use one of the following tools:
• rclone obscure;
• Go playground.
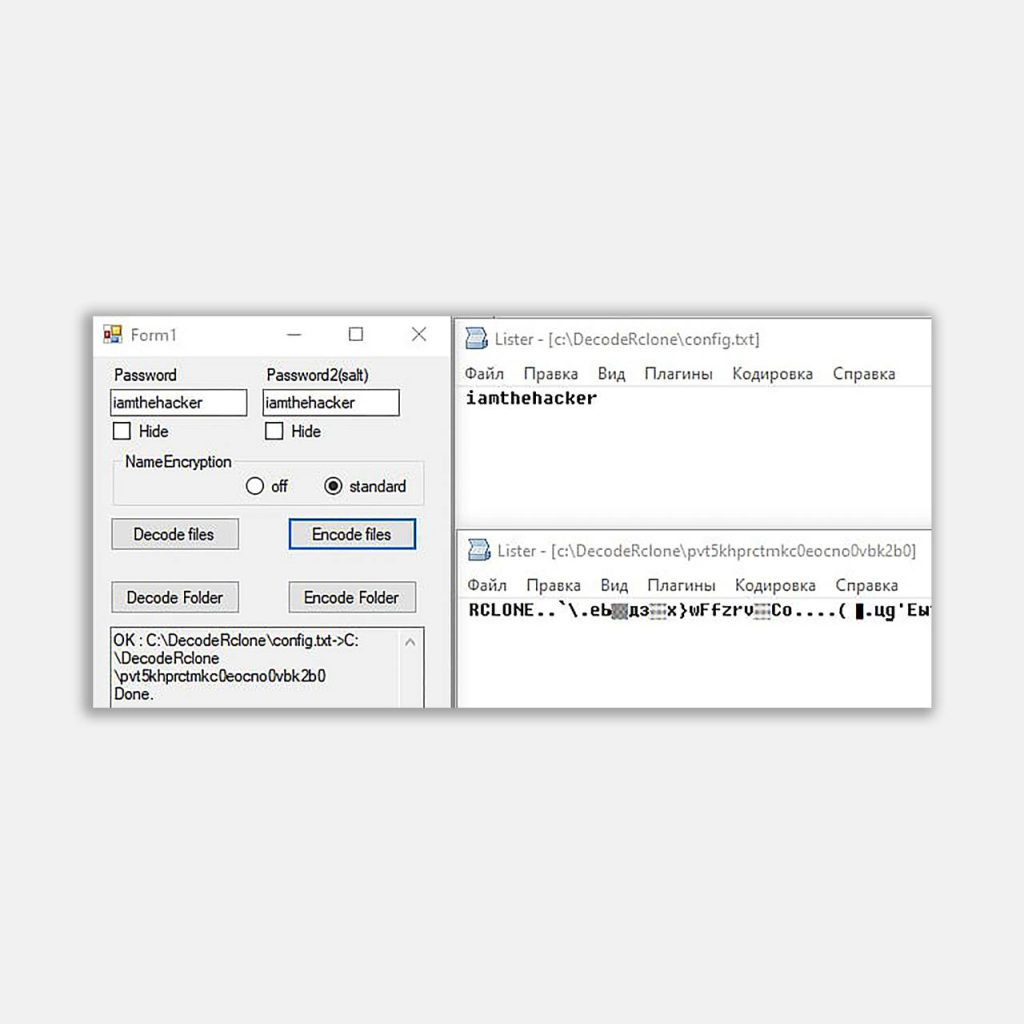
When transferred to cloud storage, files (as well as their names) may be encrypted. To solve this problem, there is a utility called DecodeRclone.
Thus, we discovered:
• the fact of data exfiltration;
• the time of exfiltration;
• the threat actors’ account;
• the list of leaked data (for risk assessment, for example);
• authentication credentials in the “cloud” (for general knowledge 🙂).
#tools #detect #tips #dfir
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…
More in General
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…