
Exploit for CVE-2024-30085
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




The vulnerability was featured at the recent Pwn2Own 2024 in Vancouver, where Team Theori used an exploit for this vulnerability in an exploit chain performing Guest-To-Host-Escape from under VMware Workstation management, for which they received their well-deserved 13 points in the Master Of Pwn nomination.
Competitions like pwn2own and matrixcup help highlight real-world exploitable vulnerabilities, exploits for which are typically not disclosed (resulting in a Known-Unknown state, where it is known that an exploit exists, but how it works is unknown), and draw special attention to them, because such competitions are followed not only by us, but also by attackers who can reproduce them and exploit them against an unpatched system.
🧐
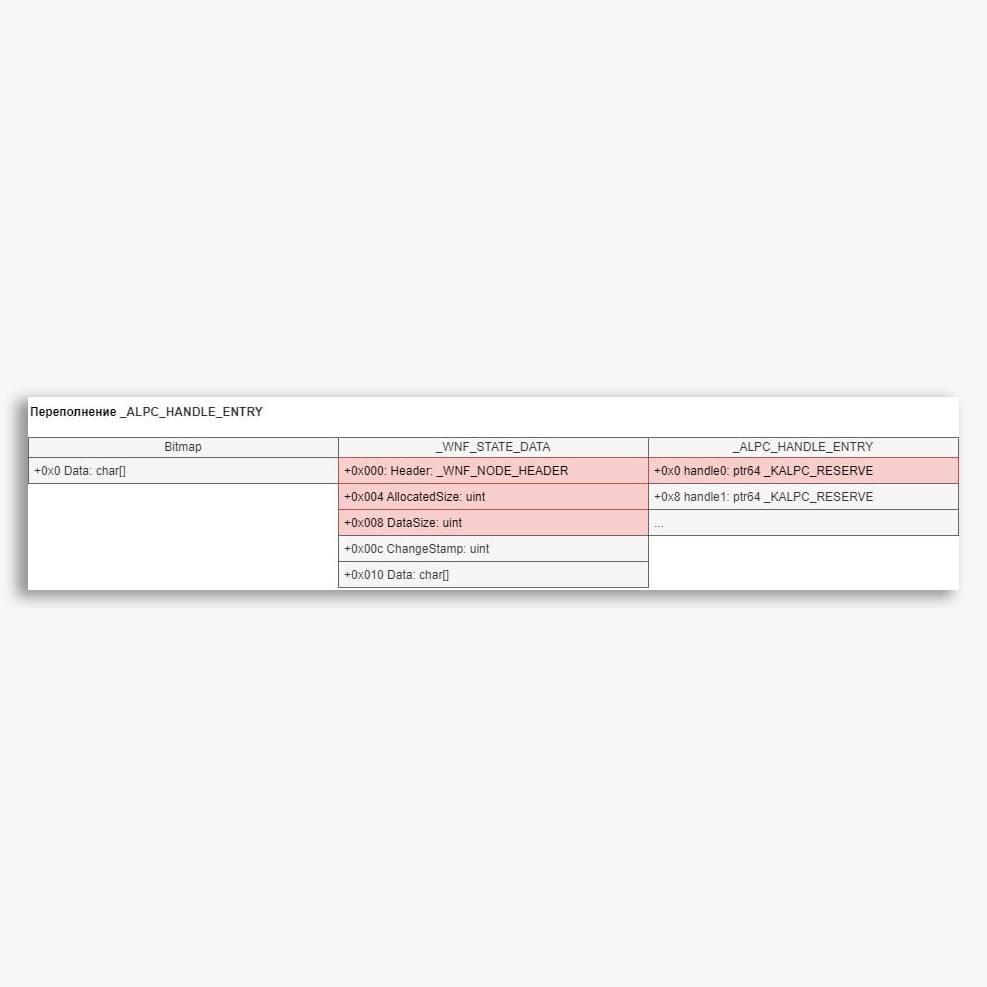
Cldflt.sys — is a minifilter driver responsible for synchronization between the user file system and the OneDrive cloud. The driver had a CWE-122 error, arising as a result of incorrect validation of the bitmap size, the contents of which are obtained from a Reparse Point. At the same time, the memory allocated for the bitmap has a fixed size of 4096 bytes, but the size of the actual data that will be copied into the allocated memory is not checked. Our exploit utilizes the WNF and ALPC subsystems to obtain write and read primitives, specifically for the
_WNF_STATE_DATA and _ALPC_HANDLE_ENTRY structures.💡 A few details about how our exploit works:
1️⃣ Creates multiple chunks, 4096 bytes in size, via
NtCreateWnfStateName and NtAlpcCreateResourceReserve. This sequentially places _WNF_STATE_DATA and _ALPC_HANDLE_ENTRY in memory.2️⃣ Creates multiple holes in the sequence created in step 1, via
NtDeleteWnfStateData.3️⃣ Triggers the vulnerability, thus the bitmap is placed in one of the pre-prepared holes. The bitmap size is set equal to 4096 + 16, in order to overwrite the size of the data (
_WNF_STATE_DATA.DataSize) pointed to by _WNF_STATE_DATA.Data.4️⃣ Overwrites the pointers in
_ALPC_HANDLE_ENTRY via NtUpdateWnfStateData.5️⃣ Performs arbitrary address write and read via
NtAlpcSendWaitReceivePort.6️⃣ Steals the Token from the System process (Token Stealing).
Of course, we could not help but test our own products. And they did not disappoint us: for example, PT Sandbox detects the exploitation of this vulnerability.
Verdicts:
Exploit.Win32.Generic.d,
Exploit.Win32.Generic.a,
Rootkit.Win32.Generic.a
Code language: plaintext (plaintext)
#escvr #cve #news
@ptescalator
More from author_vr
- Out-of-bounds write in ntfs!PageUpdateAnalysis
A heap buffer overflow vulnerability exists in the ntfs!PageUpdateAnalysis function of the Microsoft Windows NTFS driver.…
- How to CVE-2025-54916? Low-effort vulnerability research
How to CVE-2025-54916? Low-effort vulnerability research 💻 Hi, ESC-VR here. The Telegram post format is rarely…
- Roots of the CVE-2024-30085 vulnerability
Roots of the CVE-2024-30085 Vulnerability 🌳 Back in September of last year, we at ESC-VR successfully…
- What happened to OpenSSH security in 2024
What happened to OpenSSH security in 2024 🚪 Let's look at the timeline: • Spring. Backdoor…
- Not a Pwn2Own bug
Not a Pwn2Own bug 🙂 CVE-2024-43641: a CWE-190 type error allowed overflowing the reference count on…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…