
DragonDoll: a matryoshka in the world of Android spies
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…



DragonDoll: a matryoshka in the world of Android spies 🪆
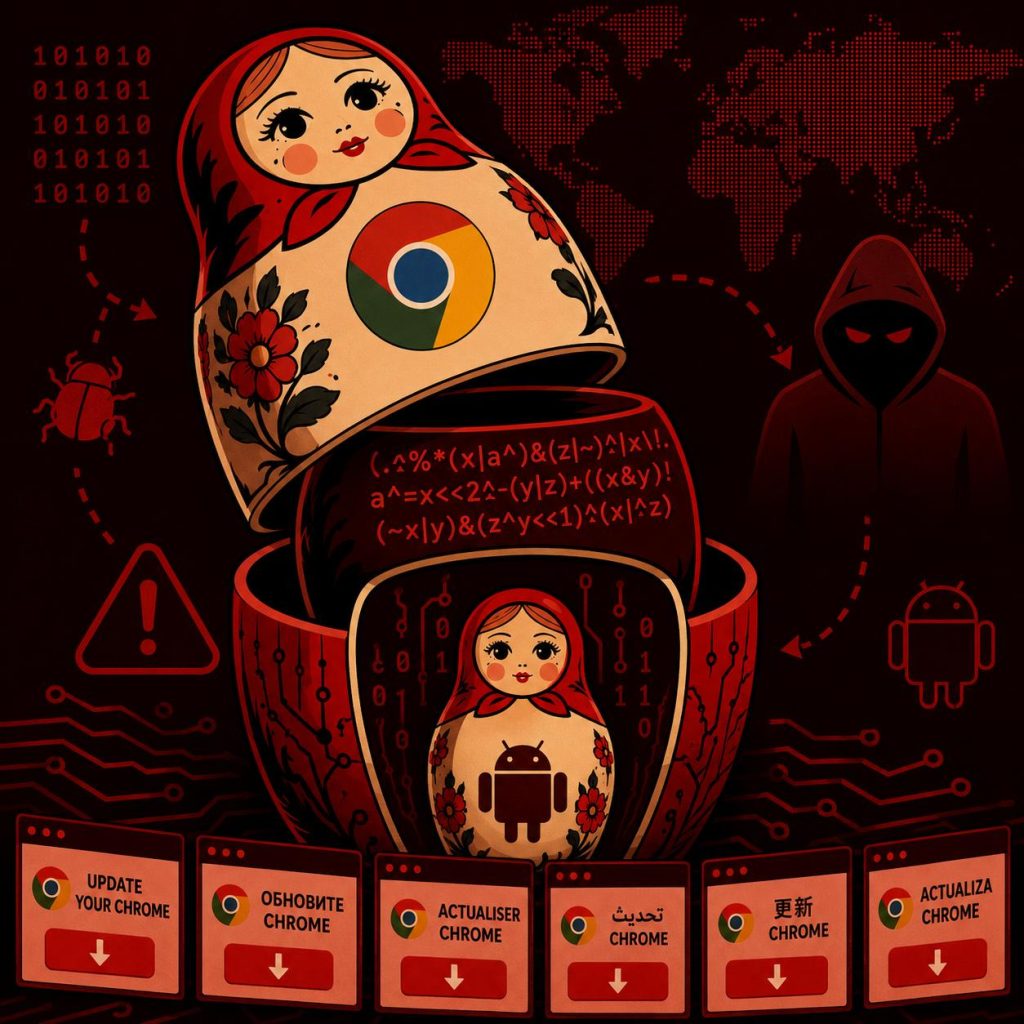
At the beginning of this spring, PT ESC specialists discovered a previously unknown APK file uploaded from Saudi Arabia. The sample itself contained many Defense Evasion techniques.
To complicate analysis, the following were used:
• 1 BadPack technique
• 2 stages of loading native libraries
• 1 LLVM-based obfuscation
• 6 checks for execution in a virtual environment
• and a countless number of MBA expressions
After long suffering stages of analysis, with the help of emulation, the laws of Boolean algebra, and several hundred lines of code, our specialists unpacked the new Android spy DragonDoll 📱
During the investigation, we stumbled upon a large-scale attack involving this malware, targeting Android users from more than 26 countries, including Russia.
The attackers used GitHub as a source for distributing and continuously updating DragonDoll. A link to this repository led to a network of fake Chrome “update” sites, the content of which adapted to the victim’s language.
A breakdown of what lay beneath the layer of obfuscation — in our blog ⬅️
#TI #Android #Malware
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
- PT ESC cyber intelligence group presented an overview of cyberattacks for Q2 2026 ✍️
PT ESC Cyber Intelligence Group presented an overview of cyberattacks for Q2 2026 ✍️ The report…

More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…