
AI-95 with a malicious additive ⛽️
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




AI-95 with a malicious additive ⛽️
In mid-June, the Threat Intelligence team discovered several resources at once using a “fuel” theme for malicious purposes.
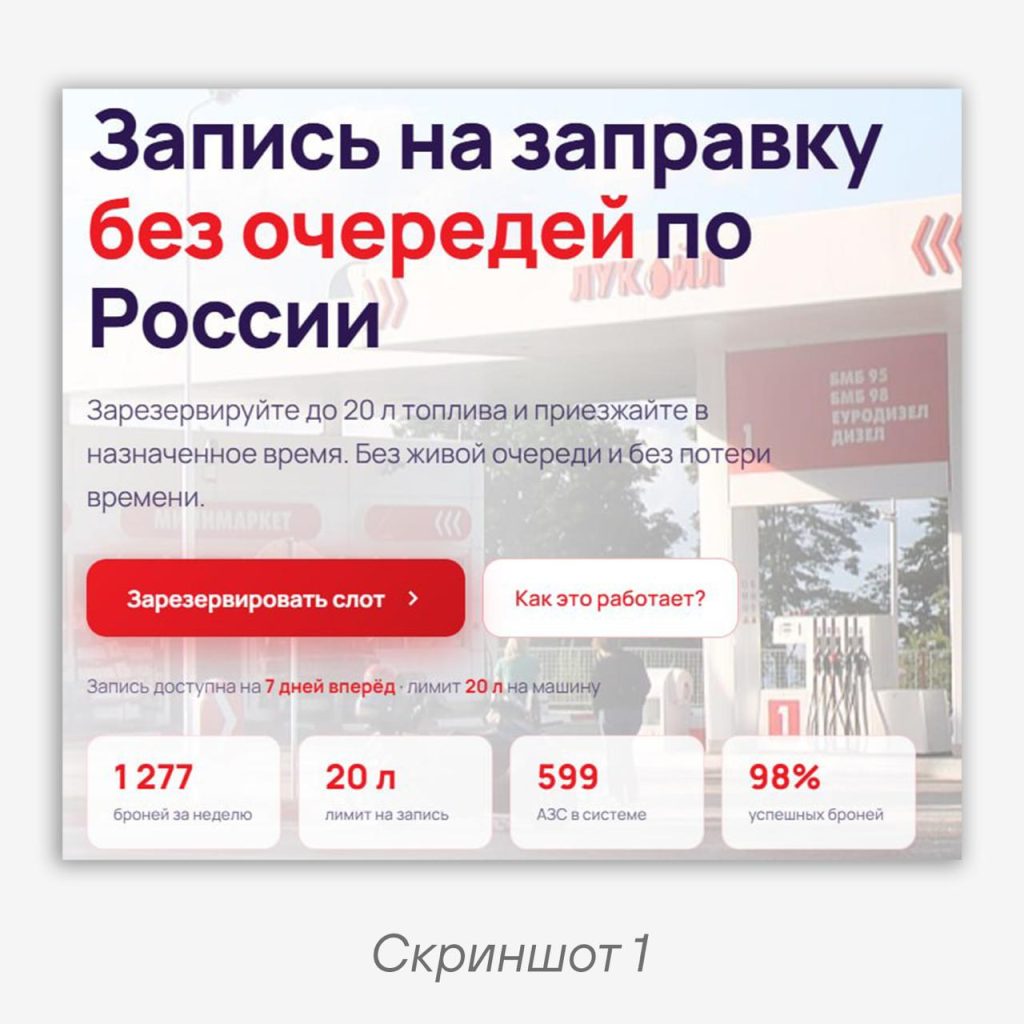
0️⃣1️⃣ In the first campaign (screenshot 1), Telegram accounts are hijacked. On behalf of a large oil and gas organization that provides fuel sales services to individuals, users are offered to “book” a time to buy fuel without queues. During the booking process, the attackers ask for a confirmation code (screenshot 2), which is actually the two-factor authentication code for the Telegram account. We note that the source code of the resources is replete with comments characteristic of code generated by large language models.
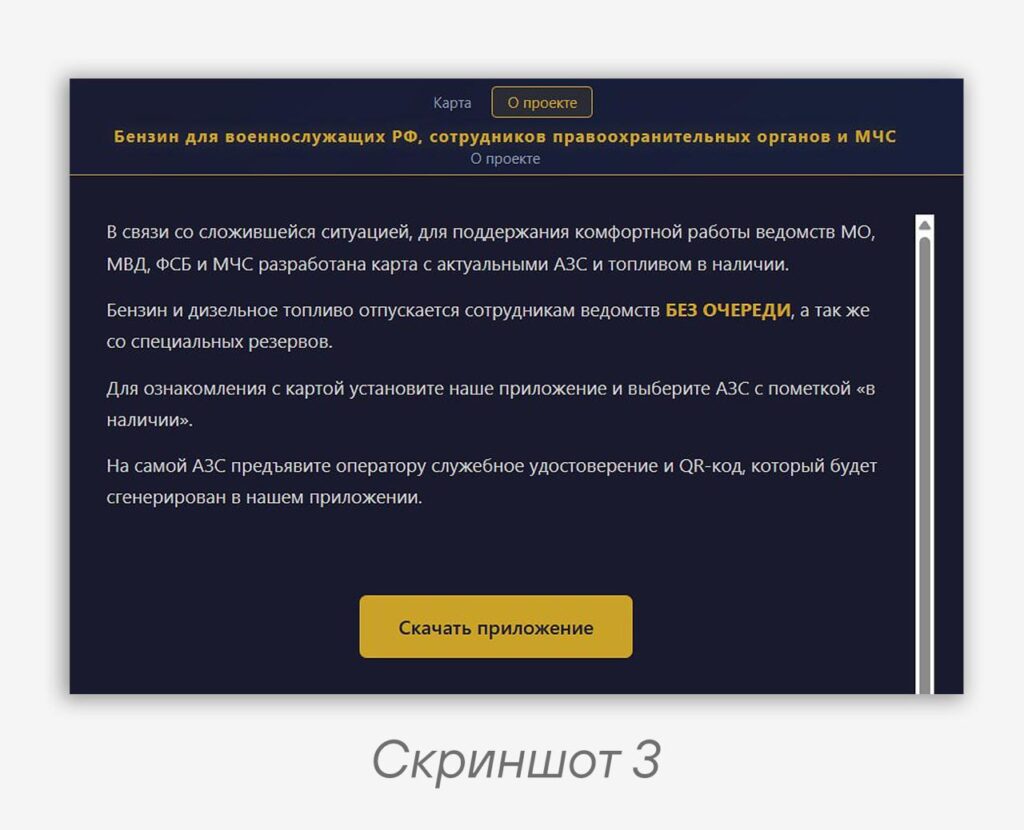
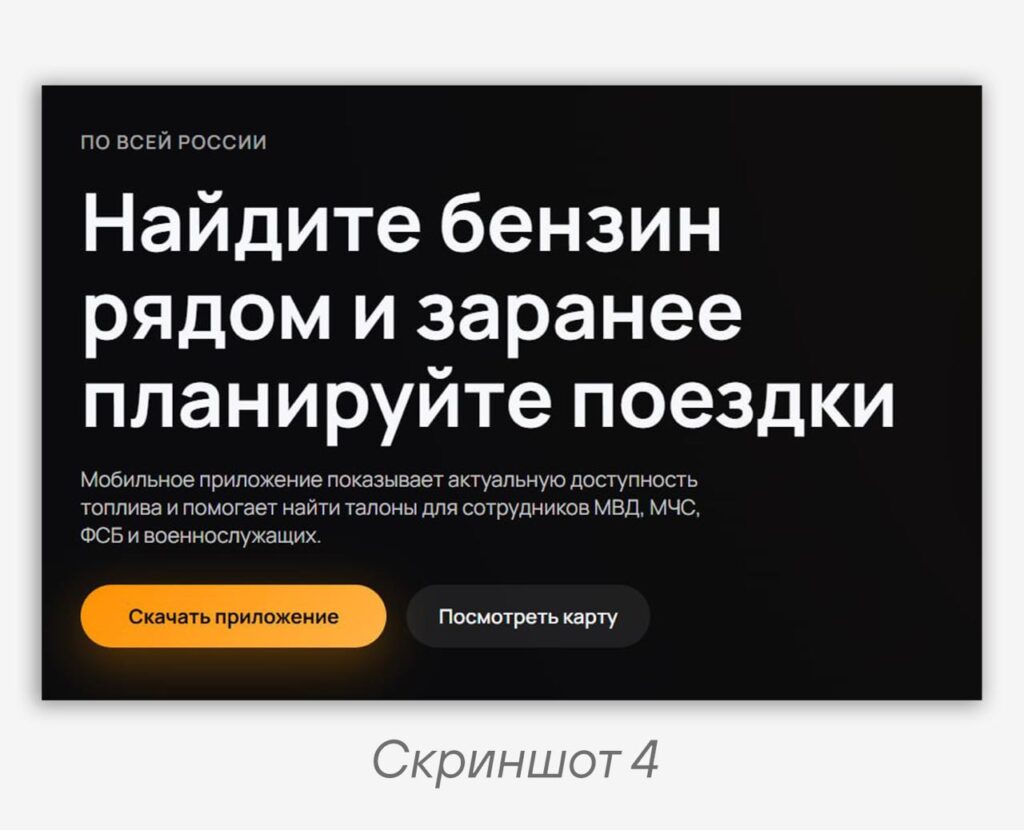
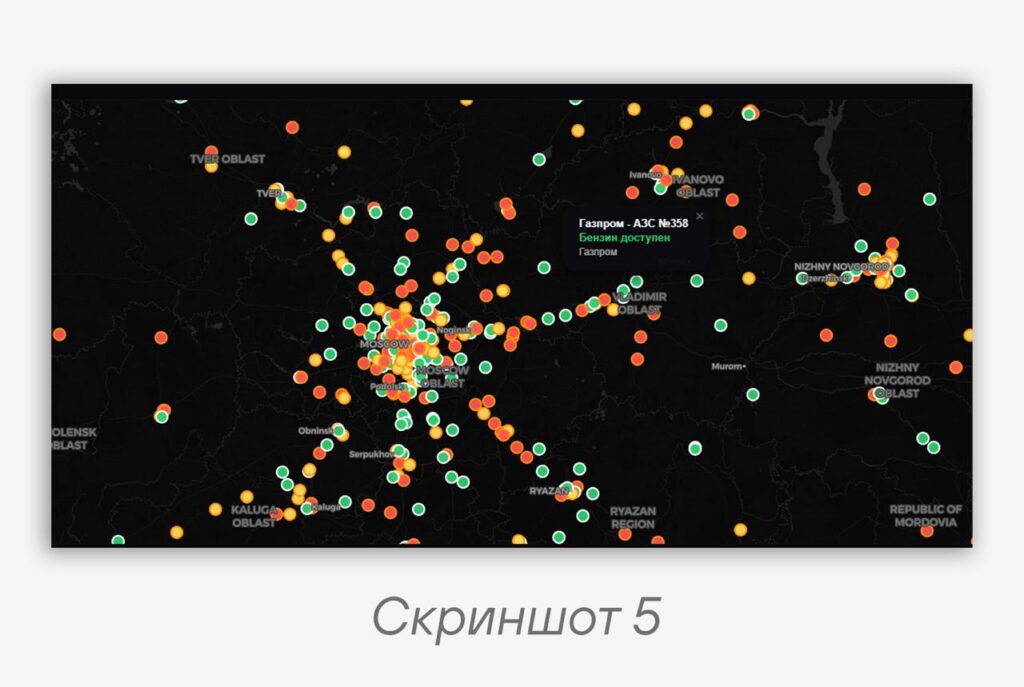
0️⃣2️⃣ The second campaign lures users with “up-to-date” data on fuel availability, offering to download an APK file (screenshots 3 and 4). The malicious website displays a map with information about fuel availability at various gas stations across the country (screenshot 5). The status of a gas station on the map is determined by a deterministic algorithm based on its coordinates:
const deterministicStatus = (station) => {
  const base = Number(station.id ?? station.lat * 1000 + station.lon * 1000);
  const pseudo = Math.abs(Math.sin(base)) % 1;
  if (pseudo < 0.58) return 'green';
  if (pseudo < 0.85) return 'yellow';
  return 'red';
};
Under the hood of the application is an infostealer, whose functions include collecting photos and the current geolocation from the device with subsequent sending to S3 storage, which can later be used to blackmail the victim and for other purposes.
⚠️ Recommendations:
• Do not share with third parties and do not enter on third-party resources any codes that arrive on your devices.
• Do not install unfamiliar mobile applications, and if you really want to — at least first use analysis through a sandbox (for example, in PT Sandbox 😉).
• Treat any resource found on the internet critically, especially if it exploits a “hot” topic.
• Buy an electric train.
IoCs:
ru-lukoil.online
tes-td.site
voentoplivo.site
gdebenzin.org
sverdlova.online
mobilecash.club

https://s3.eu-central-003.backblazeb2.com/centbrinben/benzin/
https://storage.tacticlib.com/uploads/benzin/

b192114cc04b872095015bcb0d7f708c34680eafbd43ff5393df791ea0dc04e9
140ecec54f6249370cec2f6dc0e5f485af359295bb27f6f458c5b3cf30260e3e
462611f6f8e65229e8b729038438785d447bc4da386a74fafae095b65578525c
51e18c21203e930ab3ca13327dc7d67a404e597fcf3a99f8901fdbfb169da63c
81a623c9a3b3f4a9340dd4c6bdfb5299f247b54f81ae1d39671afcf24229859a
f4102ea1718653528c503dcaaef3a2ea05ddaf6ad782e84ee7d7b2e6b073ffae
15174043fc56ca9fd8c47d2bfc0e0a2f491a17a8805afcc5eb58b8252677ef69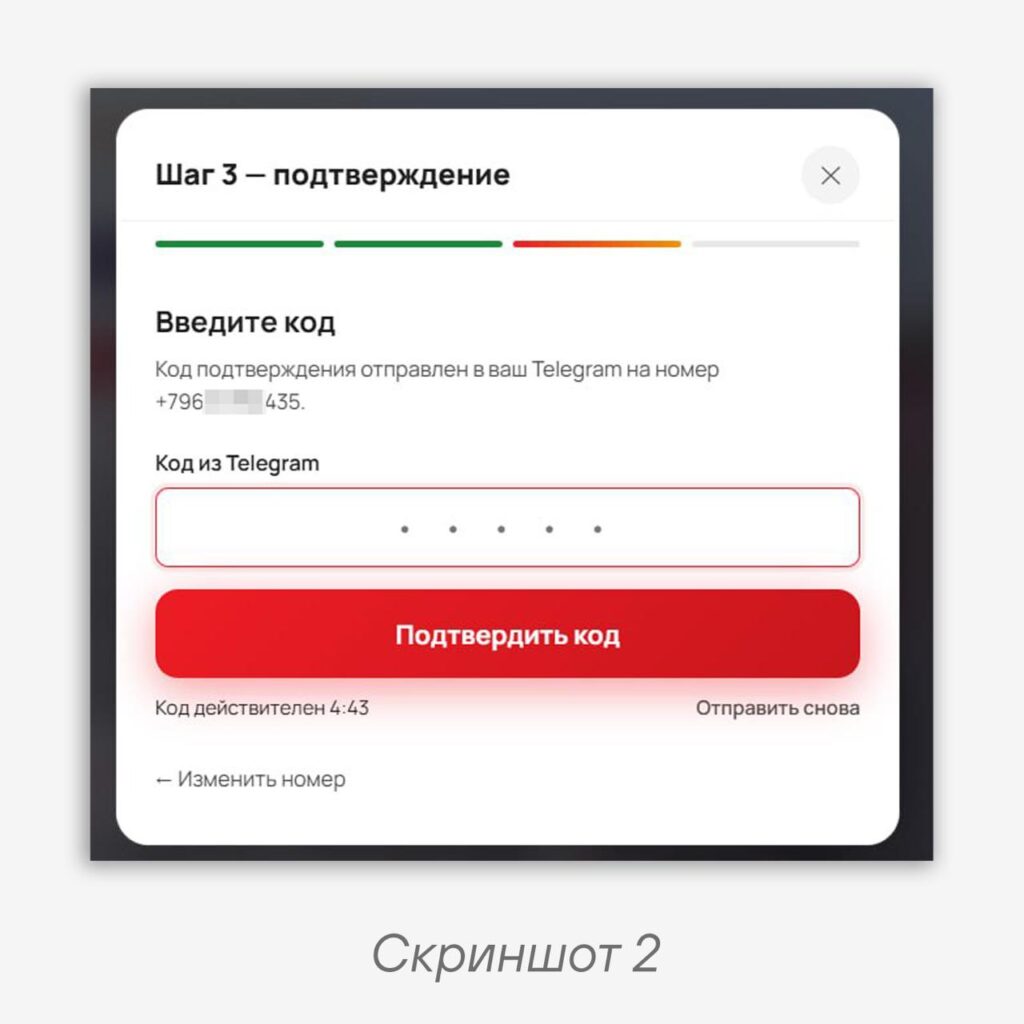
#TI #phishing #malware #ioc
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…