
APT31 grouping tool. CloudyLoader
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




In one of the incidents, the PT ESC IR team encountered an interesting malicious file that loads a payload in several stages. The malicious sample consists of a legitimate component file
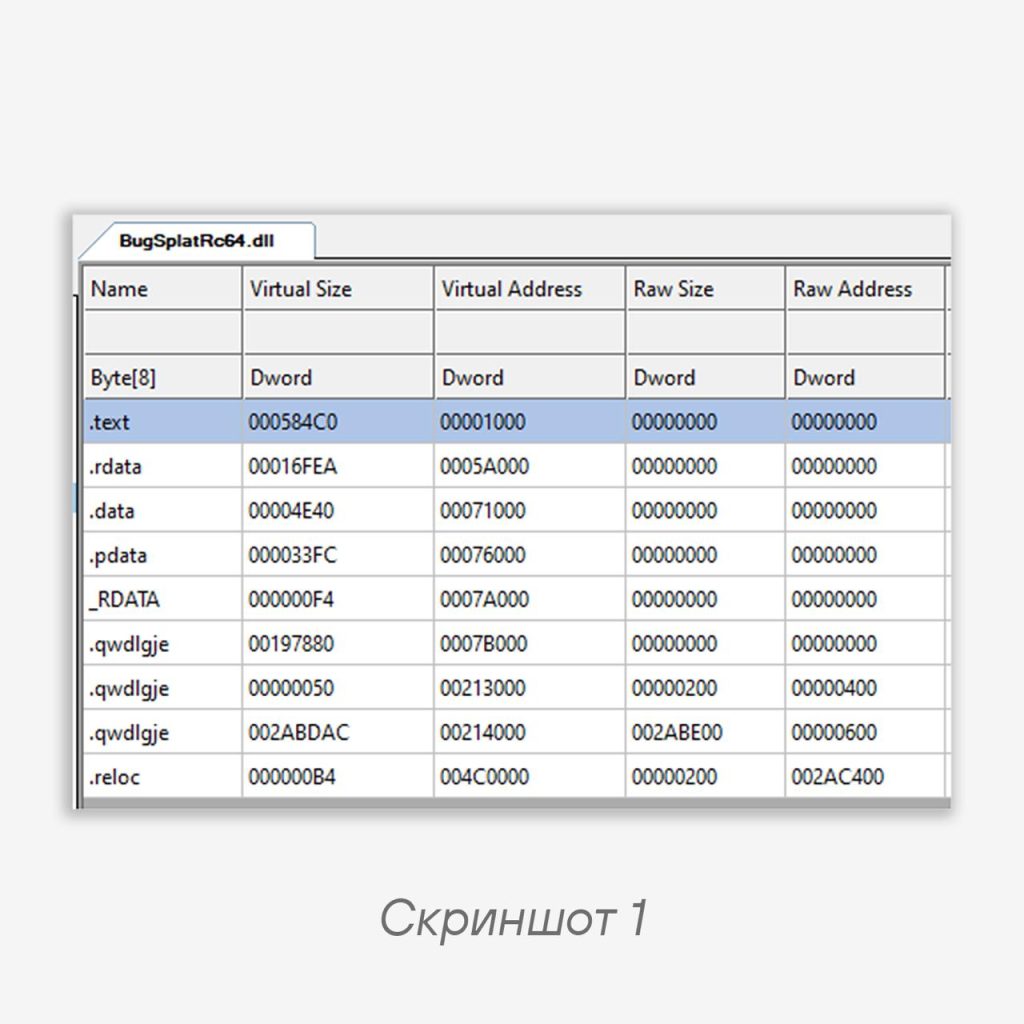
BsSndRpt.exe from the BugSplat software, which is a system for collecting and analyzing error reports, a dynamic library BugSplatRc64.dll, and a payload file (shellcode). For the legitimate file to work properly, BugSplatRc64.dll is required, which is the loader.The malicious dynamic library is wrapped with the VmProtect version 3 protector, and the section name has been changed to
.qwdlgje (screenshot 1). To hide Windows API calls, the malware uses the API Hashing technique: a hash is calculated to find the function name and DLL name. The hashing algorithm is as follows:def CalculateAPIHash(data: bytes):
v3 = 0xFFFFFFFF
for byte in data:
temp1 = (2 * byte) ^ ((2 * byte) ^ (byte >> 1)) & 0x55555555
v4 = temp1 >> 2
v5 = 4 * temp1
temp2 = v5 ^ (v5 ^ v4) & 0x33333333
v6 = ((temp2 >> 4) | (16 * (temp2 & 0xFF0F0F0F))) & 0xFFFFFFFF
v8 = int.from_bytes(v6.to_bytes(4, 'little'), 'big')
for _ in range(8):
if (v3 ^ v8) & 0x80000000:
v3 ^= 0xC520DEC7
v3 = (v3 * 2) & 0xFFFFFFFF
v8 = (v8 * 2) & 0xFFFFFFFF
v9 = (~v3) & 0xFFFFFFFF
v10 = (4 * ((2 * v9) ^ ((2 * v9) ^ (v9 >> 1)) & 0x55555555)) & 0xFFFFFFFF
v11 = (v10 ^ (v10 ^ (((2 * v9) ^ ((2 * v9) ^ (v9 >> 1)) & 0x55555555) >> 2)) & 0x33333333) & 0xffffffff
v11 = ((16 * v11) ^ ((16 * v11) ^ (v11 >> 4)) & 0xF0F0F0F) & 0xffffffff
return int.from_bytes(v11.to_bytes(4, 'little'), 'big')
Code language: Python (python)When calculating the hash value, DLL names must be supplied as input in uppercase (for example,
KERNEL32.DLL), while function names remain unchanged. After all the preparations,
BugSplatRc64.dll creates a makecab.exe process, and the payload file, which is shellcode, is decrypted using an XOR operation with the key 5d 72 89 80. All strings used in the DLL are XOR-encrypted.Stages of obtaining the main payload
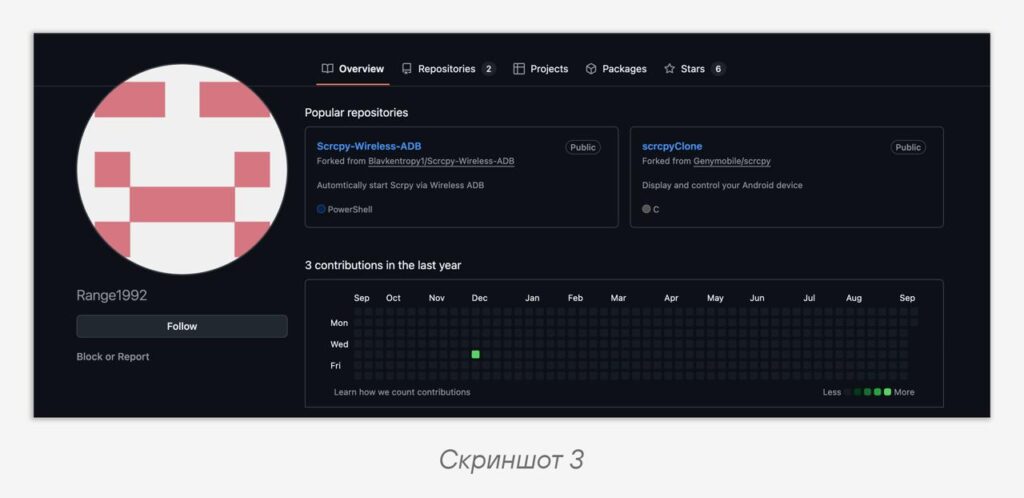
1. Request to the scrcpyClone repository of user Range1992:
https://raw.githubusercontent.com/Range1992/scrcpyClone/refs/heads/master/app/data/zsh-completion/_scrcpy (screenshots 2, 3). In the data received from Git, the malicious code looks for the start marker (QQNSR4u) and end marker (ZsNpk7Y) of the encoded string. It then extracts the data between the markers, decodes it from Base64 format, and decrypts it using the RC4 algorithm with the key 03 07 A0 B0 E3 80 88 77. The resulting data is the address of the main payload.2. Request to the address:
https://github.com/Range1992/scrcpyClone/raw/refs/heads/master/app/deps/PersonalizationCSP. The encrypted main payload contains the following data:• RC4 key — 8 bytes;
• payload length — 4 bytes;
• payload.
The main payload is CobaltStrike shellcode with the following configuration:
BeaconType                  - HTTPS
Port                        - 443
SleepTime                   - 77665
MaxGetSize                  - 409721416
Jitter                      - 46
PublicKey_MD5               - fe7aa97fbe3fe21e59ead1792ca2dc58
C2Server                    - Moeodincovo.com,/divide/mail/SUVVJRQO8QRC,www.Moeodincovo.com,/divide/mail/SUVVJRQO8QRC
UserAgent                   - Mozilla/5.0 (Windows NT 6.0; WOW64; rv:56.0) Gecko/20100101 Firefox/56.0
HttpPostUri                 - /Terminate/v6.49/LTKAZNE9
Code language: plaintext (plaintext)
An indicator of the presence of this malware may be the presence in the file system of an unsigned DLL library named
BugSplatRc64.dll.IoCs:
https://raw.githubusercontent.com/Range1992/scrcpyClone/refs/heads/master/app/data/zsh-completion/_scrcpy
https://github.com/Range1992/scrcpyClone/raw/refs/heads/master/app/deps/PersonalizationCSP
https://Moeodincovo.com/divide/mail/SUVVJRQO8QRC
3356a7d25096e24afe3409540a06f42b2b5012e55a8cad3f6ee06ec13e3471a5
879949e6d70f2d7e21c489552240b13f927fa9586ef7a9343fa07741248860f3
Code language: YAML (yaml)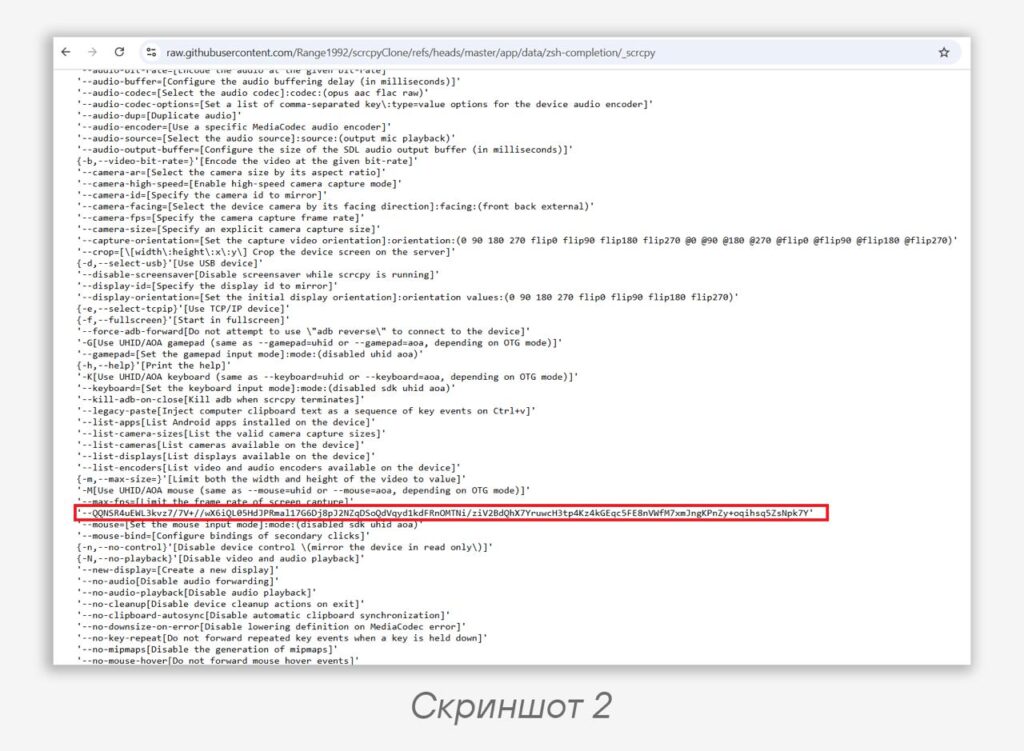
#dfir #ti #apt #reverse #malware
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…



More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…