
Big Browser is watching you
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




The cyber intelligence group has recorded a new campaign using an updated stealer Unicorn, which began in mid-February and continues to this day. The targets of the attacks are the public sector, and they are being carried out by a previously unidentified hacker group.
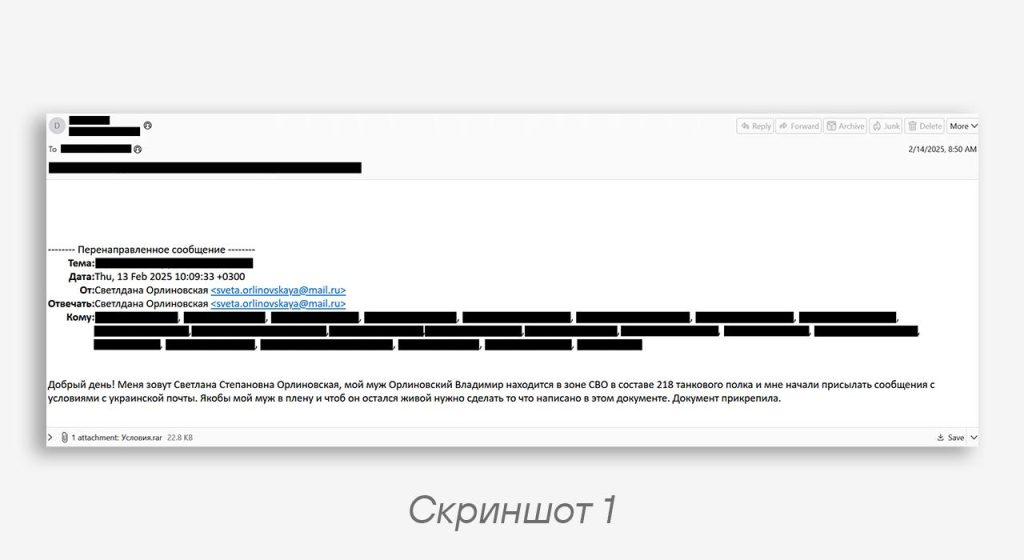
The attackers send phishing emails with a topic related to the Special Military Operation, containing attached archives with a malicious HTA file (screenshot 1). This file contains obfuscated code and has a name matching the subject of the email. When opened, a decoy document is launched (screenshot 2), along with malicious code (via the
window_OnLoad event). The malware attempts to mimic Yandex Browser. The malicious script creates VBA files at the path
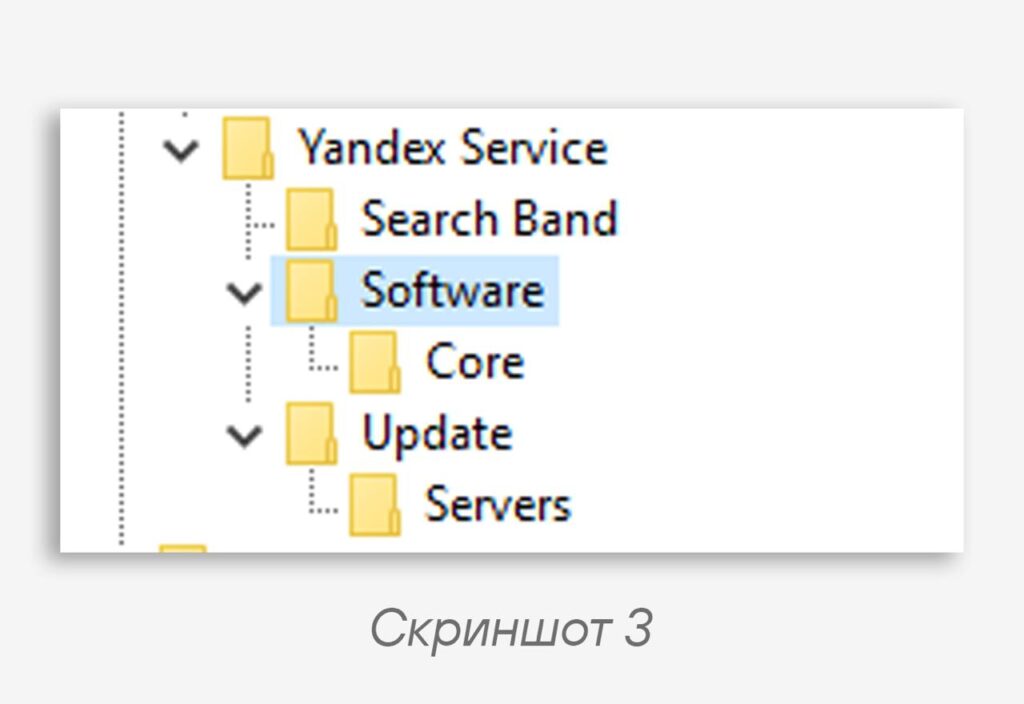
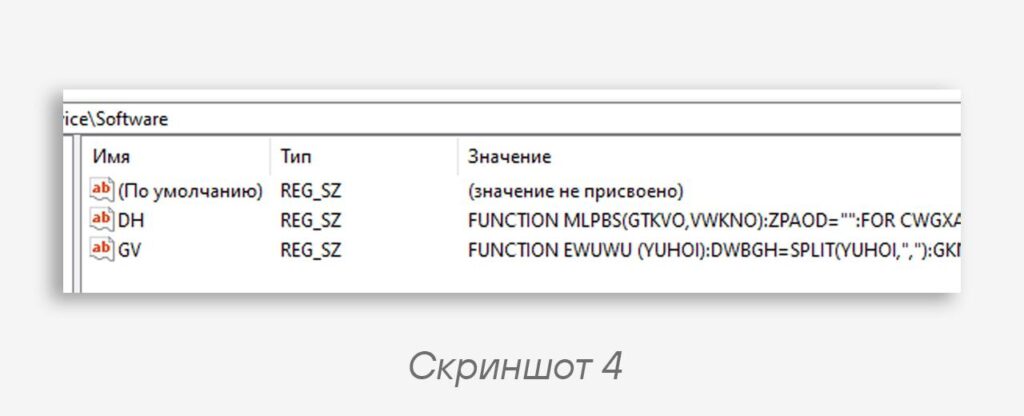
%USERPROFILE%\AppData\Local\YandexUpdate, adds the payload to the registry HKCU\Software\YandexUpdate (screenshots 3, 4), registers VBA files in autorun via the registry HKCU\Software\Microsoft\Windows\CurrentVersion\Run, and also registers tasks in the scheduler using schtasks. 🔤 Initially, the attackers used three scripts:
•
log01.vbs — traverses user directories, analyzes the contents of specific folders, and saves files with specified extensions (.pdf, .txt, .doc, .docx, .rtf, .odt, .xls, .xlsx, .ods, .csv, .jpg, .png, .zip, .rar). •
log02.vbs — steals credentials from Telegram and browsers (from Chrome, Edge, Opera, Yandex Browser). •
log03.vbs — transmits the collected data to the command server. 👾 In recent attacks, the group modified and expanded the malware’s functionality:
• In
crash_report.vbs (formerly log01.vbs), the list of file extensions for collection has been expanded (.vsdx, .vdx, .7z, .tar, .jpeg, .cdr, .kmz, .kml, .aqe). Importantly, the extensions .kml and .kmz, used in military topography, were added.• Using
service_report.vba, the attackers attempted to obtain a list of all flash drives, but the script turned out to be non-functional. • A self-defense mechanism was added:
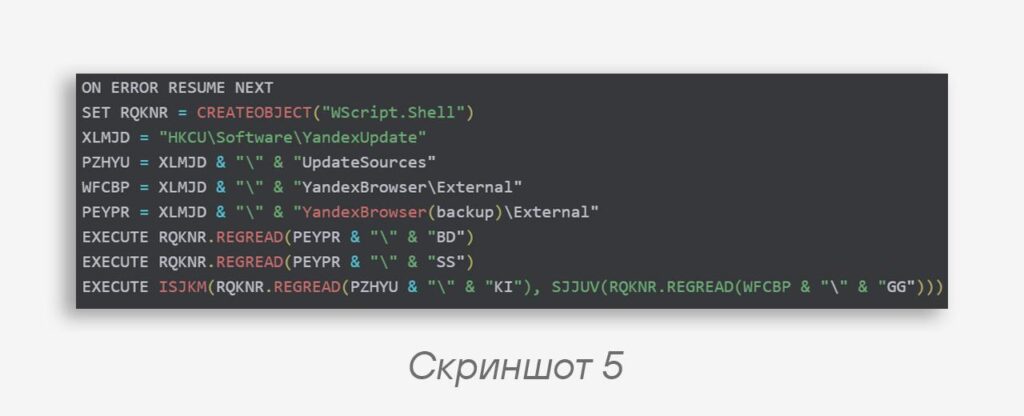
update_logging.vbs restores deleted malicious files by loading their contents from the registry. ⚠️ It is important to note that the VBA scripts are not detected by antivirus solutions, as they read values from the registry and execute malicious code directly. This complicates the detection process (screenshot 5).
Analysis of the attack indicates the evolution of the attackers’ methodology. Additionally, it is worth noting that the group shows interest in extensions related to cartography. This may indicate a specific target or a strategic interest in this area.
IoCs
Domain
vm-tiktok.org

Hash sums
096c340e9a20476a191721e6eaeedcc2
0debff602f2912127c562839c7fcd3d7
e25042fba726356d7e88efe0608a4e36
290a4cff70029ca2a0095a3e3a8b19e7
65ef77db51277a046f76f21a59dee9e0
80bc350629a1ba59b2a19b9029feece5
d0f9fadbf157a8236b88cfc03f17a811
4feaa6c50348641799a8f56e76cd52e7
Code language: plaintext (plaintext)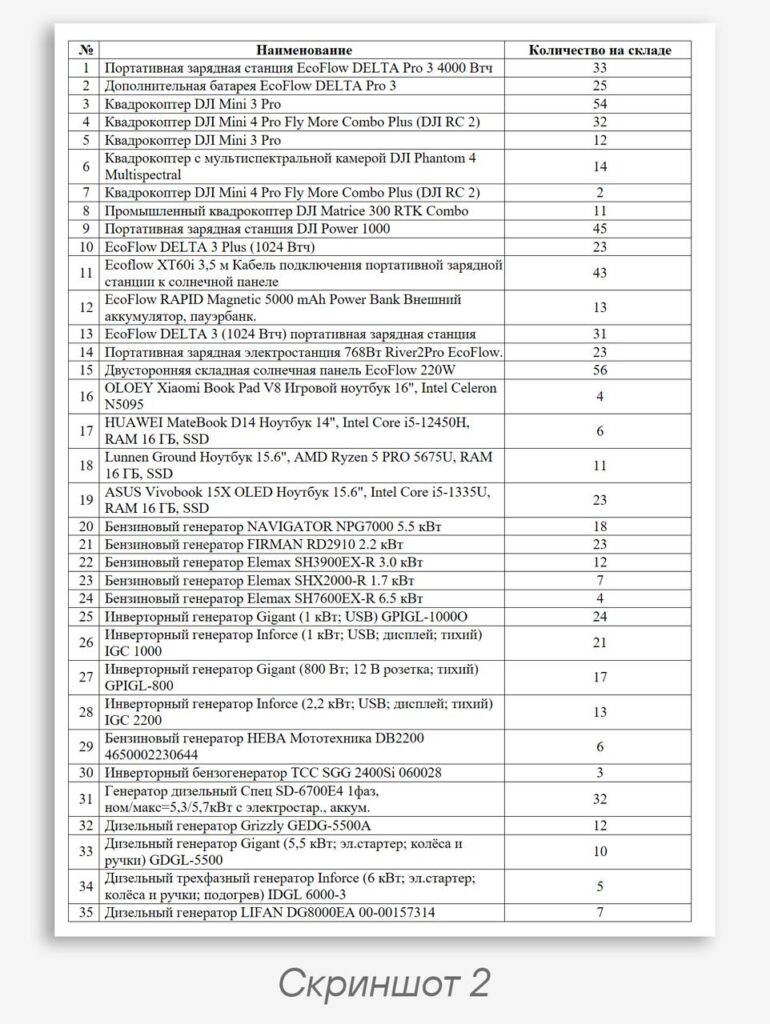
#TI #APT #Malware #Phishing
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…