
Colonels write first!
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




The collection of malicious mass mailings sent in the name of law enforcement agencies has a new addition.
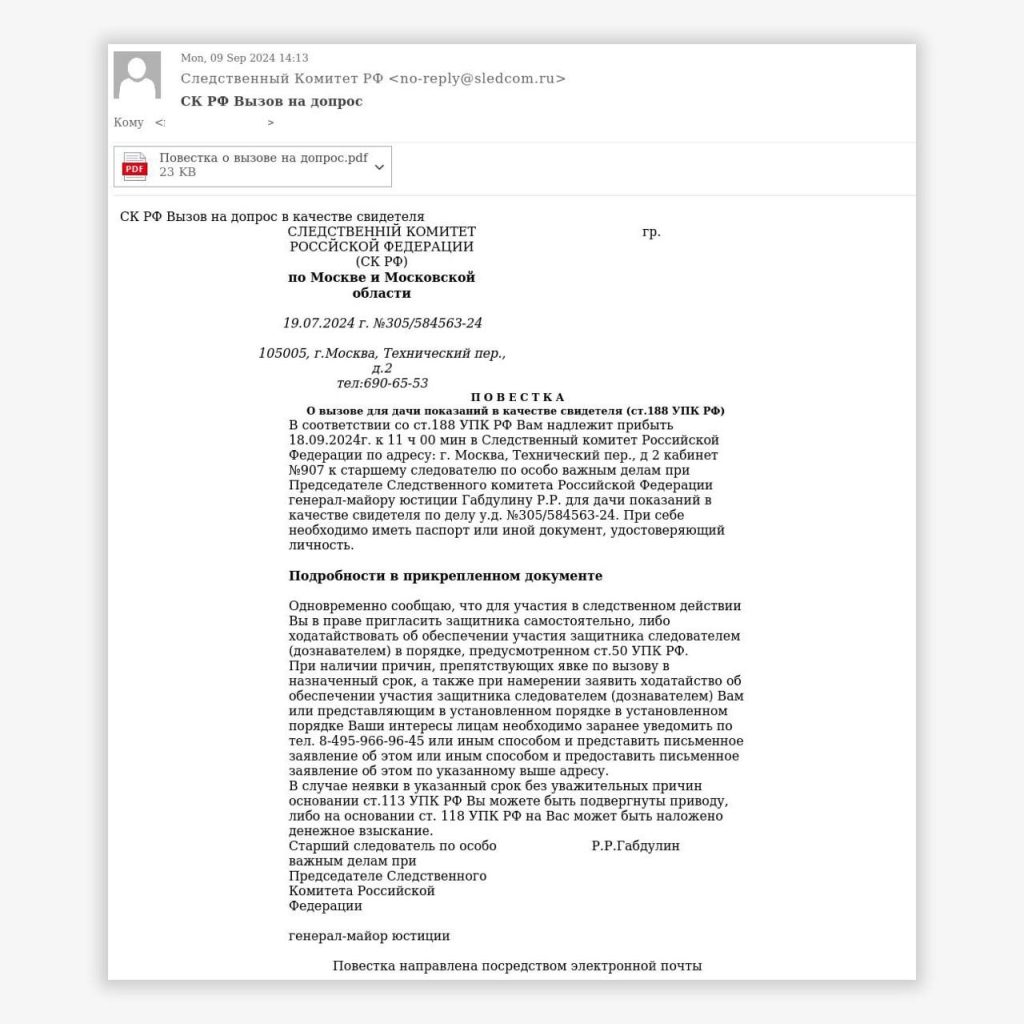
In September, several recipients received a letter from the “Investigative Committee” with a summons to appear for questioning as a witness in a criminal case (screenshot 1).
The summons itself is a PDF document that, when you try to open it, sadly states that its contents cannot be viewed and that you need to download the Adobe Font Package in order for the data to display correctly (screenshot 2).
🔗 The link leads to the domain
adobe.updatedownloader.com, from which, if accessed from a Russian IP address, a file is indeed downloaded with the name:
adobe_PDF_reader_fonts_update_24.2.5_Win_x86-64.exe (bea1dfdae82c67aac7a262c25dffadc0190270e2412db0c051da9ffab8e3a157)
Code language: plaintext (plaintext)
Unfortunately, the file is Medusa Stealer, so it will not be possible to read the document after all…
🧐 If you look closely at the letter, you can notice Easter eggs — and expose the attackers:
• The sender field specifies
noreply@sledcom.ru — this is a legitimate email address of the government agency, however, the letter does not contain a DKIM signature that would allow verifying the authenticity of the sender.• The letter was sent from an IP address that does not belong to the organization in whose name the summons allegedly arrived.
• “
СЛЕДСТВЕННIЙ КОМИТЕТ” in the header of the letter.IOCs
Net:
updatedownloader.com
62.197.48.140
5.42.73.251
Code language: plaintext (plaintext)
Files:
bea1dfdae82c67aac7a262c25dffadc0190270e2412db0c051da9ffab8e3a157
7fa0642a96e8e9a796a4dba55877d1c730c64f257956872c3f6d405417e30024
Code language: plaintext (plaintext)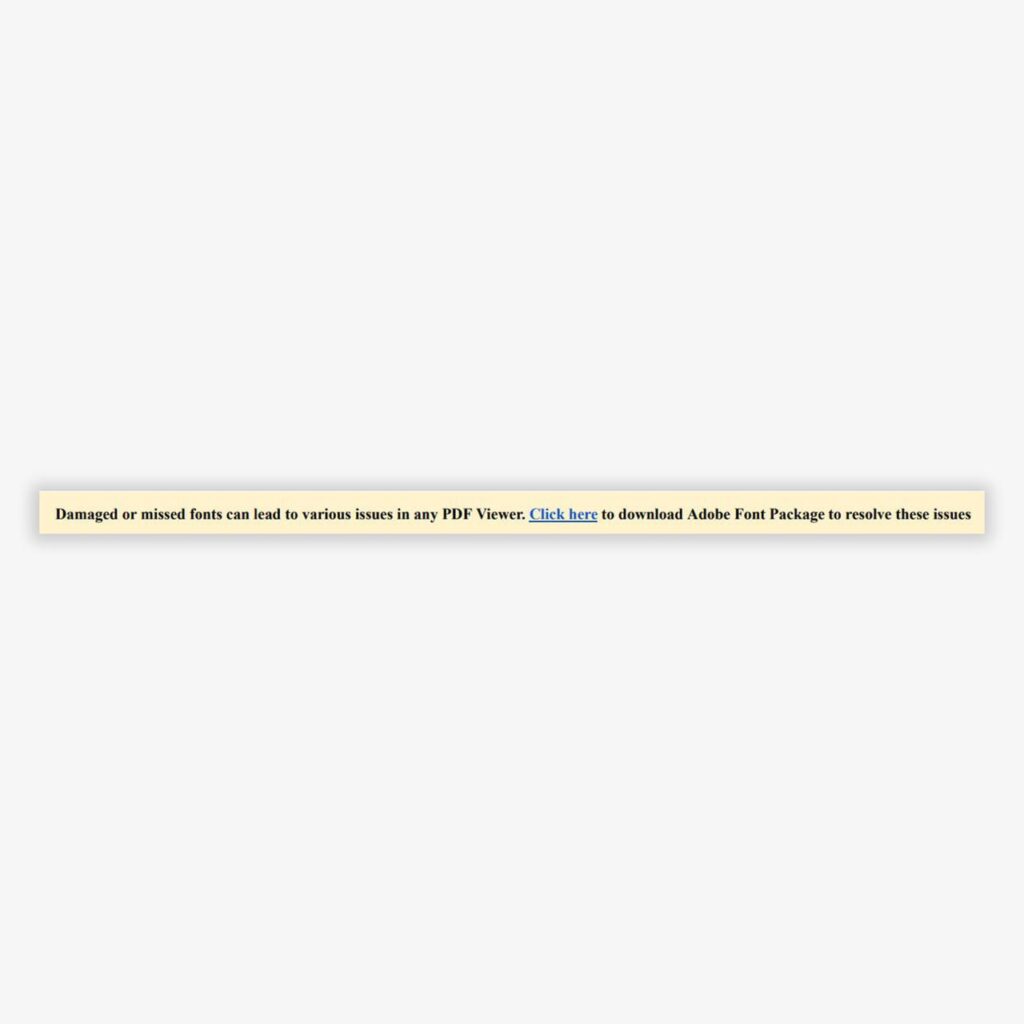
#ti #phishing #ioc
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…