
Hush, hush: a new campaign against the CIS countries
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




%APPDATA% directory under the following names:
• ebook-edit.exe — a legitimate executable file associated with the Calibre e-book editor;
• Calibre-Launcher.dll — a malicious library that decrypts and launches the payload;
• edit2.hlp — the encrypted payload.
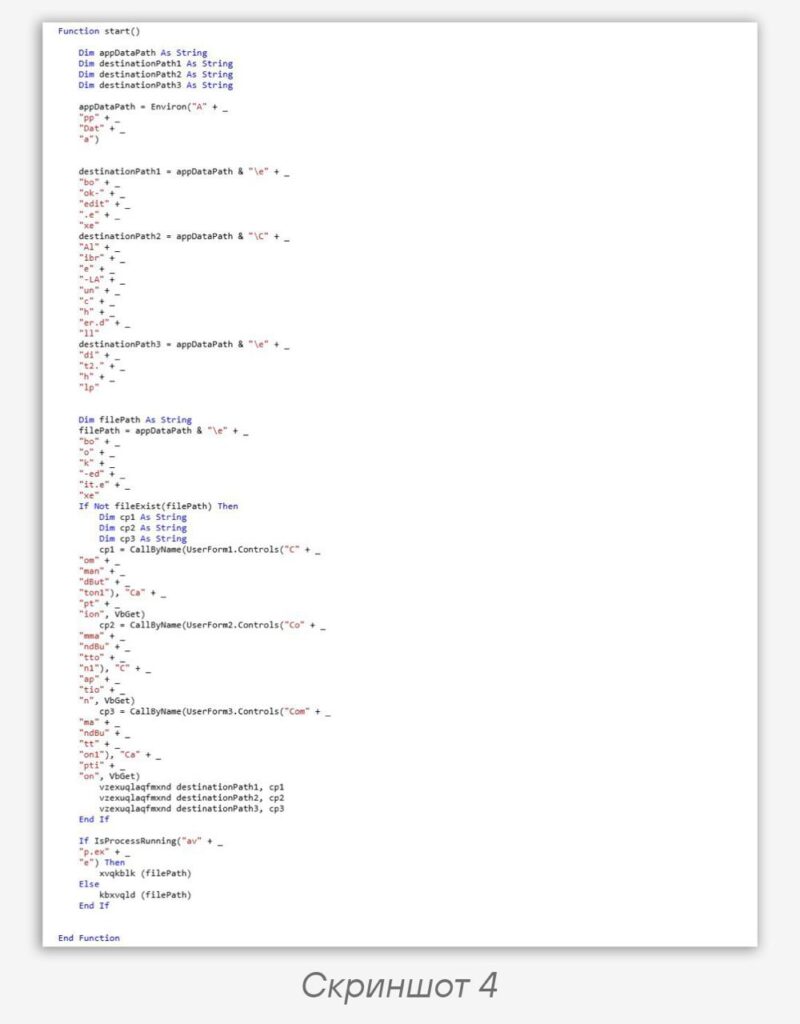
📨 Variants of this mailing included resources additionally encrypted with single-byte XOR. The malicious macros also contained a check for the presence of a running antivirus process avp.exe. If antivirus was present, the process was launched with a visible window; otherwise, it ran in hidden mode (screenshot 4).
The primary role of Calibre-Launcher.dll is to decrypt and launch the next stage of the malicious chain, the contents of which are stored in the edit2.hlp file and encrypted using the RC4 algorithm. The decrypted payload begins by executing shellcode that restores the wiped MZ and PE signatures, as well as correcting the DOS header offsets. After that, control is transferred to the entry point of the restored PE file, where the agent’s core logic begins.
💡 It is worth noting that the loader checks whether system delays have been tampered with. To do this, an auxiliary thread is created with a delayed event signal. The main thread waits for it with a short timeout. If the expected event is signaled, this means something is wrong, and execution is terminated.
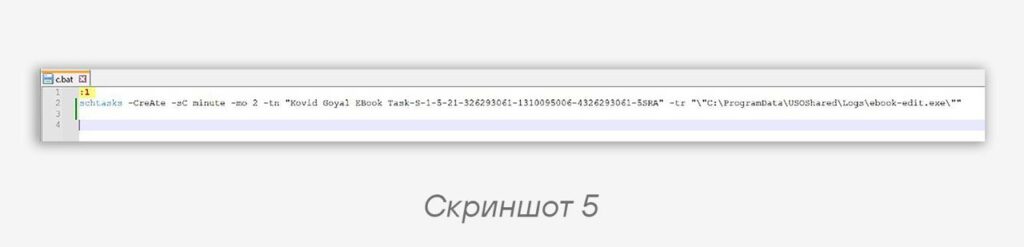
The final module, which we named SilentNode, upon launch establishes persistence in the system by moving itself and related components (ebook-edit.exe, Calibre-Launcher.dll, and edit2.hlp) to the C:\ProgramData\USOShared\Logs directory, and then, via a temporary script %TEMP%\c.bat, creates a scheduled task (screenshot 5) that ensures the payload is launched every two minutes. After completing the persistence process, the current instance terminates and is subsequently restarted within the context of the created task.
🔄 After a reboot, execution proceeds to network communication with the command-and-control server — basic system information is compiled: operating system version, computer and user name, as well as information about network interfaces. The resulting response is then packed into a binary container with the addition of a system identifier. The data is encoded using a non-standard Base64 variant and encrypted with the ChaCha20 algorithm. Subsequently, the agent in a cyclic mode, with random pauses of up to one minute, sends the prepared messages to the C2 server using HTTP POST requests and waits for a response. Notably, all analyzed samples used the same endpoint /Search/v<№>.
SilentNode is essentially a loader, and its primary functionality boils down to periodically polling the C2 server, reflectively loading, and subsequently executing PE modules received from the C2 in memory.
IoCs
DOCS
391f30807d3cf333cdc286d1ff5b0f58
0287ba0ecc176ae63ea1d1e053654f32
3eb0b0811c0ab9e87e2ee7f7bac7c46a
22573d874ac9ffa785e57d94e243b48d
f6b126c83ea4a63f277199d7c06617d6
b44a3229ab54f7367ee2acd678bec2d5Code language: plaintext (plaintext)4395e8e7351de03faac54492ee2bc874
1100e1d599b5e4f87082670673c8abfb
84533ef6651f38fe162ad2753f1ad788
15c839292684ac6374633d231dbd76a7
e0b008ea6eef411ed6f9faab8f1d3bee
7b00beb5a7ef4a142ebcdcc052b312a3Code language: plaintext (plaintext)022287b05e4c5ba5503f2b798219f5e9
17134fe1344744cf99a93483f6859212
77dc27fb2ed18f3977241e9475097746
86a164a403a94c8ccd4f0ba383fa943c
906e49f334041ebccc071985ecdcf2ba
5e7b3664311b2daa9ee040b3cff4d82fCode language: plaintext (plaintext)www.mubrn.com
188.214.39.243
www.tmtransport.org
194.14.217.146
91.132.94.58
45.153.127.226Code language: plaintext (plaintext)C:\Users\admin\AppData\Local\Temp\c.bat
C:\ProgramData\USOShared\Logs\edit2.hlp
C:\ProgramData\USOShared\Logs\CAlibre-LAuncher.dll
C:\ProgramData\USOShared\Logs\ebook-edit.exeCode language: YAML (yaml)
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…