
Move like water. Be still like a mirror. Respond like an echo...
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Move like water. Be still like a mirror. Respond like an echo… 🪞
In this post, we will discuss a discovered instance of a phishing page. It is notable for employing techniques to counter automated and manual analysis, and its code contains Easter eggs.
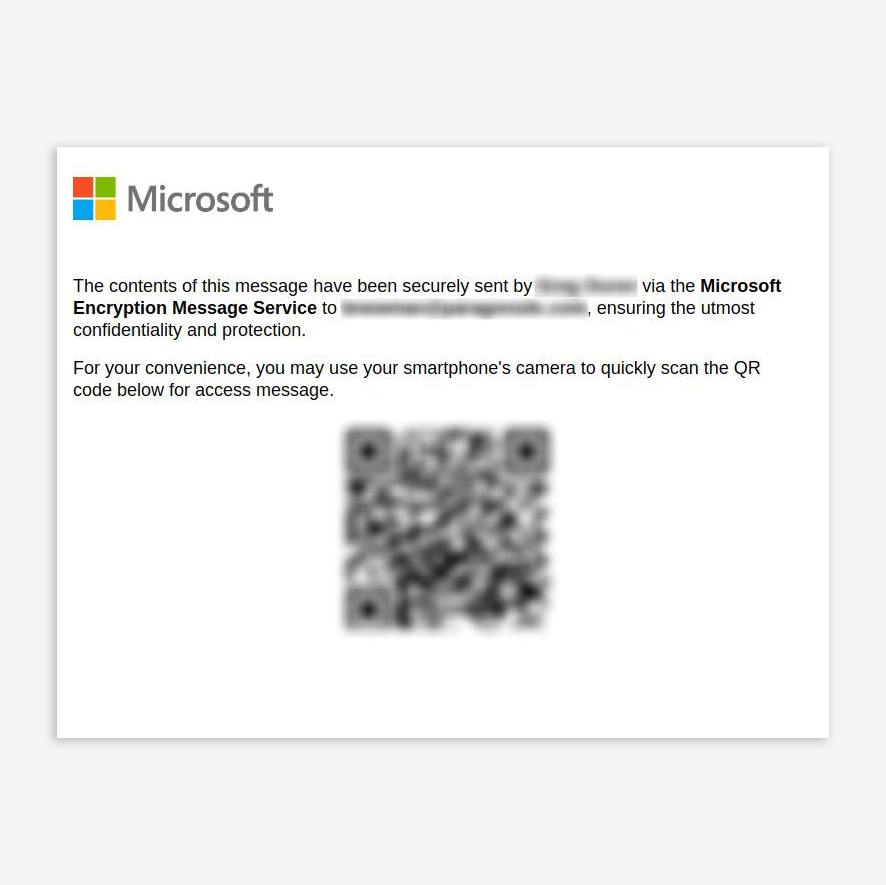
Having taken out your smartphone and followed the link. The attack begins with a phishing email in which the URL link is embedded as a QR code (visible in the screenshot). Following the link triggers the execution of JavaScript code, which checks fictitious conditions and loads another HTML code via document.write().
The content of the HTML code is decoded through a combination of atob (Base64 decoding), escape (encoding characters into HTML entities), and decodeURIComponent (decoding from percent-encoding). We have previously discussed a similar technique using a combination of (de)codings to load a page in one of our previous posts.
document.write(decodeURIComponent(unescape(atob('PCFET0NUWVBFIGh0bWw+CjxodG1sPgo8aGVhZD4KICAgIDxsaW5rIHJlbD0iaWNvbiIgaHJlZj0iaHR0cHM6Ly9kZXZlbG9wZXJzLmNsb3VkZmxhcmUuY29tL2Zhdmljb24ucG5nIiB0eXBlPSJpbWFnZS94LWljb24iPgogICAgPG1ldGEgaHR0cC1lcXVpdj0iWC1VQS1Db21wYXRpYmxlIiBjb250ZW50PSJJRT1FZGdlLGNocm9tZT0xIj4KICAgIDxt...🧐 An interesting find in the loaded HTML page was the presence of the function below. When analyzing the JavaScript code in an interpreter or via browser developer tools, the function triggers the debugger and pauses code execution; however, it does not execute during normal page loading in the browser.
Thus, by wrapping the debugger invocation in two performance methods and calculating the execution time of this code section, the function decides to redirect to a legitimate page if this time exceeds 100 milliseconds — a built-in anti-debugger on the phishing page against manual code analysis.
(function zjXTcdfpRH() {
    let TUUFRqHXUc = false;
    const lPOfbBRoMU = 100;
    setInterval(function() {
        const nzBpzARgyq = performance.now();
        debugger;
        const Mhaorlnpom = performance.now();
        if (Mhaorlnpom - nzBpzARgyq > lPOfbBRoMU && !TUUFRqHXUc) {
            TIxhHrwbpI = true;
            TUUFRqHXUc = true;
            window.location.replace('https://www.walmart.com');
        }
    }, 100);
})();
We were only separated from the actual password collection form by the launch of Cloudflare Turnstile — a frequent guest on phishing pages to counter content retrieval by automated means such as web crawlers.
Tips 🧞
• When examining the code of phishing pages, various techniques for countering manual and automated analysis can be discovered. Even if tools or security measures cannot bypass these techniques, simplifying detection rules can help protect users from threats.
• The phrase found at the beginning of the phishing page code — “The successful warrior is the average man, with laser-like focus © Bruce Lee” — should remind all researchers of the importance of persistence and concentration in combating phishing threats and acquiring new knowledge.
#TI #phishing #tips
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…