
Drama around PyPI: 🪰⮕🐘?
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




The official statement says that a wave of spam came from inbox.ru mailboxes — users with such email created 250 profiles and added over one and a half thousand projects to them, which allegedly “deceive users and pose a security threat” (leading to end-user confusion, abuse of resources, and potential security issues).The blocking of Russians in various communities is a hot topic. It was cited by other publications as well. @banksta:
Russians are being expelled from the Python programming community. They have been banned from using the PyPI repository with packages for Python. The restrictions only affected those who create a new account linked to an inboxru email and those who want to add such an email to an existing profile. The domain belongs to Mailru.@imaxairu:
Russians banned from using the PyPI repository with packages for Python The restrictions only affected those who create a new account linked to an inbox .ru email and those who want to add such an email to an existing profile The domain belongs to Mail .ru. The limits do not yet extend to other domains of the companyThe Supply Chain Security team actively collaborates with PyPI in the area of trojan detection. We decided to validate whether the actions of the repository’s administration were justified. Assessing the official statements CNews references a post on the PyPI blog published on July 15, 2025. It states that, guided by the practice of blocking spam email domains, they are closing registration of new users on the Python Package Index using email on the
inbox.ru domain.
The PyPI administration made a similar decision a year ago, on June 16, 2024, regarding the domains outlook.com and hotmail.com (owned by Microsoft) — they became a favorite solution for attackers due to the ease of mass domain registration.
It should be clarified that downloading packages does not require registration. An account is needed to publish your own projects.
PyPI provides statistics:
June 9: the first account of the campaign appeared.
June 11: 46 accounts were created in 3 hours.
June 24: 207 accounts were created in 4 hours.
From June 26 to July 7, they created 1525 projects:
2025-06-26  9
2025-06-27  295
2025-06-28  39
2025-06-29  119
2025-06-30  740
2025-07-01  249
2025-07-02  46
2025-07-10  16
2025-07-11 12Code language: plaintext (plaintext)We hope that we will be able to reverse this decision in the future when we are more confident in this email provider’s ability to prevent abuse. If you work at this provider, please write to us at security@pypi.org to discuss this decision.Let’s look into the campaign. Nature of the campaign Let’s examine the projects that published their first release during the campaign period of June 26 — July 7, capturing additional time on the left and right for clarity: from June 12 to July 15. A developer, when publishing a project, may optionally leave an email for feedback. During this interval, only 4 packages were published with an explicit email on
@inbox.ru, all legitimate.
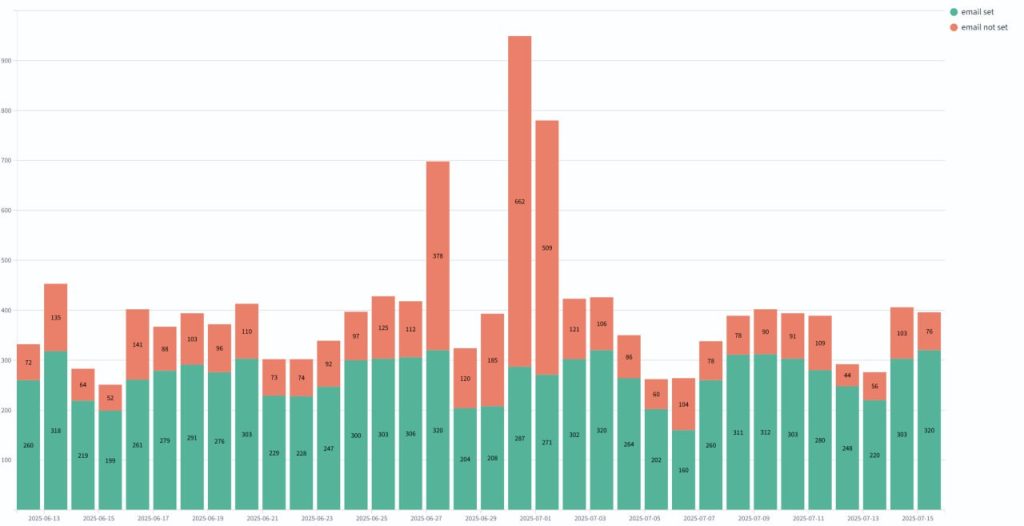
Chart 1 (see below) demonstrates whether the developer chose to provide an email in the first release of their project.
 We observe:
1. A drop in overall developer activity on weekends (two-day pits are visible, alternating with five-day workweeks).
2. Spikes in packages without email, published on June 27 (378), June 30 (662), July 1 (509).
The second observation correlates with PyPI’s statistics: on June 27, 295 packages were published on
@inbox.ru, on June 30 — 740, on July 1 — 249, adjusted for time zones.
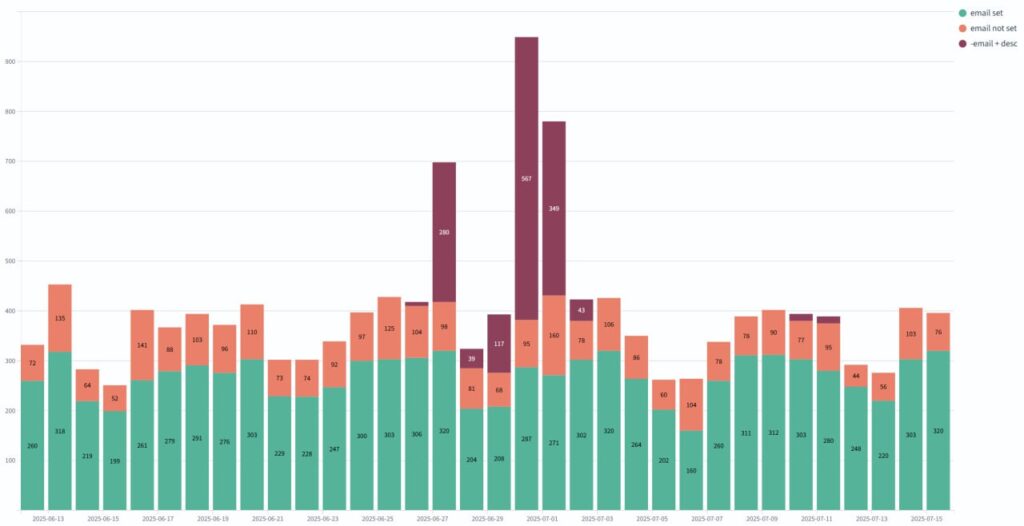
Within the activity period, there are 1403 projects without email with the same description: “Minimal package created automatically” — and version 0.0.1 (chart 2). They coincide with the period of the campaign activity that the PyPI administrators were unhappy about.
The names of the packages from this batch are clear typosquatting (an attack on the fact that a developer will make a typo in the package name during installation or fall for a good name — and install a trojan):
🟢avoid 🐱
🟢common-io
🟢win32crypt
🟢win32com
🟢pywintypes
🟢jsap
🟢webdav2
🟢arbuzmining 🍉
🟢requirements-cpu-txt
🟢requirements-cuda-txt
🟢dl-pivot-pandas
🟢steambaselib 💀
🟢catboost-spark
🟢numpynumpy
🟢antlr4-runtime
🟢celery-telegram
🟢exllama-kernels
🟢booking-api
Some of the names target developers at Russian companies:
🟢youla-spark-session 🐱
🟢ipy-kaspersky 💀
🟢vkads
🟢vkpay
🟢vkplay-sync 😺
🟢vkplay-metrics
From these names it becomes clear that the PyPI administration stopped a campaign that could have harmed our compatriots 🥺
Is blacklisting the email @inbox.ru justified?
Currently, when creating a mailbox on @inbox.ru, a phone number or VK account is required. There is a mention that two years ago it was possible to do without email. Also, you can create up to 10 anonymous mailboxes linked to your main email as part of the official functionality of mail.ru.
Probably a not insignificant role is played by the ease of automation and the simpler bypass of heuristics for suspicious actions, given that an attacker was able to manage 207 mailboxes within 4 hours.
PyPI developers who have linked an @inbox.ru email are not affected by the “repressions” — only the “users” who participated in the campaign were blocked. It is not possible to create new accounts or link these mailboxes to existing accounts.
In summary
The restriction on creating new accounts using @inbox.ru email is a natural reaction to a campaign in which a couple hundred accounts registered within a short time began to run amok.
Microsoft’s email domains also came under blocking a year ago, which further reduces the likelihood that these actions express any kind of bias.
It turned out to be open-source myth busters 👀
#ti #pypi #pyanalysis #scs
@ptescalatorMore from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…