
Proactive hunting for C2 servers
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Proactive Hunting for C2 Servers 👨💻
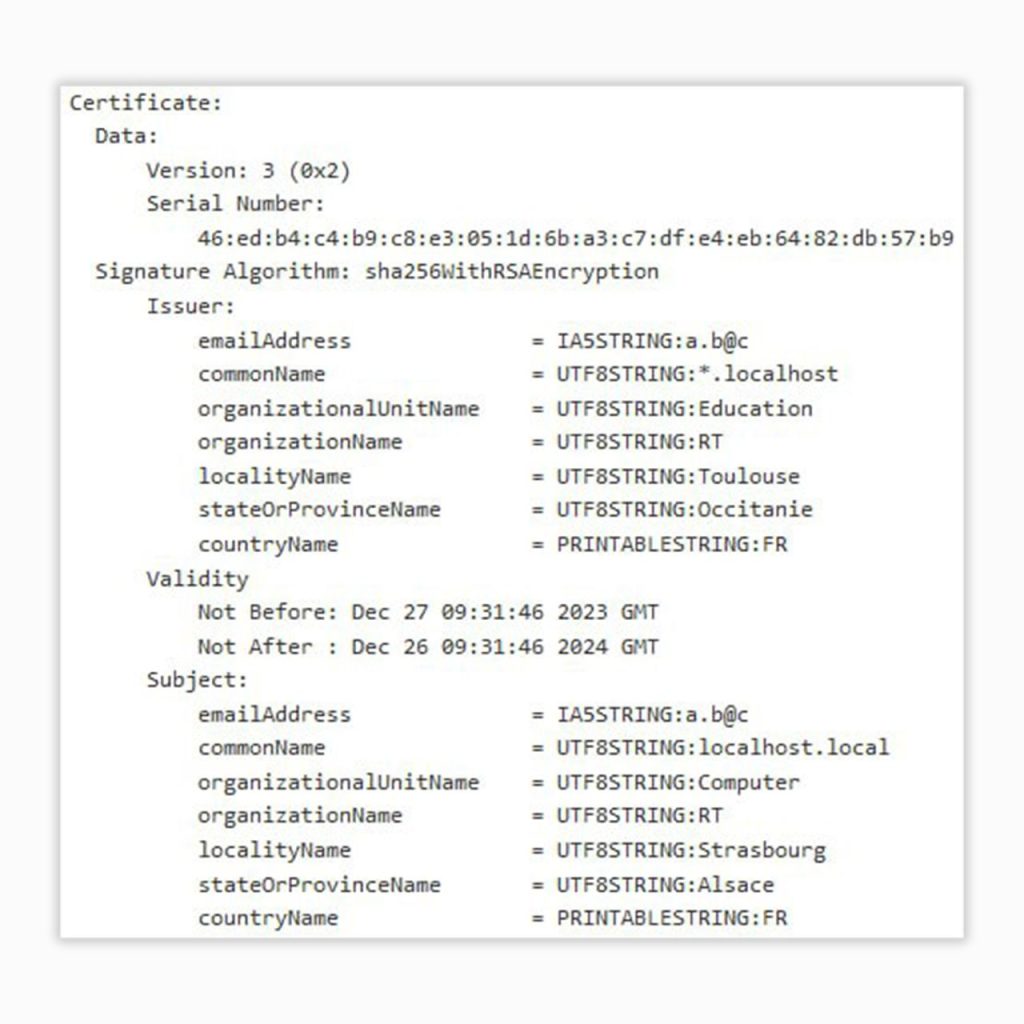
In the process of hunting for C2 servers, an important question arises — which artifacts to use for better effectiveness and accuracy: searching by WHOIS records, regular expressions for subdomains, by NS servers, DDNS, resolutions to a single IP address, etc. From this standpoint, the best option most often is the fingerprint of the SSL certificate used on the C2 server.
Thanks to monitoring the certificate fingerprint via Censys,
services.tls.certificate.fingerprint_sha256: "aea6e20b6abcf58c27eab43de08d7b1cd988fc68c471b5cdcc812851df8c8748"
Code language: YAML (yaml)
which we had previously seen on a C2 server used by GoRed in attacks on Russian organizations, a new GoRed C2 server was discovered in June of this year, along with additional network indicators.
IoC:
passwade.ru
dnslan.ru
wglan.ru
mskde.ru
mskde.online
myldap.ruCode language: plaintext (plaintext)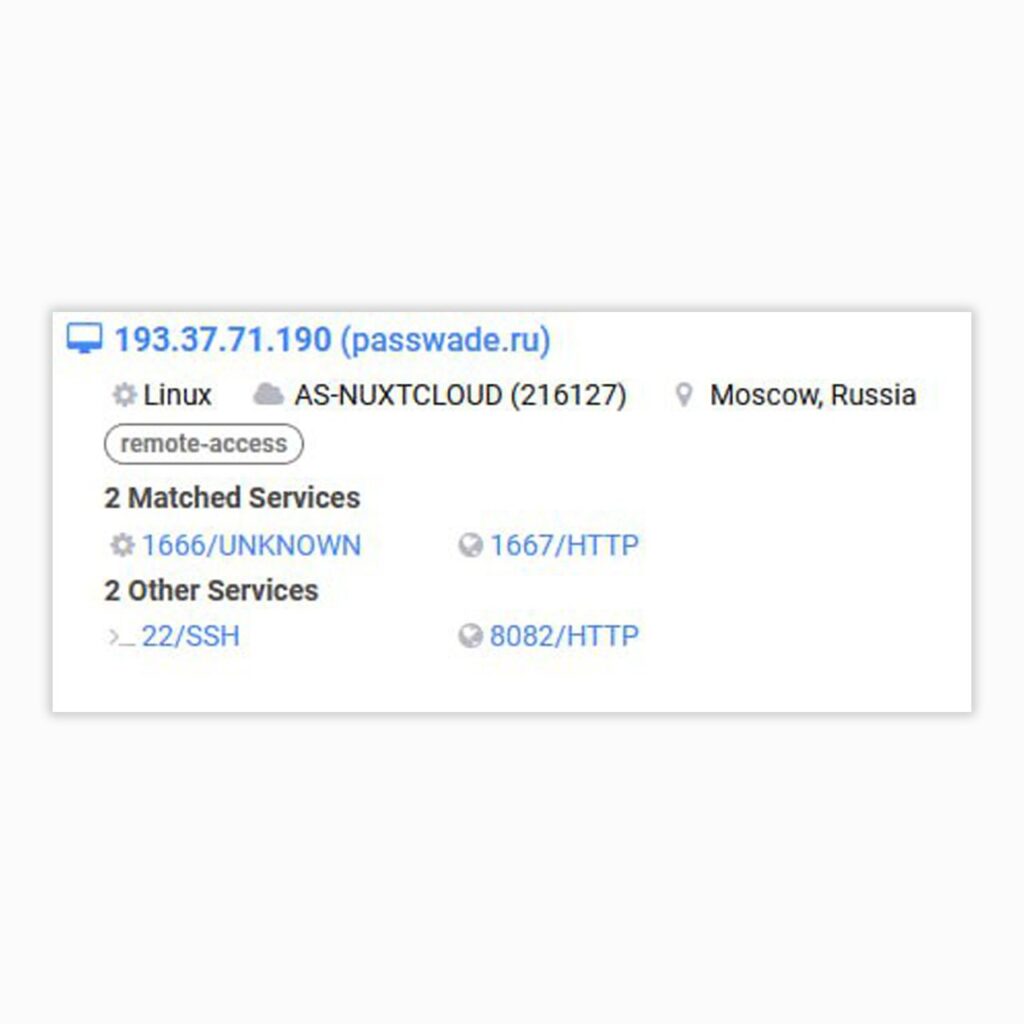
#TI #ExCobalt #GoRed #C2
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…