
Time to update.
More in General
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…




Time to update ⚠️
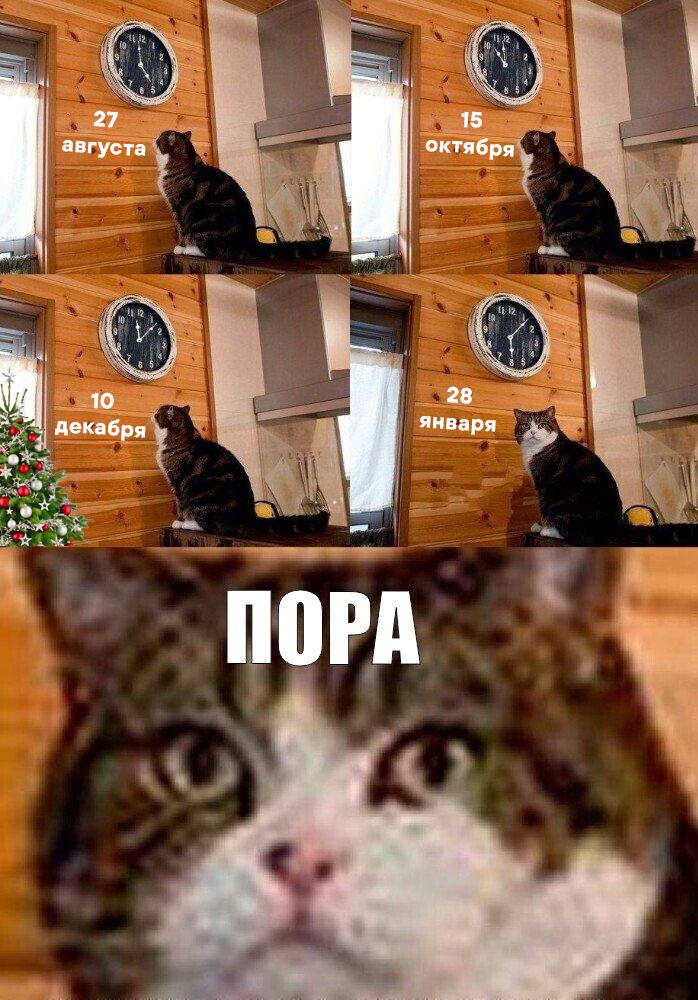
In early December we already reported how hackers infiltrate infrastructure through unpatched vulnerabilities in the TrueConf server that administrators failed to fix, vulnerabilities that became known in late August.
Now it’s the end of January, but the situation hasn’t changed — attackers are still actively exploiting this loophole. Since the start of the year, the PT ESC IR team has investigated several incidents where a TrueConf server placed on the perimeter served as the initial attack vector.
😐 Don’t do that. It’s time to remember those New Year’s resolutions, pull yourselves together, and install updates. The vendor published a detailed security guide back in August.
Just in case, we also recommend checking your server — in case compromise has already occurred and attackers have managed to establish a foothold in the infrastructure (IoCs were published here, plus a couple of new ones from the PhantomCore group: 31.59.105.51, 31.56.227.100). MaxPatrol SIEM and PT NAD can help with detection.
And yes, if you’re going to have a call with someone via TrueConf — warn all conference participants about this 📱
#ir
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…
More in General
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…