
Work order for malware operation
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




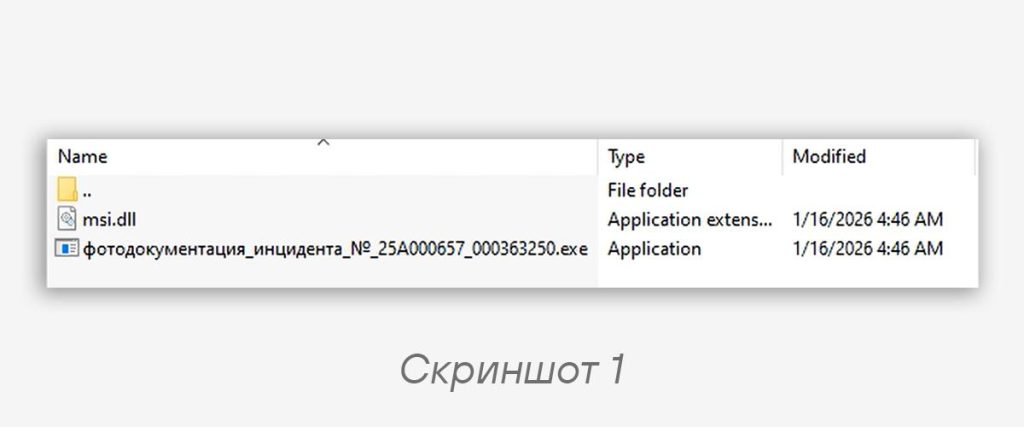
In mid-January, the cyber intelligence group recorded a campaign by the hacker group XDSpy targeting organizations in Russia and Belarus. A malicious DLL library and a legitimate executable file are distributed in archives (screenshot 1). PDF documents with contract-themed content are used as lures.
1️⃣ After launching the executable file, a decoy document is displayed to the user (screenshot 2), while the main actions are performed in the background. The contents of the archive are moved to the
C:\Users\Public directory, after which the malicious DLL library is injected via the DLL Side-Loading technique. Persistence in the system is established via an autorun entry
HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run with a name matching the name of the legitimate EXE and the value C:\Users\Public{legit_exe_filename}, which ensures automatic launch of the component when the user logs into the system.2️⃣ At the next stage, network interaction with the attackers’ infrastructure is established. A payload is downloaded from a specified link and saved to
C:\Users\Public\ followed by execution.3️⃣ The group’s domains, from which the next stage is downloaded, deserve special attention.
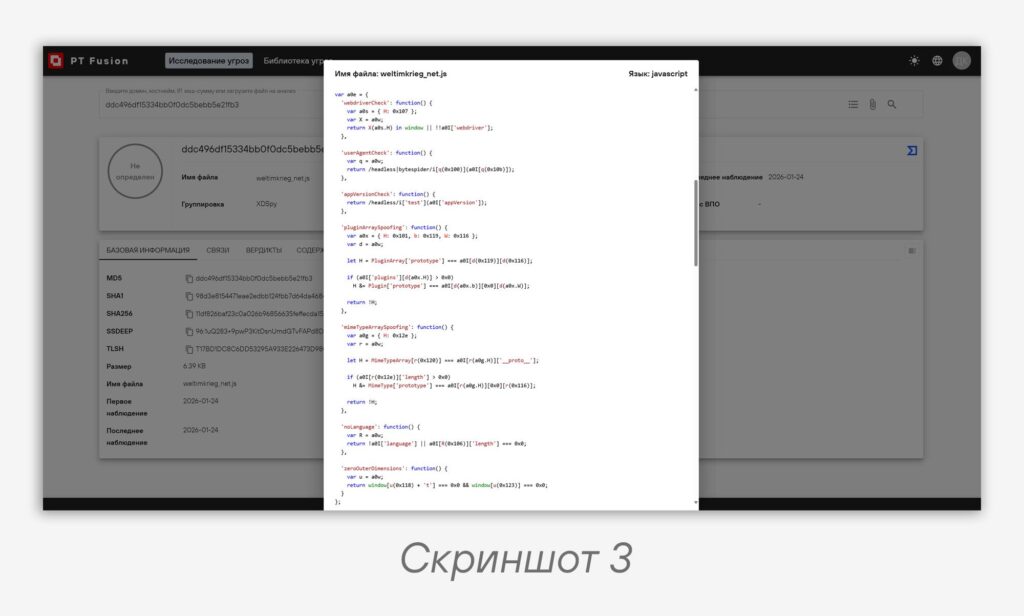
The body of the HTML page of the attacker-controlled websites contains obfuscated JavaScript (screenshot 3) that performs a preliminary check of telemetry and signs of an automated environment, including the presence of
navigator.webdriver, headless indicators in userAgent and appVersion, the validity of the navigator.plugins and navigator.mimeTypes objects, whether language/languages are populated, as well as anomalous outerWidth/outerHeight values. If the client fails the check, instead of serving the subsequent malicious stage, the domain returns a redirect to download a large file for speed testing from the proof.ovh.net domain.This approach complicates extraction of the next stage and reduces the likelihood that malware researchers will be able to obtain the group’s stage for subsequent reverse engineering. We have previously described a similar XDSpy chain and mechanisms for delivering the next stage.
IoCs
Domains:
weltimkrieg.net
cflbombardier.org
lelacdespassions.org

Archives:
7ce9d21fdd56d0881771502544ce5699
67a8f63c021839e30ee2e1910dc07ff7
3578a1b96820789059393ee9717d431c
919c5f6ce38586bd827a82e97dd44fb1

Malicious DLLs:
e338abdf9c3160be43b0fa2ee9692292
e758df62f6a0e52f37edd91d3fdf84ac
33a72ef5916bafff2c83d0f4e0f2aa16
0cf610531681f5aeef534f333026c6c2

EXE:
96b307d7d8f4c8b9d7aca9f0ee2ede75

Decoy documents:
acd3ca48b3ce0677ecb7ab1ab57936f8
ccc49c64b44977563a1fb7c6af52ceed
df98e0bd1e8e6c20ab07bfe790a6ef6eCode language: YAML (yaml)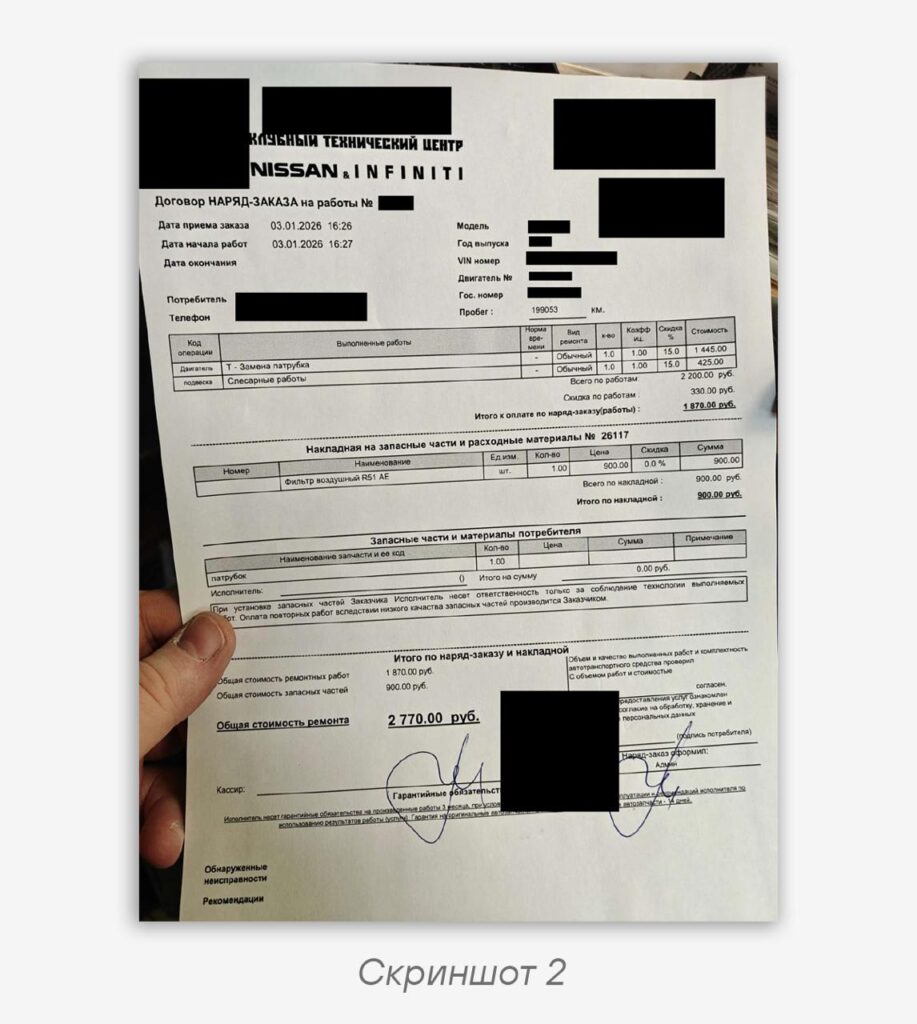
#TI #APT #ioc
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…