
utmpdump dual-purpose
More in General
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…




utmpdump dual-use
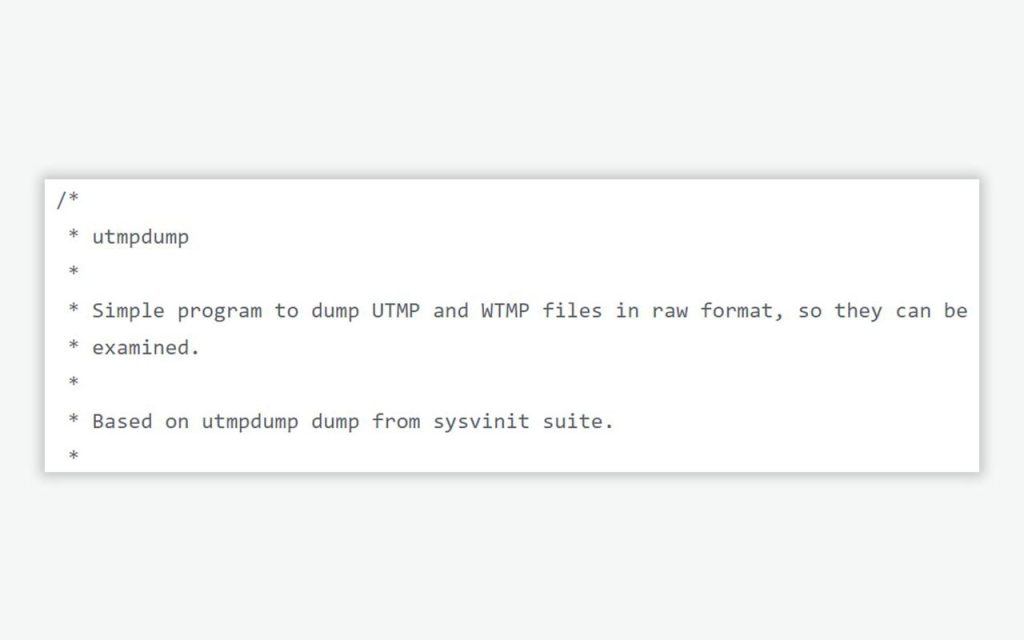
Default Unix systems have little forensic information (vs Windows) and a lot of useful utilities. For example, there is a “wonderful” utility that allows dumping information from [ubw]tmp files into ASCII files, and also, verbatim from the man page:
…which can then be edited to remove bogus entries, and reintegrated using:
utmpdump -r < ascii_file > wtmp
So if some “crooked” IP address ended up in the logs, illegitimate “system administrators” can simply delete it, which is exactly what we encountered on cases:
Dumping:
utmpdump /var/log/wtmpThrough a pipe, lines are grepped with the exclusion of the “crooked” IP address and output to a temp file:
| grep -v $EYE_PEE >/tmp/.wt The result is imported back:
&& utmpdump -r </tmp/.wt >/var/log/wtmp Then the temp file is deleted:
&& rm -f /tmp/.wtAnd of course, as stated in the man page:
But be warned, utmpdump was written for debugging purposes only.
The detections have been described a very long time ago, you can refresh your memory on them.
#tool #detect #hunt #nix #dfir
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…
More in General
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…