
The ExCobalt group uses a new GoRed tool
More in Threat actors
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- We will croc you
We will croc you 👻 PhantomCore continues to actively exploit misconfigurations in 1C to attack Russian…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…



❕ The ExCobalt group uses a new tool GoRed
During incident response at our client, we discovered a file named scrond on one of the Linux nodes, “wrapped” with UPX (Ultimate Packer for eXecutables).
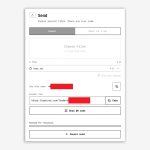
The file turned out to be a backdoor written in Go and, in its functionality, resembling components of the Sliver and Cobalt Strike frameworks. After unpacking it, we found package paths containing the substring:
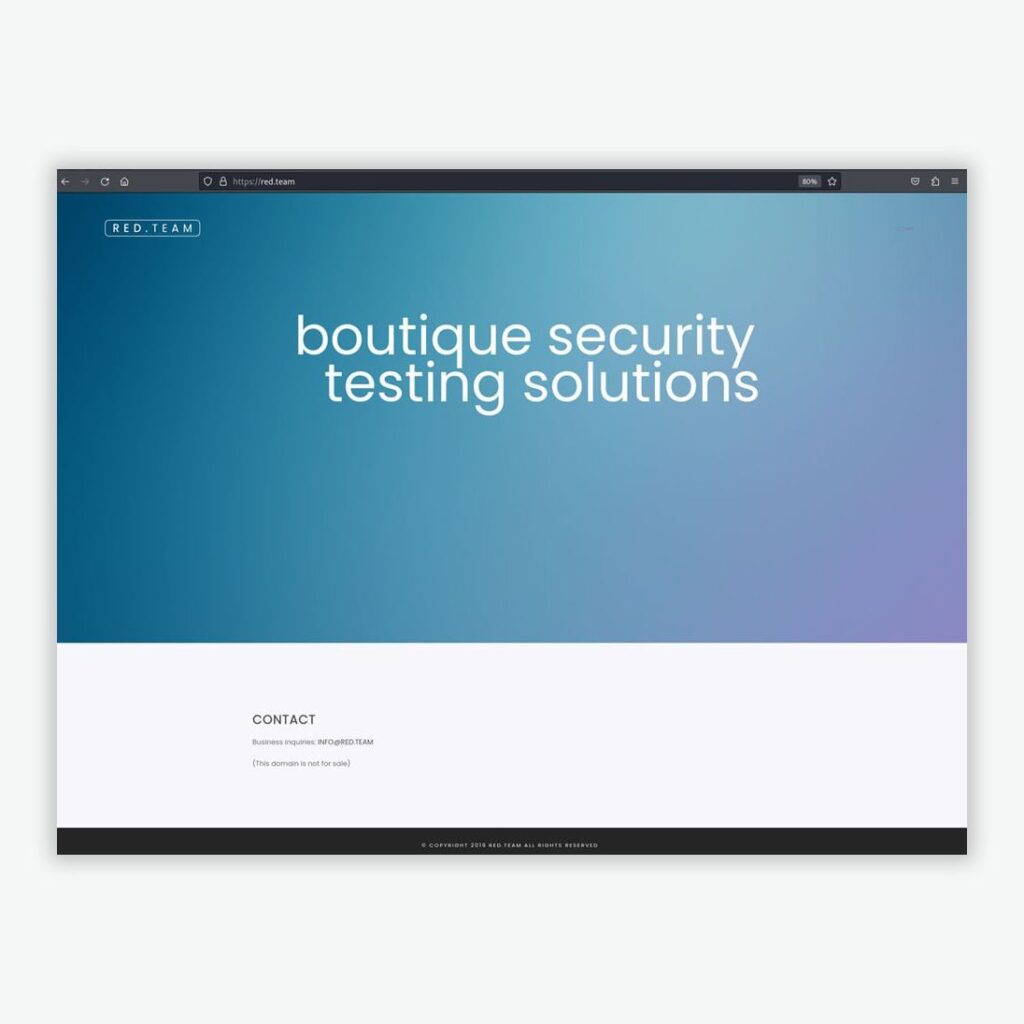
red.team/go-red/It subtly hints at the name of the tool (GoRed) and its creators, red[.]team. Presumably, they have a website that looks more like a business card than something significant and related to the attack. According to our data, the tool has been actively developed at least since 2023: while responding to one of the past incidents, we encountered version 0.0.1 (now it is 0.1.4).
In the course of further research, we confirmed that the tool is used by the ExCobalt group: there are infrastructure overlaps with the indicators described in our previous report.
💡 What kind of group this is
ExCobalt is a cybercriminal group focused on espionage. Some of its members have been active at least since 2016 and are believed to have been part of the well-known Cobalt group.
Cobalt attacked credit and financial organizations with the goal of stealing funds. A distinctive feature of the group was its use of the CobInt tool, which in 2022 ExCobalt also began using in some attacks.
🎯 Who the attacks are aimed at
Over the past year, PT ESC specialists have recorded attacks and investigated incidents related to the ExCobalt group in Russian organizations from the following sectors of the economy:
• Metallurgy
• Telecommunications
• Mining industry
• Information technology
• Government institutions
• Software development
A full technical description of the GoRed tool, as well as indicators of compromise, can be found on our website.
#APT
@ptescalator
More from global_author
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…




More in Threat actors
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- We will croc you
We will croc you 👻 PhantomCore continues to actively exploit misconfigurations in 1C to attack Russian…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…