
Friday newsletter
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




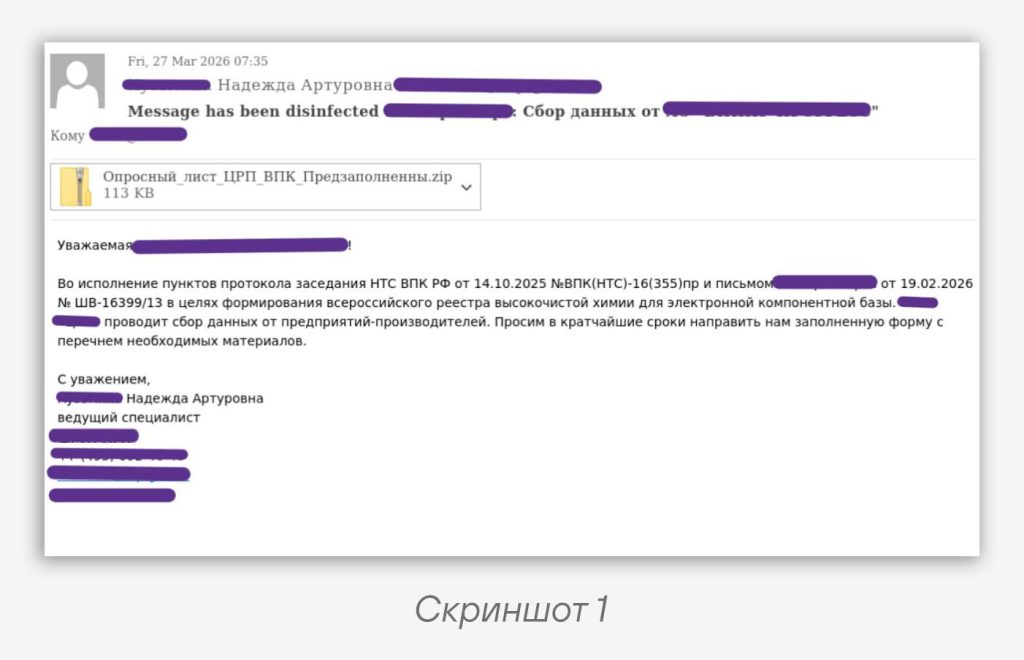
Imagine: you’re an employee of a Russian organization, and on Friday someone named Nadezhda Arturovna 😌 sends you an email (screenshot 1) asking you to take a survey. As always, a federal enterprise employee is asking for everything and as quickly as possible. Your actions? 🤔
If you believe the fake employee and try to take the survey, inside the archive you’ll find a file with the same name,
Опросный_лист_ЦРП_ВПК_Предзаполненны.xll (you noticed the typo too, right?). It’s a DLL — a special Microsoft Excel module. When the xll file is opened, a malicious payload %LOCALAPPDATA%\\Comms\\mspm.exe is dropped and executed, while you, suspecting nothing, will only see a decoy spreadsheet %USERPROFILE%\\Documents\\Tablica1.xls (screenshot 2) 😶But we sincerely hope that, despite it being Friday, you’re vigilant 👓. After all, the payload itself is an AI-generated backdoor
WarpPlugin, also known as EchoGather — a known GOFFEE tool. Its main capabilities include:🐾 executing CMD commands to control and explore the victim’s computer
🐾 exfiltrating files from that system
🐾 uploading files sent by GOFFEE to that system
We’ve been observing this kind of activity since the end of last year 😏. GOFFEE eagerly uses AI agents, constantly generating new decoy files and variations of the
WarpPlugin backdoor. The threat actors also don’t skip constantly generating new names for C2 addresses.IoCs
9c189eb72315960a6bc10d25dc8f8808f9ed13088951bae37ca0d7502fec8e10
1b6dd18db3da8b9df1c3ca99a2de0a0296ce7c5f92c2f6a6a8831d0e4f61aed1
b02c4d355a1c8f3209f62221b2bafcfefa3ab1444461a209fdcd75fa04f4fb1e
f75b3e37c9683d4862e71ef204fd4128169168ce22e2722618b9aed69bf6add0
https://ntp.report/api/v4/projects/report/nowCode language: YAML (yaml)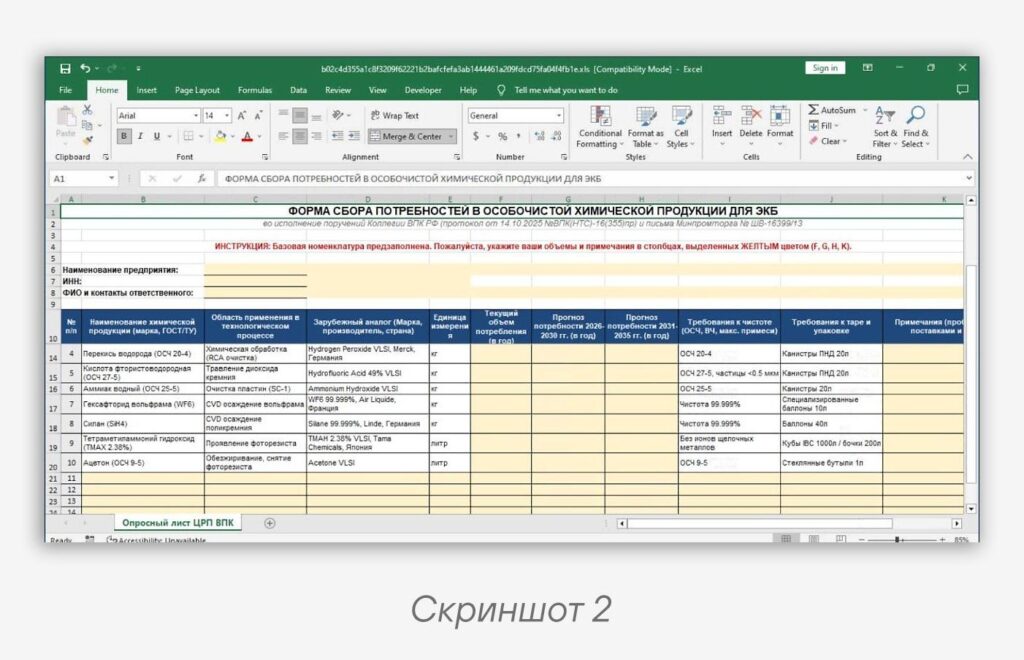
#Malware #TI #APT
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…