
Another Python stealer?!
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Since the beginning of September, we have been tracking attacks that at first glance could be attributed to the activity of the Lazy Koala group. A Telegram bot is used as the C2 server for exfiltrating compromised data, and the lure names resemble the names of the files that Lazy Koala used in its attacks:
Исковое_заявление_о_взыскании_убытков_и_морального_вреда_в_связи_с_нарушением_условий_договора_№1234_от_28_августа_2024_года_и_неудовлетворением_претензии.exe
Претензия_о_нарушении_договорных_обязательств_и_требование_возмещения_ущерба_по_договору_№1234_от_28_августа_2024_года.exe
Code language: plaintext (plaintext)
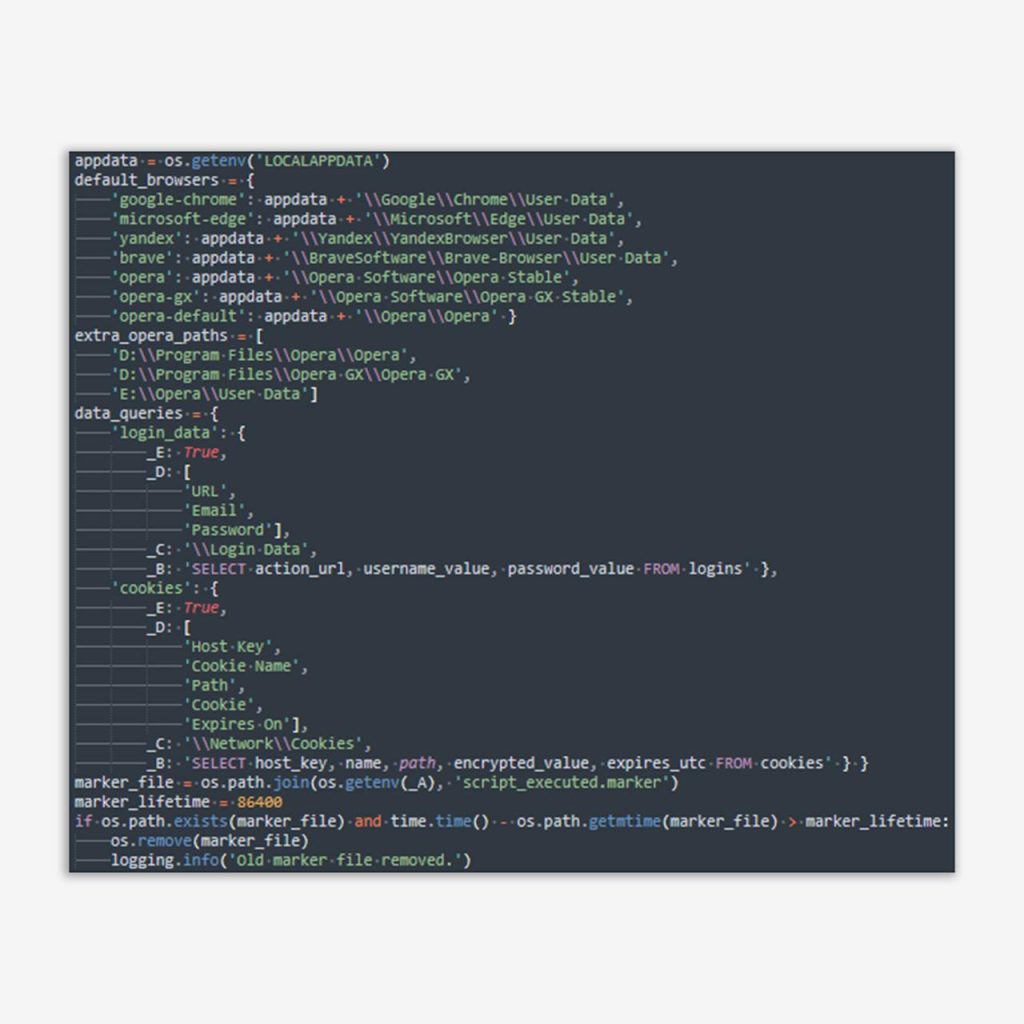
However, upon further examination of the code of the stealer, which we named MarkerStealer (due to the
script_executed.marker artifact), as well as the Telegram bots, no connection to the group could be established.👾 MarkerStealer itself has the functionality standard for all stealers: it allows obtaining credentials and cookies from browsers and exfiltrating them to a C2 server.
The only thing that sets it apart from others is the creation of a so-called marker at the path
%TEMP%\script_executed.marker, signaling that the stealer has already run. The marker has a lifetime: if, upon re-launch of MarkerStealer, the creation time of %TEMP%\script_executed.marker exceeds one day, then the malware re-collects accounts and cookies from browsers.IoCs:
1b9f8a0edfedb141753d080f6200573f75d275d0d5b62bba6008e1a0424a1846
3e32ab015ad7a1c35faf649dd0dfd50084918e0ffde65c5911409a659e049022
7b8f901160f567e8fe1294dcc5477da08f1bb133935a679ac5f704df2ab2862b
37e17898d9e6e4950fe9639cbb5f4102df6cfb7b3e236120b036a0d2c5362815
7572f826e9ccde9183537afb6146c844fea177bc3b6053e27f35190d0a71f507
12458b8e63d084d161dc24b3a3d46967c9bc1ad9613deb26d76f378a34869301
400269ef55144512f0ceb74854c7d913f6aa4650de8ecf096487727895f8bc80
274784844d3c112127b7a5e7d8b60d2f256aad4c56c6e07ba681186764d63396
cd10cc5a6c69d8cffedcb80e79985c9762ab0f0853298981ce13991d51642b40
e4a6e228e88504bc622a50fdeb3f2c264466a6bc7283136675cc4f2c6aa11ca6
2ecdd29bd72d001186ca2c9946e7e8e16da84c45678d66abfde8d940cf78df09
Code language: plaintext (plaintext)
#TI #Malware
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…