
PrevedMedved 👋 — it's Lumma Stealer again
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




In mid-November, the PT ESC cyber threat intelligence team recorded a campaign distributing the malware Lumma Stealer and NetSupport RAT. A GitHub repository available at
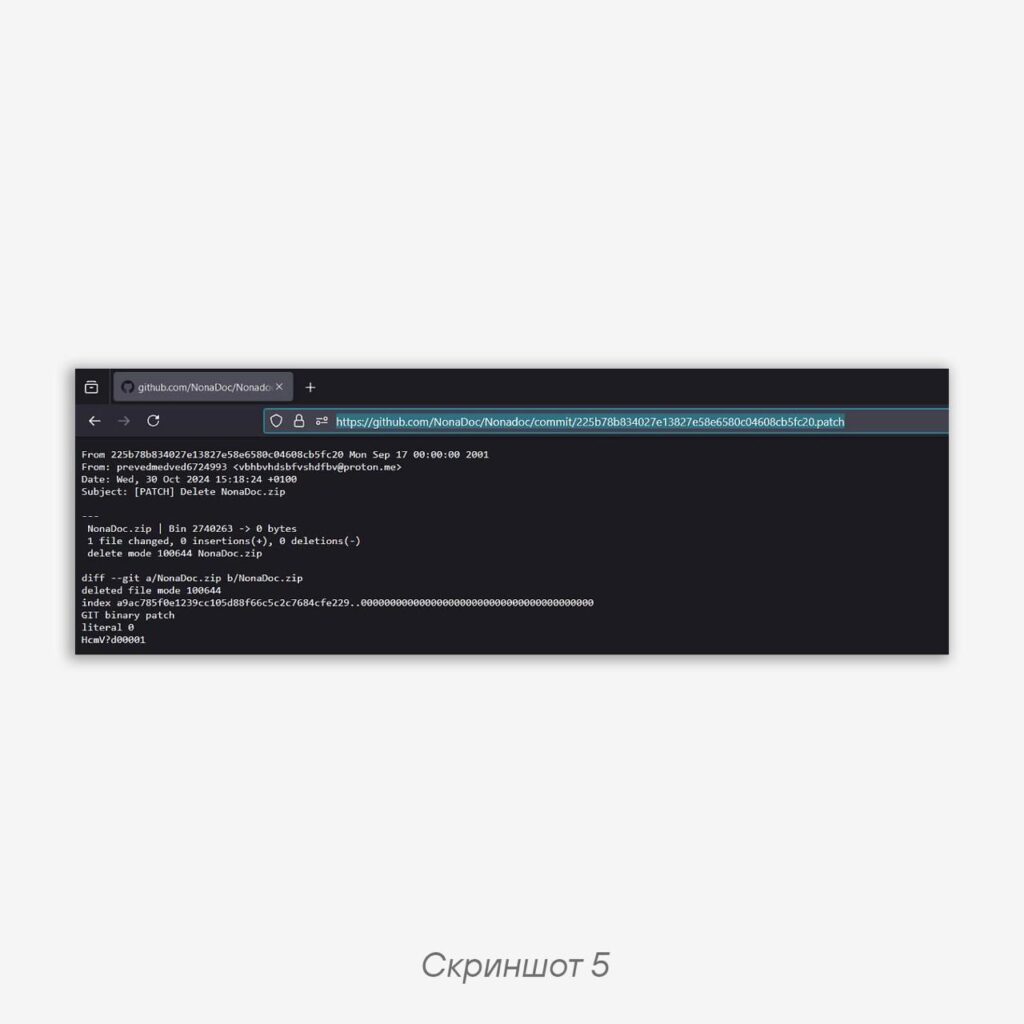
github.com/NonaDoc/Nonadoc/releases/tag/defi_prive was used as the source of infection. The malicious content was located in the tag section, while the repository’s main branch had been deleted. The GitHub account used to host the materials was registered under the name
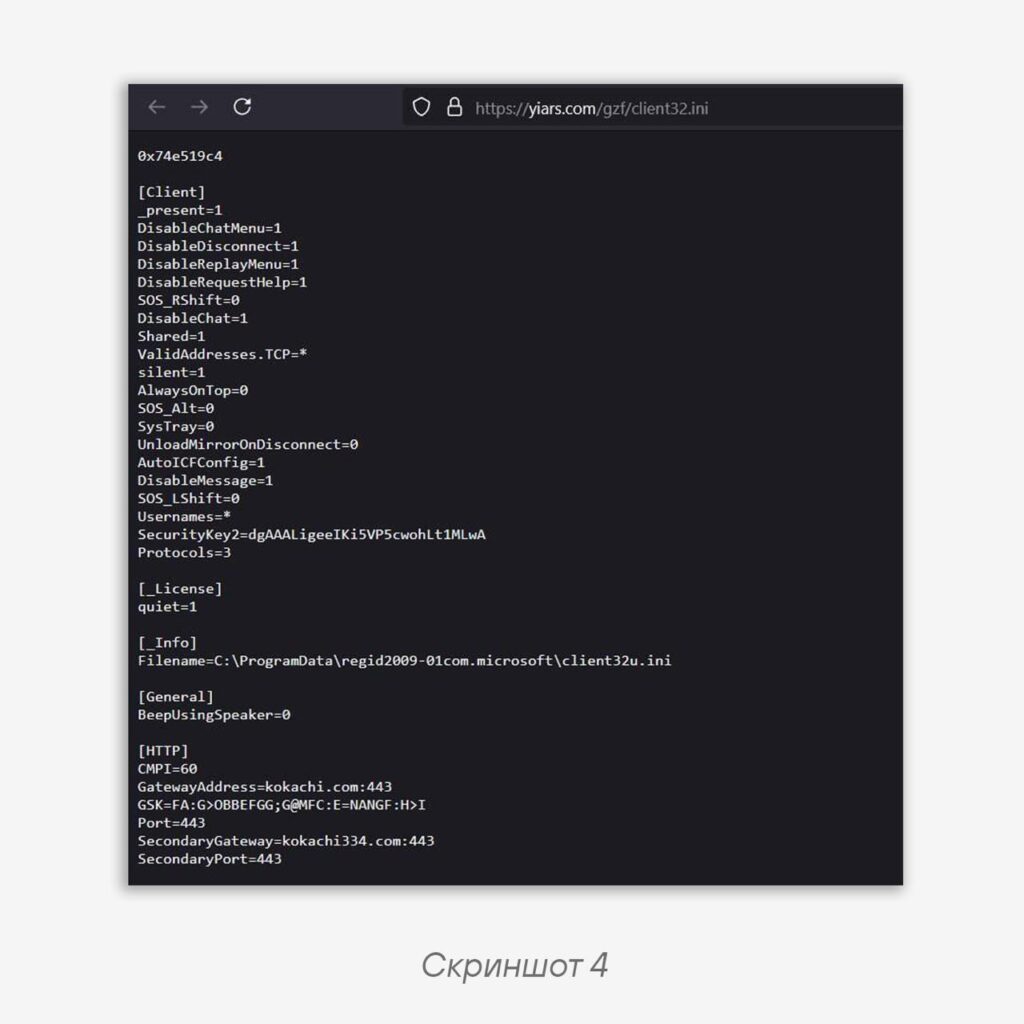
prevedmedved6724993 and is linked to the email address vbhbvhdsbfvshdfbv@proton.me.🧤 During the analysis of the repository, it was noticed that the hosted lures and malicious files are regularly replaced with new ones (screenshot 5). The average update frequency is about once a week. The threat actors focus on using phishing lure files that mimic documents from various organizations.
The first file to fall into our hands was the LNK file
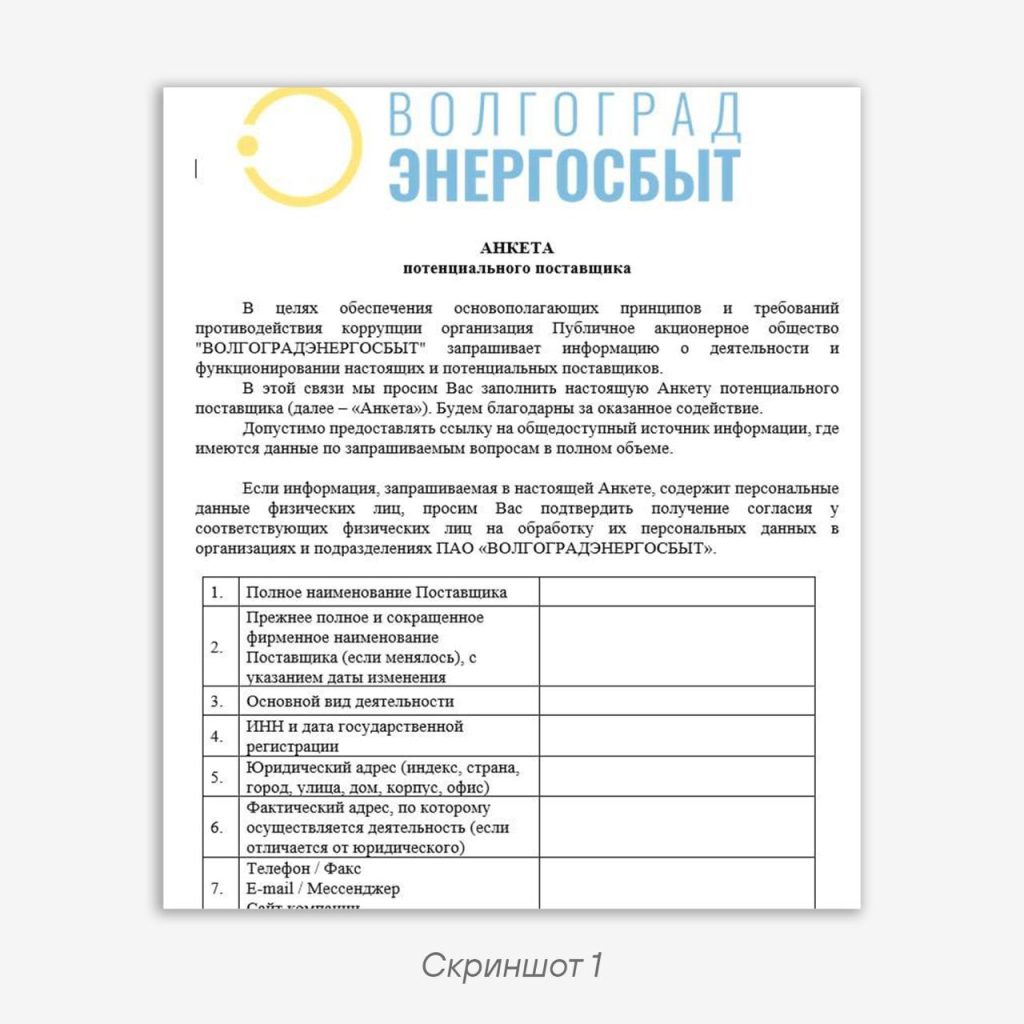
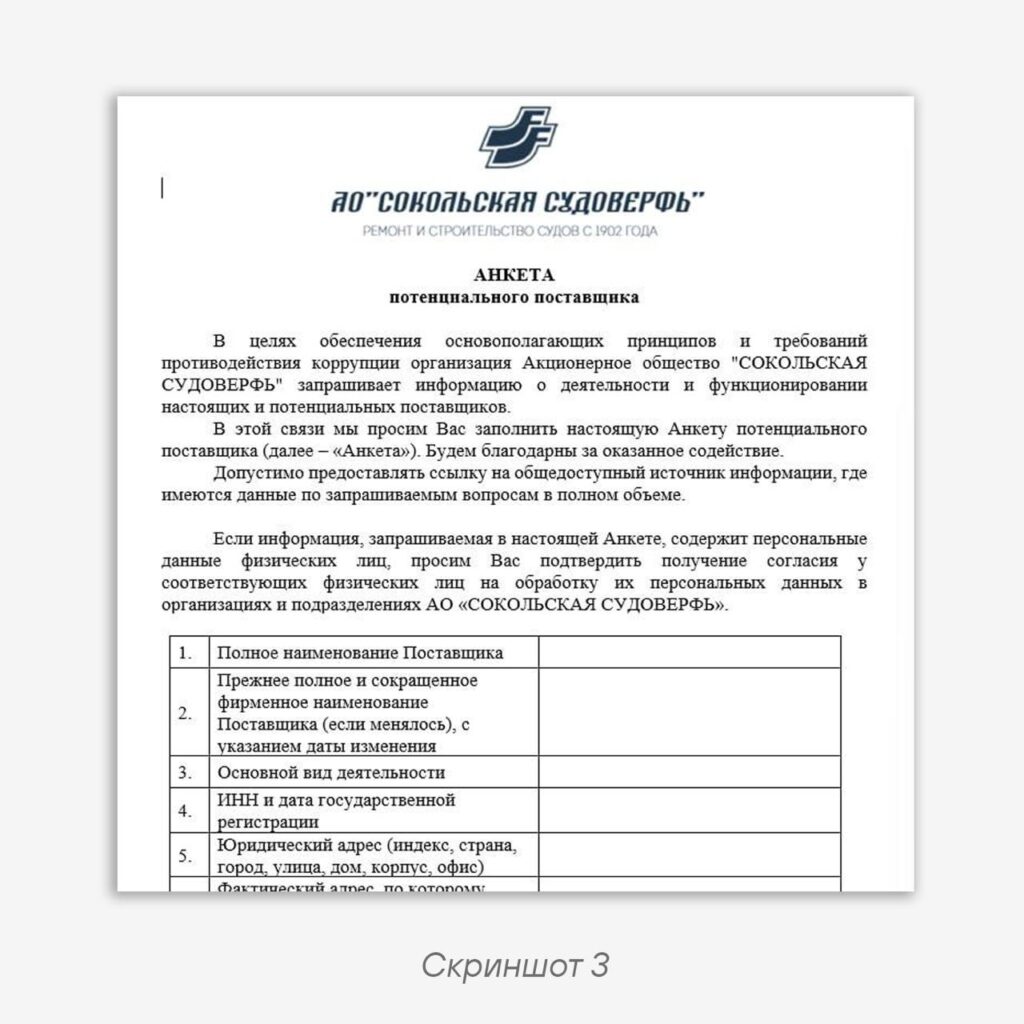
Anketa_energosale.docx.lnk (screenshot 1), stored on the website energosale34.download. After launching, the file installs Lumma Stealer from the aforementioned GitHub repository and NetSupport RAT from the threat actor’s C2 server to establish persistence on the victim’s device. The phishing document Anketa_energosale.docx (screenshot 3), purportedly associated with the organization “Volgogradenergosbyt,” was available for download from the same repository.🫡 During the investigation of the attack, other schemes were also identified in which, instead of a phishing document, a file disguised as, for example, a military enlistment summons was distributed (screenshot 2). The LNK file
povestka_378478112.pdf.lnk was stored on the host 80.78.27.201, and the accompanying files, including the malware and lures, were also hosted in the GitHub repository.Notably, the author of all lure documents in the metadata is listed as Gallyamova Rimma Abdulnurovna. This may be an attempt to divert attention or an additional part of the phishing strategy.
According to VirusTotal, Lumma Stealer samples are detected as malicious by only three antivirus solutions. This fact indicates a high level of obfuscation and the uniqueness of the malware — most protection systems find it difficult to detect.
The attacks were conducted throughout November. The threat actors actively update their tools, including malicious files and lures, and we continue monitoring. A similar malware distribution scheme has been described previously, but it did not affect users from CIS countries.
IoCs:
LNK file:
90301696accc600a3fc2a1419d0c73566a19f42424d2da6e6f215a83ba3895e6
68d0373fc7fcd74d7379f8175a894194ac285f98810359a7f48978ef15f5283e
96bd372f8a4e39e0e6e629994a2b284432c9e5a0a48e1f46100a0a6b0ce349bd
989dd914ccbd2df2a36f0500d0bdac9e286cdf39d53ab72d18f11bc726a692e8

Lumma Stealer:
26be491b59e98932bf12985cd6a24d5a0be33ee92767b19b41fe2917deb96f79
8762d87be2998ca50229e9b51a2a7700bbb1fd75b99864d05b4d630a5e091014
b0d738f7003d5bb5d7c5d0dc9441e45367fad635cbf505f129df48f8155e38a2
61e985cf63a414c5db76d1f57d9801e6d7dba106e8a8dc73ad29b53044c3c68f

NetSupport RAT:
860393e31788499f8774be83c65bcf29658cc77bf96ee2f4c86b065aedbf77de
176f7e61d26c33df91425f063c6494d6cd63f4de2654de3d72158a272bb03ae5

Files:
Anketa_energosale.docx.lnk
povestka_378478112.pdf.lnk
Anketa_energosale.docx.lnk
520a7afb8367e14661b412c65b9a805d.virus
Anketa_energosale[1]
poqexec.exe
Povestka_34.png
Anketa1
anketa_miner[1]

Domains:
energosale34.download
yiars.com
thisbusylife.com
abxweb.com
pdfbypari.com
kokachi.com
kokachi334.com

URL:
https://github.com/NonaDoc/Nonadoc/releases/tag/defi_prive

IP addresses:
94.232.43.219
80.78.27.201
80.78.24.5

Metadata:
dc:creator: "Gallyamova Rimma Abdulnurovna"

Email:
vbhbvhdsbfvshdfbv@proton.me
Code language: YAML (yaml)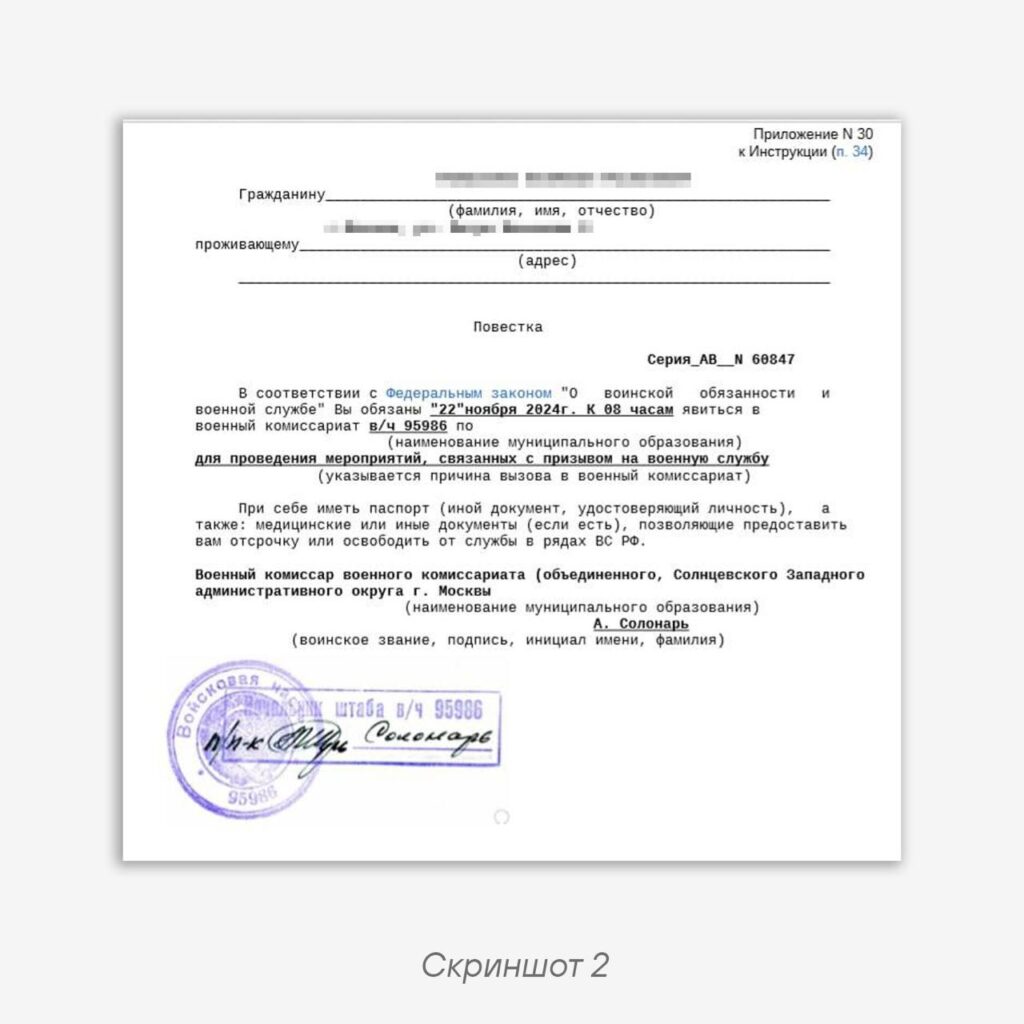
#TI #Phishing #Malware #IOC
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…