
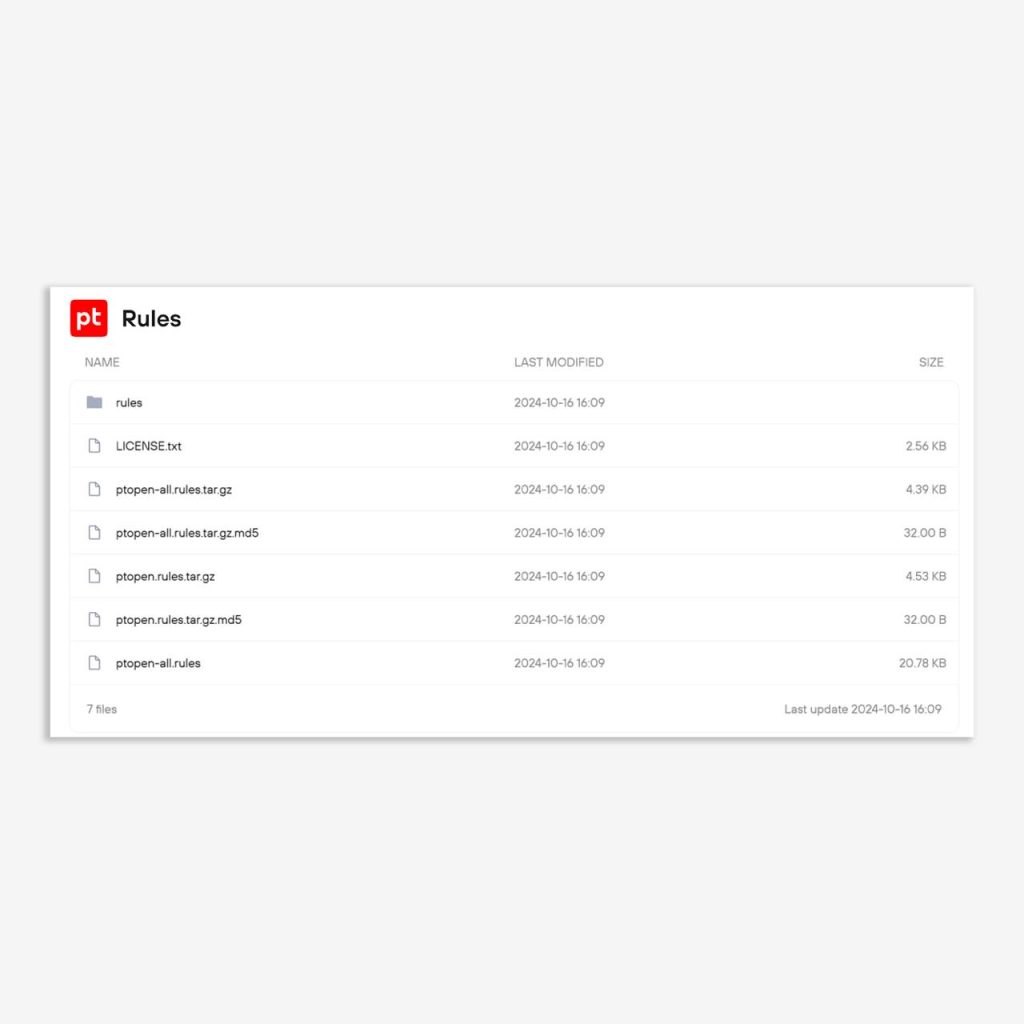
Have you heard about the public repository of Suricata rules Attack Detection?
More in Rules
- Hunting RATs by their own certificates 🕵️
Our colleagues at Censys published a breakdown of the AsyncRAT family, describing an entire genealogical tree:…
- Confusion in WSUS vulnerabilities: setting the record straight
Confusion Around WSUS Vulnerabilities: Setting the Record Straight 🕷 One of the most pressing vulnerabilities in…
- Extracting data from disk images with a damaged file system
He may not, as unvalued persons do, Carve for himself (W. Shakespeare) When investigating an infrastructure…
- New connection to old techniques
A New Connection to Old Techniques 📡 During incident investigations, the PT ESC IR team discovered…
- Idea for a correlation rule in SIEM
Idea for a SIEM correlation rule 💡 Although tracking the entire attack chain described in the…
Have you heard about the public repository of Suricata rules Attack Detection?
Yes, that’s meeee Within the large PT Expert Security Center team, there is a separate group of experts whose main task is to develop detection rules for network security tools. You are probably already familiar with some posts about network artifacts from this team.
After a two-year break, we are returning to you with an updated portal and once again starting to publish parts of our expertise in the form of Suricata rules 🔥
What’s new:
1. Rules for the latest vulnerabilities.
2. Rules for detecting the tools Croc and gsocket, which are extremely popular in narrow circles.
3. And also several rules for detecting lateral movement in an Active Directory network.
Configure suricata-update to support the official ptrules/open rule source and keep an eye on updates on our X page.
👋🏼 Stay tuned
#suricata #network #signature #rules
@ptescalator
More from global_author
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…




More in Rules
- Hunting RATs by their own certificates 🕵️
Our colleagues at Censys published a breakdown of the AsyncRAT family, describing an entire genealogical tree:…
- Confusion in WSUS vulnerabilities: setting the record straight
Confusion Around WSUS Vulnerabilities: Setting the Record Straight 🕷 One of the most pressing vulnerabilities in…
- Extracting data from disk images with a damaged file system
He may not, as unvalued persons do, Carve for himself (W. Shakespeare) When investigating an infrastructure…
- New connection to old techniques
A New Connection to Old Techniques 📡 During incident investigations, the PT ESC IR team discovered…
- Idea for a correlation rule in SIEM
Idea for a SIEM correlation rule 💡 Although tracking the entire attack chain described in the…