
Cloud services from the operator "MeHaFon"
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




📲 Cloud services from the “MeHaFon” operator
News from the field: the PT ESC team is observing a new campaign by the Cloud Atlas group targeting government organizations in Russia and CIS countries. We covered this group in our research APT Cloud Atlas: Unbroken Threat and in a post.
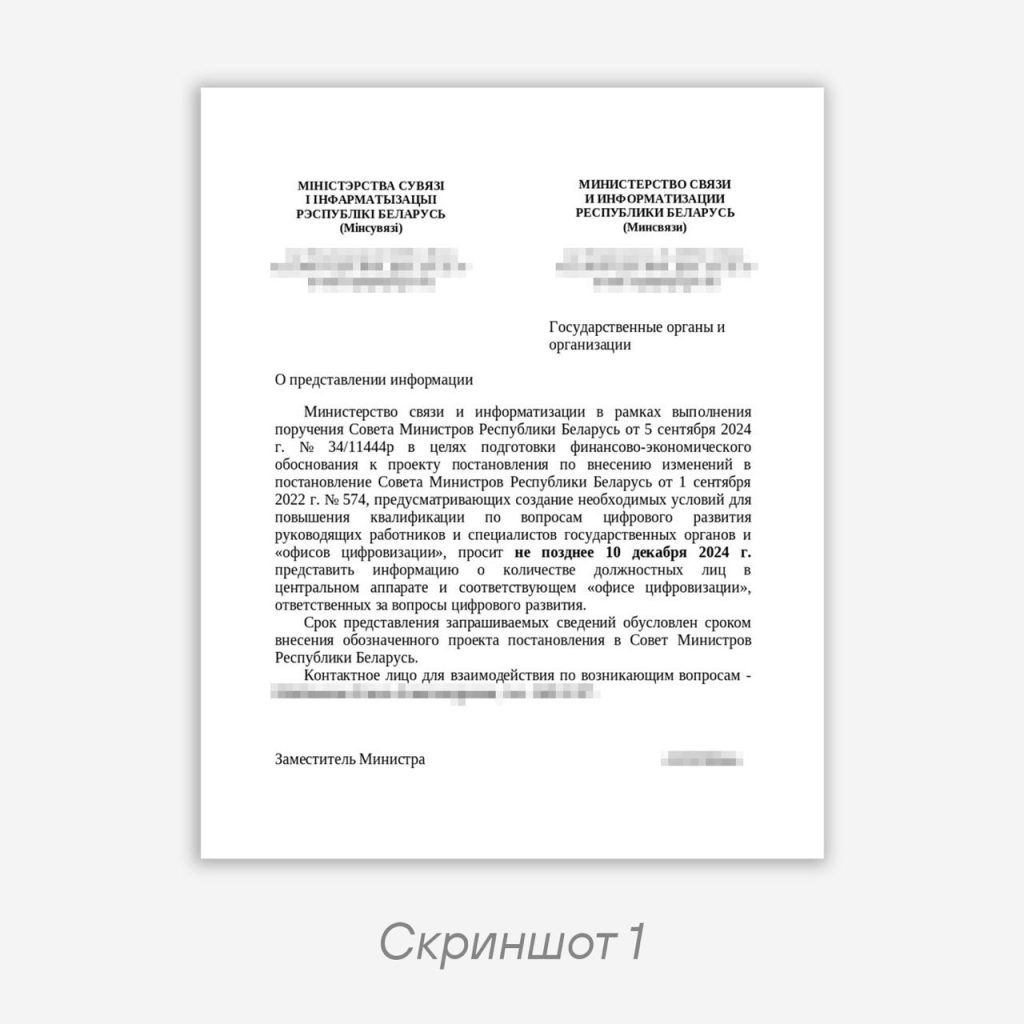
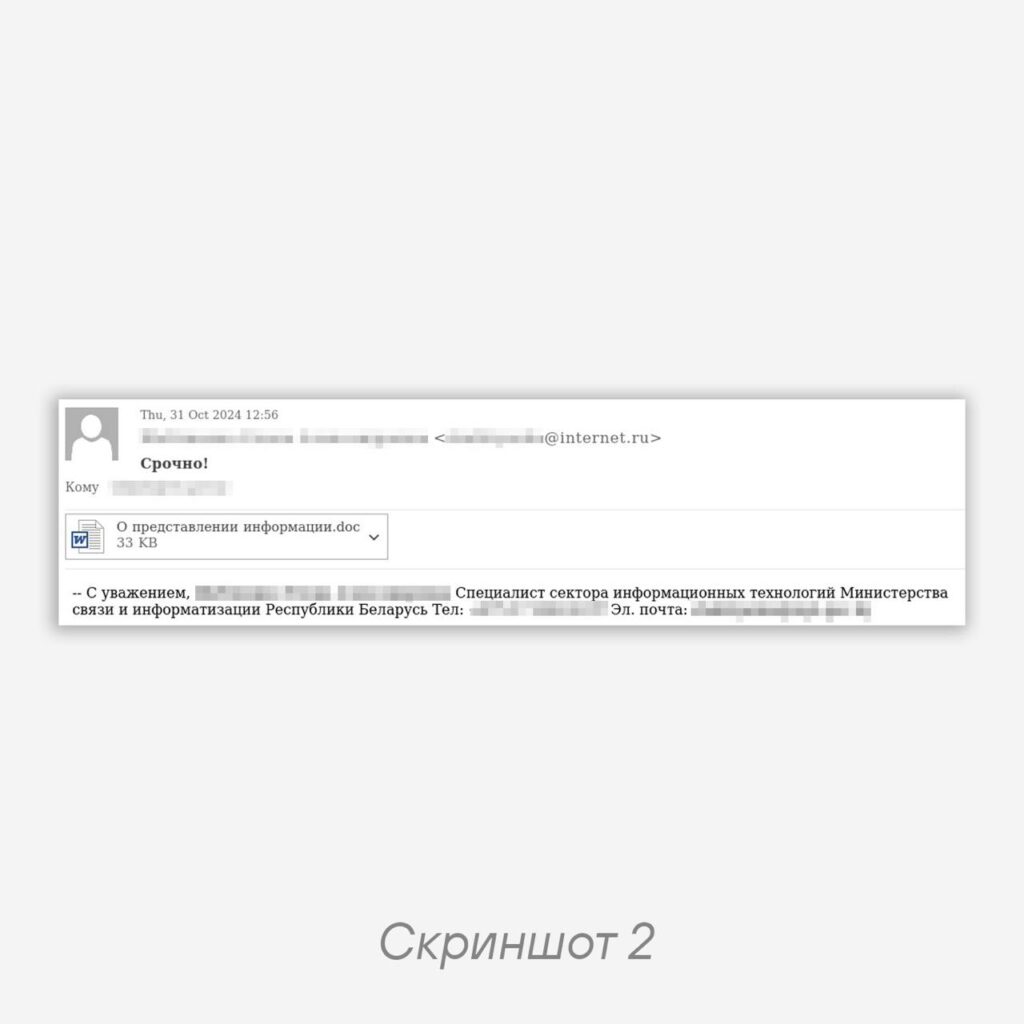
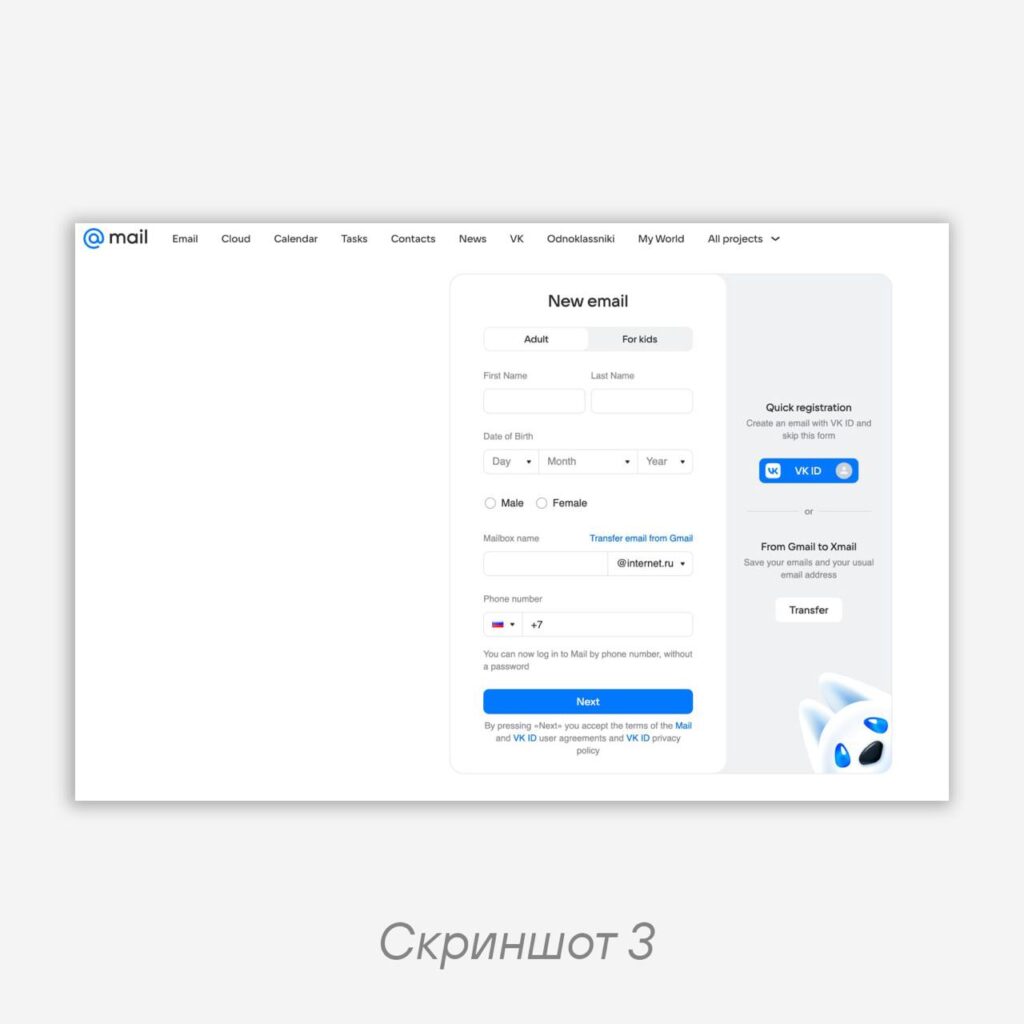
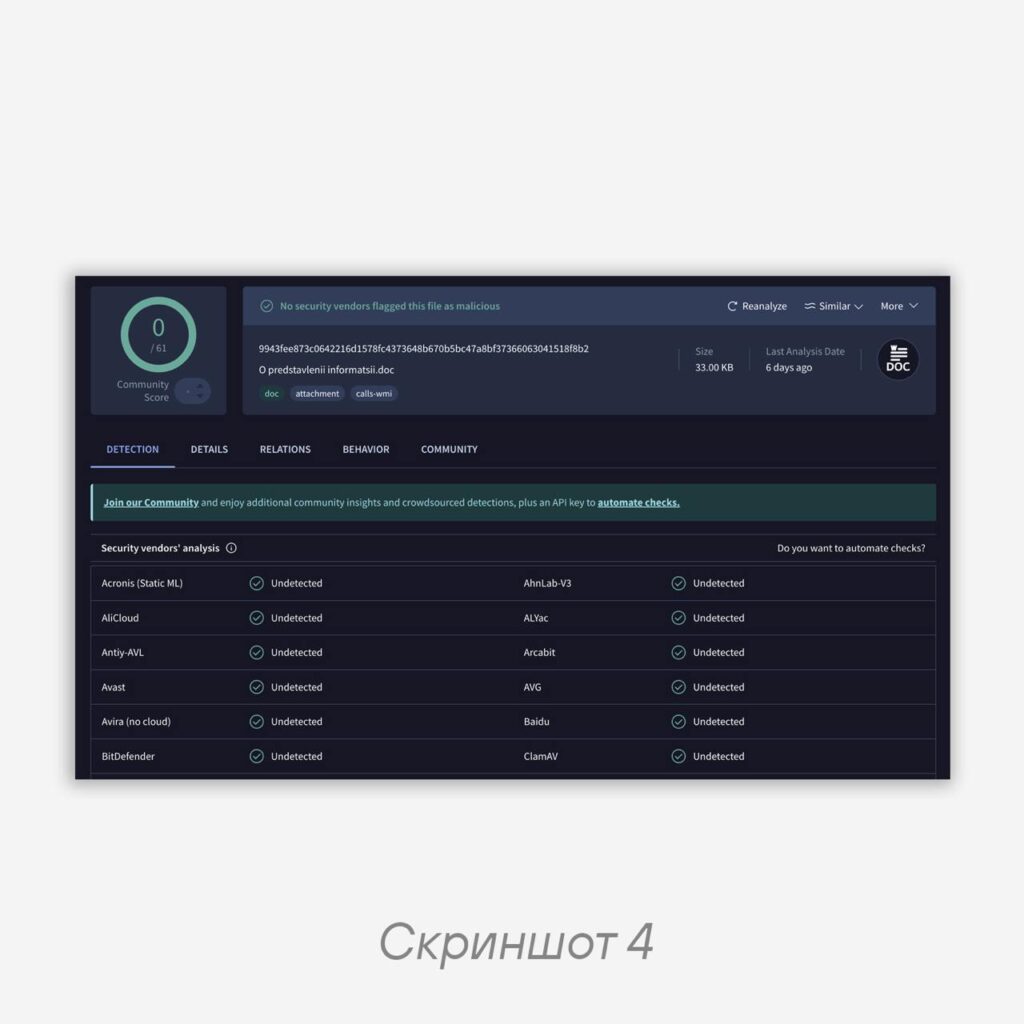
📝 As the initial vector in their attacks, the threat actors traditionally use phishing emails with a malicious attachment “О представлении информации.doc” (VirusTotal 0/62). The emails are sent from @internet.ru addresses. This email domain can be obtained by registering with the mail.ru service.
It is noteworthy that the attackers are staying true to themselves and have been using cloud services since 2014. At the same time, they continue to experiment, and new popular platforms are added to their arsenal time and again. Therefore, first and foremost, we strongly recommend checking all sessions over the “Yandex Disk WebDAV” protocol (webdav.yandex.ru) and requests via the Google Sheets API (oauth2.googleapis.com, sheets.googleapis.com).
IoCs:
mehafon.com
technoguides.org

9943fee873c0642216d1578fc4373648b670b5bc47a8bf37366063041518f8b2
Happy hunting and stay tuned!
#hunt #detect #ioc #apt #news
@ptescalator
More from global_author
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…




More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…