
Exchange_SSRF
More in General
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…




📬 Exchange_SSRF
Our practice shows that a fairly large number of organizations still have not installed updates on their public Microsoft Exchange mail servers.
As a result, attackers have the ability to gain access to email correspondence at these companies. To do this, attackers use the open-source project Exchange_SSRF.
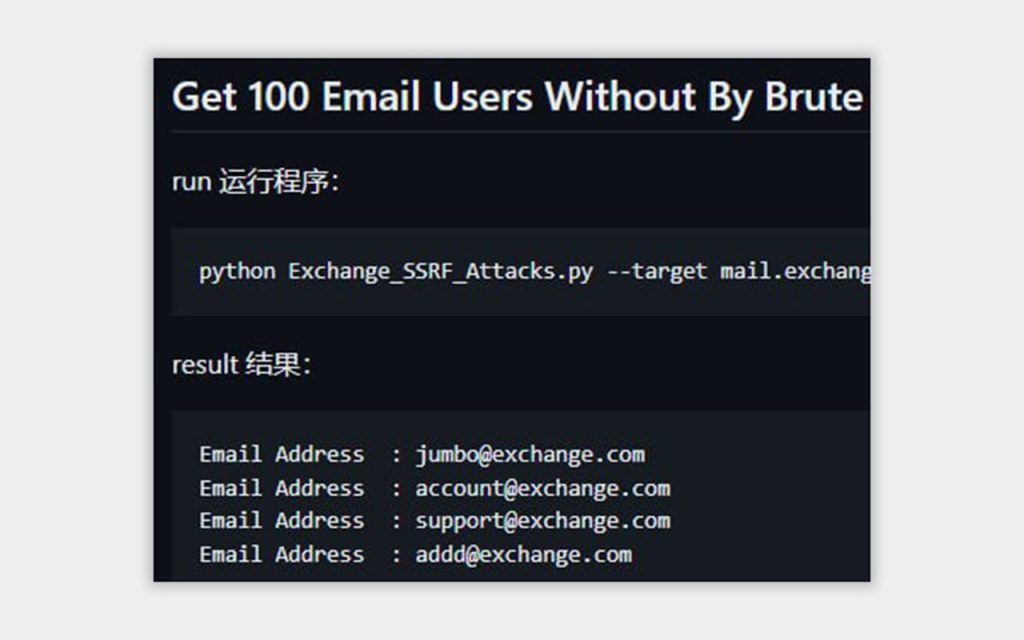
Exchange_SSRF is a publicly available Python script that allows dumping user mailboxes (100 by default) from a victim’s Microsoft Exchange server. In effect, the script exploits two vulnerabilities (CVE-2021-34473 and CVE-2021-34523) from the ProxyShell chain.
To dump mailbox files, the FindItem, GetItem, and GetAttachment methods are used, which are executed not under a user account but under the system NT AUTHORITY\SYSTEM account, which is clearly visible in the Exchange Web Services (EWS) logs:
C:\Program Files\Microsoft\Exchange Server\V15\Logging\EWS
As a rule, attackers do not modify the script and use it with the default User-Agent specified in the source code, with a period at the end.
User-Agent:
Mozilla/5.0 (Windows NT 10.0; WOW64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/92.0.4515.131 Safari/537.36.
It is also worth noting that almost all recorded attacks using this script were carried out from Latvian VPN addresses of the Mullvad VPN service.
Examples were published on Telegraph.
C2:
31.170.22.18
31.170.22.20
31.170.22.22
31.170.22.26
31.170.22.5
31.170.22.6
#tool #detect #hunt #win #dfir
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…
More in General
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…