
Jade metal: is the not-so-new Telemanmilconfav group attacking military organizations?
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




In March, researchers from F6 published a report on the Telemancon group, which attacked industrial organizations. The group was named after its use of the
telegra.ph service, man — from the word manufactory, con — because it stored its payload in %userprofile%\Contacts\.We discovered several files associated with this group. One of them is
Письмо_в_АО_УАПО_запрос_РКМ_и_закл_ВП.scr 📬When launched, as in the case of the samples described by F6, the SCR script opened a decoy PDF document and a malicious PowerShell script in the same
%userprofile%\Contacts\ directory, after which the group was named: the theme of the decoy document was related to national guard troops and defense orders But of greater interest is the discovered archive
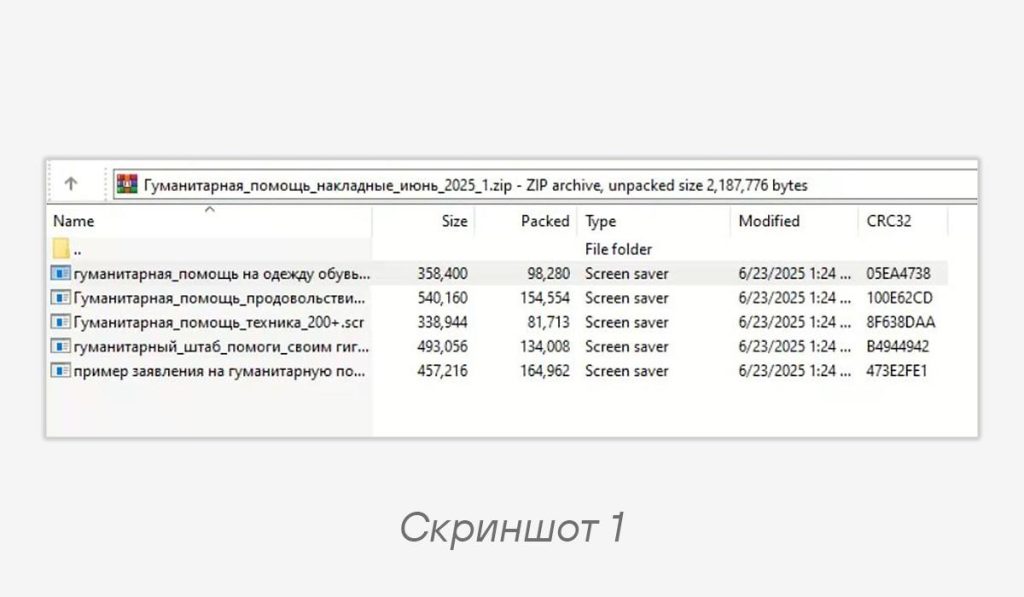
Гуманитарная_помощь_накладные_июнь_2025_1.zip. It contains five SCR scripts: four of them masquerade as XLSX files, one — as an image (screenshot 1).After launch, each of them drops two files: a PowerShell script (into the
%userprofile%\Favorites\ folder) and a legitimate XLSX file (in one of the five cases, an image). The Excel documents and the image referred to information about humanitarian aid for the military (screenshot 2).🫤 The tools themselves have undergone changes: they have become harder to analyze and have increased their resilience to defensive mechanisms. The main changes affected TMCDropper. Previously, the code had a structure with separate encrypted modules, but the new version uses VM-based obfuscation.
TMCShell itself has not undergone major changes: an additional check for the presence of files with the
.ps1 extension was added to it in order to avoid autorun on virtual machines.The key change is the use of a global variable, for example
$qvwml (it differs for each script), which controls the payload decryption process. Initially $qvwml = 0, but after successful checks (including .ps1 and disabling AMSI), its value increases:$qvwml += 2
Code language: plaintext (plaintext)This variable affects the regex mask in the decryption loop:
foreach($ucbxt in $cjzuc){
    "$ucbxt -replace ('.(.'+'.'*$qvwml+')'),('$'+$(h)+55/55)"|iex|iex
}
Code language: plaintext (plaintext)
After
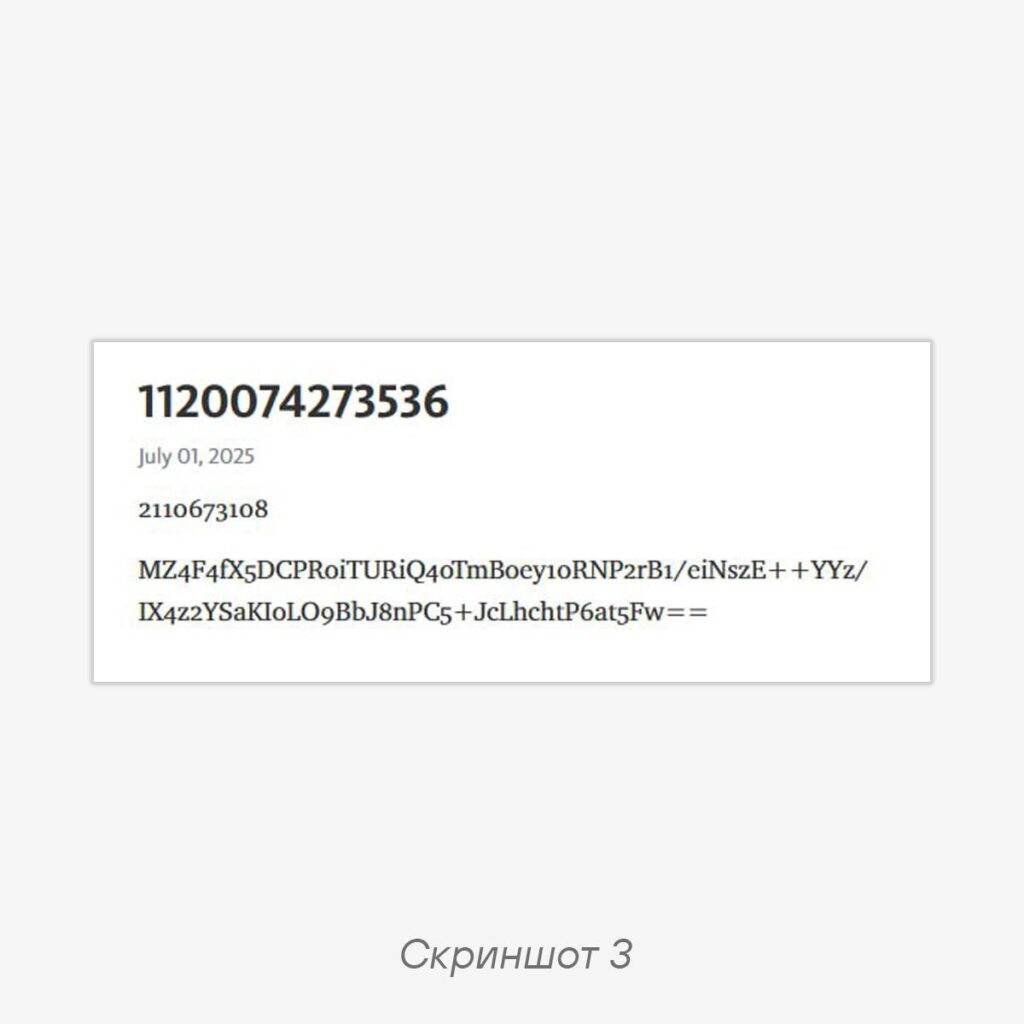
$qvwml is changed, it is impossible to run the script again, since the regex mask no longer matches the original pattern. TMCShell retrieves the contents of a page from
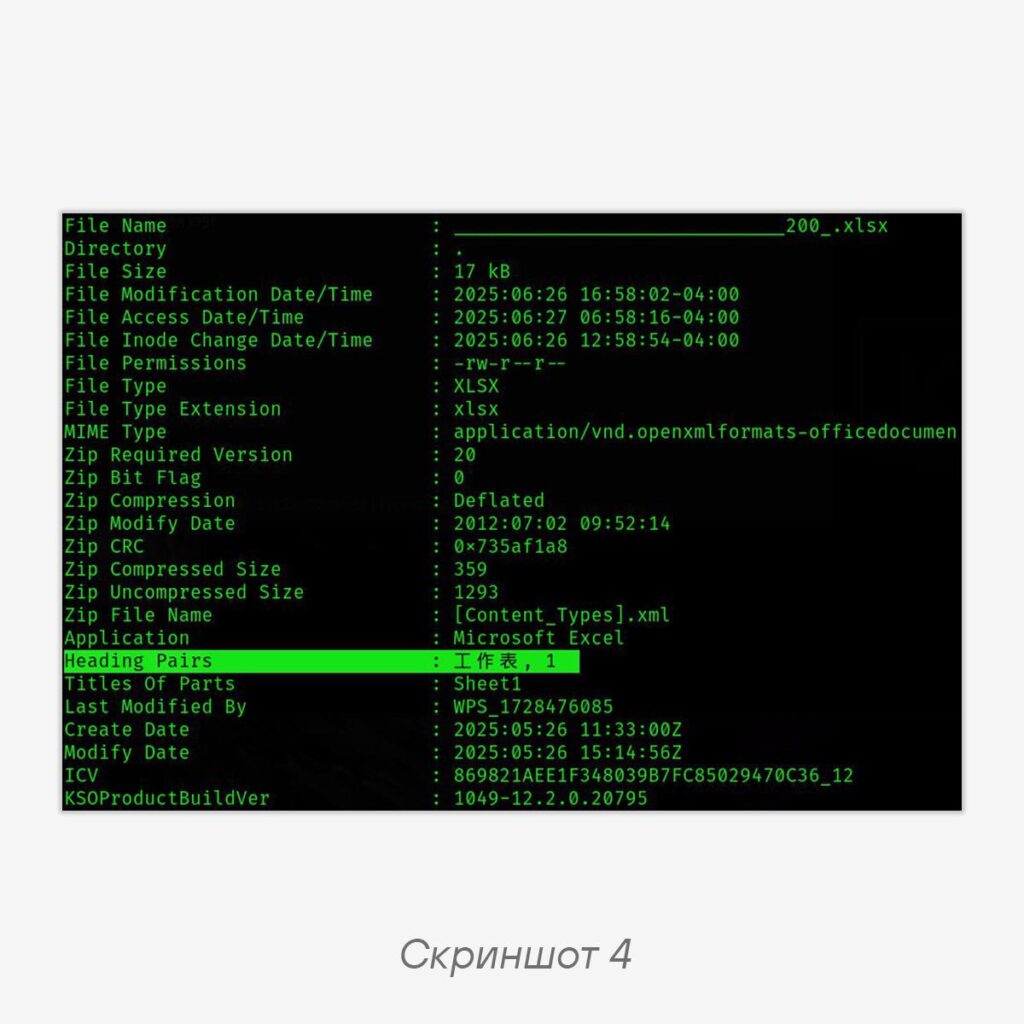
telegra.ph and decodes the C2 address from the first line, and the digital signature from the second (screenshot 3; the response that TMCShell parses). At the time of analysis, the C2 server itself had the IP address 212.80.206.125, which belongs to the Israeli AS 44709 (O.m.c. Computers & Communications Ltd), as in almost all recorded cases associated with this group.🏮 The most interesting point is that the Excel documents contained metadata indicating that the document was last edited (and probably created) on a system with a Chinese locale in WPS Office, an analogue of Microsoft Office created by the Chinese company Kingsoft. WPS Office itself supports several languages, including Russian and English, but in the Russian or English version the Heading Pairs field should contain Лист1 or Sheet1, whereas in all four decoy documents the Heading Pairs field contained
工作表, 1, where 工作表 means “worksheet” (screenshot 4).IoCs:
f8f096d2e94bbdbfd20aae45432af58a7bdf3406fa4dde568154b930cac855ca
20b0faa0f058cd71be39075ed1a0294e2a9e7c2f670b7ba5e3e35e6581907122
37bff1efb37a61f1e4d9f9fda43f33db852da01b22b623faedcef20173ee78fa
7c29891b5eacc464620db0a23b2e05b47373b98524aebba05cf3bd8c2b5f42fe
63b7073a8b74dd7810493700881b9afea3627126cbcb1d942e7a01d573207129
4102a0bec73711e754a5ad067d1779cb8c71628b0c38384e41b2041e64ffddba
5df092a5f3d088043cd5724197b63ba239b12edc8cd6dbcf7e3f9d7ce8594426

212.80.206.125
Code language: plaintext (plaintext)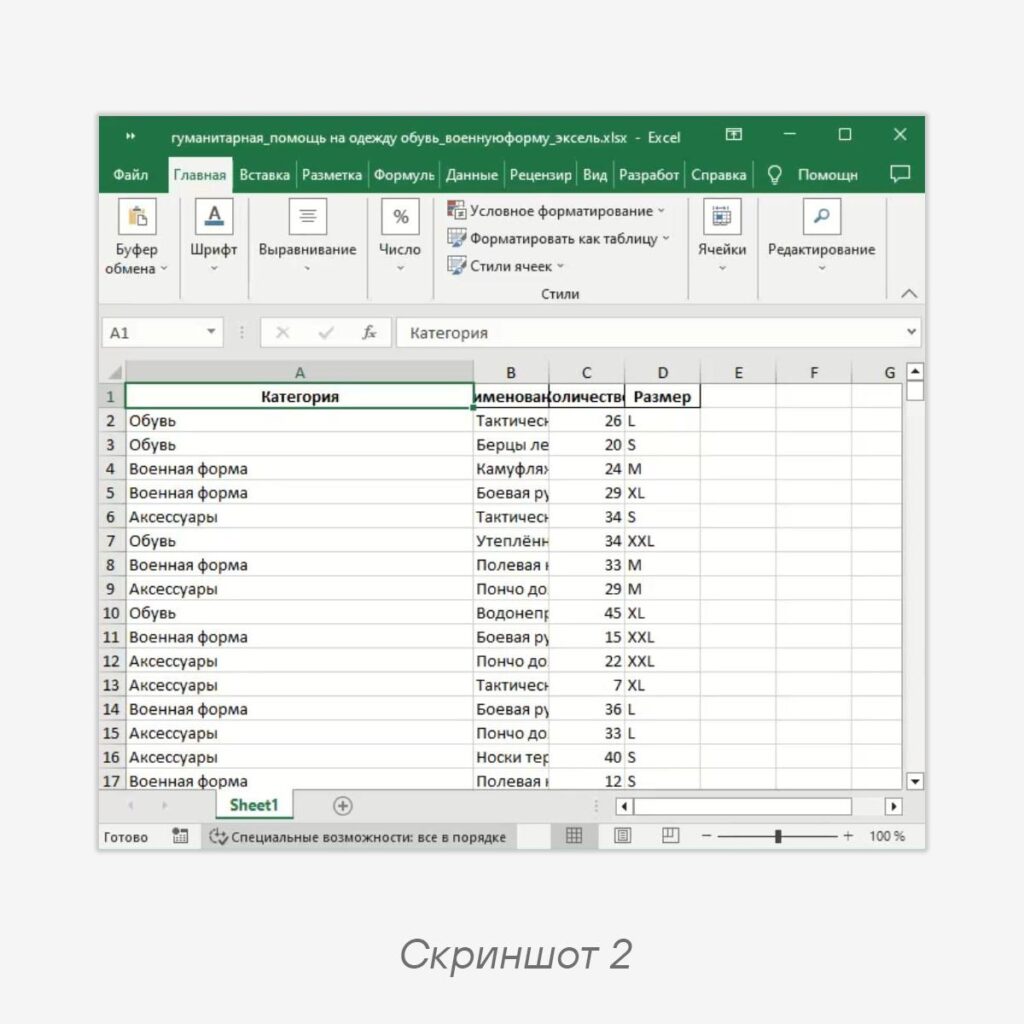
#TI #APT #malware #ioc
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…