
New PhaseShifters Campaign
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Throughout May, the PT ESC cyberthreat intelligence team has been tracking a wave of activity by the PhaseShifters hacking group, which we reported on in January of this year.
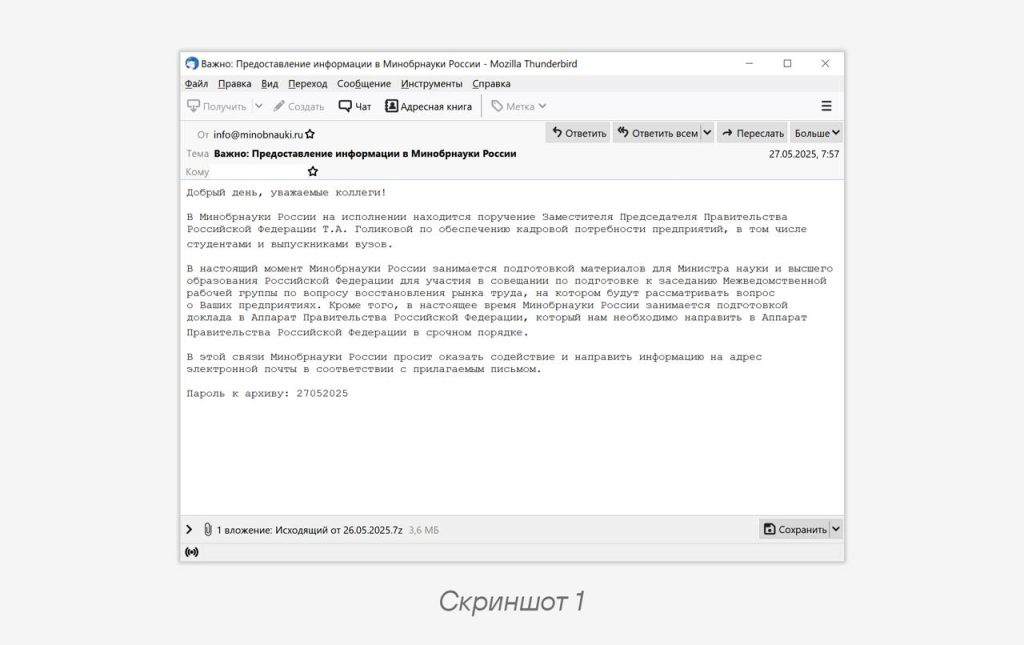
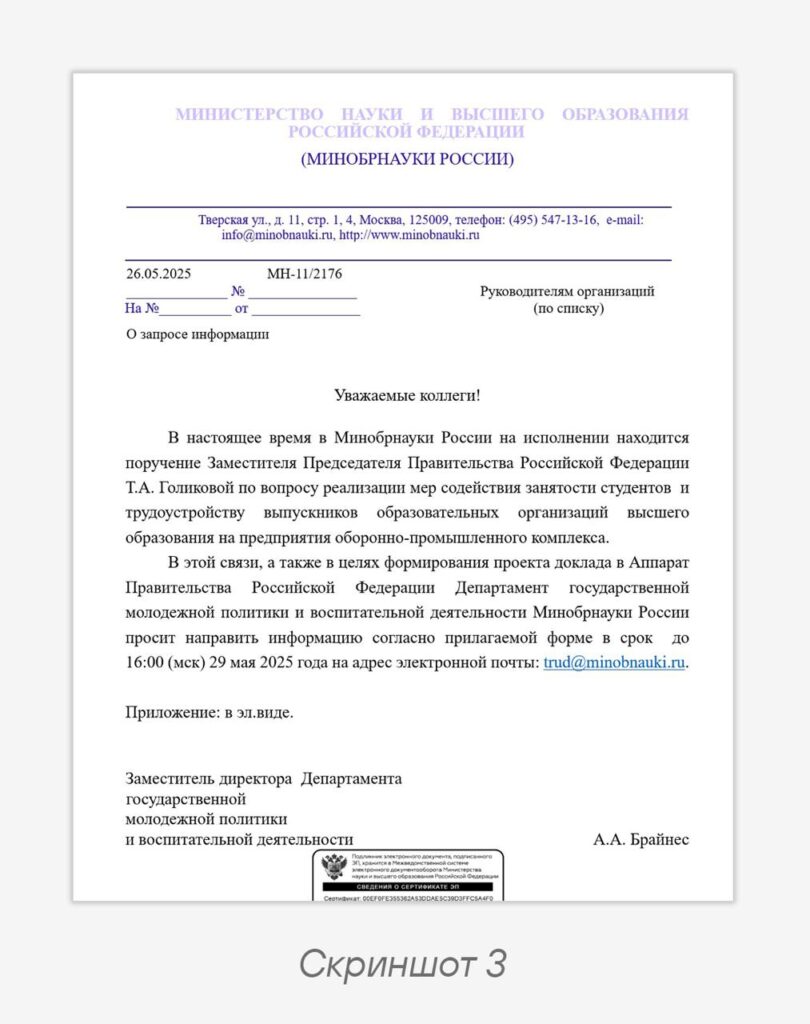
The group is conducting a phishing campaign, posing as the Ministry of Education and Science of the Russian Federation. To organize the campaign, the domain
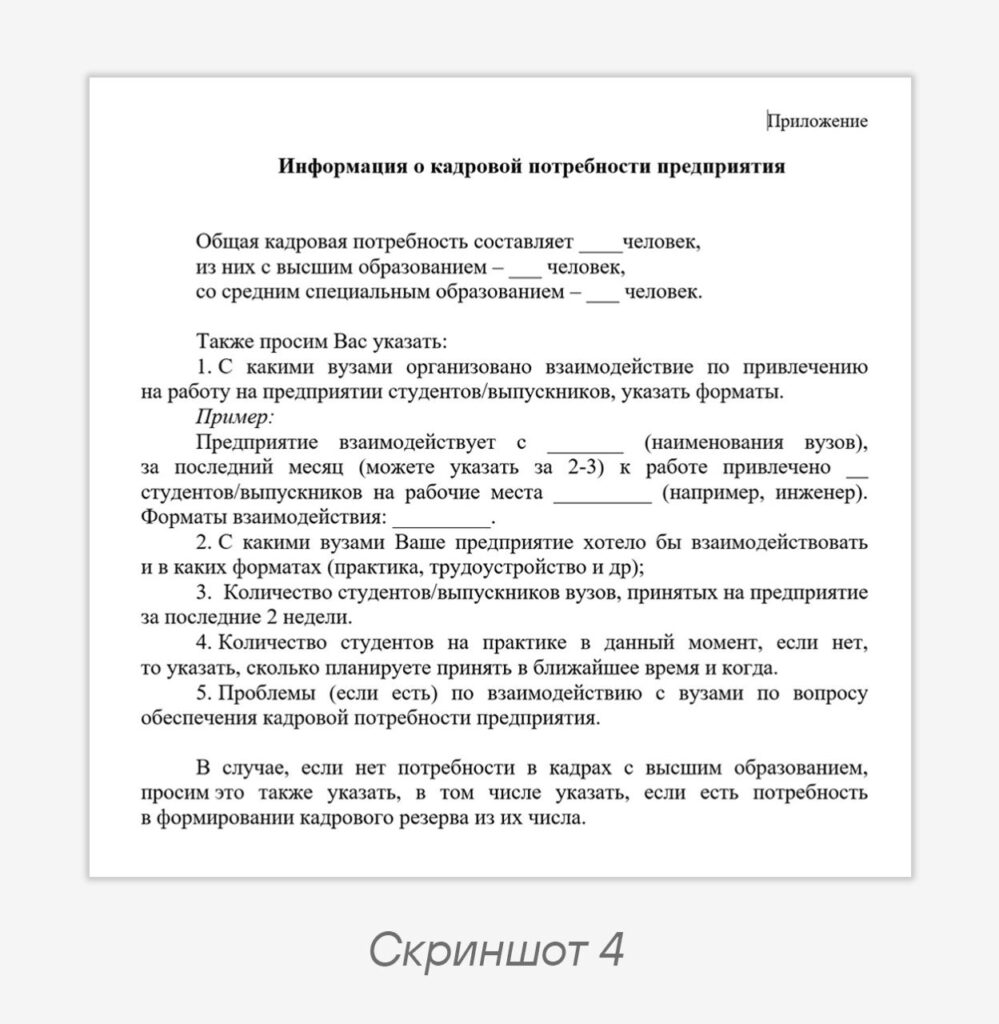
minobnauki.ru was registered, whose MX record points to the IP address 193.124.33.207. The same server also hosted the domain mail.min-prom.ru, from which PhaseShifters previously sent phishing emails on behalf of the Ministry of Industry and Trade.In the body of the phishing emails, the group attaches an encrypted archive containing QuasarRAT malware disguised as an ordinary DOCX document. Inside, QuasarRAT contains the main email, and alongside it in the archive is a separate lure document serving as an attachment to the main file.
During unpacking and execution of the malware, checks are performed for the presence of various antivirus solutions by the keys
bdservicehost SophosHealth AvastUI AVGUI nsWscSvc ekrn, and depending on the result, the launch parameters change slightly.The hidden payload of QuasarRAT is delivered in several fragments with the
.adt extension, and is then assembled into a single executable file by sequentially concatenating them with the commandcmd /c copy /b ..\Quiet.adt + ..\Achievements.adt + ..\Yen.adt + … + ..\Panic.adt k
Code language: plaintext (plaintext)After successfully concatenating the fragments, the malicious program establishes persistence in the system by copying a shortcut to the user’s startup folder, which ensures it launches automatically at system logon.
To disguise itself, the attacker process creates an instance of
RegAsm.exe, into which QuasarRAT is injected, after which a secure connection is established with the command server 5.8.11.119:4782, which hosts the QuasarRAT certificate.Notably, Regasm is not located at the standard path but is copied to another folder, from which it is then launched for subsequent code injection. Such launch variants make it possible to build detections or hunt for system binaries launched from non-standard locations.
This C2 infrastructure has already been used by this group in previous operations, but in those attacks the server configurations used the domains
thelightpower.info and crostech.ru.When analyzing the registration patterns of phishing domains, it was also found that the threat actors prefer to use IP addresses from autonomous system AS41745 (Baykov Ilya Sergeevich).
IoCs:
2b7004cb00d58967c7d6677495d3422e
0bbb3a2ac9ba7d14a784cbc2519fbd64
40ef2615afb15f61072d7cea9b1a856a
681af8a70203832f9b8de10a8d51860a

Prilozenie_k_pis_mu.docx
Pis_mo_zapros_na_predpriatia_OPK.doc.exe.exe
Исходящий от 26.05.2025.7z

193.124.33.207
minobnauki.ru
5.8.11.119
min-prom.ru
mail.min-prom.ru
superjoke.ru
forum-drom.ru
cloud-telegram.ru
about-sport.ru
Code language: plaintext (plaintext)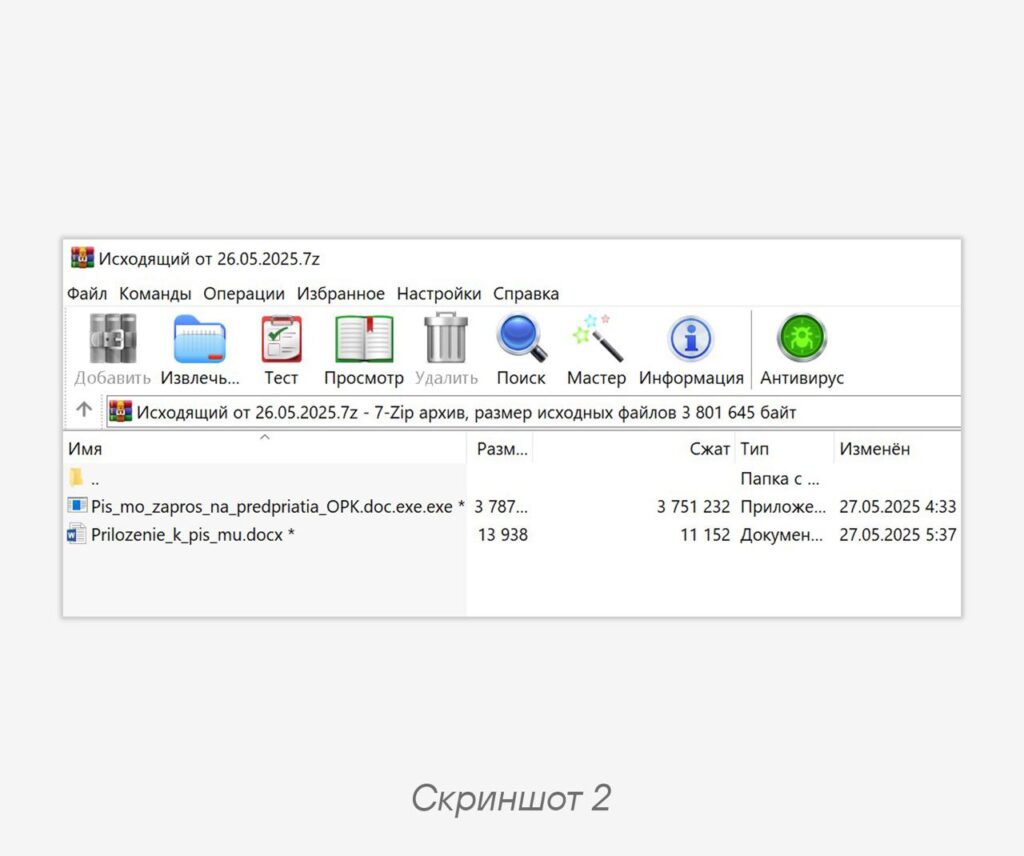
#TI #APT #Phishing
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…