
Repeat, it's hard to see
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Recently, the PT ESC cyber intelligence team discovered an example of a multi-stage phishing attack in which the attackers first tried to win the victim’s trust and then get them to launch a payload.
Watch the hands 👐
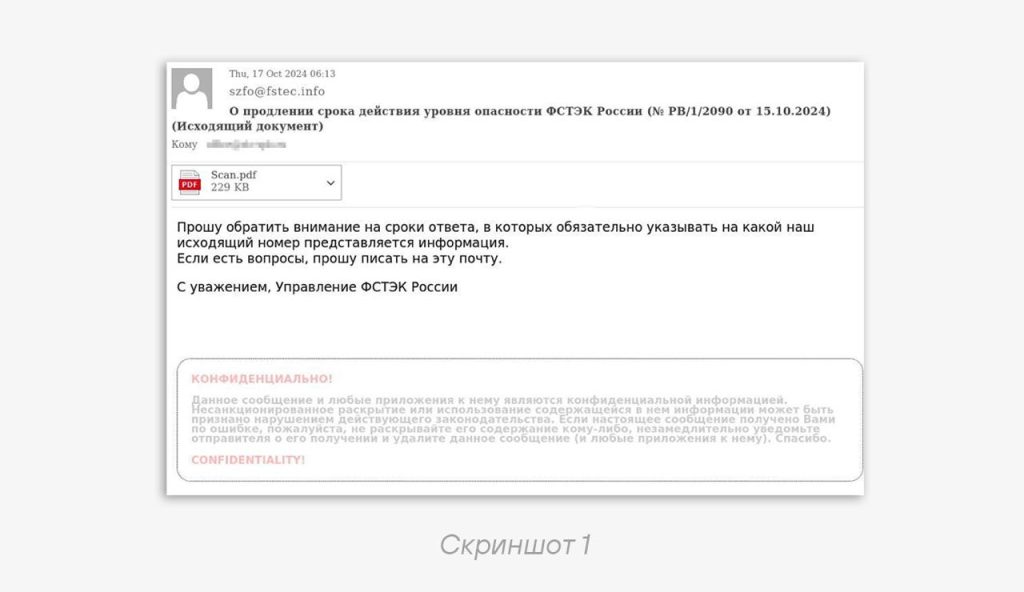
1️⃣ At the end of October, we came across an email sent in the name of the FSTEC Directorate for the Northwestern Federal District (screenshot 1).
The attachment contained a scan of an FSTEC information letter “On extending the validity period of the threat level.” There was no malicious content or any links in it, and the PDF file itself was not dangerous. But the quality of the document scan left much to be desired and was clearly unsuitable for visually reviewing the requirements (screenshot 2).
The domain
fstec.info was used to send the email; it is not an official FSTEC domain and was registered on October 16, 2024.2️⃣ After putting the
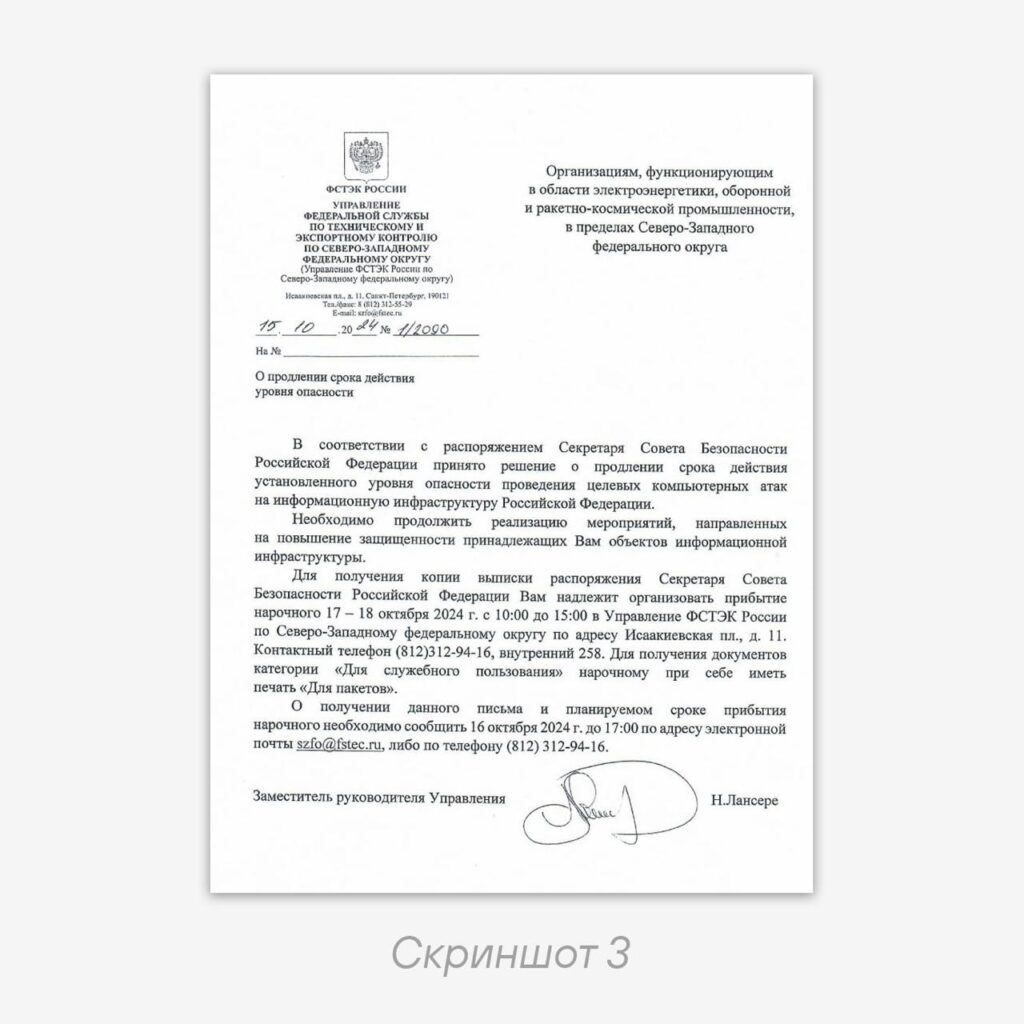
fstec.info finding in the backlog for thorough analysis, a few days later we discovered a higher-quality scan of the same document (screenshot 3), which, on closer inspection, turned out to be an executable file with a PDF icon.This executable launches an
UltraVNC server with a connection to the host toproducts.ru:80, as a result of which a remote control session is created that an attacker can connect to. And to distract attention, that same legitimate document is launched, but now in improved quality (screenshot 3).Most likely, the attackers use a multi-stage social engineering technique: first they send a safe and hard-to-read document, prompting the victim to start a dialogue with them. And after gaining trust, they send them a payload.
🤔 The tactics, techniques, and procedures of this attack are similar to those used by the PseudoGamaredon group (Core Werewolf), but confirmation requires further observation.
IOCs
Sender:
szfo@fstec.info

Scan.pdf
3b6010acae660c9455154b9b847c5b12
0f37bf48736fa806112d0413f42840bbdb75e378
d4878ba0cad42eb7ec012b9f71faa49e0ef2ac48665dbaaec627b603639fc2e7

исх 1-2090 от 15-10-2024_О продлении.exe
e77ab4faa8632a184a1d9e6ea9e6459d
65a538ee9f0e59495281661ee4c68dd08f339d5f
66a3a8cab5d3a88fb1e854f69178b9468cfa4ec49d1b6ba3d4f6d190e57c85a5

Domains:
toproducts.ru:80
fstec.info
Code language: YAML (yaml)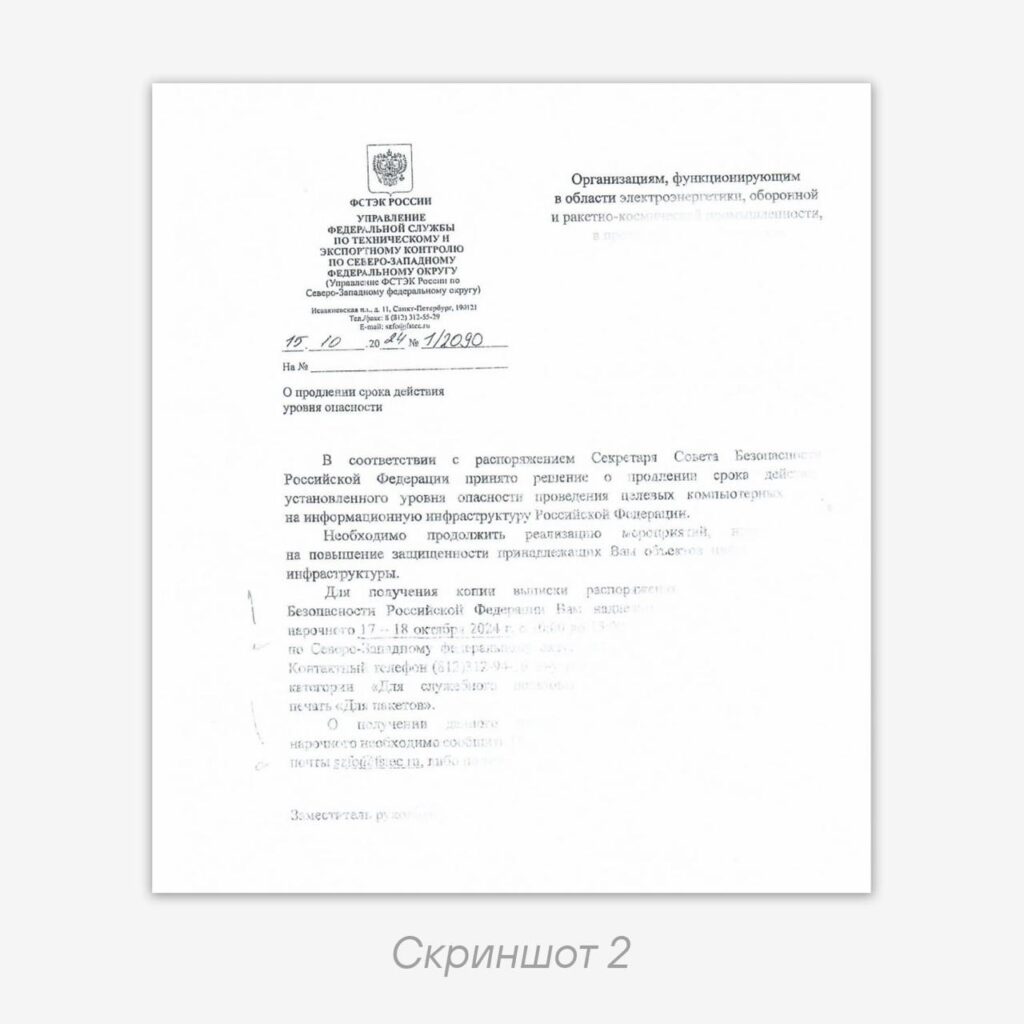
#TI #phishing #ioc
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…