
Slam screen locker. What are you?
More in Malware
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…





Next up is fast malware analysis, conducted on one Sunday evening.
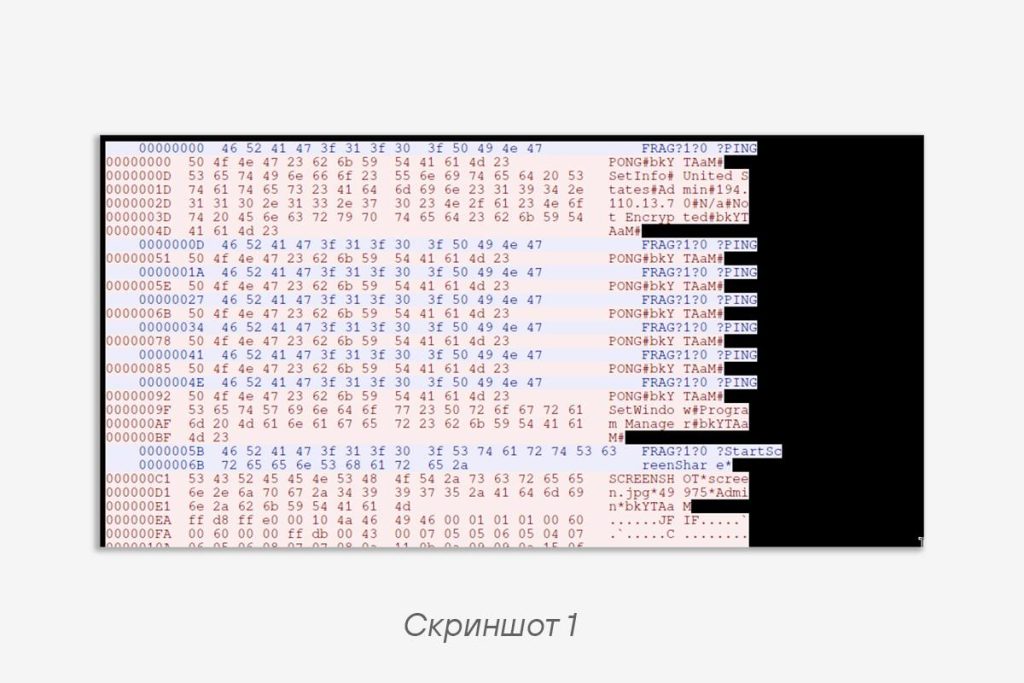
An interesting sample flew into our networks, generating equally interesting network traffic (screenshot 1).
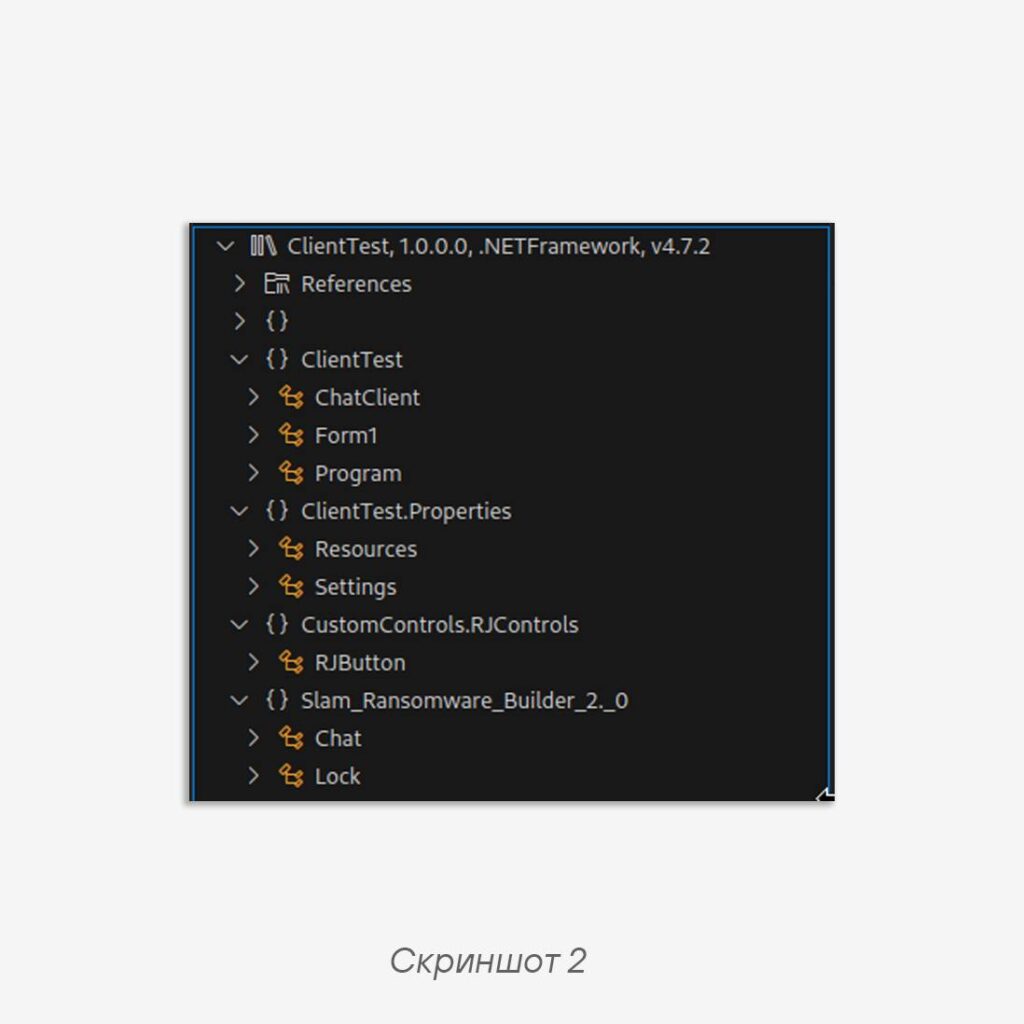
This file (a .NET executable) contains a non-obfuscated namespace Slam_Ransomware_Builder_2._0 (screenshot 2). Its name is all too similar to the well-known-in-narrow-circles Slam Ransomware, just with a bigger version number. An example of builder 1.4 in action — at the link.
🏃♂️ A cursory analysis showed that the class Slam_Ransomware_Builder_2._0.Lock is responsible for locking the screen, and the class Slam_Ransomware_Builder_2._0.Chat implements the chat logic with the locker’s victim.
Of greatest interest is the class ClientTest.ChatClient, which contains the implementation of the network protocol. From it, one can determine the full set of functions of the malware under investigation.
• remote control (for example, LCD*<coord_x>*<coord_y> — emulation of a left mouse button click, Command#<command> — executing a command in cmd, SetStartup*<prog_name> — adding a program to autorun);
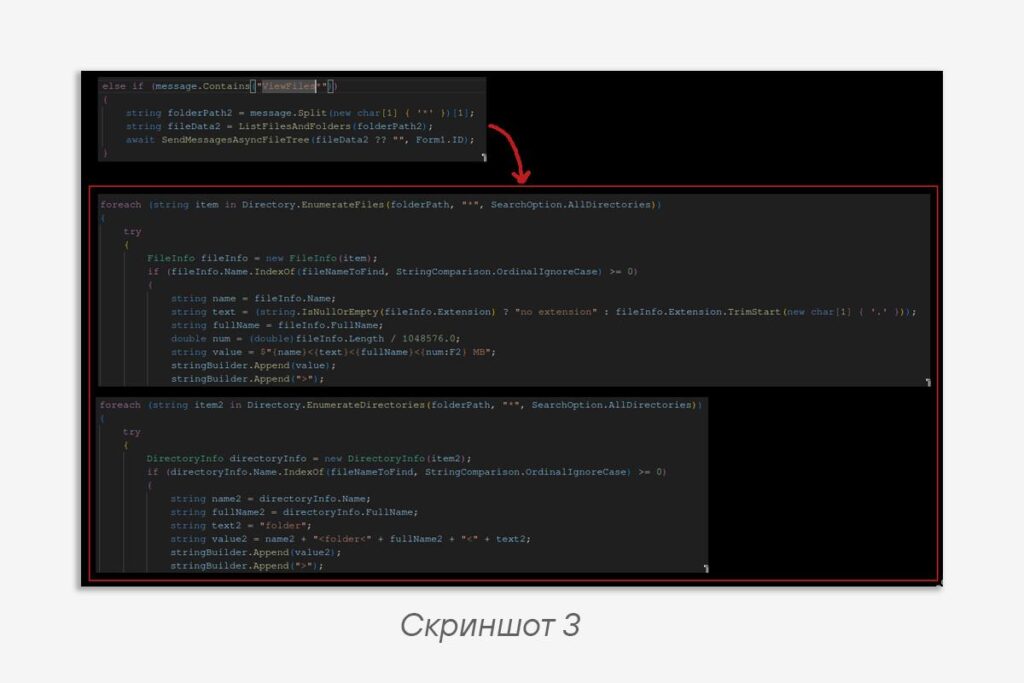
• sending and receiving files (for example, ViewFiles*<dir_path>, the client sends back *FileTree*<files>*FileTree*, screenshot 3);
• taking screenshots (for example, StartScreenShare*, StopScreenShare*, the client sends back SCREENSHOT*screen.jpg*<file_size>*<user_name>*<form_id>);
• keylogger (for example, StartRealtimekeylogger*, StopRealtimekeylogger*, the client sends back SendrtKeylogger*<key_code>*).
And much more — the scale of the RAT is impressive, any video conferencing client would be envious.
😃 The nastiest and most interesting mischief
Command: LOCK*, LOCKUN*.
Action: activate or deactivate the desktop locker.
Command: textts*<text_to_speek>.
Action: text to speech.
Command: msgboxshow*<title>*<msg>*{Error,Information,Hand…}*<buttons>.
Action: show a notification.
Command: Wallpaper*<path_to_img>.
Action: change the desktop image.
Command: BSOD#.
Action: trigger the blue screen of death.
And the very first screenshot shows PING-PONG, which is easily covered by rules with flowbits:
alert tcp $EXTERNAL_NET any -> $HOME_NET any (msg: "Slam V2.0 FB set ping"; flow: established, to_client; dsize: 8<>17; content: "?PING"; endswith; flowbits: set, slam_ping; flowbits: noalert; sid: 1; rev: 1; classtype: trojan-activity;)

alert tcp $HOME_NET any -> $EXTERNAL_NET any (msg: "Slam V2.0 ping-pong"; flow: established, to_server; dsize: 8<>17; content: "PONG#"; startswith; content: "#"; endswith; flowbits: isset, slam_ping; threshold: type limit, track by_dst, count 2, seconds 240; sid: 2; rev: 1; classtype: trojan-activity;)
Code language: plaintext (plaintext)
IOCs
SHA-256: e42088a37531929e3e775bdfacc5a3ee974e4f59d5290907c2131f434eef345b
C2: 77.231.153.42
Code language: YAML (yaml)
Happy hunting!
#Hunt #C2 #Tips #IOC #detect #malware #network #suricata
@ptescalator
More from global_author
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…

More in Malware
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…