
"Tax Audit" from East Asia
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




onmbv.com, for example: TAX@notifications.onmbv.com, TAX@news.onmbv.com
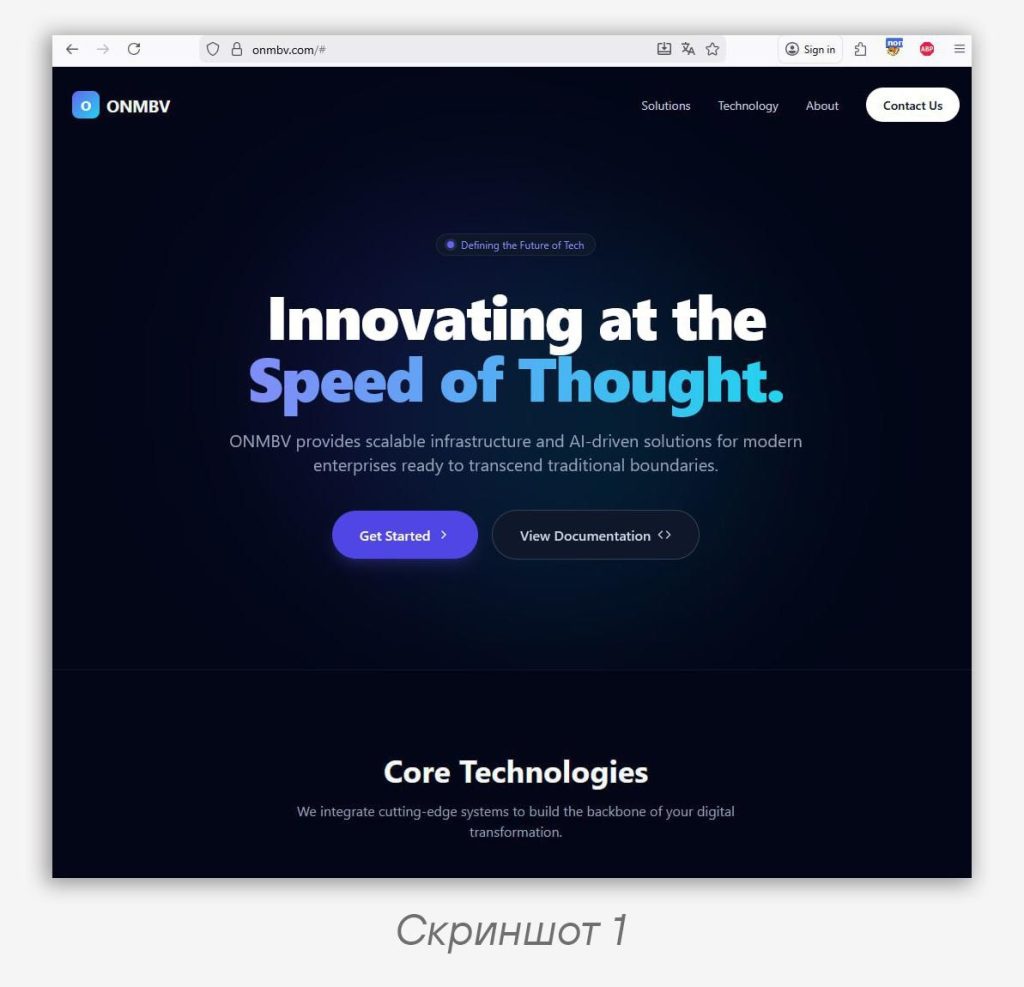
The domain onmbv.com itself was registered on 2025-09-14. If you visit the website, ONMBV positions itself as scalable infrastructure with modern technologies. However, the site itself looks like a phishing stub with non-functional features, aside from the most basic display with a typical interface (screenshot 1).
The malicious emails contained notifications about a tax audit purportedly from the Federal Tax Service (FNS) and urged users to download a “package of documents” attached to the message (screenshot 2).
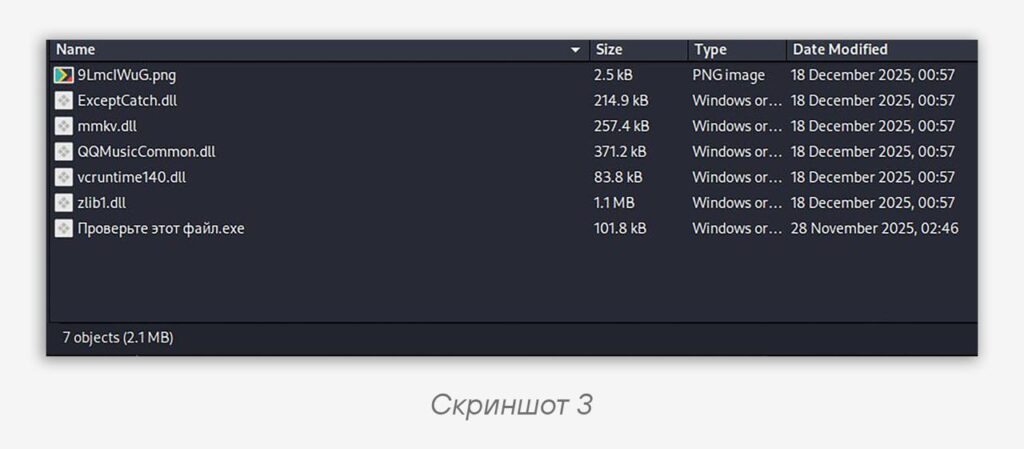
The archives contained several DLL files, .exe and .png. For example, the file -ФНС России.zip (SHA-256: 81e64f5c5b06dd415e4fd60defac5f1573d5c9d83094181bf359f9e5af8765da) contained the files from screenshot 3.
👀 Three files are of particular interest:
• Проверьте этот файл.exe — 2b6679179a67b3c4b24e4708802a15b3bd3655a60aa0de4ce5b39b6814ec31d1
• QQMusicCommon.dll — 9a037129dd9fd9f2f776c7d996b82dac76042ae0f69c765522ff2f0904d726da
• 9LmcIWuG.png — dc7b25b00804ca264648ea5e280bfec4d818495ad24daa11daa6069a0621d317
The .exe file itself is a clean .exe with a PDF icon as a decoy.
On VirusTotal it was uploaded under various names, mostly from Russia:
• Документ.exe
• Откройте и ознакомьтесь с файлом.ex_
• 坏抉抗批技快扶找.exe (Simplified Chinese)
It was also uploaded from Taiwan under the names Namelist.exe and Откройте.exe.
When the .exe is launched, the DLL-sideloading technique loads QQMusicCommon.dll, which masquerades as a component of the popular Chinese music application and service QQ Music. The library itself is obfuscated using Control-Flow Flattening.
The malicious DLL is a dropper that reads and decrypts the payload from the file 9LmcIWuG.png and executes it.
In all cases we discovered, the payload was ValleyRAT, associated with Chinese cybercriminal activity. In our case, the C2 was the IP address 207.56.138.28 from Hong Kong.
🐀 ValleyRAT is a RAT (Remote Access Trojan) type of malware written in C++. It allows hackers to secretly control an infected computer, monitor the screen, steal data, and download additional modules. Some sources call ValleyRAT a variant of the old Gh0st RAT, but it is a separate piece of software with similar functionality. It was first spotted in early 2023 and spreads through phishing and fake installers of popular programs.During further study, we saw that in addition to the “
ФНС” samples, we have many “CBDT” archives, for example “CBDT.zip“. In our case, CBDT — Central Board of Direct Taxes, the Indian equivalent of the FNS.
Although some of the files targeting India used the same C2, during our investigation of archives related to the attacks on India, we discovered an additional C2 that was used predominantly in those attacks — 108.187.37.85. The files associated with this C2 used the same kill chain: .exe, DLL-sideloading, and “images” with ValleyRAT.
Besides India, some files were uploaded from Nepal and Indonesia, but most were still from India. The attacks on Indian companies began earlier than those on Russian ones — in early December. At the time of the attacks, the C2 108.187.37.85 was also located in Hong Kong, but the ASN has since changed (the server is no longer located in Hong Kong).
Given the TTPs used by the software, as well as the likely phishing resource, we assume that the attack may be attributed to the East Asian financially motivated Silver Fox group 🦊
IP
207.56.138.28
108.187.37.85Code language: plaintext (plaintext)0f4da8c2fdd9aaefba2c1d0f6337721ac403bfc7e2177bc38b605e035bfadf60
0f84ecd6bd04a4b5913d305f767f56e53087156ab4f1f4beb128ae17a16dc1d1
1086d5aaced335416cedc3d9ec1ca9aad77afbccc49aa4a4460faf74ee15f0d1
236fa94fa00681030feab630da5e31b5cbefcdbe59d05f010daaa0ec708fcf77
3a7d55c863db954943a43a1a1dd04b8c48f56e6d24f3f012e1c89c235ae44b7f
3d48fdc9f7c1f4b29436ff47c3d5ef493970ca77e4e79f93df85fc402ea82aef
3d20ccf0e05679d1bf088ca78b3ffe9227addad049c46b33bbfa1a2437b8ac62
51379a11387e751a378d405025a66d3514bcf3be85c1bce39666ce685e9ea58f
56a88209101dbf0ec53cc9a1c7a7cae706bbd752d18b6697798a7adf232e7fc7
701f0faf0ec6ff9897ca57ca432ed706e7dcd66031a9562ad4dba7ac1c18d654
81e64f5c5b06dd415e4fd60defac5f1573d5c9d83094181bf359f9e5af8765da
86ea0c005ad74b10fc97af3f7888475c8edab7bdef23b00e5f96bd5d85126c4f
a59d51bf883fb55b2b6b71599aa9da06cac939144f60ab5b19adf0c6f20daa88
a1ed64257af8e9611e06ac3cfd9124eae643f200dd9a04d09a89846618d365dc
a7989bcd4d80bc63d0dbf0477ea518adc38a979c81fb54b104899ec40e93cc51
b76d9da3f165e39706ac18bf0b5c63391a10895a98aa1d94ae018a459bace1fa
bb14e58401fd1d9f49f53e3824873efd4d5e4abb854d0916881fe010eca71c01
bc06467cd87e0b3f3d8fa61a1923a1ed792be53e861f669a55e8d6611ccef139
bff760e249b5dc853d0bbdbb880da92af5b6c662641c678ef7766eb329d25500
095c63062309fc53186bffbbb7b2b0c7665f27b73b809e9cb1818a4157baa8a8
1c5dffd48c2a7408a87cc7b8767395ff234a96f6a9e95a7fb807624f4c89ef2e
25111d40ae6dd2388f044068f2d13464d3c0c84d1d371f7e237e9a3c773fcaaf
2a035ef28877e8eb10bb1fe59aad0080b902cb5fa9ca307c4208afed45cbcd50
3296bd88e0a85ebad4f429878bf8bca16ac43e609133b4781f88a339c37bfe9f
50dd0af7bae4f476b757097f0730ed5d297799b34e53aafeaa14e5be73921234
628180916e70a07df3de917fcd2038bcf645923523307f4c5ca50595f4917eb8
83f56c57101a3a524cd3da2aba762acb4a72e651290b0b5caaf022a477a30e84
9e75b289d692968de0f951323f5e45d38b758ecf247adb39370f699cb9ee857a
a8f0d406c3f0d5e0bbac8e014e6dc79ba9f195a4490653835906383af3747856
b5210853def4430a10b88dc669b123dbbd91e290e88f8942ac1bbe54f1508a1f
e0c36e483a1a80dfe7e3b2ffa5e00cd4e01208ed7311f7e2a403878bbe1c270c
e416e872086c2578d88e0a096fef613b88a68a57b220cc33d5ae9bd452355937
ea11cfbf1ac6e77506ff7b904056e9034599fe2e78bd3fa56b082dec7abaf49f
ec11e3db546c0738337123ef39048b207534be052fad9085f39fc6556431a45d
f74fae0fad77f7b4f4be37cd305c8f07d33098e82a0405ee37131ef0a975ef37Code language: plaintext (plaintext)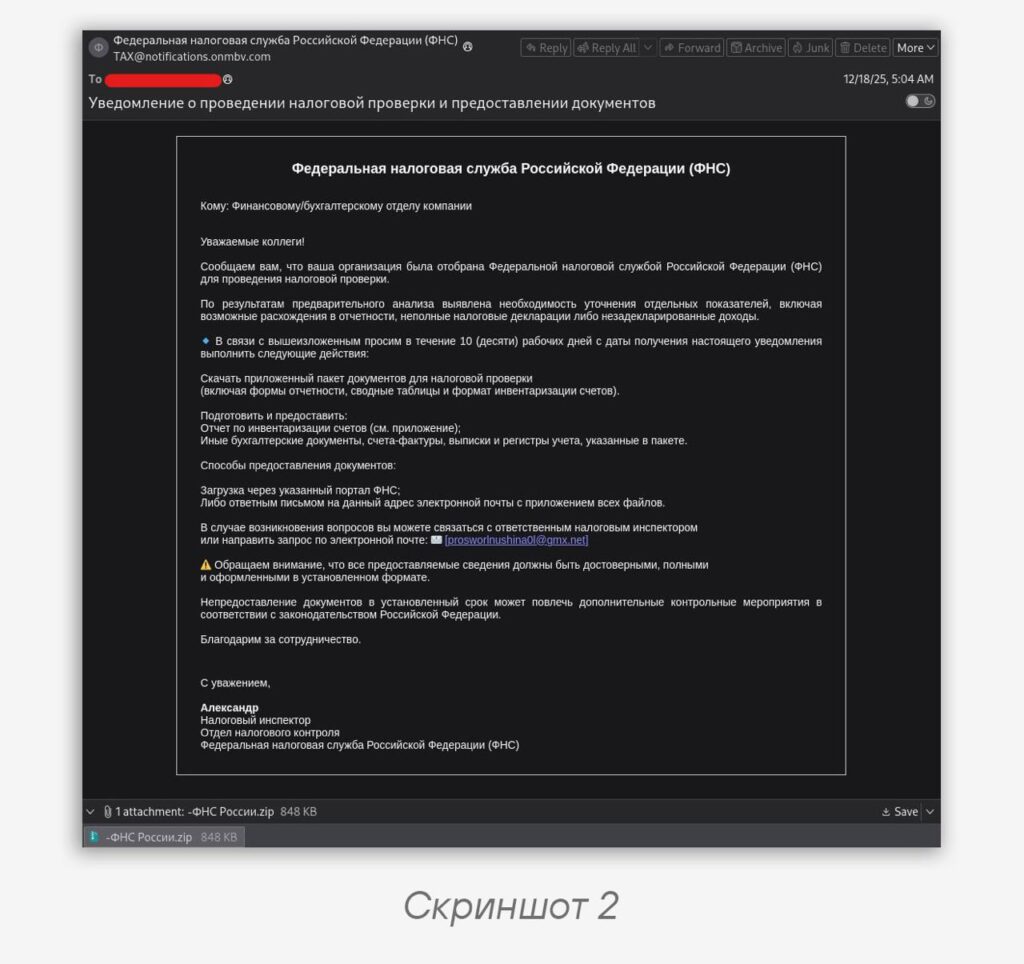
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…