
Dirty Frag 🐧
More in Phishing & sandbox
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
- PT ESC cyber intelligence group presented an overview of cyberattacks for Q2 2026 ✍️
PT ESC Cyber Intelligence Group presented an overview of cyberattacks for Q2 2026 ✍️ The report…
- Citizen, update yourself 🫵
Citizen, update yourself 🫵 Recently, a sample mir-pay.apk flew into our sandbox. At first glance, nothing…
- NetMedved: summer campaign against Russian organizations
NetMedved: Summer Campaign Against Russian Organizations 🐻👍 The PT ESC cyber intelligence group has recorded a…
- AI-95 with a malicious additive ⛽️
AI-95 with a malicious additive ⛽️ In mid-June, the Threat Intelligence team discovered several resources at…

Dirty Frag 🐧💥
A week after the widely discussed Copy.Fail, researcher v4bel disclosed a new privilege escalation technique in the Linux kernel — Dirty Frag.
As of May 8, Dirty Frag has no CVE number and, more critically, no official patch from the kernel maintainers either. Dirty Frag belongs to the same class as Dirty Pipe and Copy.Fail, but uses a different mechanism: instead of pipe_buffer, it attacks the sk_buff structure.
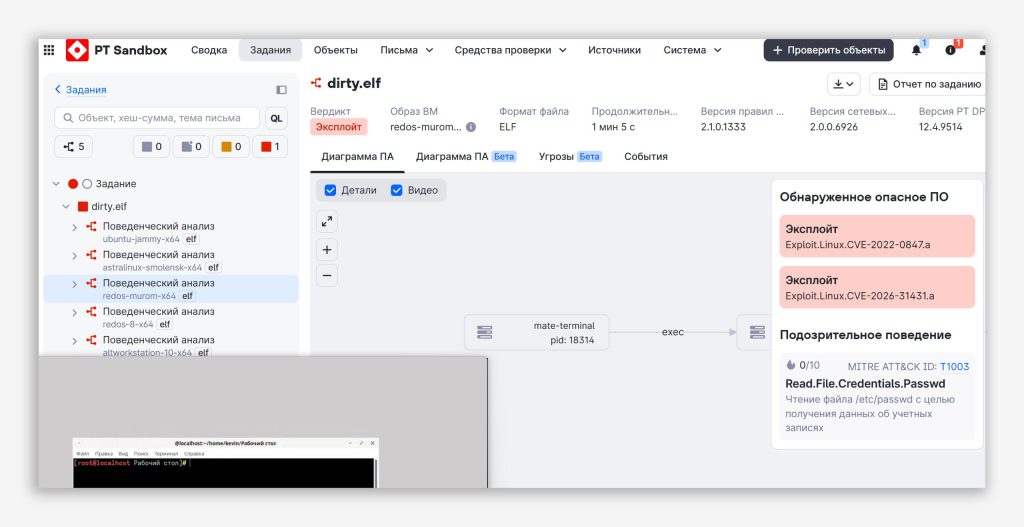
The shared mechanisms of operation allow the exploit to be reliably blocked by behavioral expertise in PT Sandbox (Exploit.Linux.CVE-2022-0847.a, Exploit.Linux.CVE-2026-31431.a, Backdoor.Linux.Generic.a) — see the screenshot.
How does it work? 🧐
Dirty Frag is a chain of two vulnerabilities that complement each other to cover all major distributions:
1️⃣ Page-Cache Write (since 2017): provides the ability to write 4 bytes to the page cache, but requires the right to create user namespaces, which on some systems (e.g., Ubuntu) may be blocked by AppArmor.
2️⃣ RxRPC Page-Cache Write (since June 2023): does not require namespace privileges, but the rxrpc.ko module is present only in some distributions, including Ubuntu, where it is loaded by default.
By combining them, an attacker gets a working exploit on any system, which allows:
• Replacing suid files (e.g., /usr/bin/su) with their own version
• Modifying /etc/passwd by clearing the root user’s password
Who is at risk? ⛳️
Virtually all systems with a Linux kernel released since 2017. The researcher confirmed the exploit works on the following versions: Ubuntu 24.04.4, RHEL 10.1, openSUSE Tumbleweed, CentOS Stream 10, AlmaLinux 10, Fedora 44, and others.
How to protect yourself? 🔧
Since there is no official patch from the kernel maintainers yet, the only way to protect yourself is to immediately disable and unload the vulnerable kernel modules.
Command to disable:
sh -c "printf 'install esp4 /bin/false\ninstall esp6 /bin/false\ninstall rxrpc /bin/false\n' > /etc/modprobe.d/dirtyfrag.conf; rmmod esp4 esp6 rxrpc 2>/dev/null; true"Some distributions (e.g., AlmaLinux) have started releasing their own patches without waiting for upstream.
UPD: the vulnerability has received an identifier — CVE-2026-43284, and a patch has been added to the kernel code (f4c50a4034e6).
#avlab #cve #linux #sandbox
@ptescalator (X, Max)
More from global_author
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…




More in Phishing & sandbox
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
- PT ESC cyber intelligence group presented an overview of cyberattacks for Q2 2026 ✍️
PT ESC Cyber Intelligence Group presented an overview of cyberattacks for Q2 2026 ✍️ The report…
- Citizen, update yourself 🫵
Citizen, update yourself 🫵 Recently, a sample mir-pay.apk flew into our sandbox. At first glance, nothing…
- NetMedved: summer campaign against Russian organizations
NetMedved: Summer Campaign Against Russian Organizations 🐻👍 The PT ESC cyber intelligence group has recorded a…
- AI-95 with a malicious additive ⛽️
AI-95 with a malicious additive ⛽️ In mid-June, the Threat Intelligence team discovered several resources at…