
We will croc you
More in Threat actors
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
- PT ESC cyber intelligence group presented an overview of cyberattacks for Q2 2026 ✍️
PT ESC Cyber Intelligence Group presented an overview of cyberattacks for Q2 2026 ✍️ The report…




We will croc you 👻
PhantomCore continues to actively exploit misconfigurations in 1C to attack Russian organizations.
We previously wrote about attacks on 1C using 1cshell (1, 2, 3).
During the incident investigation, the PT ESC IR team discovered the compromise of a 1C server running on a Linux-family operating system 🐧
Among the characteristic indicators are the presence of malicious executable files in subdirectories of the home directory of the service user usr1cv8 and commands in the .bash_history of the same user — in particular, viewing and deleting the file res.txt, into which the result of code execution via 1cshell is written.
/home/usr1cv8/.bash_history: cat res.txt

/home/usr1cv8/.bash_history: rm res.txt
After gaining access to the system, PhantomCore installed a ReverseSSH tunnel, which is typical behavior for this group.
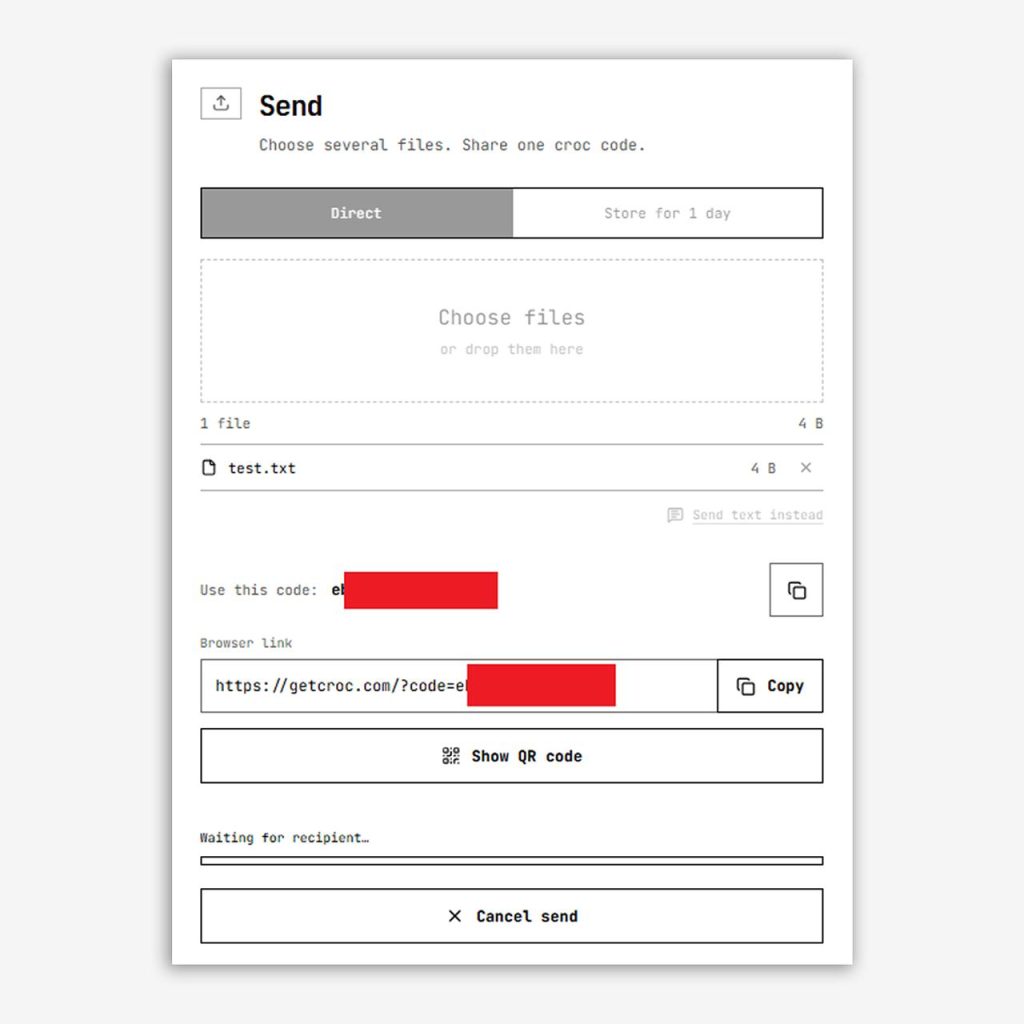
🕵️♂️ In addition to the frequently used tooling, we also encountered a more exotic utility, croc, designed for remote file upload and exfiltration.
On the investigated host, commands of the following format were discovered: CROC_SECRET=[REDACTED] ./croc
With its help, the attackers could upload to the compromised host a file that had been previously sent via the web interface https://getcroc.com/ (in the screenshot) or from another computer on which croc is installed.
💡 To search for traces of croc usage, you can look for an executable file with the corresponding name, as well as the use of the CROC_SECRET environment variable.
The domain getcroc.com can serve as a network indicator.
#ir #tip #apt #detect #dfir
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…



More in Threat actors
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
- PT ESC cyber intelligence group presented an overview of cyberattacks for Q2 2026 ✍️
PT ESC Cyber Intelligence Group presented an overview of cyberattacks for Q2 2026 ✍️ The report…