
Drama Rat: a malicious app that, once installed, really does make you sad
More in Malware
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…





Recently, the Department for Comprehensive Response to Cyberthreats (PT ESC IR) received a number of samples of an Android banking trojan with remote control capabilities — Drama Rat.
This malware family spreads through phishing messages in messengers and masquerades as VPN services, banking applications, and other cracked utilities with built-in paid functionality.
During the research, it was discovered that all the applications are droppers-loaders. When the dropper is launched, a “device fingerprint” is sent to the command-and-control server. In response, the C2 server sends a payload that subsequently implements the trojan’s main functions.
📱 For full functionality, the installed trojan needs access to the Android “Accessibility” service — through this, it automatically grants itself the necessary permissions and gains full control over the device.
After installation, the trojan sends information about the device to the C2 server: the Android version, its assigned identifier, battery charge level, network connection type, desktop wallpaper image, data about SIM cards, granted permissions, and other information.
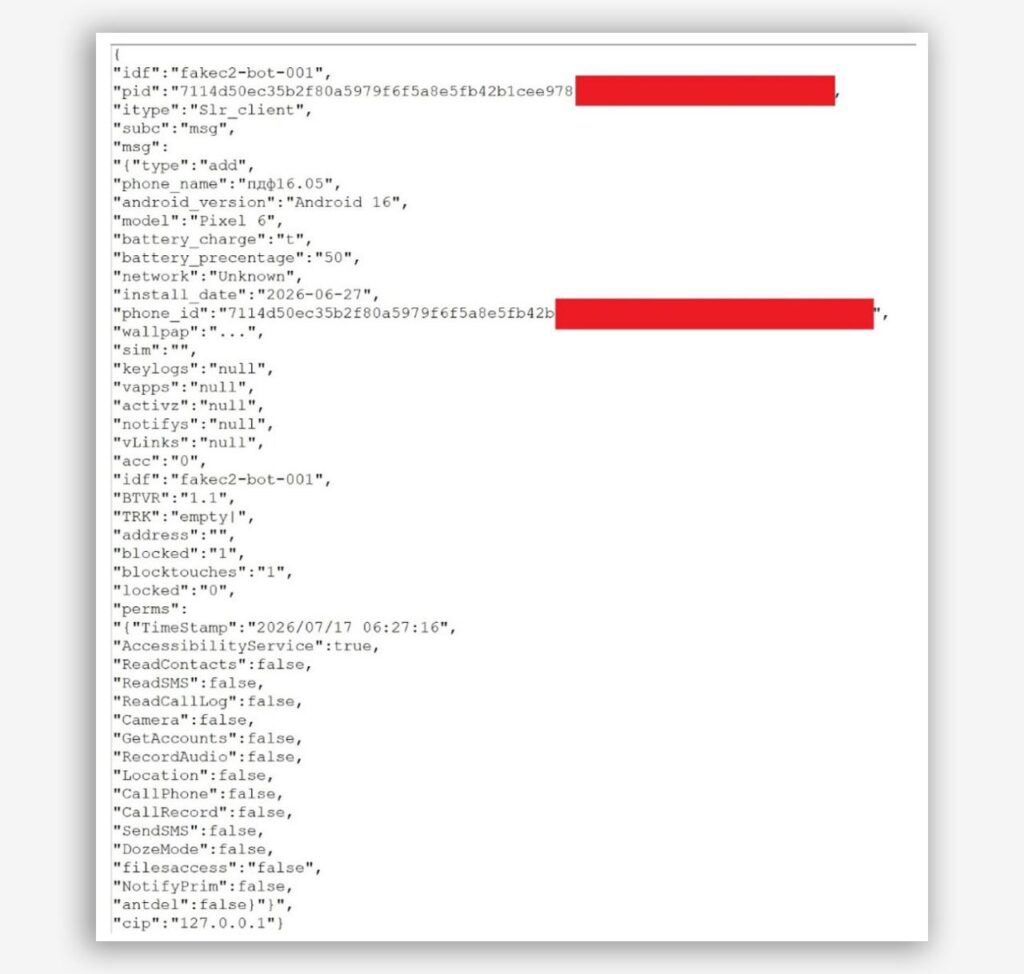
Drama Rat’s capabilities significantly exceed the functionality of ordinary banking trojans.
In addition to the functions that the “Accessibility” service enables (screen taps, access to screen content and the clipboard), the application is capable of recording the screen and video from the device’s camera while hiding the camera-in-use indicator 🟢
Furthermore, the application can read incoming notifications and use the infected device to conduct DDoS attacks on internet resources selected by the attackers.
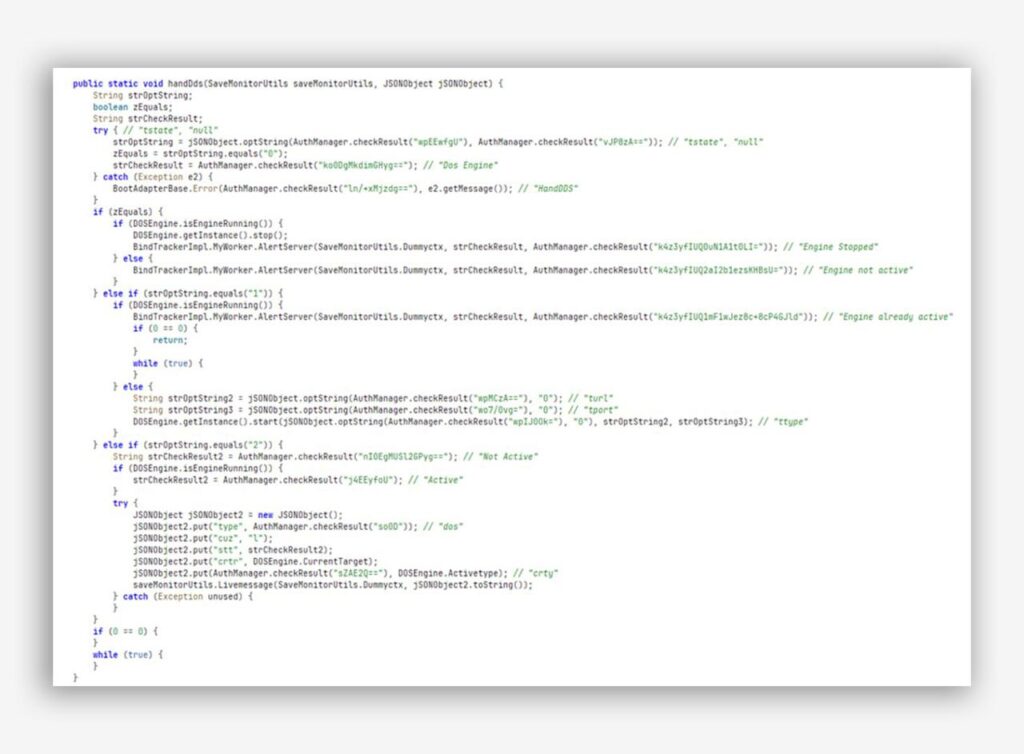
The dropper and the payload are heavily obfuscated: strings are decrypted only at runtime. The application protects itself from dynamic analysis through a number of mechanisms, including root access detection, searching for Frida traces, detecting debuggers, checking whether it is running in an emulator, and others.
At the same time, Drama Rat does everything possible to protect itself from removal and permission revocation: as soon as the device settings are opened, the trojan returns the user to the home screen.
The trojan’s code implements a persistence mechanism using the AlarmManager system service. When individual activities are stopped or crash, it restarts inactive components, ensuring the stable operation of the malicious application.
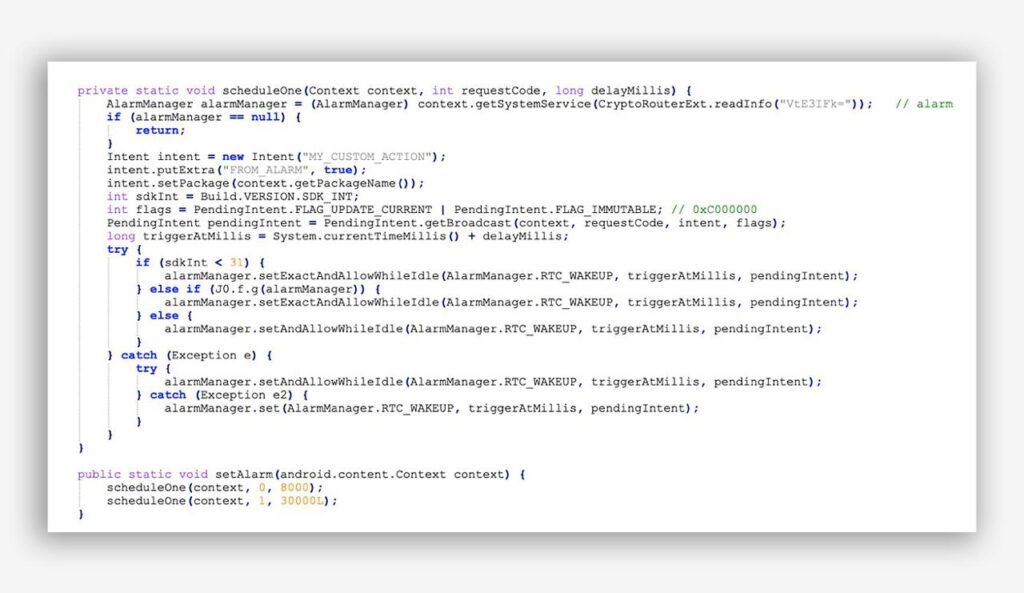
Rebooting the device also will not stop the malicious program from functioning: the use of BOOT_COMPLETED/QUICKBOOT_POWERON/REBOOT filters was discovered, which allow the application to receive a signal from the OS at system startup and relaunch all of its components.
🐭 Drama Rat is not just a banking trojan, but a tool for seizing full control over a device: it automatically grants itself permissions, hides in the system, counteracts removal, and maintains independent communication channels with the server.
The application complicates analysis and tries to conceal its malicious functionality as much as possible.
Read more technical details and recommendations in our blog on Habr 😮
#ir #malware #android
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…


More in Malware
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…