
A new batch of soup
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




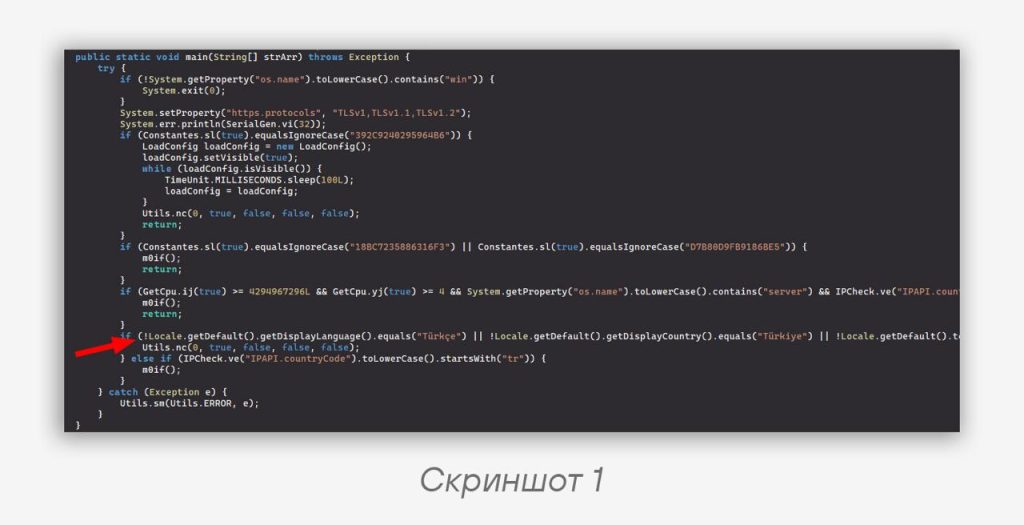
Back in summer 2025, our foreign colleagues already wrote about the SoupDealer trojan — an attack tailored specifically to users in Turkey. The sample had many distinctive features, the key one being that it was a JAR file with multiple AllatoriObfuscator obfuscation techniques and anti-dynamic-analysis protections. For example, it only runs on devices with the Turkish locale (screenshot 1). We won’t go into all the details — the family has already been thoroughly investigated.
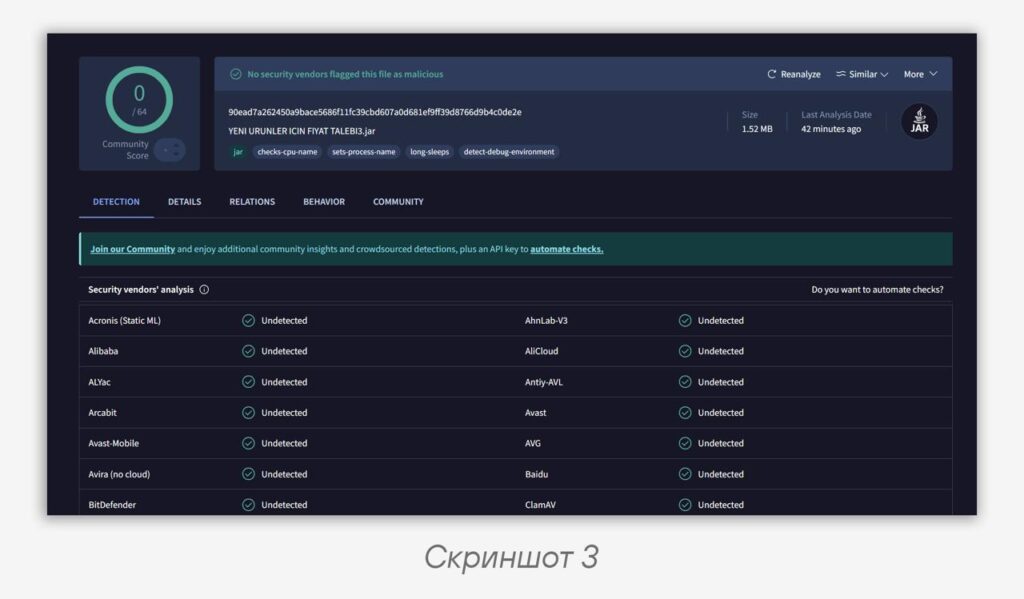
Today we noticed that a new wave of attacks using the same family has begun (screenshot 2), which was blocked in our PT Sandbox. They all roughly follow the same pattern: an email with a Google Drive link asking to review documents; the link leads to a malicious JAR file. And we wouldn’t have paid attention to this (we block a huge number of samples every day), but at the moment not all samples are still detected by popular security tools (screenshot 3).
So — we’re publishing indicators of compromise so that security tools can promptly update their expertise.
Sender addresses:
arslan@arsavukatlik.com
bilgi@dermamed.com.trCode language: plaintext (plaintext)
C2:
gocmenkusgiller.blogCode language: plaintext (plaintext)File names:
YENI URUNLER ICIN FIYAT TALEBI3.jar
FIYAT TEKLIFI BEKLENEN URUN LISTESI.jarCode language: plaintext (plaintext)
File hashes SHA-256:
90ead7a262450a9bace5686f11fc39cbd607a0d681ef9ff39d8766d9b4c0de2e
8dc7f7d298291c042e9f51feff3c8d690f4889a9a141e9657d33da7bb8456c7fCode language: plaintext (plaintext)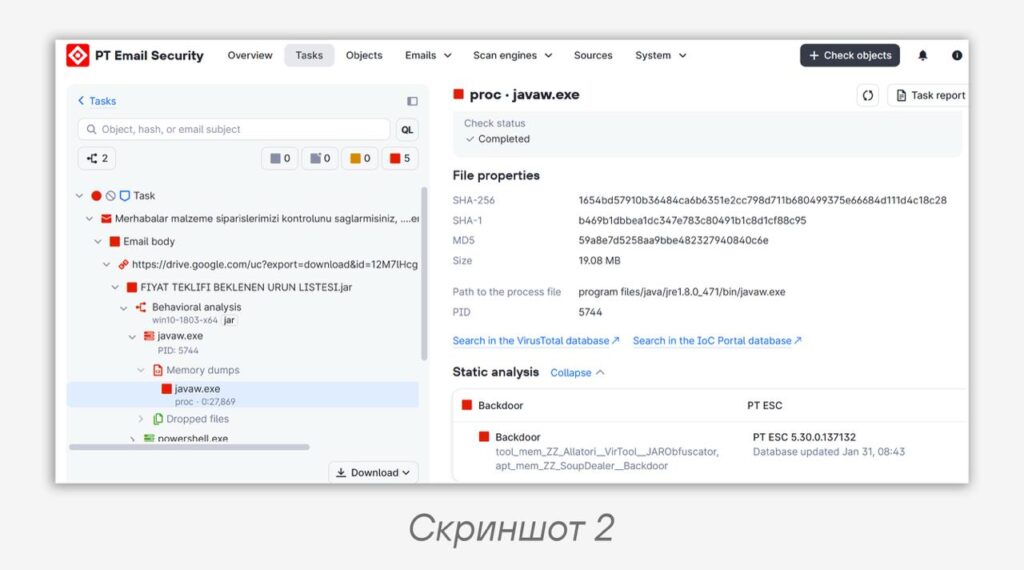
#phishing #ti #ioc #avlab #emailsecurity #sandbox
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…