
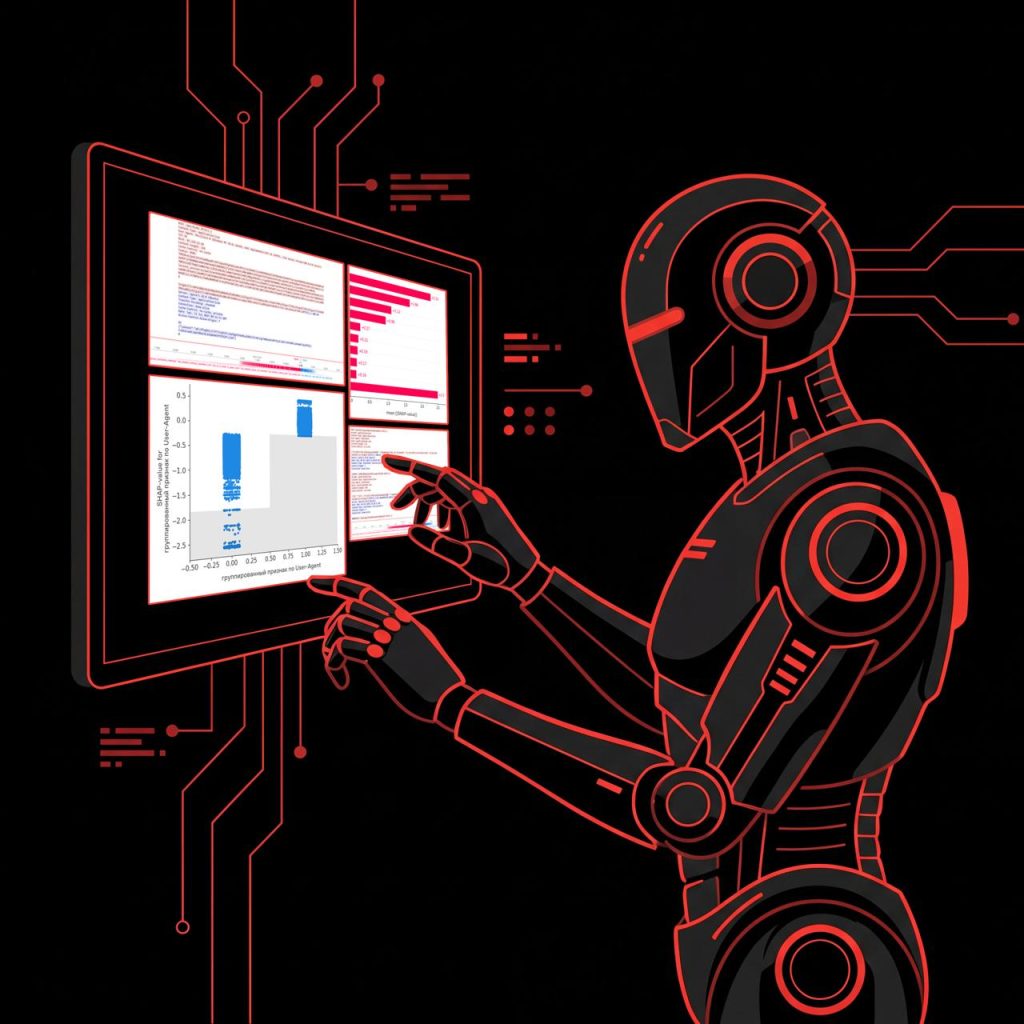
Dissecting network traffic with ML in search of new malware
More in Phishing & sandbox
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
- PT ESC cyber intelligence group presented an overview of cyberattacks for Q2 2026 ✍️
PT ESC Cyber Intelligence Group presented an overview of cyberattacks for Q2 2026 ✍️ The report…
- Citizen, update yourself 🫵
Citizen, update yourself 🫵 Recently, a sample mir-pay.apk flew into our sandbox. At first glance, nothing…
- NetMedved: summer campaign against Russian organizations
NetMedved: Summer Campaign Against Russian Organizations 🐻👍 The PT ESC cyber intelligence group has recorded a…
- AI-95 with a malicious additive ⛽️
AI-95 with a malicious additive ⛽️ In mid-June, the Threat Intelligence team discovered several resources at…

Dissecting network traffic with ML in search of new malware 📖
🧪 We — the network expertise department team of the ESC antivirus laboratory and the machine learning team — once built an ML model on network traffic, trained it on real network sessions, and launched it in the PT Sandbox sandbox to enhance malware detection capabilities. But we decided not to rest on our laurels — we conducted a series of new experiments, expanded the set of input features, and tested the model on more complex scenarios.
👾 Thanks to the update, the model has already managed to catch several previously unknown samples: a new version of the Oyster backdoor, the APT GOFFEE loader, several stealers (for example, JustAskJacky), and a number of other small but suspicious loaders.
💡 This experience confirms that machine learning is an excellent assistant to traditional signature-based solutions: it sees hidden patterns and increases the overall detectability of malicious network scenarios.
We talked about all this and more in our article on Habr.
#network #avlab #ml
@ptescalator
More from global_author
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…




More in Phishing & sandbox
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
- PT ESC cyber intelligence group presented an overview of cyberattacks for Q2 2026 ✍️
PT ESC Cyber Intelligence Group presented an overview of cyberattacks for Q2 2026 ✍️ The report…
- Citizen, update yourself 🫵
Citizen, update yourself 🫵 Recently, a sample mir-pay.apk flew into our sandbox. At first glance, nothing…
- NetMedved: summer campaign against Russian organizations
NetMedved: Summer Campaign Against Russian Organizations 🐻👍 The PT ESC cyber intelligence group has recorded a…
- AI-95 with a malicious additive ⛽️
AI-95 with a malicious additive ⛽️ In mid-June, the Threat Intelligence team discovered several resources at…