
SMS stealers of Asia: 1000 bots and one study
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




✈️ In our last post, we explained that Telegram is becoming more popular among hackers in the C2 as a service paradigm
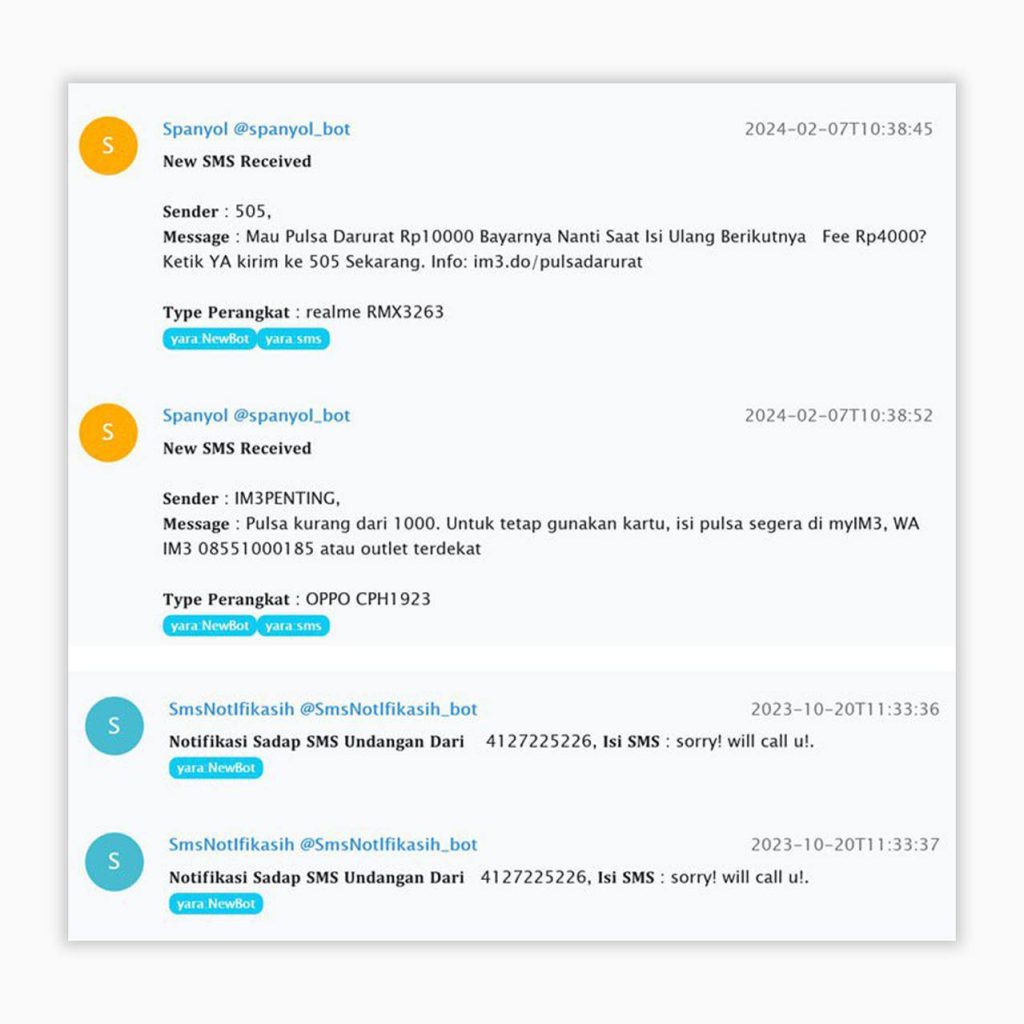
Exfiltration of victim data to attackers’ Telegram bots can occur not only from desktop computers or laptops, but also from mobile devices. It is precisely about such stealers that we released a study today.
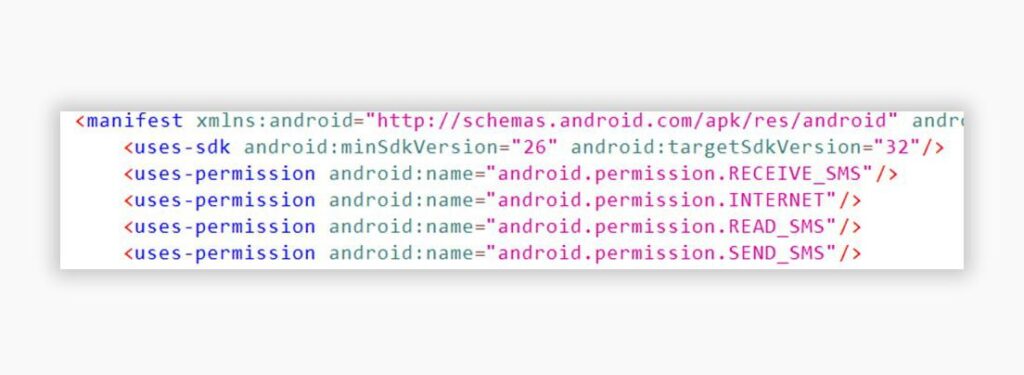
🇮🇩 Most often, the victims of attacks are residents of Southeast Asia, primarily Indonesia. In our study, we identified two families of Android malware that intercept SMS messages and relay them to Telegram bots. We named these families SMS Webpro and NotifySmsStealer.
With their help, hackers intercepted notifications from apps such as WhatsApp or banking services and uploaded photos from the device.
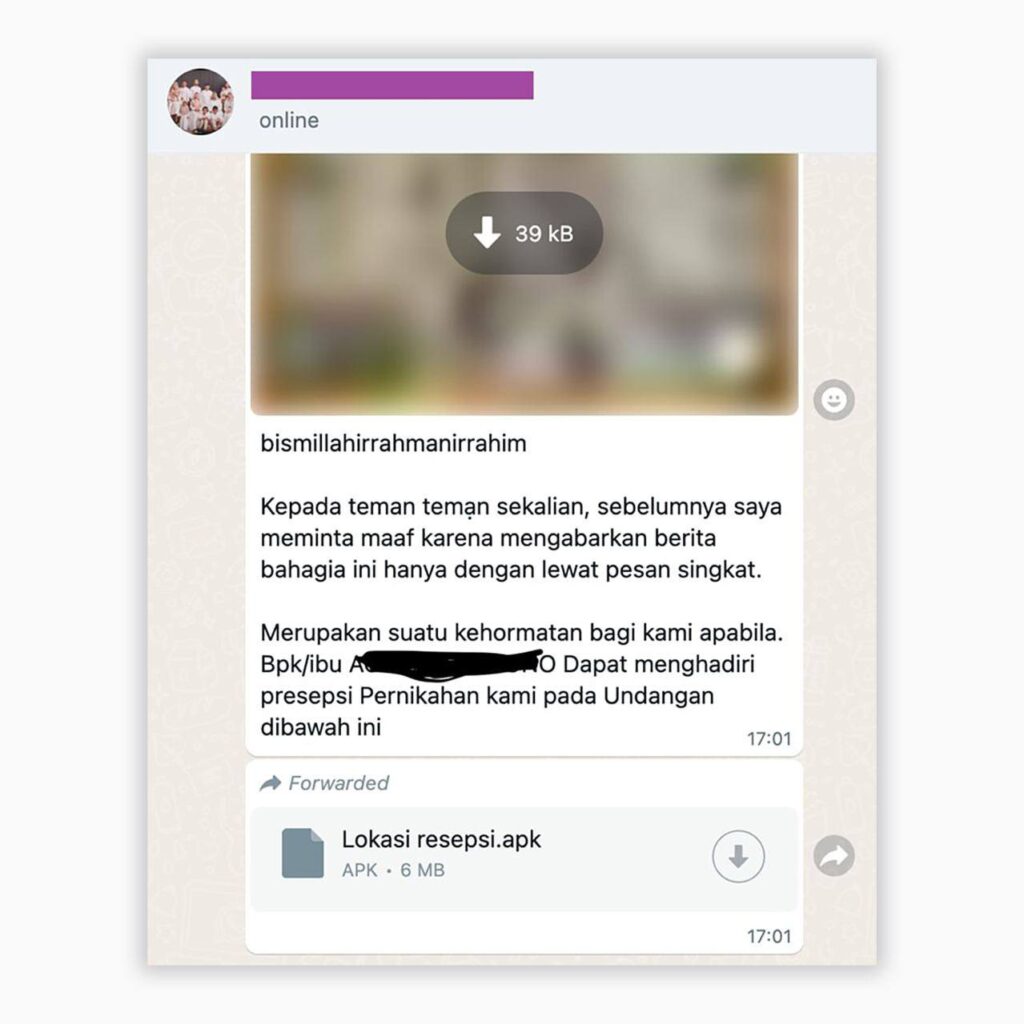
The main infection vector is phishing via WhatsApp. In messages, hackers distribute either the malicious APK files themselves or links to them. According to our assumptions, the attackers’ goal is to intercept the one-time password for a personal online banking account, log into the victim’s account, and steal funds.
#tips #android #cybercrime #TI
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…