
How attackers are changing their approach to writing phishing emails
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




📬 How attackers are changing their approach to writing phishing emails
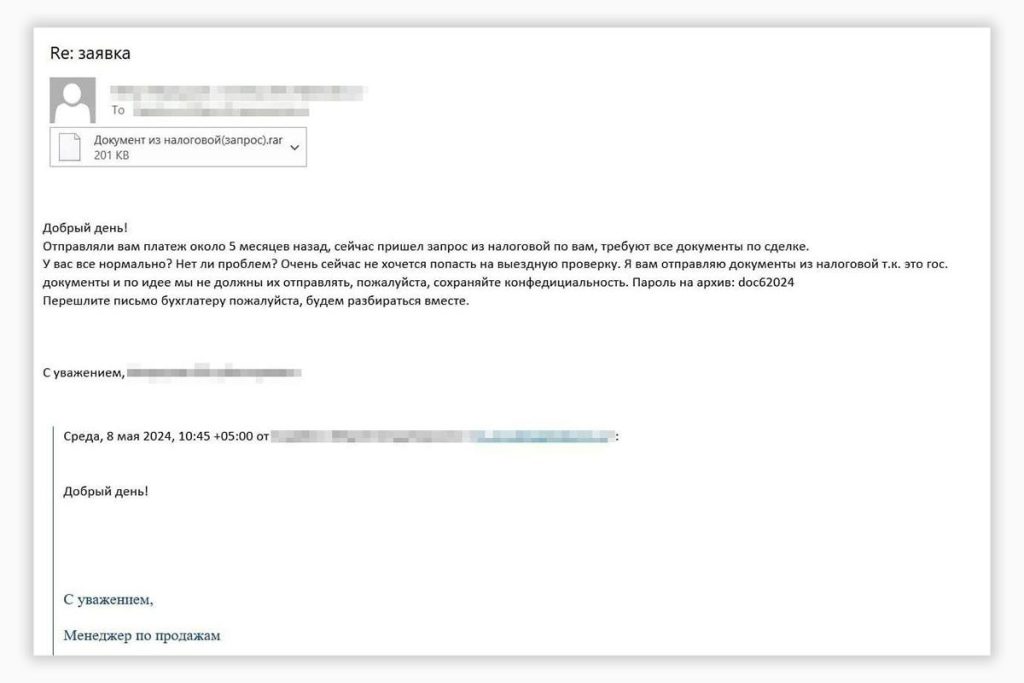
Recently, we came across an email with a malicious attachment sent by the group Hive0117. The writing approach is interesting: the email differs significantly from typical mass mailings that quite straightforwardly manipulate the recipient’s emotions by emphasizing urgency and attempting to evoke fear.
1️⃣ It looks like a reply to some old message, since people tend to trust already familiar senders more than new ones. It turned out that the sender’s email account had been compromised, and this was a reply to a real email from the past.
2️⃣ Urgency is not stated explicitly, but implied: supposedly a tax audit is currently underway.
3️⃣ To prevent the email gateway from detecting malicious attachments, attackers often use password-protected archives. In this case, the use of a password was justified by the documents being confidential. This aroused less suspicion.
4️⃣ Since Hive0117 is a financially motivated group, their target is the accounting departments of organizations. Therefore, under the pretext of a tax audit, the attackers asked to forward the malicious attachment to the actual target—the accountant. First, in this case, the attackers did not need to know their email address. Second, an email sent from a colleague inspires significantly more trust than one from an external sender.
IoCs:
Документ из налоговой(запрос).rar
a7712ac6ff3873f0106e16385e4b9b30
ba647a209c8d112f00a320a693f83827682e7e52
f226edad9d3a17d28008b376773bca62507d40494c5a1def5c8704a1bb815bae
Документ из налоговой(запрос).exe
85c8c66c34bb60e09e68f882831b1751
f96d695d04f0198fab85aa9bac66799cf2e710ed
8b309519bbb64be63ea3cf0f1ef58c5b36bbb5bf37d39f879ffb55d354937e16
fb0bf2b1.shop
185.189.13.113
http://fb0bf2b1.shop/index.php
#TI #Hive0117 #Phishing
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…