
Attackers are looking for new ways to "open the gates"
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




⛩ Attackers are looking for new ways to “open the gates”
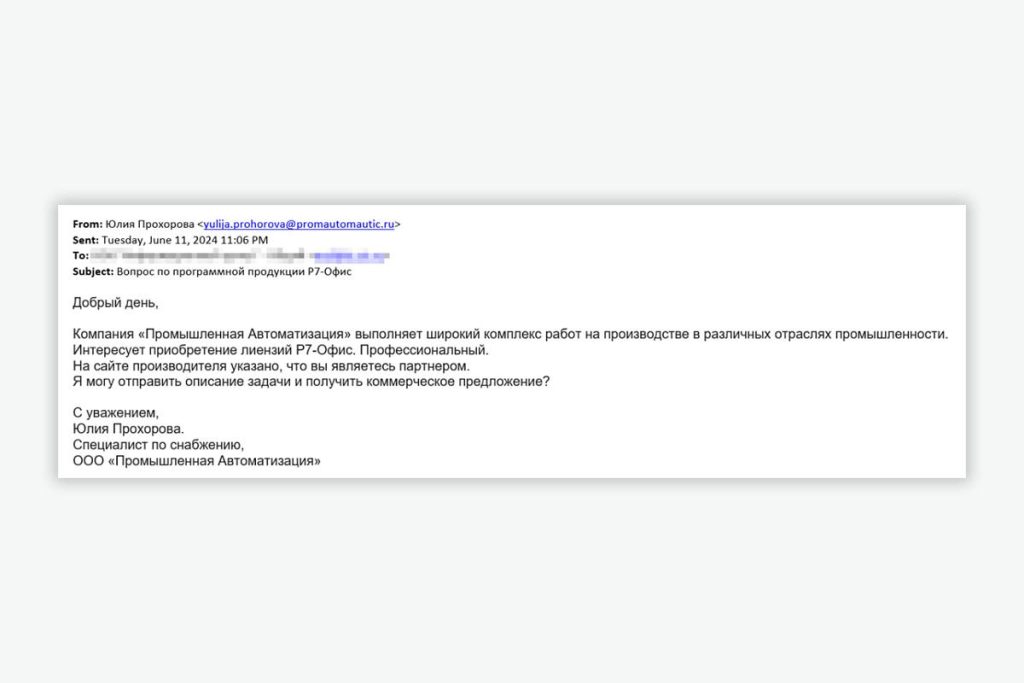
We recently discovered an unusual attack scheme. The attackers first establish contact with the victim, lull their vigilance by posing as an interested company, and after receiving a reply, send the target the malicious attachment they expect.
The urgency of opening the attachment is conveyed implicitly: for example, the sender is going on vacation and a commercial proposal needs to be prepared today, and to do that, the attachment must be opened.
The cybercriminals operate in a time zone between UTC−4 and UTC+4 and are fluent in Russian. It is evident that the text was typed manually, without a translator, which is why there is a typo in it.
👉 The choice of victim is also interesting. Import substitution is more relevant now than ever — there is a large number of requests to distributors of domestic software. Compromising such organizations can open a path to many other companies, including in critically important sectors, through trusted relationship attacks.
In this particular case, the attackers posed as the company “Industrial Automation” and used the domain promautomautic.ru. It differs from the real one by just a single letter and was registered shortly before the attack.
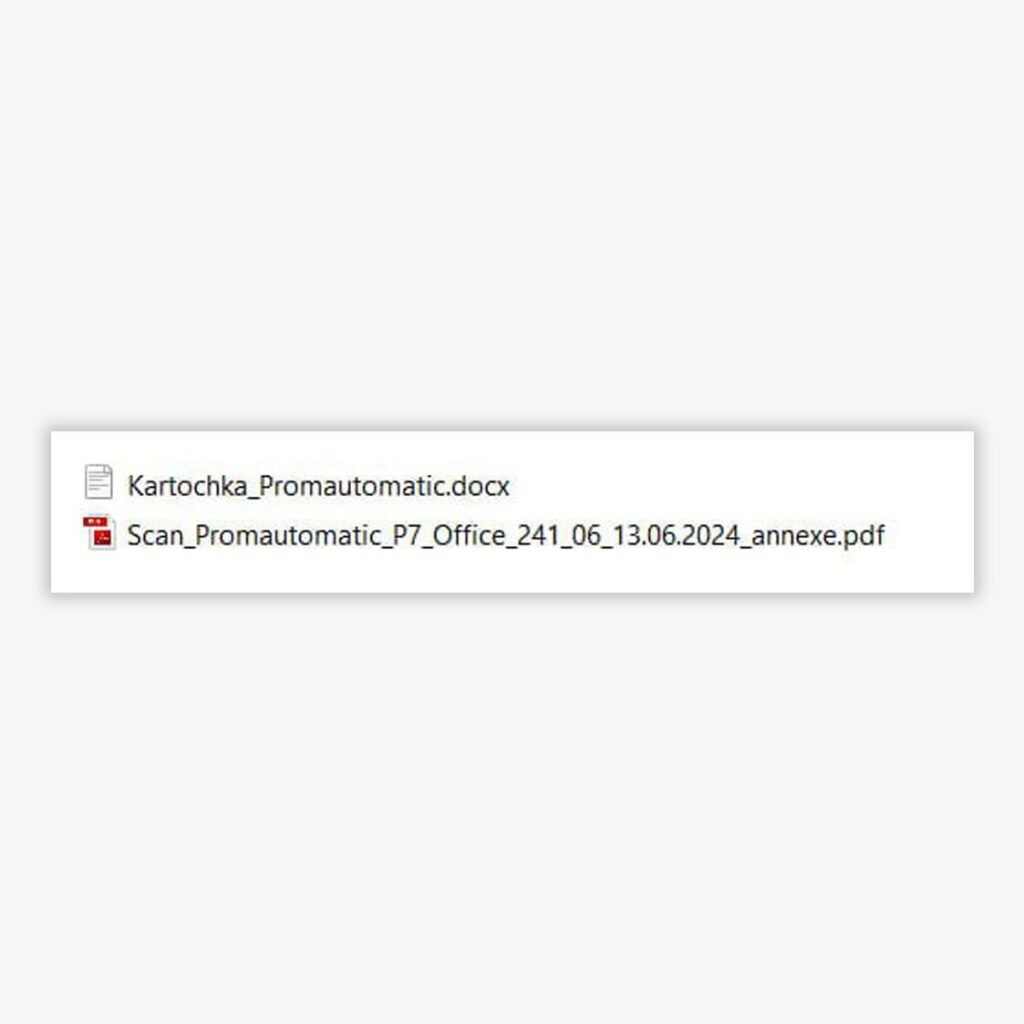
The email had an archive attached, Promautomatic.zip, which contains a DOCX document Kartochka_Promautomatic.docx (a company profile) and an executable file:
Scan_Promautomatic_P7_Office_241_06_13.06.2024_ann←fdp.exe
The file is the DarkGate backdoor, typically used to steal confidential information and gain remote access to a system. DarkGate is distributed under the malware-as-a-service model, which makes identifying the attackers difficult.
The attackers used the RTLO (Right-To-Left Override) control character to change the order of the last characters:
Scan_Promautomatic_P7_Office_241_06_13.06.2024_annexe.pdf
As a result, the victim gets the impression that this is a PDF document rather than an executable file.
IoCs:
promautomautic.ru
45.151.62.66
f81593ac3586e61eb9ee1b332eca2afc
5d586682ff20db587d991716dafa0b231ed7b2f8
f127c29f095f1771c6afc476e4b3adf3442d7f014f39cc47875226f651d64c92
35bd6ff114bbaeaa1b8f959e00042a33
00da82325086c940306d9df23fb8f8d09e044290
70afae352a5f8b2aaab952f2e702aac2fd0b4e38781f3a778b1756e67f779d54
Code language: plaintext (plaintext)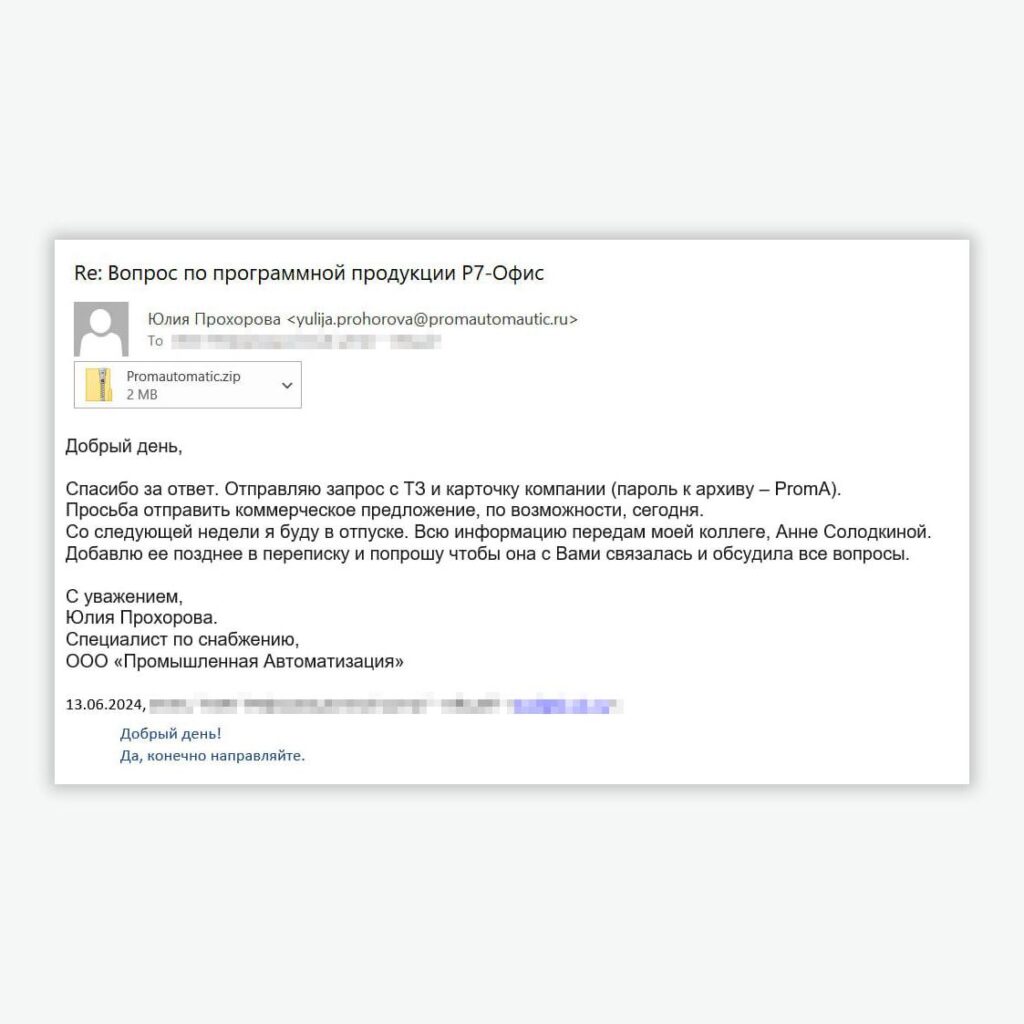
#TI #DarkGate #Phishing
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…