
The Lost Goffee Bean
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




Literally a couple of days after our research into the activity of the Goffee group, another attack was carried out, which we will now tell you about
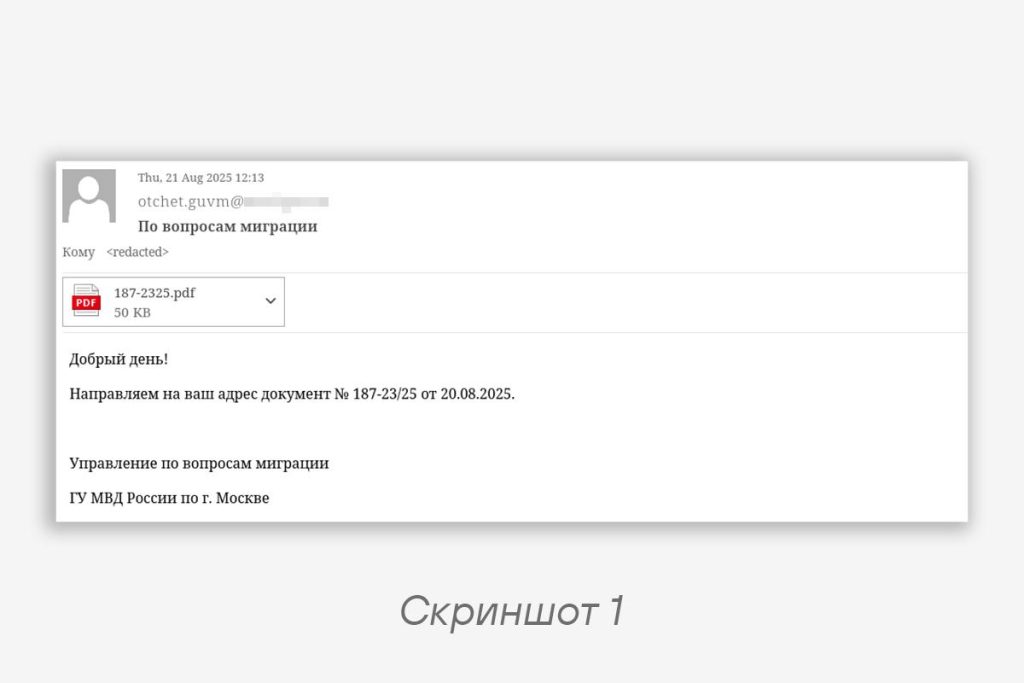
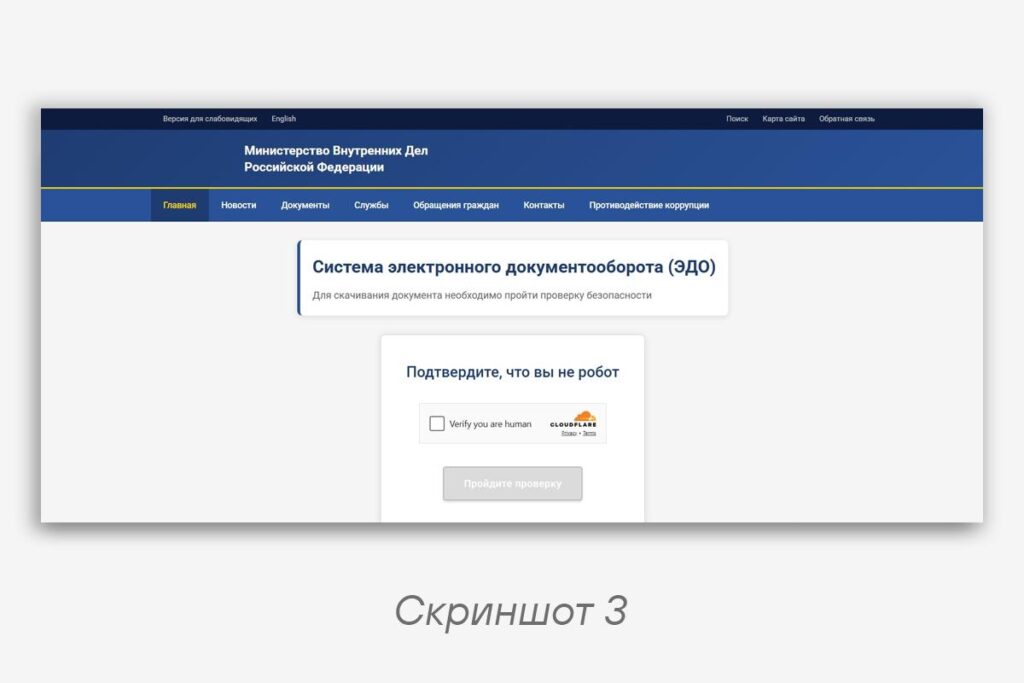
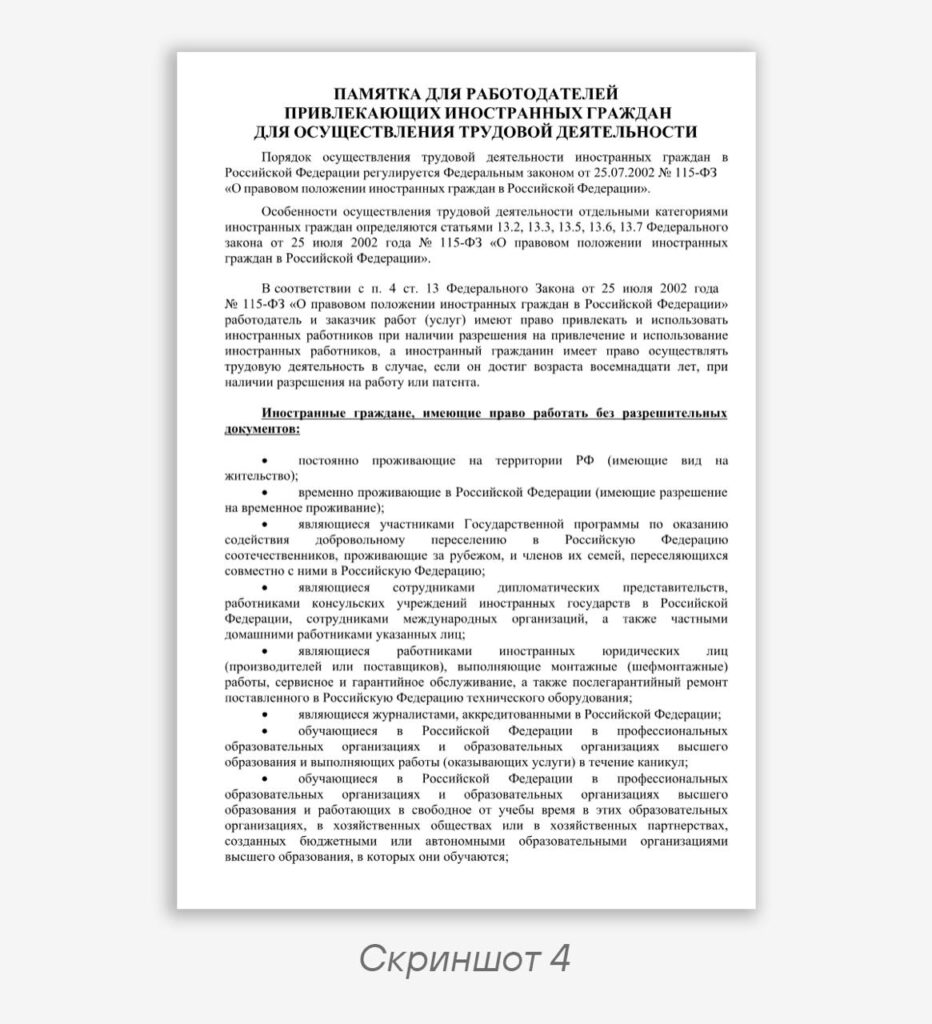
👋 It all starts with an email purportedly from the Main Directorate of the Ministry of Internal Affairs of Russia (screenshot 1), with a PDF document attached containing the following content (screenshot 2). In the document, the victim finds a link to download the attached materials, but the link itself leads to a fake MVD website (screenshot 3), where a captcha is required to download. After passing the captcha, an archive
182-1672143-01.zip is downloaded, which, in addition to three decoy documents (an example of one decoy can be found in screenshot 4), contains a payload named 182-1672143-01(исполнитель * М.Д).exe**.The payload consists of previously known .NET loaders. And if earlier the threat actors randomized the names of mutexes, methods, and types of the next stage, now the GET requests themselves are also being modernized.
🔄 The classic parameters in the URL —
hostname= and username= — have been replaced with random strings. For example, in one of the loaders, a URL of the following format was constructed:https://regrety.com/perplexed/blanket/caryatids/enthused/microlight?ToothRoofCarpet=<MachineName>&ChickWireHorse=<UserName>
Code language: YAML (yaml)In addition, some loaders could contain a decoy document named
input.docx, which did not differ in content from one of the documents in the archive.Based on similar names, a total of four archives with the malware described above were discovered. Finding the archives and attributing these attacks to the Goffee group is also helped by the network infrastructure characteristics highlighted in the article (and the OFFZONE presentation):
• All domains found in the loaders have .com/.org TLDs, and the domains themselves are second-level.
• In all loaders, links of the fourth and deeper nesting level are used to obtain the next stage of the attack chain.
• All domains are registered with Namecheap.
• All domains are hosted on Russian IP addresses.
Additional searches based on executable file characteristics (similar names, preserved Debug Paths, and others) helped identify a number of other samples belonging to Goffee.
Network indicators of compromise
Domains:
cloud.mvd.spb.ru
brothiz.com
possessionpower.org
regrety.com
votexrp.com
combibox.net
pundy.org

Links:
https://cloud.mvd.spb.ru/8u43sj
https://brothiz.com/counties/indicating/football/compress/bards
https://possessionpower.org/photographing/insinuating/predisposing/insolent/envious
https://regrety.com/perplexed/blanket/caryatids/enthused/microlight
https://votexrp.com/glossed/complainingly/blank/looks/adjudge
https://combibox.net/gravitated/larva/commends/lambswool/potted
https://pundy.org/deliberation/corslet/posterior/flavourings/eavesdroppers
Code language: YAML (yaml)
File indicators of compromise
Archives:
202645d53e040eddb41dfeb1ed0560d3500a15c09717d8853928ee9a17208e22
fd54cda0111f9746a3caa64a1117b94a56f59711a83ec368206105d5c8d757b0
e27af28d19791d18c0cb65929a530fe5aeb5db25a35fe26e2993c444dcd58352
4888c94e8a943d02f5fcc92f78a0cd19b957fb0c8709d4de484cd36c97448226

Payloads:
b8cf62b529b17f5c8cf3cfa51d47f5dcf263c8ee5fffc427ea02359d4597865a
c89ab2c5648be4f4e459422fe90be09402824e8555484f1cc51a22ad96edf19b
3f151143fc4747f0f99aeba58a3d83d9ae655da3b5721a0900320bc25992656f
6262e99b7020b8e510ae9e6d8119affb239b42f4a5966af362f58292aa0af700
c45905101c29be2993dfaf98752df6def0ac47dd4c4a732d4bfdc8c4f002b6f1
ee17de2e428b9cf80e25aeaa3272bd8516c9115f0733baec56014f6d3232b61a
Code language: plaintext (plaintext)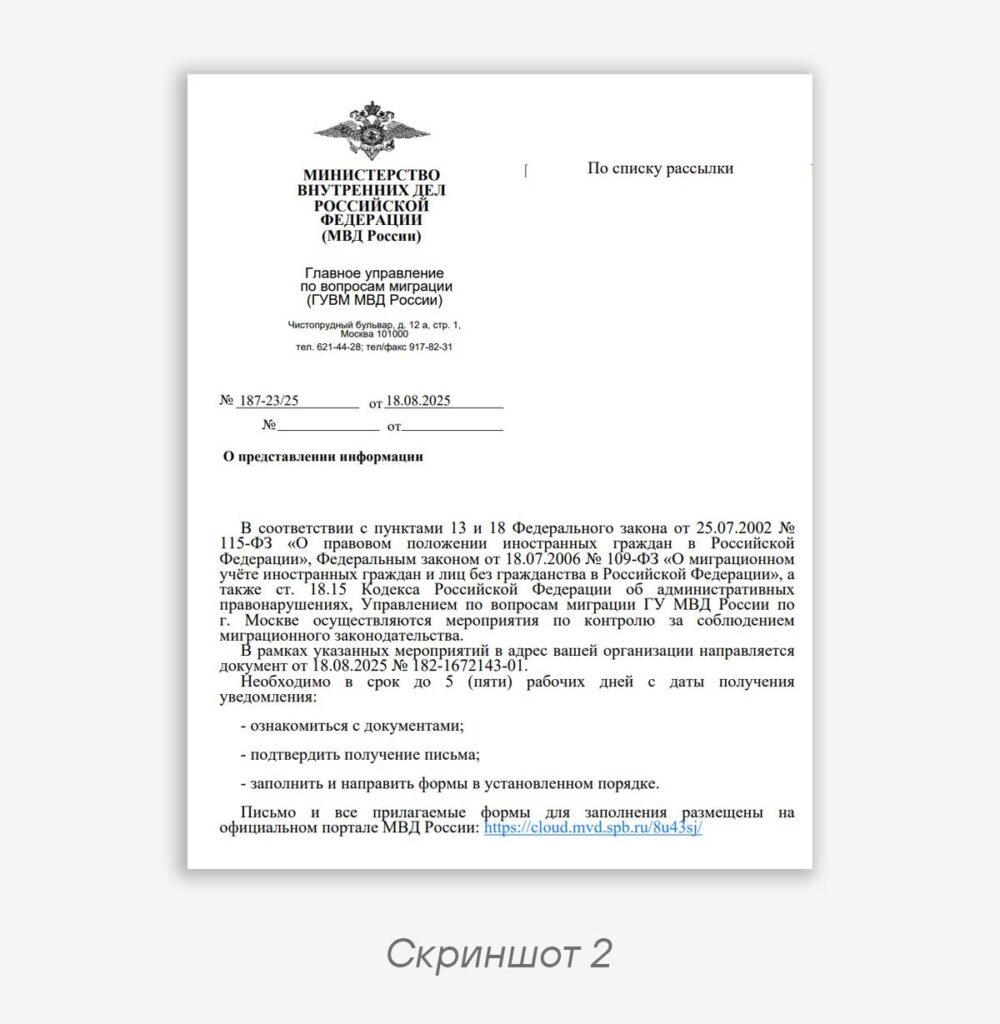
#TI #APT
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…