
Operation Tartaria — VTDoor
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




We have already covered Operation Tartaria in several posts — part 1 and part 2. In one of the cases, the PT ESC IR team discovered, in addition to PlugX modules, a dynamic library
NVIDIADEBUG.dll located in the C:\ProgramData\NVIDIA directory. To maintain persistence in the system, a task named NVIDIADEBUG was created, which runs every two hours. The command launch arguments:<Exec>
<Command>C:\Windows\system32\rundll32.exe</Command>
<Arguments>C:\ProgramData\NVIDIA\NVIDIADEBUG.dll fun</Arguments>
</Exec>
Code language: plaintext (plaintext)The executable was named VTDoor because the malware uses comments on files on VirusTotal to communicate with the C2 server.
The dynamic library
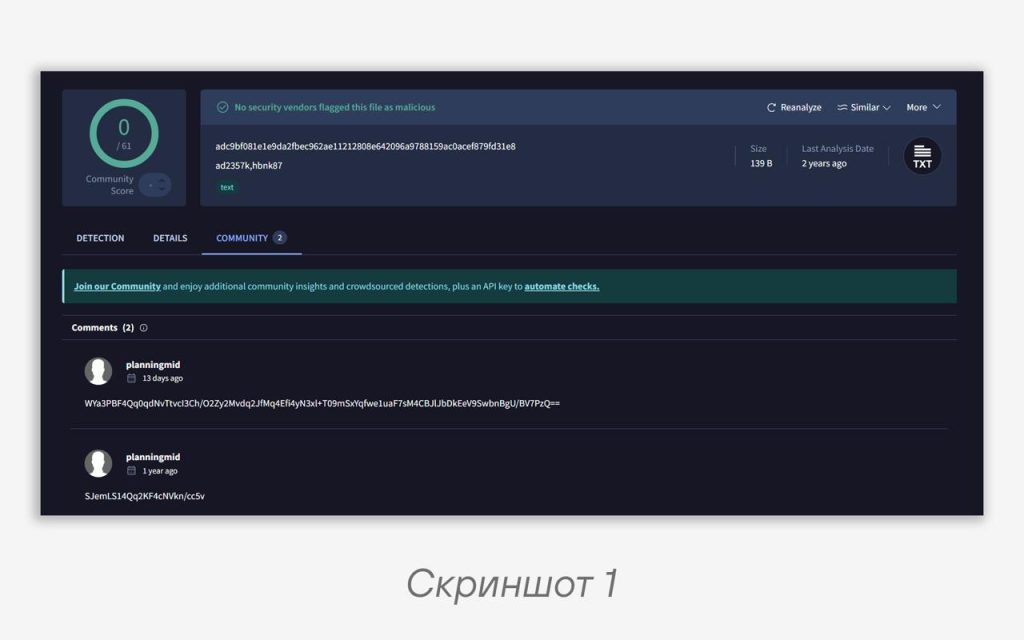
NVIDIADEBUG.dll contains an export function fun, which implements the main set of functions. Using the VT API, VTDoor retrieves an encrypted command from a file comment: https://www.virustotal.com/api/v3/files/adc9bf081e1e9da2fbec962ae11212808e642096a9788159ac0acef879fd31e8/comments (screenshot 1). After executing it, it publishes the result; the file hash and the VT token (x-api-key) are encrypted in the module using the RC4 algorithm with the key 032yhns1!-=.👀 The method of using VirusTotal as a two-way C2 channel is not new and is already used in some C2 frameworks. Let’s look at how the command exchange protocol is structured.
➡️ VTDoor retrieves the list of comments in a JSON file and extracts the
id and text fields from it. It decodes the data from Base64 format and decrypts it using RC4 with the key usde-092d.The decrypted data must contain:
• a marker (0xAAAABBBB) — 4 bytes;
• the payload length — 4 bytes;
• the RC4 key for the payload — 4 bytes;
• the payload.
➡️ Next, the payload (the command to execute) is decrypted with a second RC4 key, and cmd.exe is launched with output redirected via Windows Pipes.
Sending the command result:
After the command is executed, a 4-byte RC4 key is generated, with which the result will be encrypted. It is packed into a message:
• a marker (0xBBBBAAAA);
• the length of the executed command result — 4 bytes;
• the RC4 key — 4 bytes;
• the executed command result.
The message is encrypted using the RC4 algorithm with the same key
usde-092d and encoded in Base64.➡️ To post a comment on the file on VT, a JSON file is generated in which the result of the executed command is added to the text field:
{"data":{"type":"comment","attributes":{"text":"<Comment>"}}}
Code language: JSON / JSON with Comments (json)
It was discovered that the user
planningmid (screenshot 2) also left comments on the files 90d2d1af406bdca41b14c303e6525dfc65565883bf2d4bf76330aa37db69eceb, f506898cc7c2e092f9eb9fadae7ba50383f5b46a2a4fe5597dbb553a78981268, in which the command whoami was encrypted.IoCs:
MD5: ca3820abd0331090c77116e2941f7b99
SHA1: b49a3d0f6f1af2d12d96a38a90f4c656c61ffdeb
SHA256: 1f5e377bdcc92c44e4aab816758560b07ac98003cbe0fb93960c1d710972bb7f

https://www.virustotal.com/api/v3/files/90d2d1af406bdca41b14c303e6525dfc65565883bf2d4bf76330aa37db69eceb/comments
https://www.virustotal.com/api/v3/files/f506898cc7c2e092f9eb9fadae7ba50383f5b46a2a4fe5597dbb553a78981268/comments
https://www.virustotal.com/api/v3/files/adc9bf081e1e9da2fbec962ae11212808e642096a9788159ac0acef879fd31e8/comments
Code language: YAML (yaml)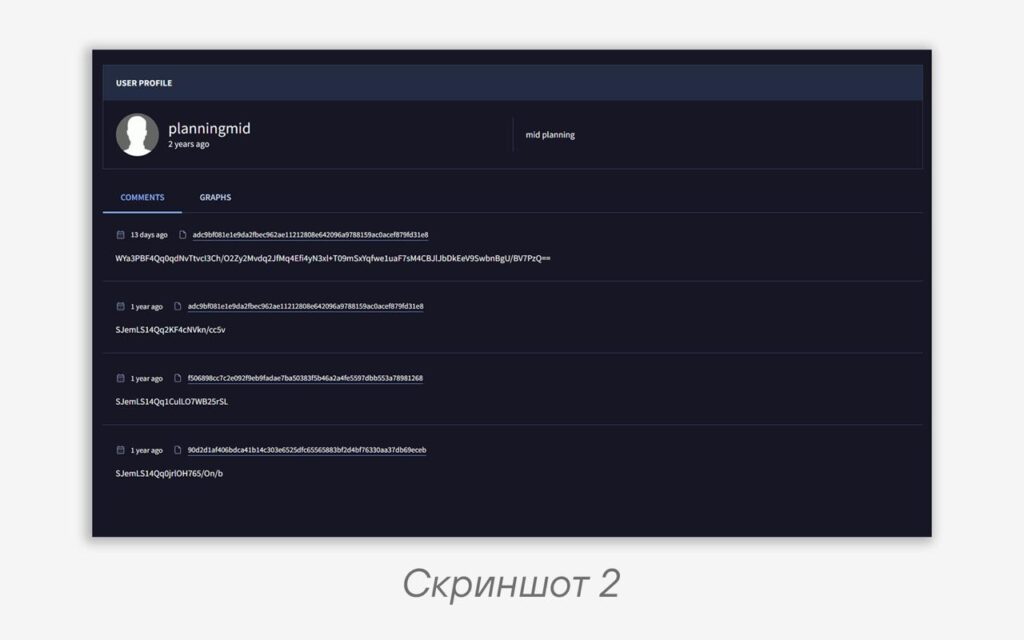
#dfir #ti #apt #reverse #malware
@ptescalator
More from oUth0R
- We helped Apple fix a vulnerability in the kernel of its operating systems
We helped Apple fix a vulnerability in the kernel of its operating systems PT ESC expert…
- Recovering EVTX records: carving methods
Recovering EVTX records: carving methods 🧩 When investigating incidents where attackers encrypt virtual machine images, a…
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Your Zimbra server is at risk
Recently, our PT ESC IR team encountered a new attack by ransomware groups on Zimbra mail…
- He's not your gsocket
He's not gsocket to you 😑 During the investigation of one of the incidents, PT ESC…



More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…